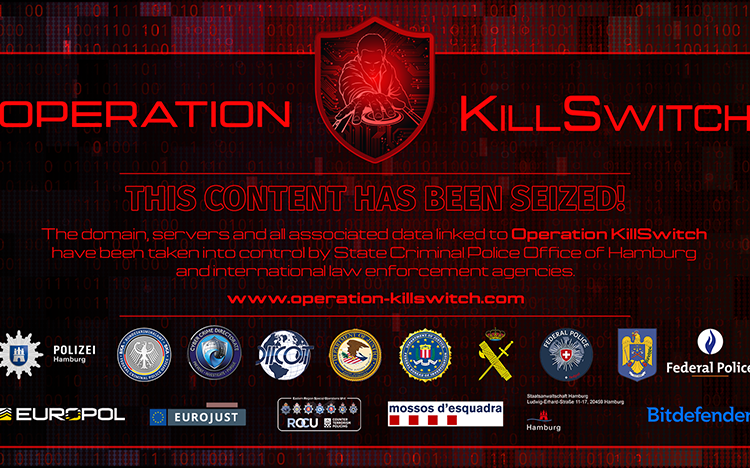
KillSec, active since 2024, used poorly secured cloud-linked access points to break into organisations, steal data, and extort victims by threatening public leaks. An international investigation led to arrests, seizures of infrastructure and stolen data, and ongoing efforts to trace the group’s financial proceeds and identify more victims and suspects. #KillSec #Eurojust #Europol
Keypoints
- KillSec exploited weak cloud access points to enter victims’ systems.
- The group stole data and copied it to its own infrastructure.
- Victims were threatened with public leaks unless they paid a ransom.
- Authorities identified suspects in roles such as administrator, developer, negotiator, and affiliate.
- International raids led to arrests, server seizures, and the recovery of at least 110 terabytes of stolen data.