The ransomware group incransom claimed it compromised https://eclmn.com/, impacting a family-run health and residential care organization in Minnesota that provides adapted housing, professional in-home support, and daily living solutions for adults with physical disabilities and limited mobility. #UnitedStates

Lasso’s AI Security Platform is designed to secure agentic AI by continuously discovering agents, assessing posture, red teaming behavior, and enforcing runtime guardrails based on intent rather than static content. It creates a closed-loop defense that maps risks to OWASP, NIST, and MITRE controls while helping organizations detect misconfigurations, behavior drift, and attack paths across AI systems. #Lasso #OWASP #NIST #MITREATLAS

Daily Recap, Organizations are facing a surge in shadow AI agents, with guidance on discovery and security as Nvidia and other tech giants push an AI security alliance to protect expanding AI systems and agent deployments. Meanwhile, attackers continue to evade detection with MedusaHVNC, supply-chain defenses were strengthened by GitHub and PyPI using time-based protections, and new breach disclosures from Coca-Cola and MCBS keep ransomware and large-scale exposure in focus.
#ShadowAI #Nvidia #AIAlliance #MedusaHVNC #GitHub #PyPI #CocaCola #Fairlife #MCBS #Wyden #ZeroTrust #VPN
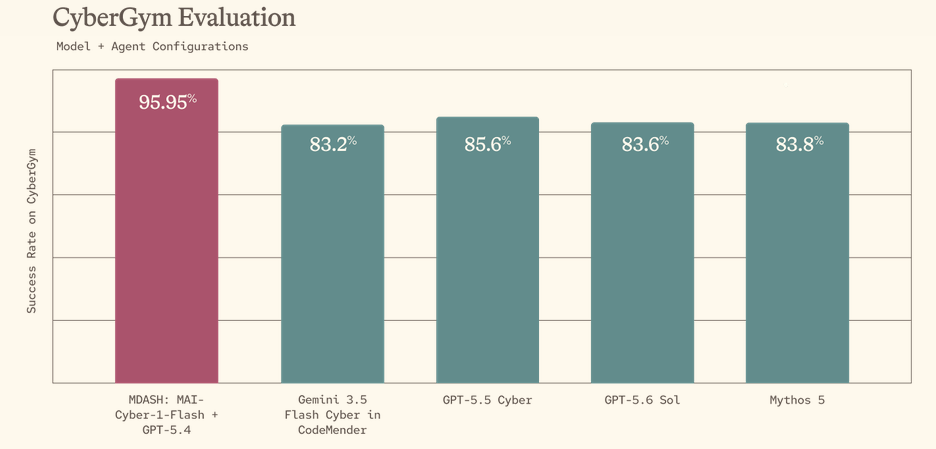
Microsoft has introduced MAI-Cyber-1-Flash, its first cybersecurity AI model, and says it outperformed Google’s 3.5 Flash Cyber, OpenAI’s GPT-5.6 Sol, and Anthropic’s Mythos 5 in vulnerability discovery. The model is integrated into MDASH and will be available through Project Perception, which enters public preview on August 3. #Microsoft #MAI-Cyber-1-Flash #MDASH #ProjectPerception…
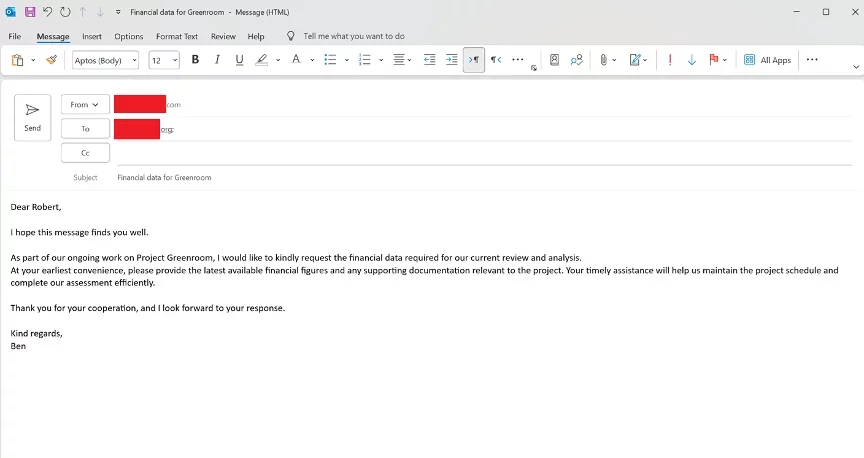
Threat actors are increasingly discussing and selling indirect prompt injection (IDPI) tools on underground forums, with generators for email, PDF, calendar invite, and webpage attack content. The activity suggests near-future abuse of hidden prompts in mail, documents, calendar invites, and malvertising to manipulate AI agents and exfiltrate data. #IndirectPromptInjection #TycoonPhaaS #OWASP…
This episode of the Securanoia podcast features a deep discussion with Brook Scharli about the cyber risks, challenges, and best practices associated with artificial intelligence. It explores how AI, agentic AI, and autonomous systems are reshaping cybersecurity, risk management, and personal protection for families. #Securanoia #BrookScharli #AgenticAI #ArtificialIntelligence

Europol’s IOCTA 2025 shows how stolen data has become a core commodity in cybercrime, fueling fraud, account takeovers, extortion, and access brokering across dark web forums and encrypted channels. The report highlights the growing impact of infostealers, ClickFix, vishing, and generative AI, while also noting major law enforcement disruptions to Lumma, LabHost, Cracked, and Nulled. #Europol #IOCTA2025 #Lumma #LabHost #Cracked #Nulled #ClickFix #Infostealers
A forum user known as ChimeraZ allegedly leaked a 222MB Allo.Solar database containing 208,694 order lines and personal data for 101,349 French customers. The exposed records reportedly include names, phone numbers, addresses, partial card details, and itemised solar equipment orders, with the post framed around the Gironde wildfire emergency. #AlloSolar #ChimeraZ…

The ransomware claim targets landesmuseum.de in Germany, attributed to the safepay threat actor. The established 1919 museum, preserving and presenting more than 50,000 years of human cultural history, including prehistoric artifacts, is reported as impacted in #Germany
Prelys Courtage in FR reported a ransomware-related client data breach affecting a major mortgage brokerage franchise attributed to the anubis threat actor. #France
Gran valle negocios in AR was targeted by ransomware attributed to the qilin threat actor, resulting in disruption to their systems and encrypted data. The attack led to operational impact and data compromise for the organization in #Argentina
Medical Computer Business Services (MCBS) says a 2025 network breach exposed sensitive data belonging to 1,261,464 people, including names, Social Security numbers, medical history, and insurance details. The PEAR ransomware group claimed the attack and alleged it stole 3.3 terabytes of data from MCBS systems. #MCBS #PEARRansomware
OCS, a company in the ANA Group, confirmed that its overseas resident e-commerce service OCS FAMILY LINK SERVICE was hit by a cyberattack involving unauthorized external access to its servers. The company shut down the system and related networks while investigating with authorities, and said personal data may have been leaked. #OCS #OCSFAMILYLINKSERVICE #ANAGroup
CubePilot, an Australian supplier of embedded hardware and software for the civil uncrewed systems industry, has reported a security incident affecting some of its systems. As a precaution, the ERP portal was taken offline while the company investigates the incident with Australian authorities and has not yet identified a threat actor. #CubePilot #ERP
Mirage Kitten (also tracked as UNC1549, Smoke Sandstorm, and Nimbus Manticore) deployed custom malware including the NightLedger backdoor and the ArcBridge and BridgeHead WebSocket tunnelers to conduct targeted espionage against aerospace, aviation, defense, and telecom victims in the Middle East, Europe, and Africa. The campaign used spear-phishing, fake recruitment portals, and proxy-aware tunneling infrastructure to maintain access, exfiltrate data, and hide command-and-control traffic. #MirageKitten #UNC1549 #NightLedger #ArcBridge #BridgeHead