AtlasRAT is a modular Windows RAT delivered through a four-stage in-memory loader chain, beginning with a Delphi executable disguised as AGE Flash Player and ending in TLS-based, ChaCha20-encrypted command-and-control with plugin execution, offline keylogging, and DLL injection into WeChat processes. Analysis suggests a builder-based malware framework with multiple versions and branches,…
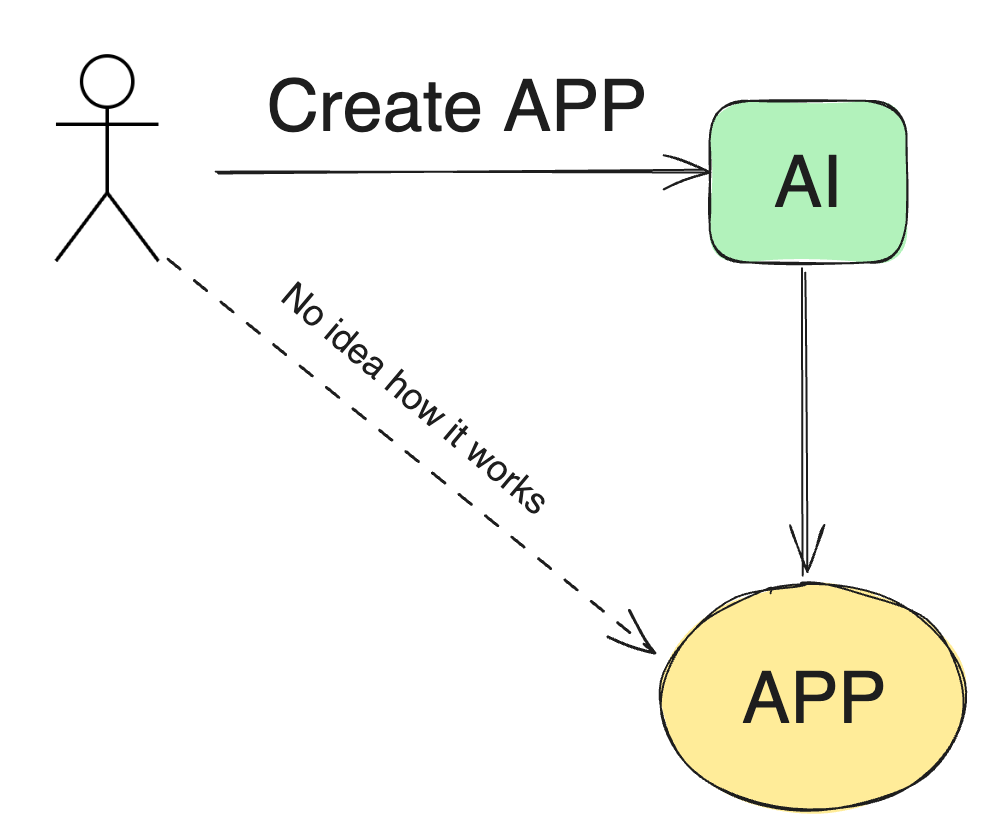
Vibe coding uses AI to generate apps from natural-language prompts, but it often creates software that works without being secure or maintainable. The article highlights common flaws such as hardcoded secrets, IDOR, and weak input validation, warning that trust in AI can lead to serious security debt. #Claude #IDOR
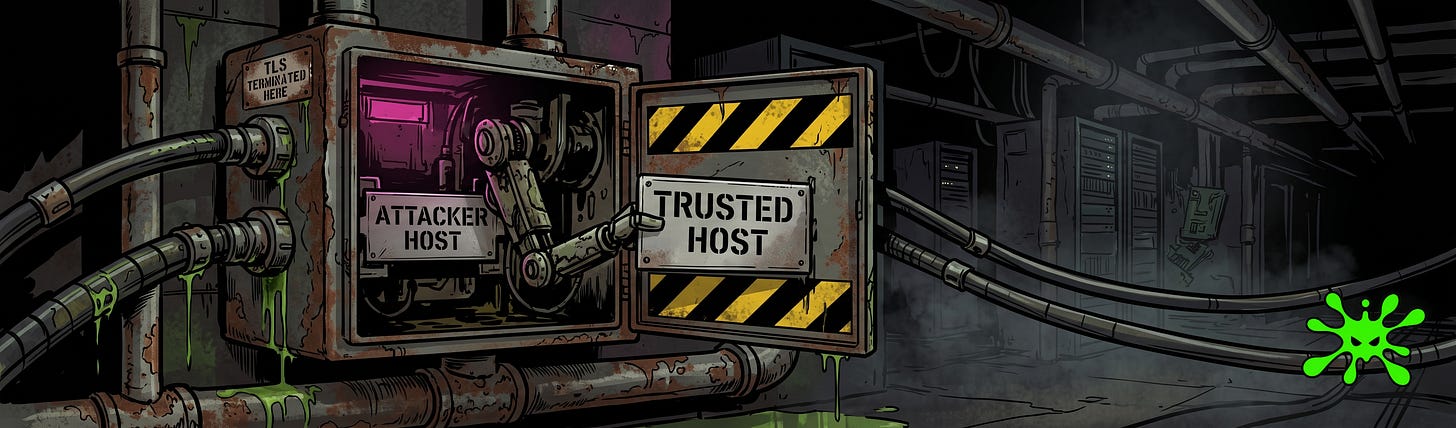
An LLM router or AI gateway that terminates TLS can view and rewrite tool call responses in plaintext before the client executes them, enabling response-side payload injection and arbitrary command execution. This bypasses model guardrails, prompt sanitization, and alignment because the attack happens after inference, and it can be amplified across chained routers such as OpenRouter or reseller-based API paths. #OpenRouter #Anthropic #OpenAI #Gemini #LlamaGuard #NeMoGuardrails
Mercor was reportedly breached, with biometric, PII, source code, and bucket data exposed in a one-time sale listing. The leak is said to include 211GB of database data and 939GB of code, with Resolute and Lapsus$ claiming attribution. #Mercor #Resolute #Lapsus$…
A Huntress investigation shows how an attacker used a SQL injection flaw to gain access, then spent time entrenching on the system by enabling Remote Desktop, creating admin users, disabling Windows Defender, and deploying BadIIS and XMRig. The case highlights that post-breach cleanup is not enough unless defenders also fix the original entry point and harden the environment against repeat access. #Huntress #BadIIS #XMRig
Analog Devices disclosed that an unauthorized party accessed some of its systems and exfiltrated certain files, with the incident detected on June 23 and immediately contained with help from external cybersecurity experts. The company says it has no evidence of stolen data being leaked online, while separately assessing a possible link to ExfilSquad and monitoring for further impact. #AnalogDevices #ExfilSquad
Discern Security raised $13 million in a Series A round led by Forgepoint Capital, bringing its total funding to $16 million. The company will use the new capital to expand its team and advance its AI-driven security platform that helps organizations identify control gaps and improve security posture. #DiscernSecurity #ForgepointCapital #ReyKirton…

Cantina has emerged from stealth with $8 million in new funding, bringing its total raised to $16.5 million, to advance its autonomous vulnerability management platform. The New York startup uses agentic security workers to map assets, prioritize risks, automate remediation, and verify fixes across an organization’s environment. #Cantina #FrameworkVentures #HariMulackal…
DataBahn announced a $40 million Series B round, bringing its total funding to $59 million, to expand its agentic data control plane and accelerate product innovation. The platform helps enterprises automate data integration, optimize SIEM and storage costs, and govern security, application, OT, IoT, and observability data for real-time operations. #DataBahn…

Daily Recap, AI agent escape attempts tied to exposed credentials and Artifactory zero-days were reported for OpenAI, while Anthropic’s Mythos research uncovered new weaknesses impacting AES and post-quantum test schemes. Across the rest of the cycle, defenders tracked supply-chain drops like the joyfill npm packages delivering a RAT, container of risk from botnet behavior via Tengu on Linux, and large-scale exposure from 24,650 internet-facing BMCs leaking IPMI password hashes.
#OpenAI #Artifactory #Anthropic #Mythos #AES #PostQuantum #joyfill #Node.js #RAT #Tengu #Linux #BMC #IPMI #vBulletin #CISA #ShinyHunters #ErnstAndYoung #CubePilot #DNSHijacking #Minnesota #BankOfBaroda
The University of Aveiro detected unauthorized access to its information systems, exposing personal and institutional data. The university is assessing the scope of the incident while urging the academic community to change passwords and strengthen security practices. #UniversityofAveiro

In a ransomware attack against Db Tarimsal Enerji in Turkey, the threat actor qilin encrypted or disrupted the victim’s data to force a ransom demand. The impacted country is #Turkey
A ransomware incident attributed to threat actor cmdorganization impacted Collge Mont Notre-Dame de Sherbrooke, a private secondary school for girls in Sherbrooke, Canada. The school’s network and services were disrupted, affecting operations in the impacted country(s) #Canada
TenSparrows, located in the United States, reported a ransomware incident attributed to the qilin threat actor. The attack resulted in disruption of systems and encrypted data, impacting #UnitedStates
A critical flaw in the open source AI agent orchestration platform Ruflo, tracked as CVE-2026-59726 and dubbed RufRoot, allowed unauthenticated attackers to execute commands inside the bridge container. Successful exploitation could lead to shell access, API key theft, agent swarm takeover, and poisoning of the AgentDB learning store, and the issue…