Arch Linux has temporarily disabled AUR package adoption after a wave of malicious takeovers led to infected packages being pushed through the repository. The campaign, which started with openconnect-sso and may involve over 200 packages, uses a Tor-based two-stage payload to steal credentials, spread via SSH, and maintain persistence. #ArchLinux #AUR #openconnect-sso #IFIN
Amgen said attackers stole corporate data and patient information from multiple third-party cloud environments, and the company detected the unauthorized activity in July 2026. The investigation is still ongoing as Amgen works to determine the full scope of the breach and whether it is linked to ShinyHunters. #Amgen #ShinyHunters
President Donald Trump blamed Minnesota for recent cyberattacks on the state’s water systems, despite U.S. investigators attributing the activity to Iran. Cyber experts and officials pushed back, citing CISA warnings, evidence of Iranian involvement, and the need to protect critical water infrastructure. #Minnesota #CISA #WaterISAC #TimWalz #SolarWinds

Additive Manufacturing LLC, a U.S.-based 3D printing and rapid prototyping provider, reported a ransomware incident attributed to the threat actor thegentlemen after an attack on its operations. The compromised systems impacted operations in #UnitedStates
Insomnia ransomware targeted Laempe Reich, the US-based leading foundry core machine supplier providing sand core equipment and technology for metal casting, disrupting operations as a long-standing partner in the industry for over 80 years. The claim indicates impact in the United States. #UnitedStates
Merritt Woodwork in the US, a provider of strategic interior solutions for global estates and superyachts, was targeted by the insomnia ransomware threat actor. The attack disrupted operations and impacted business activities in #UnitedStates
Bitsight says the Fuyao operation used cheap Android TV boxes to spoof phone identities, click ads, and sometimes relay other people’s traffic as SOCKS5 exit nodes. The campaign was attributed to Zhejiang Fengwo IoT Technology Co., Ltd., with researchers linking it to a large fraud infrastructure and advising users to check…

Researchers uncovered HollowFrame, a Go-based loader framework, and Matryoshka, a Rust-based malware family used in a multi-stage intrusion against two endpoints at a law firm. The attack used spear-phishing, DLL side-loading, and GitHub-based command-and-control to enable persistence, reconnaissance, file transfer, and follow-on payload delivery. #HollowFrame #Matryoshka #GitHub #BlackpointCyber…

A suspected Chinese-speaking threat actor has launched a new campaign against government-related organizations across Central Asia and the Syrian Arab Republic using the backdoors OctLurk and SilkLurk, alongside the proxying tool LurkProxy. The malware operates largely in memory, supports extensive post-compromise activity, and shows infrastructure overlap with the SilentRaid, MystRodX, and…
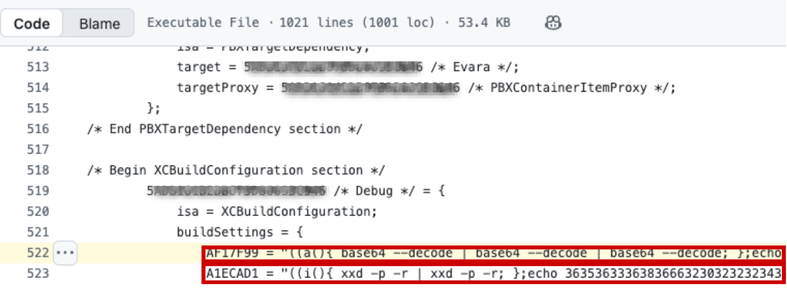
XCSSET v40 is a heavily updated macOS malware family that uses memory-resident execution, polymorphism, and supply-chain infection through poisoned Xcode projects to target developers. It also adds browser hijacking, Telegram trojanizing, defense evasion, and a rotating C2 infrastructure across domains, IPs, and endpoints. #XCSSET #Xcode #GoogleChrome #Telegram #Apple…

Google Threat Intelligence Group (GTIG) reports a sharp rise in open source software supply chain compromise in 2025 and early 2026, including major campaigns tied to UNC6780, MIDNIGHT NEPTUNE, and UNC4899. The article also outlines detailed mitigation guidance for protecting ecosystems such as PyPI, npm, Docker Hub, GitHub Actions, and developer pipelines from package poisoning, credential theft, and workflow abuse. #UNC6780 #MIDNIGHTNEPTUNE #UNC4899 #axios #PyPI #npm #DockerHub #GitHubActions
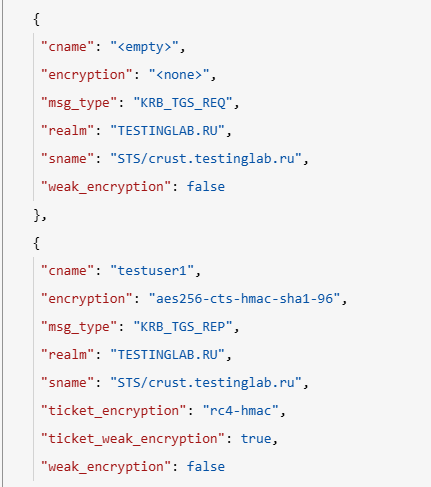
The article explains how Kaspersky Anti Targeted Attack (KATA) uses Network Anomaly Detection to identify Kerberoasting and DNS tunneling by spotting deviations from normal Kerberos and DNS behavior rather than relying on signatures. It also shows how prebuilt NAD rules, variables, and SQL-based logic help reduce false positives and surface actionable alerts for attacks that blend into legitimate network traffic. #KATA #Kerberoasting #DNStunneling #Kerberos #DNS
The Kenaitze Indian Tribe (kenaitze.org) in the US reported a ransomware incident attributed to the threat actor thegentlemen, impacting its operations supporting the Dena’ina Wellness Center and related community services. The attack affected the Tribe’s critical health, education, and elder care functions, creating disruption across its services provided within the #UnitedStates
Las Cenizas (CL) reported a ransomware claim affecting its operations linked to its mining activities across Cabildo, Taltal, and Franke, with the threat actor thegentlemen. The incident has impacted #Chile
Authorities in Minnesota are investigating cyberattacks that hit more than 30 water systems, with officials not yet identifying the culprit. The incidents come as US agencies warn that Iranian hackers have been targeting water and wastewater systems and other critical infrastructure. #MinnesotaITServices #FBI #CISA #IranianHackers…