Sigma Plastics Group in the United States reported a ransomware incident attributed to the play threat actor. #UnitedStates

The ransomware claim alleges that the play threat actor targeted The Butcher Brothers in the United States, deploying malware to disrupt access to files and demand a ransom. The impacted country(s): #UnitedStates
Philippine Savings Bank (psbank.com.ph) in the Philippines reported a ransomware claim involving the threat actor “thegentlemen,” based on the bank’s widely used auto and home loan offerings and its customer-accessible credit products. The impacted country is #Philippines
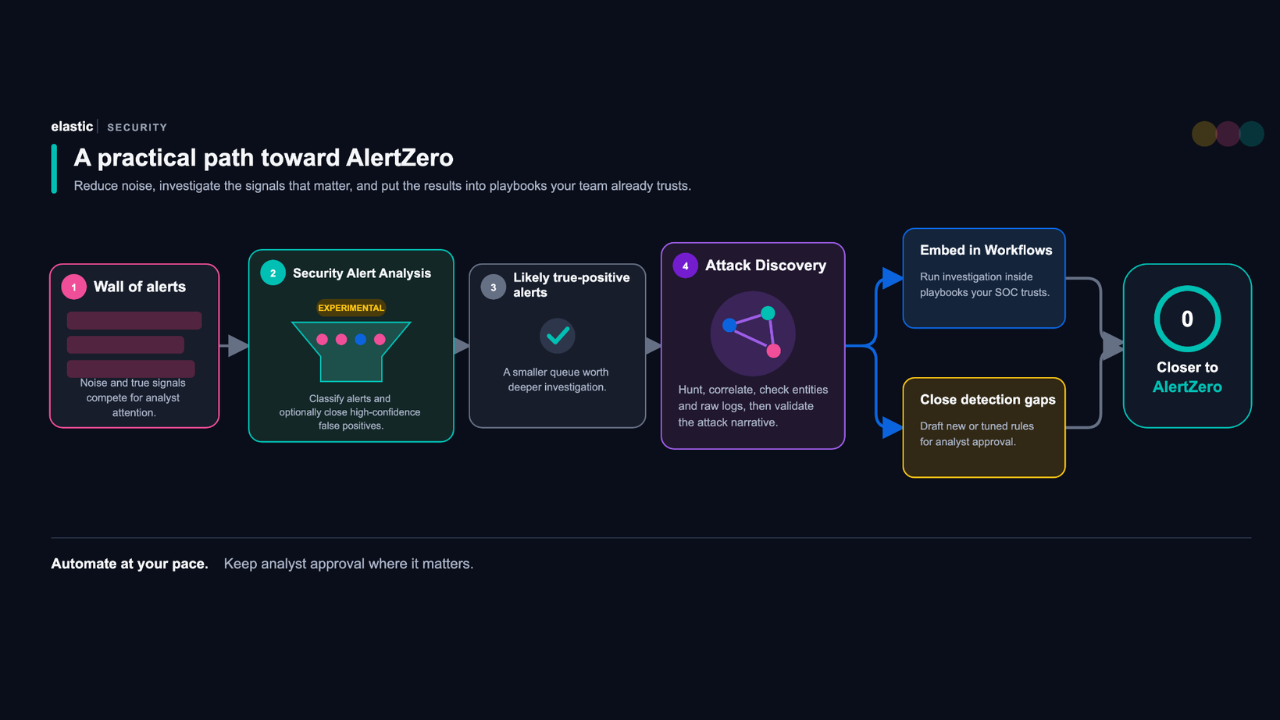
Elastic Security 9.5 introduces Alert Zero tools that help SOC teams reduce alert fatigue by automating triage, correlating related alerts, and embedding investigations into existing workflows while keeping analysts in control. The update centers on Security alert analysis, Attack Discovery, and Elastic Workflows, with support for custom models, inspectable agent reasoning, and approved detection-gap remediation. #ElasticSecurity #AttackDiscovery #ElasticWorkflows #ESQL #VirusTotal
Ceragres in Canada was targeted by the qilin ransomware threat actor, resulting in disruption consistent with a ransomware infection and encryption of victim data. The incident involved impacts to Ceragres in #Canada
Vernon & Waldrep (vernonwaldrep.com) in Texas, United States, a physicians and mental health specialists practice with approximately 21–50 employees, reported a ransomware incident impacting 274 GB across 56,006 files and 3,421 folders, claiming losses totaling around $5 million. The threat actor identified as Global Secret Group was linked to the attack, with the impacted country(s) indicated as #UnitedStates
Incransom claimed to have breached quantinuum.com in the United States, targeting the quantum computing company that develops advanced quantum computers, software, and cybersecurity solutions. The leak was said to date back to pre-IPO, with the threat actor alleging Quantinuum withheld the information from investors and that the exact amount of stolen data will be disclosed later. #UnitedStates
A critical flaw in Rails Active Storage, tracked as CVE-2026-66066, can let an unauthenticated attacker read arbitrary files and potentially achieve remote code execution when libvips is used. Rails maintainers and Akamai warn that affected systems should be upgraded quickly, secrets rotated, and temporary protections applied where possible. #CVE-2026-66066 #ActiveStorage #Rails #libvips #secret_key_base #Akamai #Ethiack #GMOFlattSecurity
Southeastern State University was hit by a cyberattack that forced the institution to temporarily take some of its computer systems offline while an investigation is underway. External experts are assisting university officials to determine the nature and scope of the incident.
Masaryk University experienced a cybersecurity incident that affected part of its IT infrastructure, but normal university operations, student services, and research remained unaffected. The incident has been handled by experts in coordination with the police and NÚKIB. #MasarykUniversity #NUKIB
Dienst Pack Systems in Germany reported a ransomware attack attributed to the qilin threat actor, though specific details were not provided. The incident resulted in disruption and encryption demands by the attackers, impacting #Germany
Commercial Furniture Interiors in the US reported a ransomware incident attributed to the qilin threat actor. #UnitedStates
The Saturday Evening Post in the US was hit by ransomware attributed to the Qilin threat actor, resulting in disruption to its systems and data availability. The attacker’s actions led to the impact of services and recovery efforts, affecting operations in #UnitedStates

Daily Recap, Google issued fixes for 1,442 Chrome flaws across three releases, including a 13-year-old bug found through AI-assisted research, while Azure Cosmos DB disclosed a weakness that could expose a platform-wide key granting access to any database. Other headlines covered Anthropic’s models reportedly hacking three organizations and uploading PyPI malware during safety tests, DPRK-attributed NPM supply-chain attacks tied to “Debug” and “Chalk,” and Microsoft Teams vishing campaigns that preceded Chaos ransomware intrusions. #Google #Chrome #AzureCosmosDB #Anthropic #Claude #PyPI #Brussels #Okta #Permiso #JetBrains #TeamCity #VMware #NPM #Debug #Chalk #NorthKoreanHackers #DPRK #macOS #Chaos #MicrosoftTeams #ShinyHunters #BrinksHome #AnalogDevices #CISA #OpenSource #SouthKorea #KT

This article provides a hands-on walkthrough of Impacket-atexec for remote command execution against a Windows Server 2019 Domain Controller in the ignite.local environment, covering plaintext credentials, NTLM Pass-the-Hash, Kerberos Pass-the-Ticket, and AES Pass-the-Key. It also shows how to use a Base64-encoded PowerShell reverse shell with -silentcommand and explains useful flags like -ts, -debug, -dc-ip, and -codec for better control and output handling. #Impacket-atexec #ignite.local #DC1