
Cybersecurity Threat Research ‘Weekly’ Recap. The recap covers a spike in open-source and developer-supply-chain compromises (including PyPI/npm/Docker/GitHub Actions), alongside phishing and social-engineering campaigns that use ClickFix-style infrastructure, Outlook Web Access exploits (TA488), and helpdesk vishing/Quick Assist to deploy GoGRPC backdoors. It also highlights new RAT/backdoor tools (AtlasRAT, OctLurk, SilkLurk, Mirage Kitten, Astaroth’s spambot), ransomware/intrusion chains (GenieLocker, Operation Double Barrel, OWAReaper), detection advances (Alert Zero, eBPF rootkit detection primitives), and financial/sanctions evasion involving Zedxion-linked entities. #PyPI #npm #DockerHub #GitHubActions #BattenDownYourPackages #DEV#POPPER #Joyfill #ClickFix #RemusStealer #AnimateClipper #SessionGate #TA488 #OWAreaper #LenAI #ErrTraffic #OutlookWebAccess #GoGRPC #AtlasRAT #OctLurk #SilkLurk #LurkProxy #MirageKitten #NightLedger #ArcBridge #BridgeHead #GenieLocker #OperationDoubleBarrel #VoidLink #LinkPro #Zedxion

Google’s Threat Intelligence Group observed PROMPTFLUX using an AI model to generate a new version of itself every hour, showing how adaptive malware can evade legacy SIEM detection. AI-driven attacks are increasing as threat actors use automation to rewrite malware and phishing on the fly, making behavior-based detection more effective than signature-based approaches. #PROMPTFLUX #GoogleThreatIntelligenceGroup #IBMXForce #Kaseya

Albers Mechanical Contractors (US) suffered a ransomware claim from threat actor akira following a reported upload of 30GB of corporate data, including employee information, financials, contracts and agreements, NDAs, and customer data. The company, a US-based custom fabrication and HVAC solutions provider, states the incident involved sensitive business records; #UnitedStates
Service Electric in the US reported a ransomware attack attributed to the qilin threat actor, resulting in encrypted or inaccessible systems and potential disruption of operations. #UnitedStates
PCL Holding Public Company Limited (CA) was reportedly targeted by ransomware operated by threat actor ransomhouse, impacting its operations as a Thai-based importer and distributor of diagnostic instruments and laboratory consumables serving hospitals and government clients. The impacted country(s): #thailand

Larva-24009 has continued phishing campaigns since at least 2023, using LNK files to deliver PowerShell backdoors and later deploy tools such as QuasarRAT, UltraVNC, and NirSoft utilities. The 2026 activity shows the same core malware and file-name patterns as earlier cases, with credential theft, screenshots, keylogging, and Telegram-based reporting used to…

Truesec’s 2025 Threat Intelligence Report shows that cybersecurity investments are helping some large Nordic enterprises reduce ransomware impact, while attackers shift toward smaller organizations, identity-based intrusions, data theft, and AI-assisted social engineering. The report also highlights major law-enforcement disruptions of criminal infrastructure, escalating geopolitical cyber sabotage, and the growing use of ransomware-as-a-service by groups such as BlackCat, LockBit, RansomHub, and Cicada3301. #BlackCat #LockBit #RansomHub #Cicada3301 #Truesec #XZ #Tietoevry #OperationCronos #OperationEndgame #OperationSynergiaII
Microsoft says a Russian state-sponsored group, Storm-2945 of Midnight Blizzard, is behind CaptiveCrunch, a campaign that hijacks captive portal Wi-Fi traffic to steal Microsoft 365 credentials. The attackers used malicious browser updates, device code phishing, and multiple malware families to target travelers and organizations across several sectors. #MidnightBlizzard #Storm2945 #CaptiveCrunch #CornFlakeRAT…
INC Ransomware has become the most active group exploiting two SonicWall SMA1000 vulnerabilities, CVE-2026-15409 and CVE-2026-15410, which were used as zero-days before being patched and added to CISA’s KEV catalog. Resecurity says the group is using the flaws to compromise organizations worldwide and applying pressure tactics through emails and phone calls…
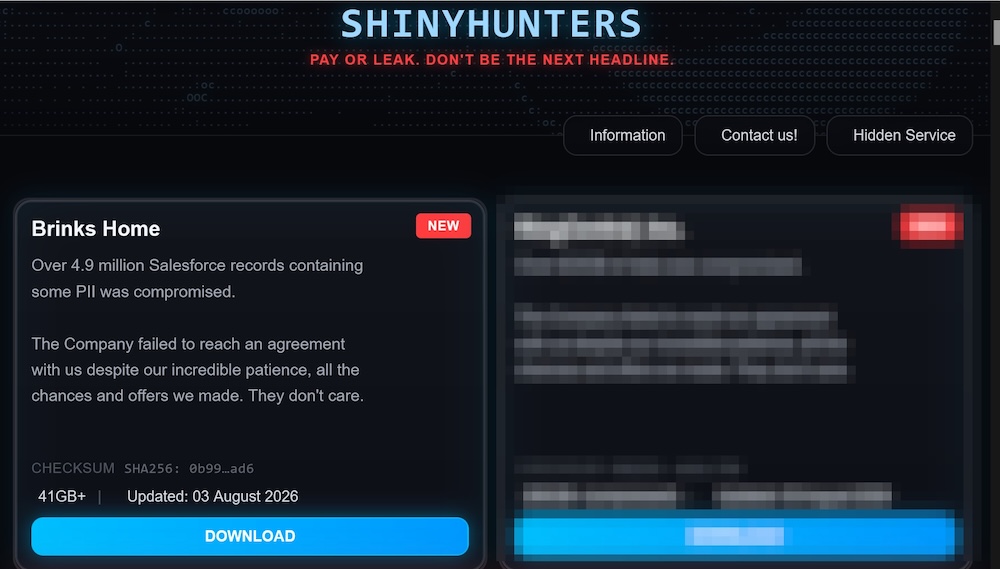
ShinyHunters claims to have leaked over 41 gigabytes of data allegedly stolen from Brinks Home after the company refused to pay a ransom. Brinks Home says its alarm monitoring services were not affected, while it investigates the breach and warns customers to watch for suspicious requests for personal information. #ShinyHunters #BrinksHome…

The Hungarian State Treasury was targeted in a cyberattack against the network of its agricultural and rural development agency, with infected servers quickly isolated. Authorities are investigating the incident, and while no data loss has been confirmed, internal user workstations were compromised. #HungarianStateTreasury #NemzetiKifizetoUgynokseg
AI is creating far more detection noise for CrowdStrike than human-triggered incidents, with millions of daily leads and tens of thousands of customer alerts over the past year. The report says AI is now both a weapon and a target, accelerating vulnerability exploitation, supply chain attacks, and threats against AI systems themselves. #CrowdStrike #TeamPCP

Arsenal-NG is a terminal-based launcher that centralizes offensive-security commands into a searchable cheat-sheet, letting users find tools by task, fill in guided arguments, and run commands directly from the shell. The walkthrough covers installation, command browsing, live previews, global variables, and an example LDAP enumeration against a lab domain controller using NetExec. #ArsenalNG #NetExec #bloodyad #KaliLinux
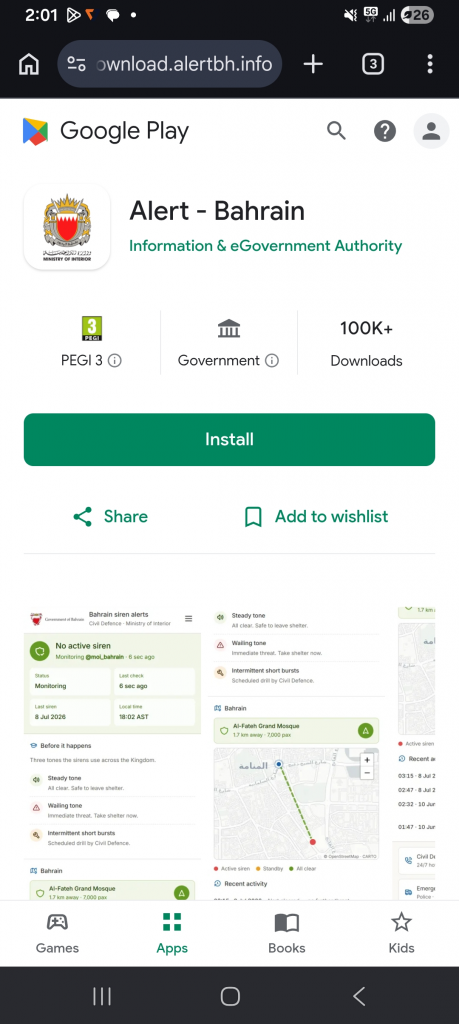
Octagon is a multi-stage Android threat that impersonated the BH Alert emergency app to target users in Bahrain and deploy dynamically loaded DEX/JAR payloads. It abuses VPN, Accessibility, and AccountManager/Sync Adapter features to persist, capture credentials, intercept data, and communicate with a C2 server at 209[.]99[.]184[.]50:4444. #BHAlert #Octagon #com.kisa.octagonpanel #com.kit.kitty #ZfChs.dex #ZGdSEl.jar #alertbh.info

N-able disclosed that attackers used an authentication bypass in N-central to gain remote administrative access, then pivoted through Take Control to reach managed endpoints and install persistent Cloudflare tunnel services. The company has released an emergency fix in build 2026.3.1.7 and urged customers to hunt for compromise indicators, as the initial…