The Virginia Peninsula Regional Jail (vprj.org) in the US was hit by ransomware attributed to incransom, disrupting operations at the state-authorized correctional facility in Williamsburg, Virginia. The incident impacted operations in #UnitedStates
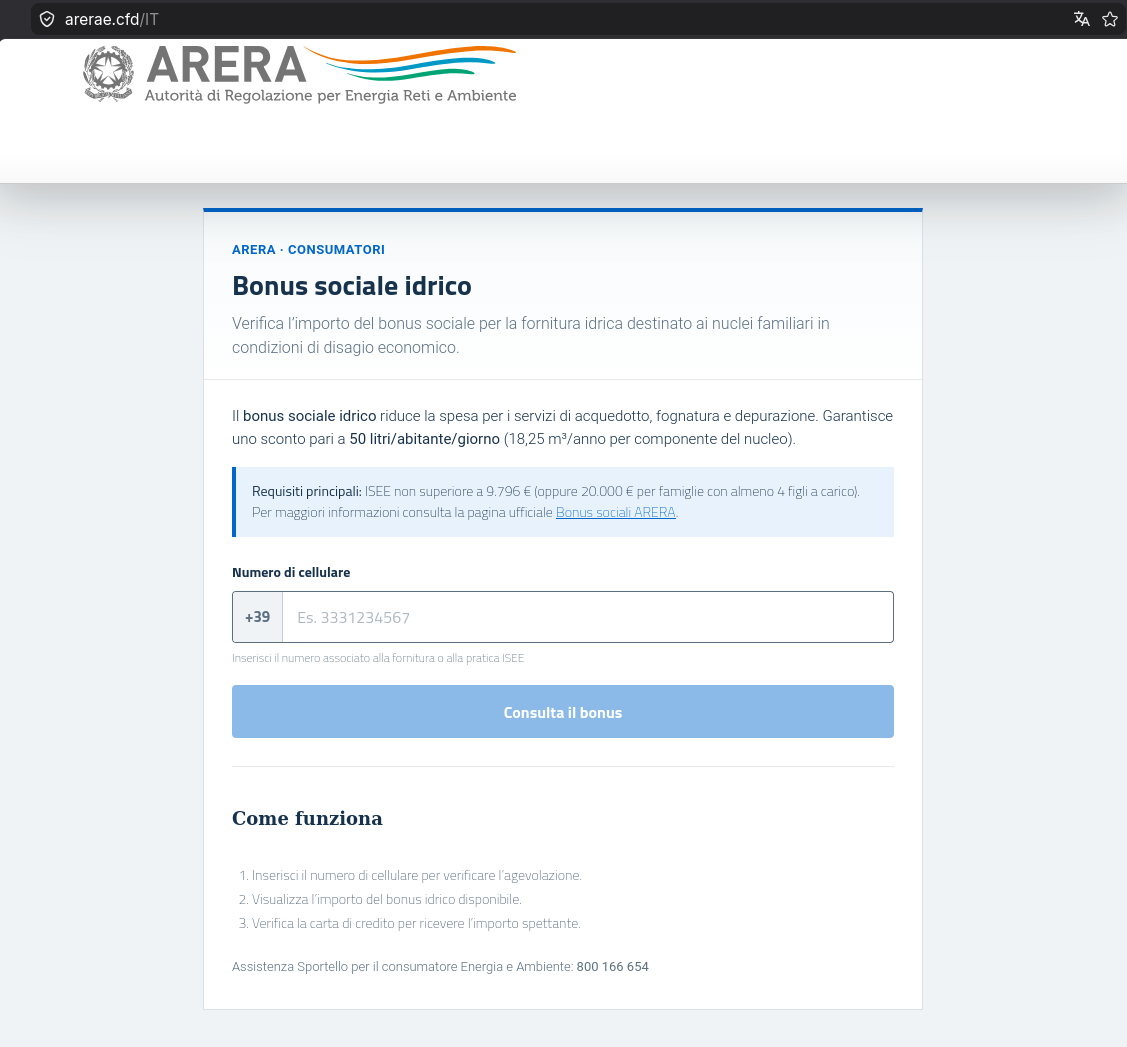
CERT-AGID identified and disrupted a fraudulent website impersonating ARERA to trick users into revealing personal and financial data through a fake refund tied to the social water bonus. The site used typosquatting and a staged flow that led victims from a phone-number check to a bogus credit card verification page. #ARERA #CERT-AGID #bonussocialeidrico
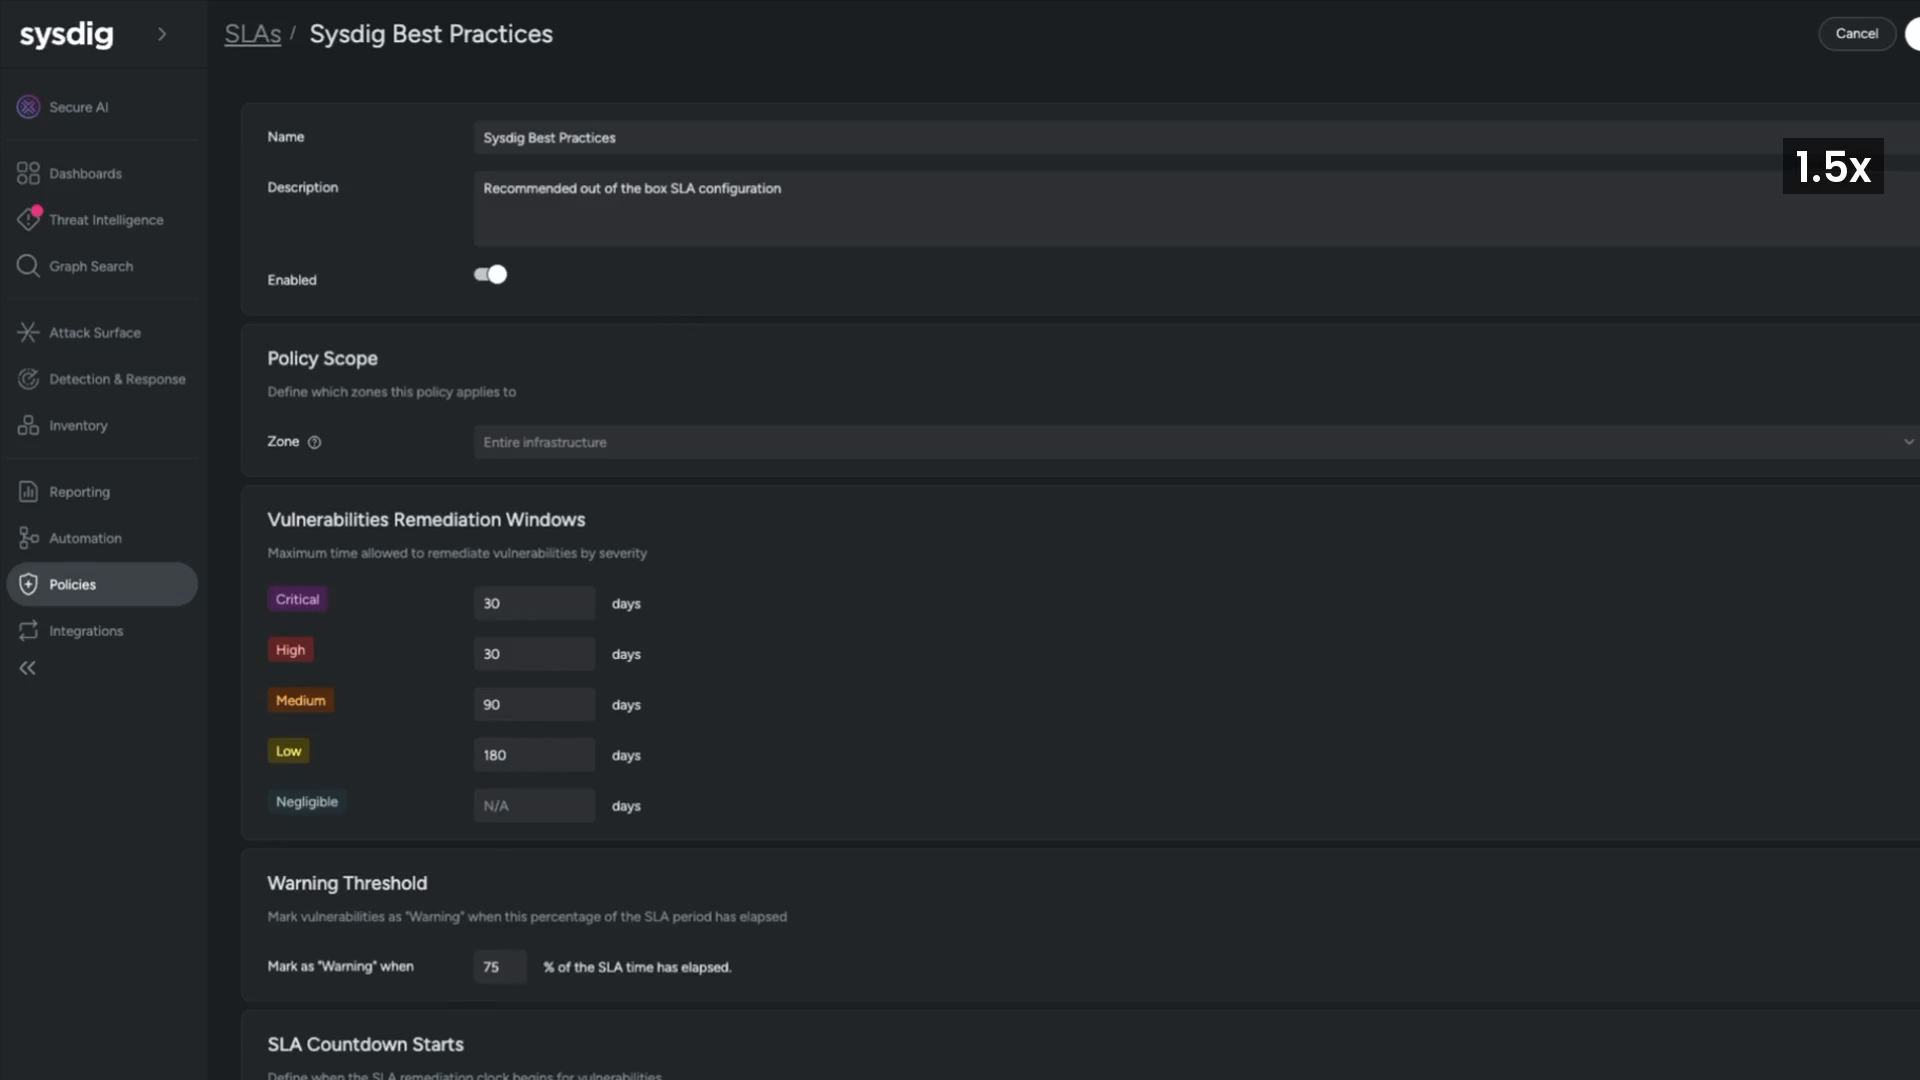
Sysdig Secure AI uses agentic cloud security to continuously triage vulnerability backlogs, trace 2,731 SLA-breaching findings in a Node.js base image to one fix, and route the remediation through human approval into Jira ticket DEJI-342. The same capability also runs headless in Claude via the Sysdig MCP server, using runtime data to prioritize issues by exploitability, KEV status, and reachability. #SysdigSecureAI #Jira #Claude #SysdigMCPServer #DEJI342
Hackers used a SQL injection flaw in a public-facing Java application to implant the khunt toolkit directly inside an Oracle database and then execute commands on a Windows server with SYSTEM privileges. Huntress linked the attack to IP address 178.162.151[.]229 and recommended stricter input validation and lower database permissions for internet-facing applications. #Oracle #khunt #Huntress
Connor Riley Moucka pleaded guilty for helping steal data from Snowflake customer accounts and extort victims after accessing accounts that lacked multi-factor authentication. The attacks affected more than 100 million people and targeted organizations including AT&T, Ticketmaster, Santander, Pure Storage, and Neiman Marcus. #Snowflake #ConnorRileyMoucka #JohnErinBinns #AT&T #Ticketmaster #Santander #PureStorage #NeimanMarcus

OpenAI disrupted a Cambodia-based scam network operating from Poipet that used ChatGPT to support investment, romance, gambling, and law enforcement impersonation frauds. The operation relied on fake personas, translated messaging, forged documents, and AI-assisted administration to target hundreds of victims across multiple schemes. #OpenAI #ChatGPT #Poipet #WhatsApp #Telegram…

Microsoft tracked a macOS ClickFix operation across more than 250 front-end domains that uses server-side fingerprinting to hide the lure from crawlers and sandboxes while serving targeted Mac users a fake software download. The attack chain leads to Atomic Stealer (AMOS) and sometimes MacSync, and it still depends on the victim…
Researchers from Microsoft and Mobile Hacking Lab chained multiple Samsung flaws to remotely compromise Galaxy devices through Bixby, Samsung Members, and Samsung Account. Samsung later patched the issues after the Pwn2Own Ireland demo, but older devices may still be at risk if the affected apps are installed. #Bixby #SamsungMembers #SamsungAccount #CVE-2025-21079…

This article demonstrates a full attack chain using impacket-reg against a Windows Server 2019 domain controller, covering remote registry authentication, enumeration, credential harvesting, RDP enablement, persistence, and reverse shell execution. It also explains defensive measures for limiting RemoteRegistry abuse, protecting registry hives, and detecting malicious registry changes and outbound callbacks. #Impacket-reg #RemoteRegistry #WindowsServer2019 #DomainController #Evil-WinRM #Msfvenom #Pypykatz #SAM #SYSTEM #SECURITY

Threat actor clop targeted ecc*******, encrypting and exfiltrating data associated with [CVE‑2026‑12569], including DBF, Cad-files, Project, Soft, and Backups. #
The ransomware campaign attributed to the Clop threat actor targeted ipm*******, with affected files reportedly including PDF documents and CAD files, as well as other sensitive software-related data. Data exfiltration was claimed in connection with CVE‑2026‑12569, with impacted country(s) #UnknownCountry
The ransomware claim attributed to Clop involves nuv******* with data exfiltrated including Project and Soft, exploiting CVE‑2026‑12569. #

A forum user known as 2019 allegedly leaked a Waggle customer database containing data on more than 106,800 pet camera customers across three tables. The exposed information includes contact, billing, and review records, but the claim remains unverified. #Waggle #2019…
A user posting as kitta allegedly released the database of Ramp4u, a Russian-language cybercrime forum, exposing 7,709 users along with private messages, posts, threads, and 340,333 IP log entries. The claim is unverified, but the leak could help investigators correlate forum identities and activities, especially through IP logs and reused email…
An actor claiming to be exfilar says Qara’s backend was publicly readable and writable without authentication, allowing live changes to a Saint-Gobain app deployment and exposing data tied to multiple tenants. The alleged leak also includes session tokens, plaintext employee passwords, and records connected to a Saudi government health and safety…