Platinum Group in Singapore was targeted by the play threat actor in a ransomware attack. The incident impacted Singapore #Singapore

GCATS Investments in the United States reported a ransomware attack attributed to the play threat actor. The incident involved unauthorized access and data encryption leading to disruption of operations, with the impacted country being #UnitedStates
play ransomware claim against Signature Services indicates an attack that likely involved encrypting files and demanding a ransom for decryption. The impacted country(s): #UnitedStates
Maksim Silnikau was sentenced to 16 years in prison for creating and running Ransom Cartel, a ransomware operation that targeted at least 18 companies and tried to extort $5.2 million. His arrest in Poland and extradition to the United States ended the group’s activity after attacks on law firms, medical technology firms, schools, and multinational corporations. #RansomCartel #MaksimSilnikau #DirectConnection

A new Forescout scan found more than 4,000 Rockwell Automation and Allen-Bradley controllers exposed on the internet, with 22 still visible in cities affected by recent attacks on U.S. water systems. The research highlights ongoing risks from public-facing EtherNet/IP devices, stale remote-access services, and possible exposure to CVE-2017-16740 on some MicroLogix 1400 systems. #RockwellAutomation #AllenBradley #MicroLogix1400 #CVE-2017-16740
Senators from both parties pressed Trump administration officials on whether U.S. agencies and foreign partners are coordinated enough to combat transnational scam centers. Witnesses said the administration is moving toward a whole-of-government and international task force approach, with progress varying by country, especially in Cambodia, Burma, and Laos. #SCAMAct #Interpol #JointInteragencyTaskForceSouth #Cambodia #Burma #Laos
Switzerland’s federal IT office says attackers breached its Microsoft SharePoint servers by exploiting a vulnerability and compromised about 200 accounts. BIT responded by blocking external SharePoint access, patching the suspected flaws, resetting passwords, and investigating the incident with the Swiss Federal Office for Cyber Security and Microsoft. #SharePoint #BIT #Microsoft
A wave of vishing attacks against hedge funds and private-equity firms has been attributed to UNC6671, a group linked to the BlackFile extortion campaign. The attackers used help-desk impersonation and cloud phishing to steal credentials, access Microsoft 365 and Okta accounts, and extort organizations including Point72, Two Sigma, Millennium, and Citadel. #UNC6671 #BlackFile #Point72 #TwoSigma #Millennium #Citadel #Okta #Microsoft365
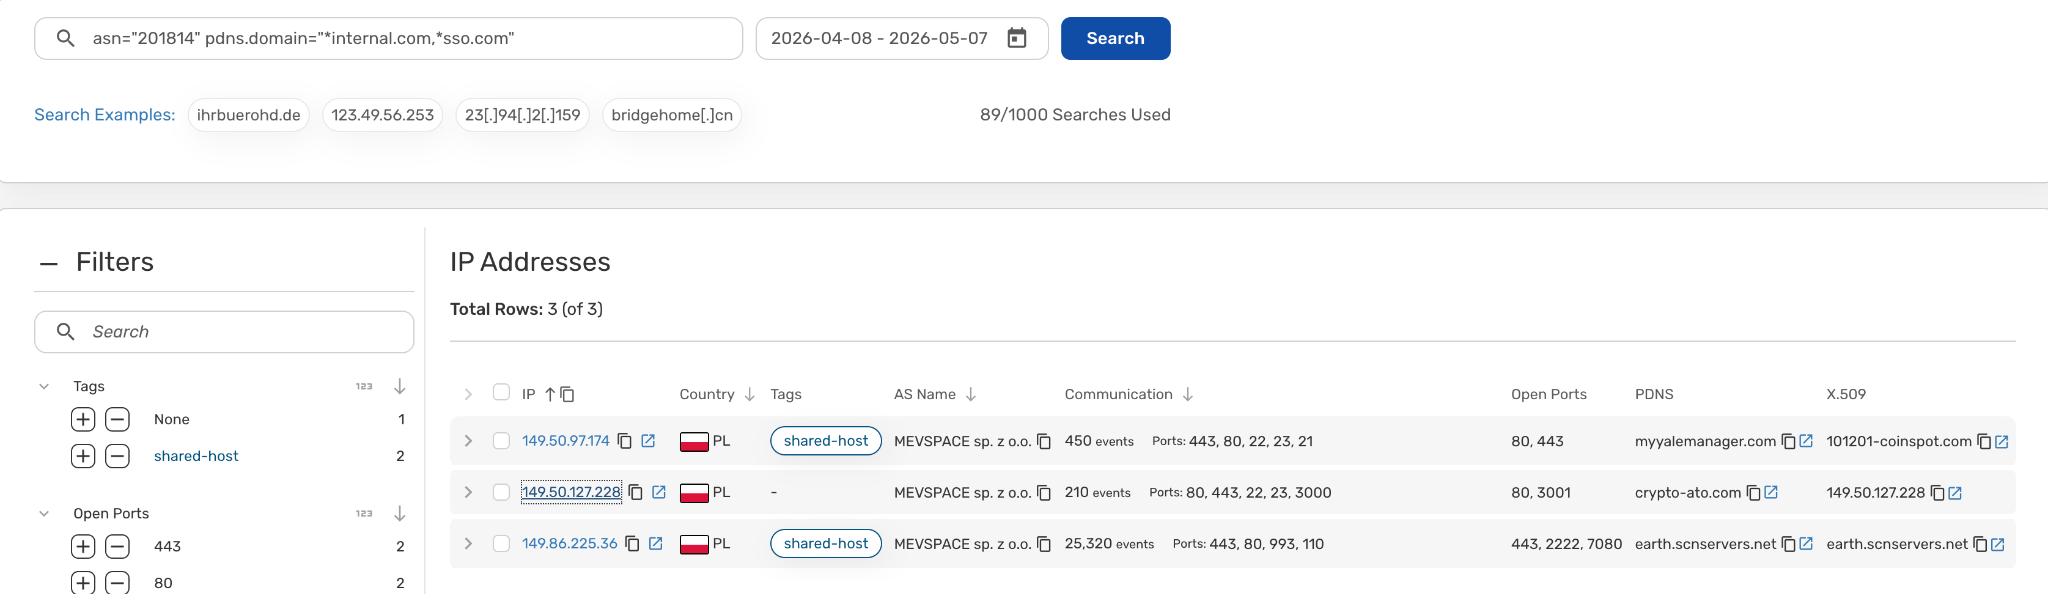
Team Cymru validated active Cluster A phishing infrastructure linked to Push Security’s research on ShinyHunters and BlackFile, confirming Mevspace-hosted domains, a Doko-branded artifact, and recurring victim-themed naming patterns. The analysis surfaced more than 40 additional domains and highlighted how phishing panels are built from hosted infrastructure, certificates, exposed services, and reusable…

MIT CSAIL researchers Daniël Trujillo and Mengjia Yan discovered INTERRUPT INJECTION, a technique that can time Linux interrupts to slip between branch predictor sanitization and kernel use, enabling speculative execution leakage. They demonstrated arbitrary kernel memory disclosure on AMD Zen 2 and showed the issue affects AMD’s Safe RET mitigation on…

Cisco has released fixes for multiple critical vulnerabilities in Catalyst SD-WAN and IOS XE Software, discovered during internal testing and not known to be actively exploited. It also addressed a high-severity flaw in the Integrated Management Controller, while separately warning about active exploitation of CVE-2026-20316 in Cisco Secure Firewall Management Center….

Zapscape is a Linux KVM/x86 shadow-MMU vulnerability, tracked as CVE-2026-64561, that can let an attacker with kernel-level privileges inside an L1 guest VM escape to the host and run code as root. The issue affects systems with nested virtualization exposed to untrusted guests, and the upstream fix has already been merged…
www.talbotdes.org in the United Kingdom was targeted by the lynx ransomware group, disrupting Talbot County Department of Emergency Services’ essential 9-1-1 communications, emergency medical services, and emergency management operations. The attack impacted public safety preparedness and services for residents, first responders, and local businesses supporting community alerts and CPR resources. #UnitedKingdom
In a ransomware attack attributed to threat actor lynx, www.jerryleigh.com, a family-owned women’s, men’s, and children’s clothing manufacturer and brand management headquartered in Panorama City, California, was targeted, disrupting access to its systems and data. The incident impacted #UnitedStates
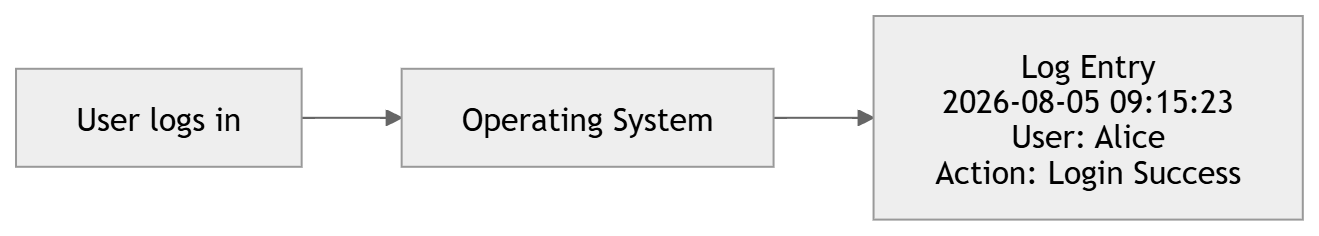
A SIEM helps security teams analyze and correlate logs from many sources to detect suspicious activity that would be hard to spot in individual events. The article explains that log management is not the same as SIEM, and that tuning, false positives, and human analysts are essential for effective detection. #SIEM #SecurityPlus #CISSP