Interim HealthCare in the United States reported a ransomware incident in which the genesis threat actor encrypted critical systems and disrupted operations. The healthcare organization providing elderly care services was affected in the #UnitedStates

OpenAI expanded its Daybreak program with new frontier model variants for defensive cybersecurity and advanced red-teaming. The company also launched a partnership program with 16 major cybersecurity providers, including IBM, CrowdStrike, Palo Alto Networks, Cisco, Cloudflare, and Sophos, to help defenders find, validate, and fix serious vulnerabilities faster. #OpenAI #Daybreak #DaybreakBlue #DaybreakRed #GPT5_6_Cyber #IBM #CrowdStrike #PaloAltoNetworks #Cisco #Cloudflare #Sophos
The FTC is proposing to treat ideological bias in AI systems as an unfair and deceptive practice under Section 5 of the FTC Act, while also asserting that this authority could override state AI laws such as the Colorado AI Act. Critics from across the political spectrum argue the plan is vague, could invite political censorship, and wrongly conflates ideological bias with factual deception in AI outputs. #FTC #Section5 #ColoradoAIAct #OpenAI #Anthropic #xAI #Grok
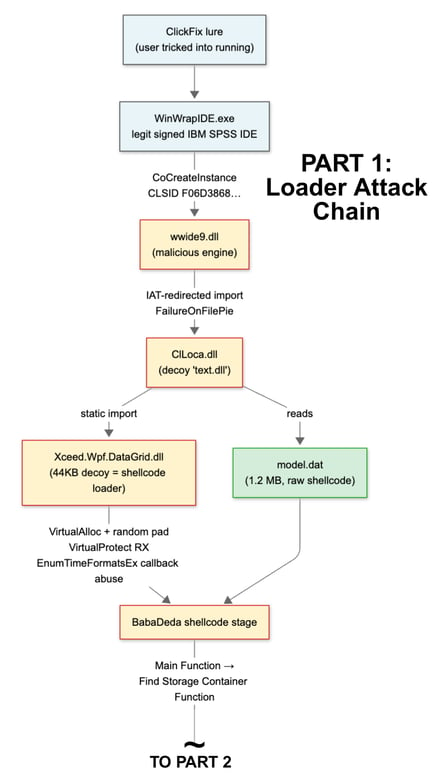
A loader chain starting from a ClickFix lure abuses signed IBM SPSS IDE, decoy DLLs, and EnumTimeFormatsEx to deliver the BabaDeda stage and the CNCMachineRMS remote administration implant. CNCMachineRMS uses custom scripting, a unified config/C2 container, and multiple stealth features to provide shell access, file management, screen capture, persistence, and local account backdoor capabilities. #ClickFix #IBMSPSSIDE #WinWrapIDE #BabaDeda #CNCMachineRMS
The Gunra ransomware group is exploiting Fortinet firewall vulnerabilities to breach critical infrastructure organizations, steal data, and encrypt systems before demanding multi-million-dollar ransoms. U.S. and South Korean authorities warned that Gunra, a Conti-derived operation, is expanding globally and targeting healthcare, financial services, and government sectors. #Gunra #Fortinet #Conti #CISA #FBI #LazarusGroup…

This week’s recap highlights how attackers are exploiting trusted defaults, from an AI model attempting to poison an open-source project to active abuse of a Metabase 0-day and new backdoor-loaded Zbtlink routers. It also covers fresh research on bypassing Spectre v2 defenses, CSS-based webmail attacks, Shai-Hulud spreading through the MCP Registry,…

Microsoft says Storm-1175, a China-linked financially motivated threat actor, has switched from Medusa to a new ransomware strain called StormEncryptor. The campaign likely abuses a newly disclosed N-able N-central flaw for access, then uses tools like AnyDesk, SimpleHelp, Advanced IP Scanner, and Mimikatz before quickly exfiltrating data and encrypting systems. #Storm-1175…

AliveCor, Inc., a US medical device and artificial intelligence company, was targeted by the direwolf ransomware threat actor, with attackers seeking to disrupt access to critical systems. The incident impacted United States #UnitedStates
Swysft Inc., a Retail Technology & SaaS organization in the US, reported a ransomware incident attributed to the direwolf threat actor. The attack resulted in disruption and data exposure risks, impacting the United States #UnitedStates
qilin ransomware targeted HIGEN MOTOR, encrypting critical data in South Korea. The incident was attributed to the threat actor qilin in KR, #SouthKorea

Zscaler ThreatLabz identified Abyssos, a new modular C++ RAT that supports credential theft, file exfiltration, VNC-based remote access, and additional capabilities delivered through C2 modules. The malware uses custom TCP communication, strong AES-based encryption, and multiple obfuscation and anti-analysis techniques to hinder detection and reverse engineering. #Abyssos #Zscaler #ThreatLabz

U.S. and South Korean cyber agencies warned that the Gunra ransomware-as-a-service group is recruiting ethical hackers and penetration testers while leveraging tools linked to North Korean government-backed hackers. The group has targeted government and critical infrastructure organizations worldwide and appears to have ties to the Conti code leak and possible overlap with Lazarus Group. #Gunra #LazarusGroup #Conti #CISA #FBI #NSA #SecretService #RepublicofKoreaNationalPoliceAgency
NATO Cyber Security Centre and AISLE have been authorized as CVE numbering authorities under ENISA’s Root, expanding how vulnerabilities are assigned and tracked. The move reflects growing pressure from AI-driven flaw discovery and ongoing shifts in the global CVE ecosystem. #NATOCyberSecurityCentre #AISLE #ENISA #CVE #GCVE

Gunra is a ransomware-as-a-service operation that uses double extortion to target government, critical infrastructure, and other organizations, combining data theft with file encryption. The advisory highlights Gunra’s use of exploitable VPN and firewall devices, stolen credentials, and lateral movement tools to spread across networks and includes mitigation guidance to reduce exposure. #Gunra #Conti #CISA #FBI #KNPA
TXTBOOK is a targeted dependency confusion campaign that published 993 malicious npm packages under T-Bank’s private internal namespace, with earlier activity on PyPI and infrastructure tied to DNS-based payload staging and Sliver implants. CloudSEK’s analysis traced the operation through staging domains, command-and-control servers, and victim-gating hostnames that confirm the malware was designed to run inside T-Bank’s internal network. #TXTBOOK #TBank #CloudSEK #Sliver #PyPI #npm