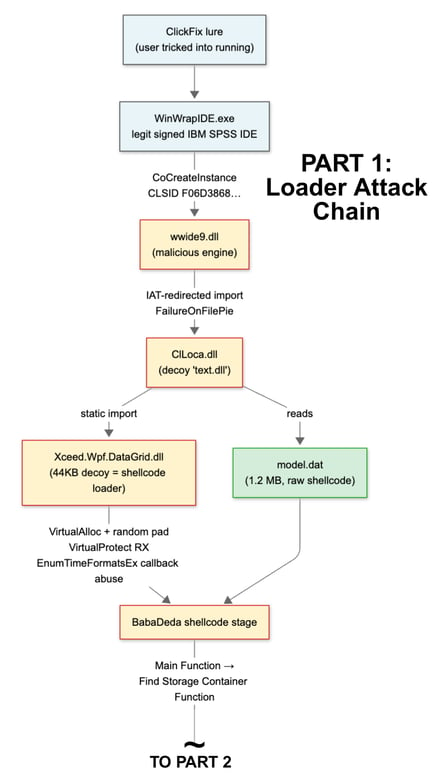
A loader chain starting from a ClickFix lure abuses signed IBM SPSS IDE, decoy DLLs, and EnumTimeFormatsEx to deliver the BabaDeda stage and the CNCMachineRMS remote administration implant. CNCMachineRMS uses custom scripting, a unified config/C2 container, and multiple stealth features to provide shell access, file management, screen capture, persistence, and local account backdoor capabilities. #ClickFix #IBMSPSSIDE #WinWrapIDE #BabaDeda #CNCMachineRMS
Keypoints
- The infection starts with a ClickFix lure and eventually launches the legitimately signed IBM SPSS IDE binary, WinWrapIDE.exe.
- A chain of four decoy DLLs is used to reach shellcode without suspicious direct API calls or obvious loading behavior.
- The final decoy uses EnumTimeFormatsEx as a benign trampoline to execute shellcode indirectly.
- The shellcode stage, called BabaDeda, depends on a separate obfuscated config file named HelperStandardizationApplication.bin.
- The embedded payload is CNCMachineRMS, a 1.14 MB x64 implant built for remote administration rather than simple payload delivery.
- CNCMachineRMS includes interactive shell access, file management, screen capture, local account backdoor creation, seven persistence mechanisms, and 20 typed commands.
- The malware uses its own scripting language and a shared serialized container format for config, local state, and C2 traffic, with the campaign associated with “novm.”
MITRE Techniques
- [T1218.009 ] Signed Binary Proxy Execution: WinRAR/Self-Extracting Archives – Abusing a legitimately signed IBM SPSS IDE binary to activate the attack chain (‘a legitimately signed IBM SPSS IDE, WinWrapIDE.exe, is launched’).
- [T1055 ] Process Injection – Shellcode is written into memory and executed in-process through a benign callback path (‘writes shellcode into the middle of it, and marks it executable’).
- [T1202 ] Indirect Command Execution – The malware is triggered through EnumTimeFormatsEx instead of a direct malicious call path (‘Windows calls the malware on the attacker’s behalf’).
- [T1027 ] Obfuscated Files or Information – The config, state database, and payload use layered obfuscation and high-entropy random-looking data (‘looks like an encrypted blob’, ‘under two layers of obfuscation’).
- [T1027.002 ] Software Packing – The embedded payload and config are concealed in packed/serialized containers rather than plain binary structures (‘the config and its command and control (C2) traffic travel in the same custom binary container’).
- [T1059 ] Command and Scripting Interpreter – The implant runs behavior through its own custom scripting language (‘driven by a custom scripting language the author wrote’).
- [T1105 ] Ingress Tool Transfer – The operator can stage and run additional payloads through typed commands (‘twenty typed commands for pulling down and running further payloads’).
- [T1068 ] Exploitation for Privilege Escalation – The implant creates local accounts and adds them to privileged groups (‘It creates local accounts and adds them to privileged groups’).
- [T1547.001 ] Registry Run Keys / Startup Folder – Persistence via a Run key is explicitly described (‘A Run key or scheduled task named IBM SPSS WinWrap Basic IDE’).
- [T1053.005 ] Scheduled Task/Job: Scheduled Task – Persistence is also established with scheduled tasks (‘Scheduled tasks created with /SC ONLOGON /RU SYSTEM /F /RL HIGHEST’).
- [T1010 ] Application Window Discovery – A screenshot is taken on first contact, indicating host interaction and reconnaissance (‘It takes a screenshot on first contact’).
- [T1087.001 ] Account Discovery: Local Account – The host profile and backdoor actions involve local account context (‘Domain, SID, and elevation status’, ‘Creates local accounts’).
Indicators of Compromise
- [Domain / IP] C2 and network beaconing – Notepadreleased[.]com, 85[.]158.110.78
- [DNS-over-HTTPS endpoints] DNS resolution path used by the implant – dns.google, cloudflare-dns.com, dns.quad9.net
- [File path] Task payload dropped under TEMP – %TEMP%CNCMachineRMStasks*task_payload.bin
- [File path] Local state database – %LOCALAPPDATA%SProjectsp.bin
- [File path] VM check trigger artifact – C:Intel directory
- [Registry / task name] Persistence artifact – IBM SPSS WinWrap Basic IDE
- [Windows Event IDs] Local account backdoor activity – 4720, 4732
- [SHA256] Signed loader and DLLs – 0562c588997fa9961d55c6ab1db2656344324bca8db9ea7b64fe309132b2399f, 5b71b49bad415643ff3e291ee3ba550e5edfd584eb913859dadb81634450e7e7
- [SHA256] Additional payload components – 3d4e7187f74de912f9d52f5ba6a95bd41868348b16583d72957d732c0ed8f0e7, b804b9dd2726e69fb4f496a6872f90edf9146ad8044c6d3a592040ce1074a5d0, and other 5 hashes
- [SHA256] Memory-only stages – 744b8165b6161cbd1d5ecc423ecfdb8306485afdc80262000ab3c6908881ef9e, bb81786286be437b3ec6d562055767097c9277054e1d09172caa96376451481c