The ransomware claim targets FREYWILLE in Austria, allegedly by the aurora threat actor, compromising 142+ employee files including salary statements, social security numbers (ELDA), employment contracts across 24 countries, and identity and benefits documentation. It also claims theft of FREYWILLE trade secrets such as 2025 product costing data and enamel color recipe formulations, plus legal and incident records tied to lawsuits and prior attacks affecting #Austria.

Leafwell, a US healthcare provider, reported a ransomware incident involving Hospitals & Physicians Clinics attributed to the direwolf threat actor. The attack impacted healthcare operations and data access, affecting the United States #UnitedStates

Cybersecurity researchers uncovered a supply chain compromise at BdThemes that poisoned remote JSON data used by several WordPress plugins, leading WordPress to temporarily disable downloads pending review. The attack leveraged the Biggopti component to trigger XSS in wp-admin, enabling rogue administrator creation, web shell deployment, and persistent backdoor access. #BdThemes #WordPress…
Mozilla issued a new GPG signing subkey for some Firefox and Thunderbird artifacts after the previous key was accidentally exposed in a private GitHub repository. The company revoked the exposed key, found no evidence of unauthorized access, and said most users do not need to take action unless they manually verify…
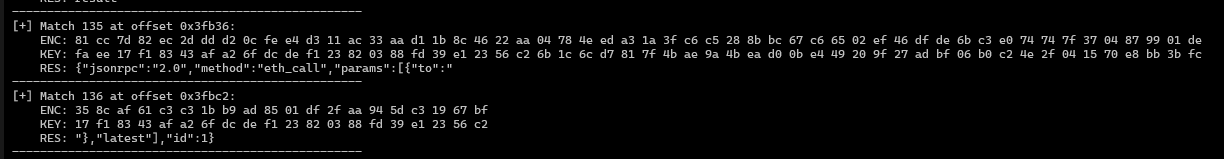
Aeternum is a C++ botnet loader that moves command-and-control operations onto the Polygon blockchain, using smart contracts and RPC queries to retrieve encrypted or plaintext instructions. The investigation also links Aeternum to a Telegram-based Python malware family and a blended payload set involving XWorm RAT and the XMRig miner, while highlighting…

An actor using the name GordonFreeman claims to be selling a 15.7GB database from RENAPER, Argentina’s national identity registry, allegedly containing 48 million citizen records. The sample reportedly includes DNI numbers, home addresses, phone numbers, and even children’s data, but the claim remains unverified. #RENAPER #GordonFreeman #Argentina #DNI…
Genesis ransomware impacted Interim HealthCare (Oklahoma and Tulsa), disrupting operations for an elderly care services provider in the United States. The attack highlights the risks facing healthcare organizations and their patients while services remain under strain. #UnitedStates
Genesis ransomware targeted Consolidated Medical Practices of Memphis, a healthcare organization in the US, causing disruption to critical medical operations. The impacted country is #UnitedStates
Deadlock ransomware activity targeted LT Group / Fortune Tobacco Corp in the Philippines (PH), where 14,836 files totaling 27 GB were allegedly compromised after the victim ignored extortion messages for 72 hours. The attackers leaked samples including passport (MRZ) data, PNB/Holco USD bank statements, BIR/eFPS credentials, and promissory notes tied to Eton Properties (PHP 2.53B debt), with the impact disclosed as “Full leak: August 18.” #Philippines
OpenAI has introduced GPT 5.6 Cyber, a specialized model for vulnerability research, penetration testing, and incident response, but it is only available through selected partners and security vendors. The company is offering Daybreak Blue and Daybreak Red through its Daybreak Access program to help defenders find, validate, and fix serious security flaws faster. #OpenAI #GPT56Cyber #DaybreakAccess
A threat actor compromised BdThemes’ upstream infrastructure and poisoned a remote JSON feed, using the attack to create rogue administrator accounts on WordPress sites. The incident affected several BdThemes plugins, including Element Pack, and has been linked by researchers to a broader supply-chain campaign. #BdThemes #ElementPack #Wordfence #Sigmative #Biggop Library
Hackers used a private APN and a compromised FortiGate/VPN path to move laterally into a second CHP plant in Poland, where they shut down a steam turbine and process-water treatment system. CERT Polska says this was the first known real-world cyberattack to enter an OT network through a private APN, and it recommends treating such networks as untrusted and enforcing client isolation and strict access controls. #CERTPolska #FortiGate #WAGO #Teltonika #Siemens #Moxa #Electrum
Lucid Stealer is a Node.js SEA-based information-stealing malware that hides its payload with encryption, obfuscation, false certificate-like data, and UAC bypass behavior while collecting browser credentials, wallet data, Discord tokens, screenshots, and keystrokes. It uses PowerShell, a malicious Node.js native module, and WebSocket/HTTP POST communication to contact lucidstealer[.]one, with the analysis also noting shared infrastructure containing AsyncRAT and promotion through a Telegram channel. #LucidStealer #Nodejs #AsyncRAT #Telegram
Cleaver-Brooks in the US reported a major data breach at a leading industrial manufacturer attributed to the anubis ransomware threat actor. The incident involved unauthorized access and encryption demands that resulted in significant data exposure. #UnitedStates
BigSpark, in AI, was targeted by the direwolf ransomware group, disrupting Business Services through unauthorized encryption and extortion. The incident impacted AI #AI