The Cybersecurity Pulse recaps a busy week of agent security research, including OpenAI’s Black Hat reconstruction, Hugging Face exploitation chains, North Korea-linked C2 investigations, and new findings on HTTP Terminator, ChainDrop, and NOVA. It also highlights major product launches and funding across agent controls, runtime security, and autonomous pentesting, with notable developments from Varonis, Corma, Opnova, Horizon3.ai, and others. #OpenAI #HuggingFace #NorthKorea #HTTPTerminator #ChainDrop #NOVA #Varonis #Corma #Opnova #Horizon3ai
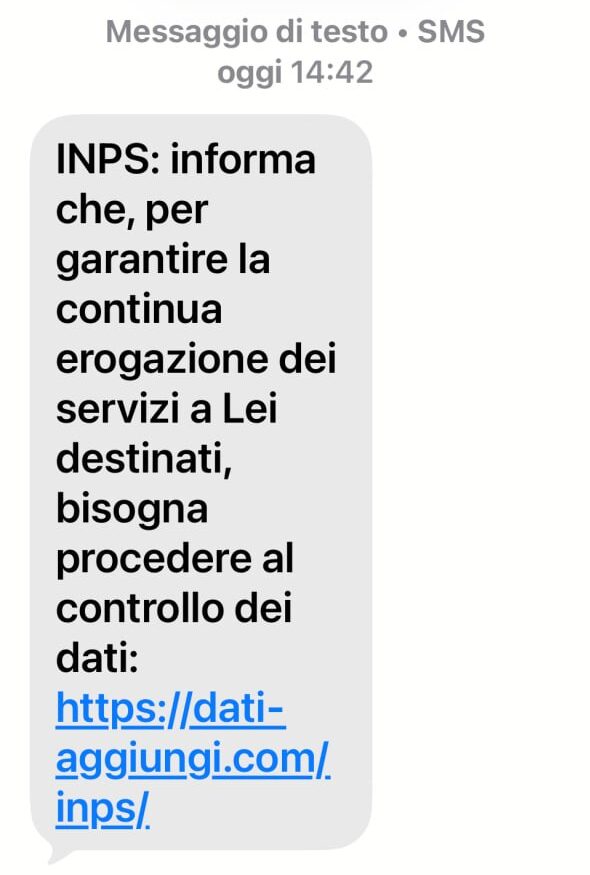
CERT-AGID observed a phishing campaign abusing the INPS name, logo, and visual identity to lure victims to a fake site that collects personal documents and photos. The fraudulent portal also uses an AI-based file validation step, reportedly identified as Gemini 1.5 PRO, to filter uploads and increase the quality of stolen data. #INPS #CERT-AGID #Gemini1.5PRO

Researchers uncovered Kimwolf v7, a new version of the Kimwolf/AISURU Android and IoT botnet that adds browser-like HTTP/2 DDoS flooding and more resilient command-and-control infrastructure. The malware now relies on Ethereum Name Service, a hard-coded Tor hidden service, and a local proxy while shifting propagation duties to an external loader and…

Microsoft’s latest Patch Tuesday fixes an actively exploited Windows kernel driver flaw, CVE-2026-68820, which can let an attacker escalate to SYSTEM. It also closes four unauthenticated 9.8-rated remote code execution bugs in Windows DNS Server, Windows Deployment Services, Microsoft QUIC, and HPC Pack, plus the remaining half of a SharePoint attack…
Microsoft released fixes for 421 CVEs in its August 2026 Patch Tuesday, including CVE-2026-68820, a zero-day in afd.sys that attackers are using to gain SYSTEM privileges. The update also addresses several publicly disclosed local privilege escalation and remote code execution issues across Windows, Exchange Server, and other Microsoft products. #CVE-2026-68820 #afd.sys…
Delta Airlines is investigating a Monday flight incident in which a passenger allegedly used an unidentified device to spoof the airline’s in-flight Wi-Fi network, causing major delays. Authorities and federal agencies are aware of the case, which resembles an evil twin attack and comes amid reports of similar Wi-Fi deauthentication attacks at DEF CON. #DeltaAirlines #DEFCON #FBI #FAA

Kaspersky reported a July 2026 Head Mare campaign that abused two TrueConf Server vulnerabilities to gain SYSTEM-level code execution, deploy a web shell, and replace legitimate client installers with infected versions carrying PhantomCore and PhantomGraph. The attackers used Microsoft OneDrive as C2 for one backdoor, installed persistence through registry and Windows services, and targeted Russian organizations across multiple industries. #TrueConf #HeadMare #PhantomCore #PhantomGraph
Delta Air Lines is investigating an unauthorized Wi-Fi network that appeared briefly aboard Flight 591 from Las Vegas to Atlanta, reportedly linked to passengers who had attended DEF CON 34. The incident did not affect flight safety, and Delta said it will work with federal law enforcement and aviation regulators to investigate the event. #DeltaAirLines #DEFCON34 #Flight591
Cisco says CVE-2026-20349 is a high-severity flaw in Secure Firewall ASA and FTD software that is being actively exploited to remotely crash affected devices. The issue affects certain VPN and remote access configurations, has no workaround, and requires upgrading to a fixed release; Cisco has also released hot fixes for multiple ASA and FTD versions. #Cisco #CVE-2026-20349 #SecureFirewallASA #SecureFirewallFTD

The US-based company powdr.com was reportedly hit by ransomware attributed to the settra threat actor, with the “Point of No Return” described as “What the Ski Empire Is Hiding.” #UnitedStates
Xpress Tech, a B2B iGaming aggregation platform, was targeted by the Panzer ransomware threat actor, disrupting operations across its Remote API integration, payment solutions, and back-office data management capabilities. The attackers leveraged their access to compromise the platform and its connected gaming provider ecosystem, impacting #countryname
Orova ransomware targeted Ganzhou Xinye Art and Craft Co., Ltd., a HK-based craft gift production enterprise affiliated with Xinlin Group, established in 1997. The company’s ransomware-related disruption impacted operations in #HongKong

Bonifatius GmbH, a publishing company based in Paderborn, took several of its web pages offline for security reasons after a cyber incident. The company has not disclosed further details about the attack or any impact on its operations.
AI governance is becoming a CEO-level responsibility because internal policies, fragmented regulations, and evolving threats like deepfakes are moving faster than many organizations can respond. Leaders should build adaptive oversight now by improving risk visibility, flexible governance, and incident-response readiness instead of waiting for clearer rules. #AIgovernance #deepfakes #disinformation…
Zoom has released patches for four vulnerabilities across its products, including CVE-2026-53413, a severe zero-click RCE flaw in the annotator function that could let an attacker take over another participant’s machine. The updates also address CVE-2026-53414, CVE-2026-53415, and CVE-2026-53416, affecting Zoom Workplace, Rooms, Meeting SDK, and VDI components. #Zoom #CVE-2026-53413 #CVE-2026-53414…