MyDr is investigating a data incident affecting part of its systems and has activated its incident response procedures. The company is working with external experts, relevant authorities, and legal advisers to determine the scope and cause of the event. #MyDr

Twenty municipal organizations in Espírito Santo, Brazil, were affected by a cyberattack that took down their public portals, with the incident claimed by the BLCKORDER hacking group. While online services were disrupted, officials said critical infrastructure remained intact, and the attackers alleged data exfiltration that has not yet been confirmed. #BLCKORDER #ÁgapeConsultoria #EspíritoSanto
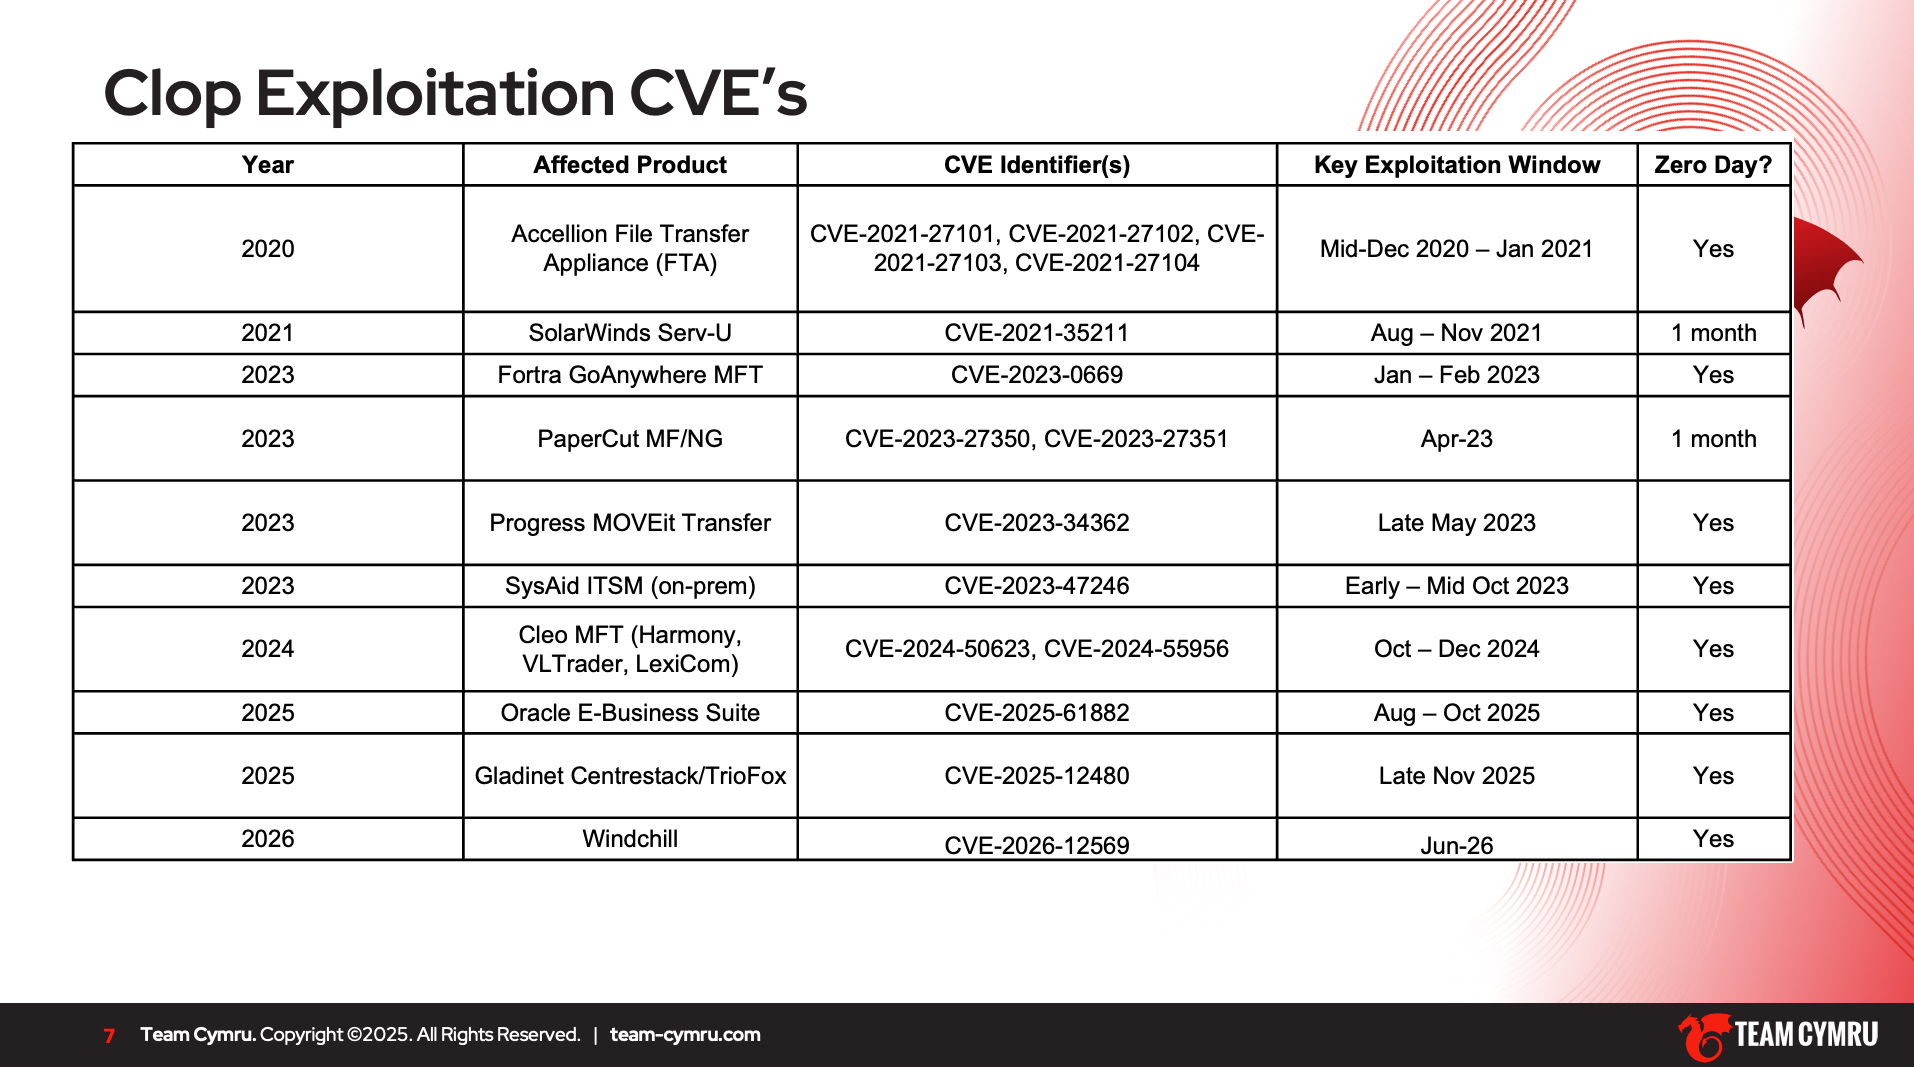
Cl0p has systematically targeted internet-facing managed file transfer and related enterprise applications, often using zero-day exploits, pre-attack reconnaissance, and reused infrastructure across campaigns such as MOVEit, Oracle E-Business Suite, and Centrestack. The report finds that Cl0p’s seasonal Q4 activity, long reconnaissance windows, and architectural weaknesses in MFT systems create strong defensive…
North Korean IT workers are using fake identities, AI-generated profiles, proxy addresses, and overseas facilitators to bypass hiring controls and gain legitimate access to corporate systems. Organizations can reduce this risk by combining government-issued document checks, biometric liveness detection, and stronger service-desk identity verification. #NorthKoreanITworkers #SpecopsSecureOnboarding #USDepartmentofState #FBI
The FBI warns that criminals are stealing sexually explicit images and videos from adults’ and children’s social media and online accounts to extort victims or sell the material on criminal marketplaces. The bureau also says student-athletes are being targeted in similar sexual exploitation schemes, and it urges stronger account security, multi-factor authentication, and caution with unsolicited reset or verification messages. #FBI #NCAA #sextortion
North Korean hackers linked to Lazarus are exploiting the Windows zero-day CVE-2026-68820 in the Operation Dream Job campaign to gain SYSTEM privileges on targeted systems. The attacks have focused on defense, aerospace, and aviation organizations, while also using the FudModule rootkit, the Troy backdoor, and the RelayShell web shell to expand access and evade defenses. #CVE-2026-68820 #Lazarus #OperationDreamJob #FudModule #Troy #RelayShell #Roundcube

Ransomware associated with the clop threat actor compromised ENTERATEK.MXESBERBEVERAGE.COM in Mexico, causing service disruption and threatening data exposure. The victim’s environment was impacted in Mexico #Mexico
The ransomware claim by clop targets the victim GATE7LLC.COMGBBEV.COM in the United Kingdom, alleging data compromise and extortion. #UnitedKingdom
In the US, threat actor clop claimed a ransomware attack involving AOL.com. AOL, an American web services and media company based in New York, had its operations impacted in the United States. #UnitedStates
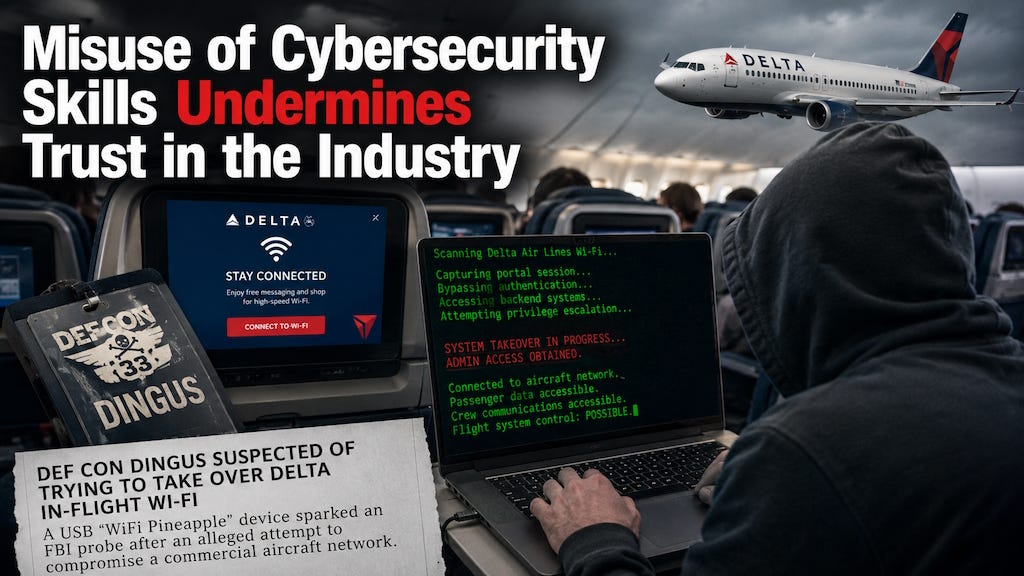
This article condemns an alleged prank in which DEF CON attendees may have used a de-authentication attack to interfere with Delta Flight 591’s onboard Wi‑Fi and collect passenger data. It argues that such behavior damages trust in the cybersecurity community and calls for accountability from Delta, the FAA, and DEF CON organizers. #DEFCON #Delta #DeltaFlight591 #FAA
Intel and AMD released patches for more than 80 vulnerabilities across a wide range of products, including processors, wireless software, and AI-related tools. The fixes address issues that could lead to privilege escalation, denial of service, information disclosure, private key disclosure, and arbitrary code execution. #Intel #AMD #PROSetWirelessWiFi #Xeon #Vitis #RyzenMasterUtility…
Ceva Logistics suffered a cyberattack that disrupted its European operations, affecting eight warehouses and delaying shipments for customers across the region. Several companies, including Bol, De Bijenkorf, ING, Ace & Tate, Ajax, and Valve, reported possible exposure of customer or delivery-related information. #CevaLogistics #Bol #DeBijenkorf #ING #AceandTate #Ajax #Valve #CoinbaseCartel…
WhatsApp is rolling out Scam Alert in limited beta, using on-device machine learning to flag suspicious messages from non-contacts while keeping all classification and reporting local to the device. Signal has also added automatic key verification to strengthen end-to-end encrypted chats by using key transparency and independent audits to detect unauthorized…
A legacy Entra ID WS-Trust autologon endpoint used for Seamless SSO can be abused to spray passwords past Smart Lockout, bypass normal sign-in logging, and reveal whether credentials are valid even when MFA or Conditional Access blocks the final sign-in. Microsoft has left this path available for older Office 2013 clients,…
Nightmare Eclipse has released ShieldBreak, a new Microsoft Defender zero-day exploit that bypasses the patched RoguePlanet flaw and can elevate attackers to SYSTEM privileges on fully patched Windows systems. The exploit has been independently confirmed and is part of an ongoing dispute with Microsoft over disclosure and bug bounty practices. #ShieldBreak #RoguePlanet #NightmareEclipse #MicrosoftDefender #Windows11 #WindowsServer