De Bernardus schools in Oudenaarde were hit by a cyberattack that led to the theft of data belonging to about 4,200 students and staff members. The stolen information included names, email addresses, national registry numbers, home addresses of teachers, and other student data. #Bernardusscholen #Oudenaarde

Indiana Area School District reported a cybersecurity incident that occurred on Sunday evening, but there is currently no indication that student, staff, or financial data managed by district systems was compromised. The district said it is continuing to assess the situation while no confirmed exposure of sensitive information has been identified. #IndianaAreaSchoolDistrict #RobertJHeinrichJr

LTM has launched BlueVerse AgenTraceIQ to help enterprises securely adopt and scale agentic AI by combining Rubrik Agent Cloud with AI governance and managed services. The offering adds monitoring, policy enforcement, and recovery capabilities for AI agents across platforms such as Microsoft Copilot Studio, Salesforce Agentforce, Amazon Bedrock, and Anthropic Claude. #Rubrik #LTM #BlueVerseAgenTraceIQ #ProjectHourglass #Claude
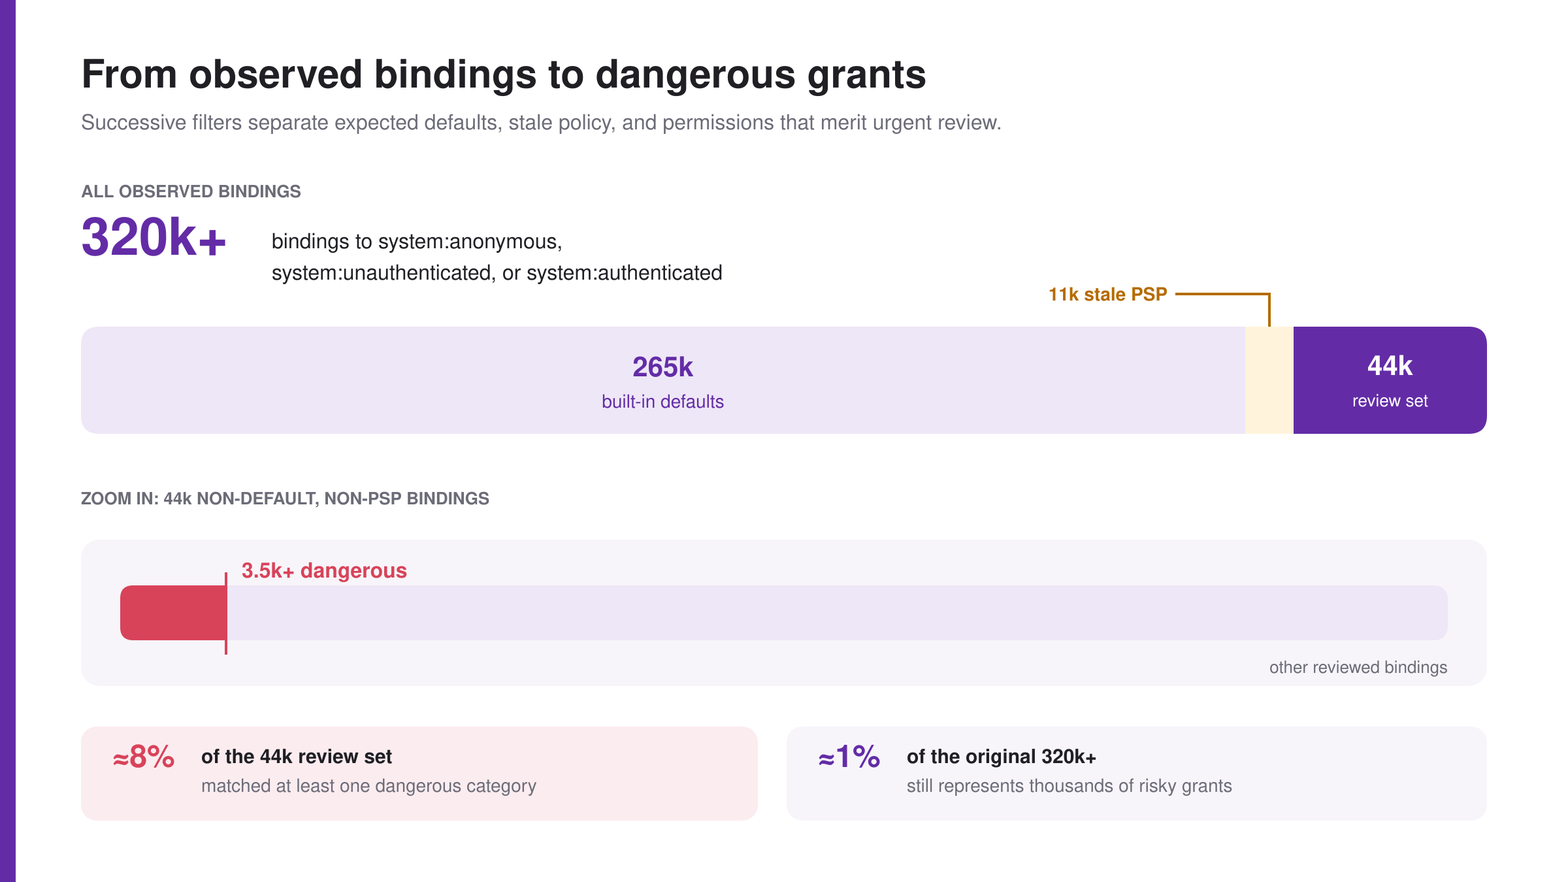
A large-scale study of more than 65,000 Kubernetes clusters found that built-in principals like system:anonymous and system:authenticated are still sometimes granted risky RBAC permissions. The findings highlight excessive and redundant bindings across AKS, EKS, and GKE, showing that many clusters could improve security by tightening authorization settings. #Kubernetes #AKS #EKS #GKE #RBAC
Italy’s Data Protection Authority (GPDP) fined IQVIA €7 million for data-processing practices that allegedly exposed and could have enabled the re-identification of roughly one million patients. The agency said IQVIA also processed health data without a proper legal basis, failed to inform patients, and kept records dating back to 2001 without adequate retention controls. #IQVIA #GPDP #GDPR

GitGuardian explains that every enterprise now relies on a sprawling credential layer across repositories, endpoints, collaboration tools, and AI agents, making discovery the foundation of security. It argues that detecting credentials with context such as validity, ownership, permissions, and dependencies is essential before remediation and prevention can work effectively. #GitGuardian #GitHub…

This week’s cyber news highlighted actively exploited flaws in Citrix NetScaler ADC, FortiMail, and PaperCut, alongside new abuse of weak defaults, exposed repos, and simple phishing paths. It also showed how groups like Star Blizzard, ShinyHunters, KillSec, and RatHat are combining automation, AI, and stealth to make attacks faster and harder…

Microsoft has issued out-of-band updates for CVE-2026-96940, a high-severity Microsoft Exchange Server flaw that could let an authenticated attacker escalate privileges and access other users’ mailboxes within the same organization. Exchange Online has already received a service-side fix, while on-premises users of affected Exchange Server versions should patch immediately; Microsoft also…
September’s security news highlighted social engineering against Revolut, rogue AI agent activity involving OpenAI research systems, and ShinyHunters-driven extortion and data theft campaigns. The month also exposed how both human operators and AI-assisted actors can move fast, evade detection, and exploit gaps between initial access and incident identification. #Revolut #OpenAI #ShinyHunters #FBI #OraclePeopleSoft #marimo

Global Secret Group ransomware claimed an attack on Turn5 (turn5.com), an automotive aftermarket/auto parts organization based in Pennsylvania (19301), resulting in the encryption of 328 GB across 26,503 files and 446 folders. The claim targets the United States, leaving impacted systems across #UnitedStates.
SilentRansomGroup extorted Sheppard, Mullin, Richter & Hampton in the US, offering $4.900.000 to prevent the publication of stolen data. The ransomware claim involved threats to release information unless the ransom was paid, impacting #UnitedStates
SilentRansomGroup reportedly targeted Nelson Mullins Riley & Scarborough in the US, demanding a $8,000,000 payment to keep sensitive data from being published. The claim centers on threats of data exposure unless the ransom was paid, impacting #UnitedStates

AI is accelerating software development and security review, but it can also produce code that looks secure while relying on flawed trust assumptions. A financial services penetration test showed how treating a GUID as proof of entitlement can expose sensitive customer data, highlighting the need for human judgment, threat modeling, and explicit security invariants in AI-assisted development. #Sygnia #ZachMead #GUID
A threat actor calling itself UWAYS and linked to Uways Qarani claims to have made a Saudi General Intelligence Presidency database available for download. The alleged leak reportedly includes officers’ names, phone numbers, home addresses, workplace details, case files, organizational charts, and global station records. #GeneralIntelligencePresidency #GIP #UWAYS #UwaysQarani…
A post attributed to the handle “nuevaeps” claims a leak of 29,018 Nueva EPS records tied to Vaupés, Colombia, with an additional 11 million records also alleged. The purported dataset is said to include personal, demographic, and health information such as names, IDs, contact details, medical history, and Indigenous-community-related fields. #NuevaEPS…