SilentRansomGroup attacked Troutman Pepper Locke in the US for the second time within a year, after gaining access via physical intrusion, and deployed ransomware to disrupt operations. The group stated it will continue its attacks, impacting #UnitedStates

A listing claims to sell a 452.29GB imaging backup from 301 Hospital, PLA General in Beijing, but the headline’s claim about a head of state scan is unverified. The archive is said to contain DICOM studies and patient metadata, yet the post remains unconfirmed and may be partly promotional. #301Hospital #Beijing…

AhnLab SEcurity intelligence Center found Larva-26010 targeting Korean web servers and MS-SQL servers to install SoftEther VPN, likely to turn infected systems into covert VPN/C&C infrastructure. The intrusion chain also included discovery commands, registry changes for WDigest credential theft, and follow-on deployment of CLR SqlShell and web shells. #Larva26010 #SoftEtherVPN #MSSQL…
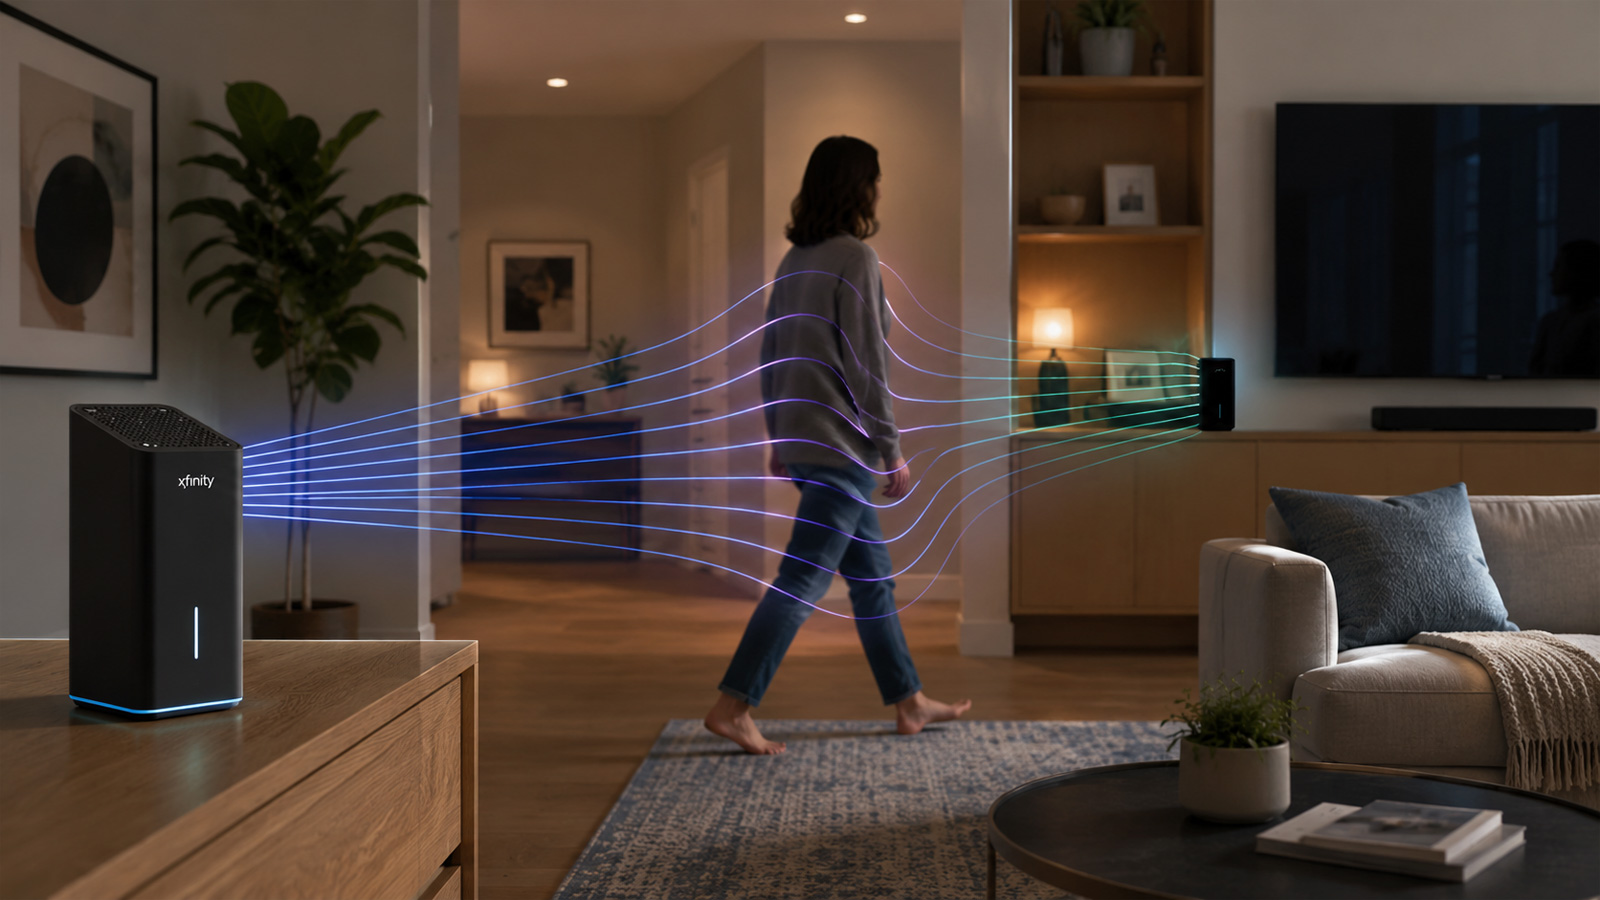
Comcast has expanded Xfinity Shield with WiFi Motion, a feature that uses WiFi signal changes to detect movement in a home without cameras or dedicated motion sensors. The company says the system is opt-in and does not identify people, but its documentation raises data-retention and law-enforcement disclosure questions. #Comcast #XfinityShield #WiFiMotion #XfinityApp
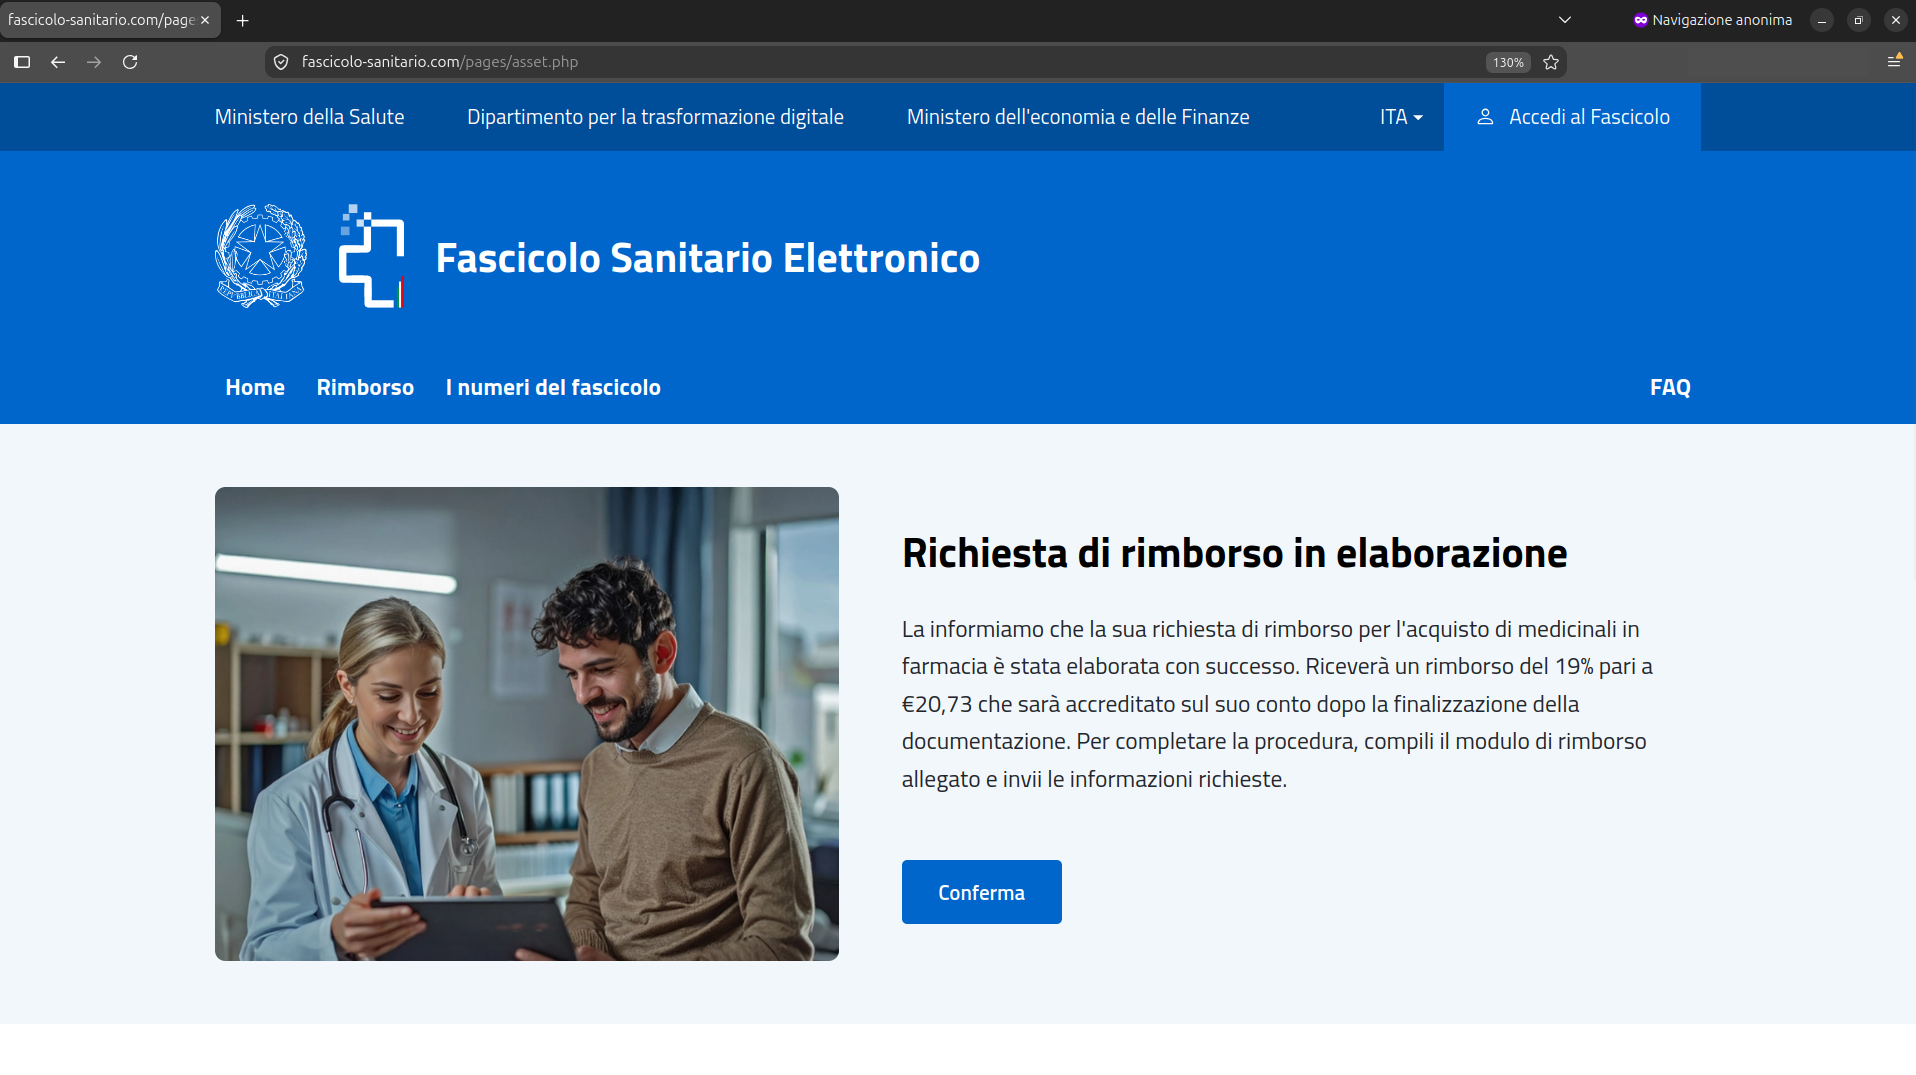
CERT-AGID identified a phishing campaign that abuses the branding of the Fascicolo Sanitario Elettronico, Ministry of Health, Department for Digital Transformation, and Ministry of Economy and Finance to steal personal and payment card data. The fake site lures victims with a supposed 19% pharmacy refund and then collects identity details and card information before showing a fabricated “in processing” confirmation. #CERT-AGID #FascicoloSanitarioElettronico #MinisteroDellaSalute #MinisteroDEconomiaEDelleFinanze
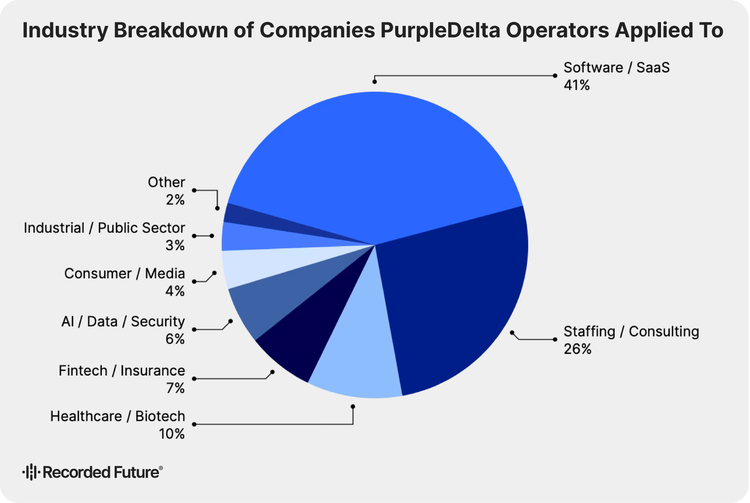
Insikt Group identified multiple PurpleDelta clusters tied to North Korean IT workers, likely based in China, that used fabricated personas, AI tools, and remote-access tradecraft to obtain and hold jobs at more than 1,100 companies. The operators applied for work at scale, recorded internal meetings, coordinated through Telegram and Slack, and used services such as ChatGPT, AnyDesk, and TrustID Card to support ongoing insider-risk activity. #PurpleDelta #ChatGPT #AnyDesk #Telegram #Slack #TrustIDCard
Federal authorities unsealed an indictment against 17 Iranians affiliated with the Mabna Institute, accusing them of a large-scale, state-sponsored cybertheft campaign targeting universities, governments, and companies. The case alleges the theft of academic and research data from thousands of accounts worldwide, with a Rewards for Justice offer of up to $10 million for information on four of the defendants. #MabnaInstitute #RewardsforJustice #HBO

R & D Machine and Engineering, US was targeted by the dragonforce ransomware group, impacting its CNC machining operations that support aerospace, defense, and space customers including NASA. The incident disrupted production capabilities for mission-critical precision components, affecting operations in #UnitedStates
T… P… L… reported a ransomware incident attributed to Threat Actor SilentRansomGroup, with full company name pending disclosure (FULL DATA TIMER active). The impacted country(s) #undefined
ADL Embedded Solutions in the US is reported to be an active ransomware victim, with the threat actor securotrop associated with the incident and the case currently in AWAITING status. The claimed impact size is 925 GB. #UnitedStates

Penetration testing delivers value only when findings move quickly from discovery to verified remediation, not when they get stuck in manual reporting and handoff steps. The article argues that platforms like PlexTrac help modernize the pentest lifecycle by connecting testing, delivery, remediation, and retesting into one workflow. #PlexTrac #DanDeCloss

Daily Recap, GitHub experienced a worldwide outage, while large-scale DDoS attacks disrupted Threema’s secure messaging service. In other security developments, Philips and GE are investigating Clop ransomware data-theft claims, SafePal confirmed a breach impacting 39,798 customers, and Microsoft is working on a Defender patch for the ShieldBreak zero-day while new AmnesiaStealer macOS malware targets browser sessions.
#GitHub #Threema #DDoS #Clop #Philips #GE #SafePal #ShieldBreak #Microsoft Defender #AmnesiaStealer #macOS
ReliaQuest uncovered a custom JSP web shell likely tied to Clop that was built specifically for PTC Windchill and FlexPLM, with functions to decrypt credentials, enumerate vaults, and steal files. The activity appears linked to CVE-2026-12569 exploitation and Clop’s broader data theft campaign against enterprise platforms. #Clop #PTCWindchill #FlexPLM #CVE2026-12569
Incransom ransomware allegedly targeted ssf-int.com and ssf-ing.de, impacting SSF International GmbH, a Munich-based engineering firm in Germany that provides comprehensive infrastructure and railway project services worldwide. The claim indicates disruption from the ransomware incident affecting operations and services in #Germany
SpearFin Ltd (MU) in Mauritius, a fund administration and corporate services provider with ~US$10 billion in assets under administration, disclosed a data leak attributed to ransomware threat actor incransom on June 26, 2026, totaling 416 GB of confidential material including KYC/AML records, passports, bank statements, shareholder and directors registers, and related investment and corporate agreements. Affected data includes documents such as NDAs, investing documents, application forms, certificates (including GBC certifications), loans and payroll records, and correspondence tied to multiple clients; #Mauritius