Semana in ES reported that the ransomware group qilin encrypted data and disrupted operations during the attack, demanding a ransom for restoration. The incident impacted #Spain
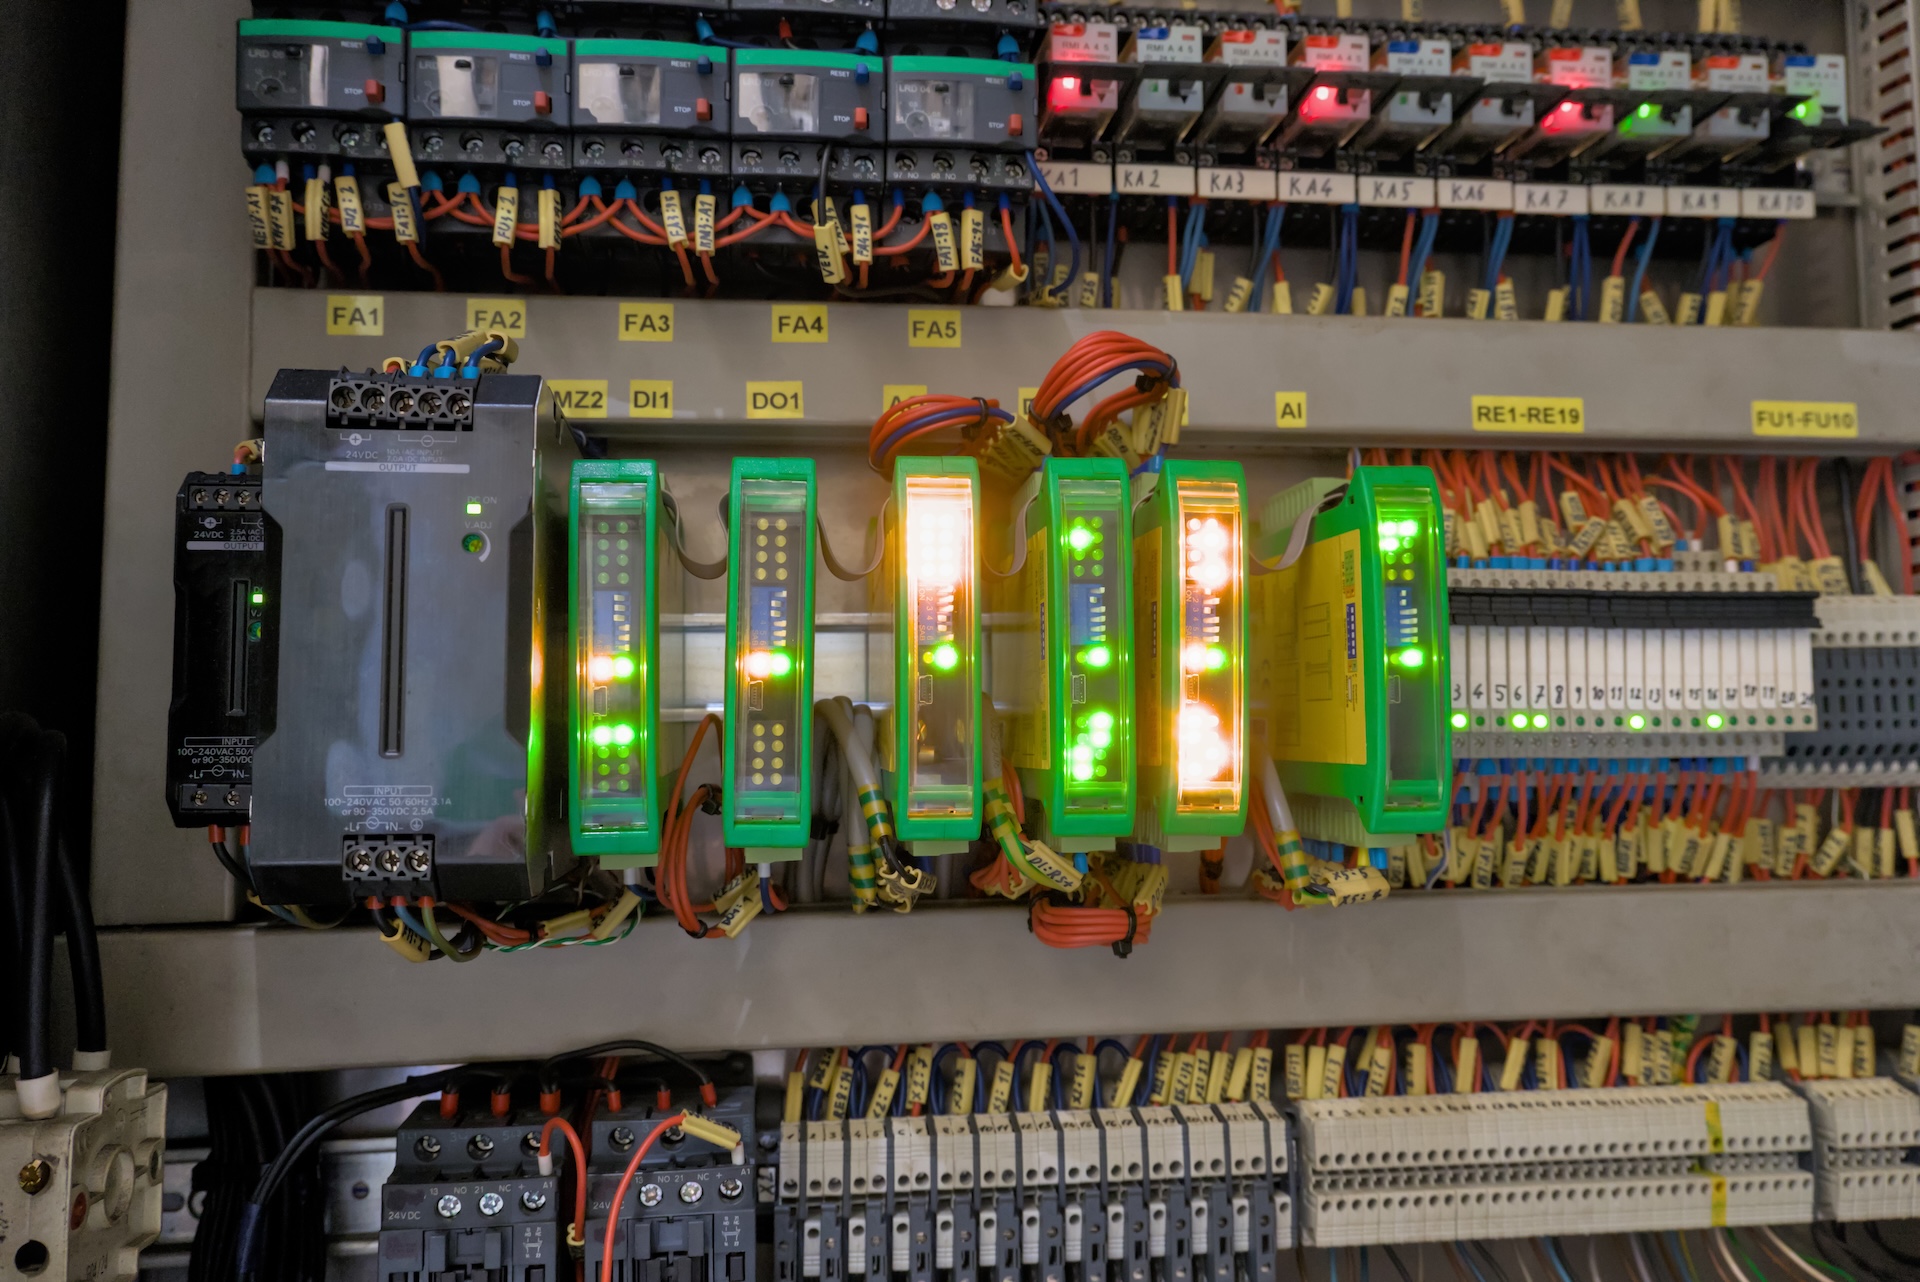
U.S. agencies warned that hackers are targeting critical infrastructure by attacking Siemens S7 Series PLCs used in industrial control systems across water, food, energy, chemical, manufacturing, and commercial facilities. The alert says the active threat uses AI-generated exploitation scripts disguised as monitoring tools, enabling faster attacks and potential disruption, safety incidents, and data compromise. #SiemensS7 #PLC #CISA #NSA #FBI #EnergyDepartment #EPA
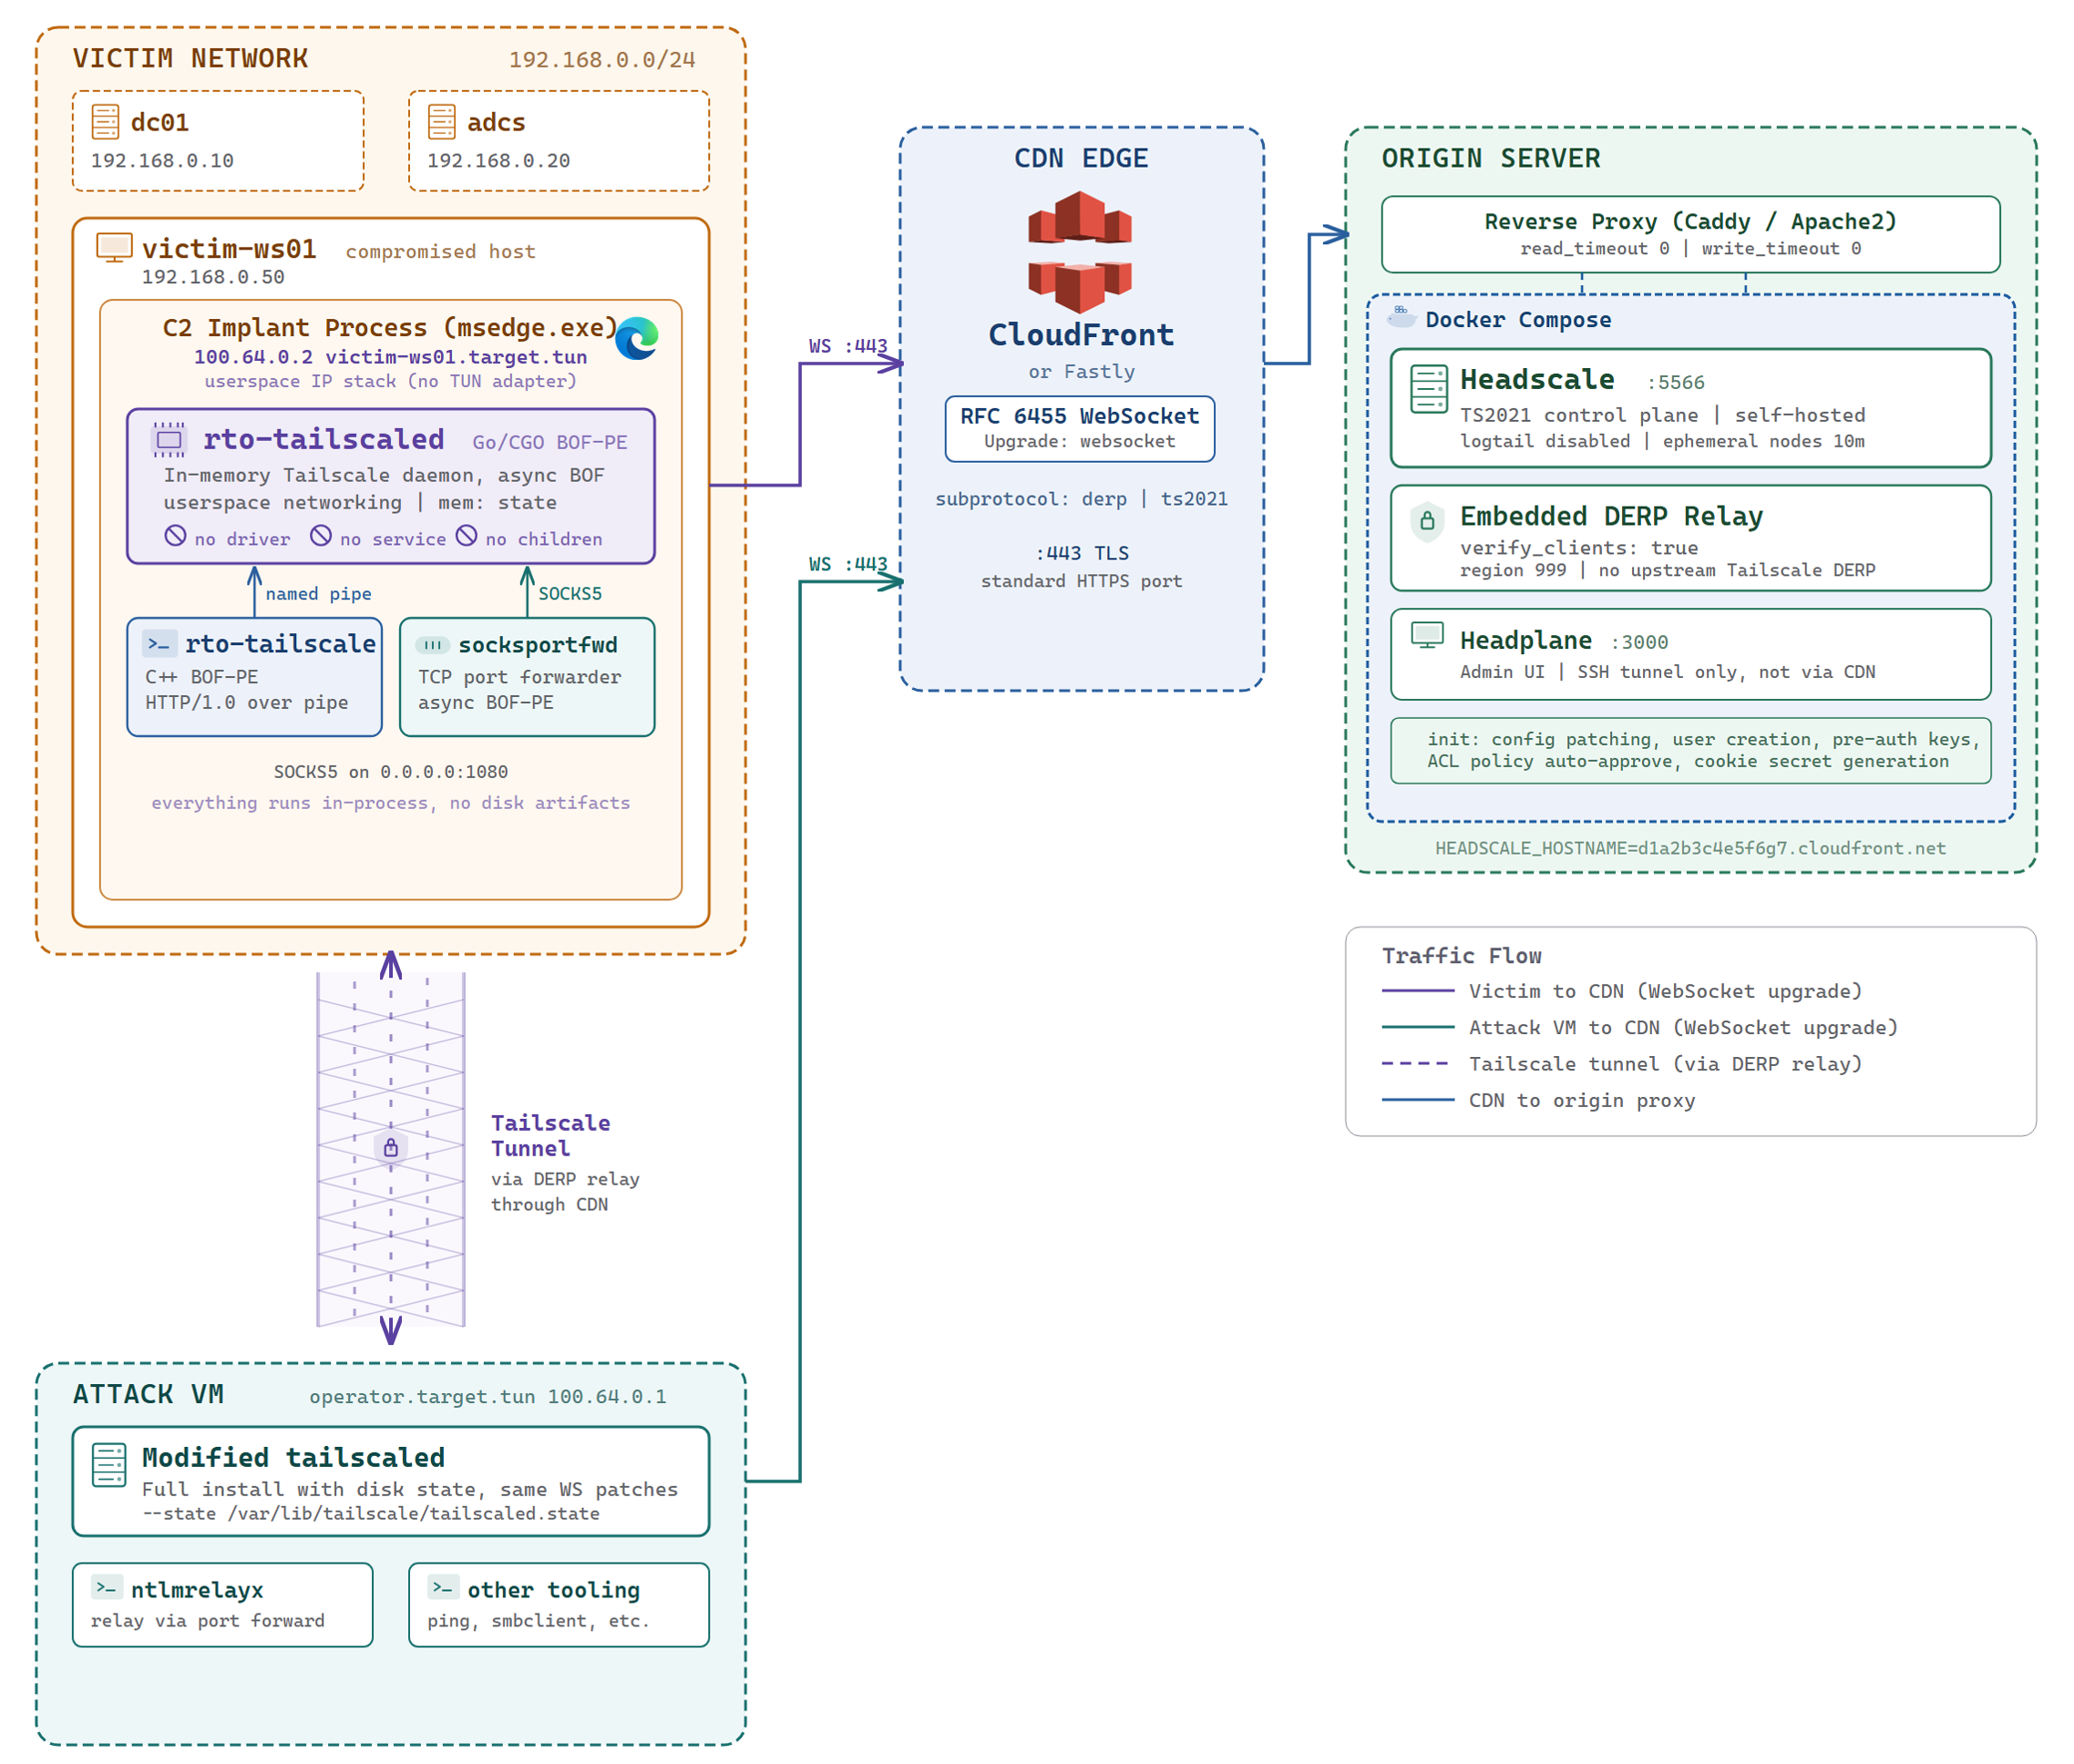
This article describes BOFScale, which runs a modified Tailscale daemon and client entirely in-memory to tunnel TS2021 control traffic and DERP relay traffic over standard WebSockets through CloudFront or Fastly. It also shows how the stack uses Headscale, SOCKS5 port forwarding, and userspace networking to support covert access, routing, and NTLM relay operations while reducing disk, service, and child-process artifacts. #BOFScale #Tailscale #Headscale #CloudFront #Fastly #DERP #TS2021
NSA, CISA, FBI, DOE, and EPA warn of an active threat targeting Internet-exposed Siemens S7 Series PLCs with AI-generated exploitation scripts, insecure credentials, and Snap7-based tooling disguised as legitimate monitoring software. The advisory urges immediate hardening, patching, segmentation, and monitoring to protect critical infrastructure sectors and prevent disruption, safety incidents, and…
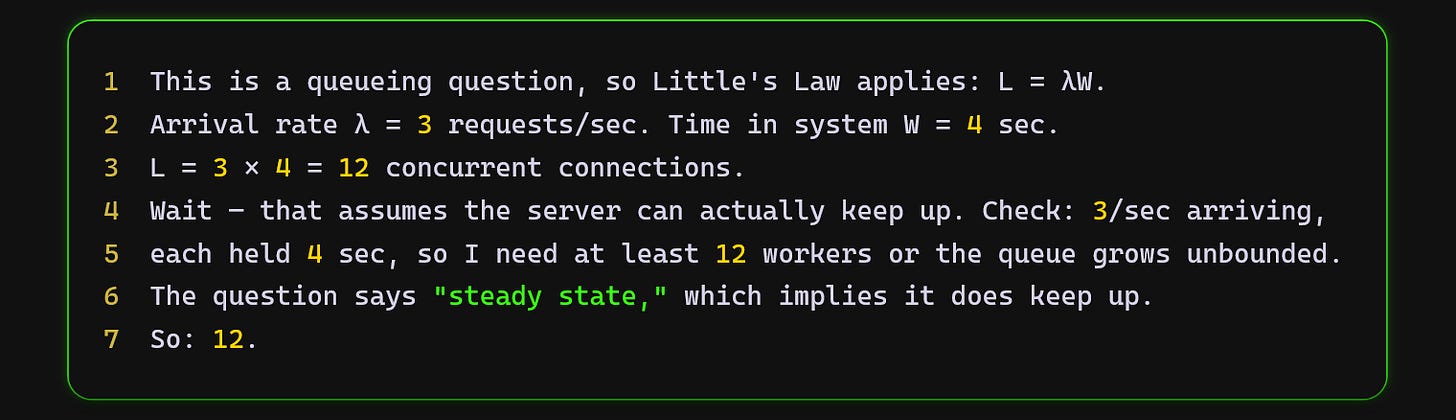
Researchers showed that encrypted reasoning traces from proprietary LLM APIs can be recovered by replaying them through weaker compatible models, without breaking the encryption itself. The study also found that hidden reasoning blocks can leak secrets, including API keys and passwords, and can even carry malicious instructions that affect later model behavior. #Claude #GPT #Gemini #Haiku #GPT-5.6 #GeminiRobotics #StealingReasoningTracesfromProprietaryLLMAPIs
This HRMCon 2026 keynote preview explores how cybersecurity must become more autonomous and continuously adaptive by 2030 to keep pace with AI-enabled threats operating at machine speed. It also emphasizes that while technology will evolve rapidly, accountability for security outcomes will still rest with people and organizations. #HRMCon2026 #LivingSecurity

Daily Recap, AI security coverage highlighted escalating vulnerability pressure alongside new funding and acquisitions, while multiple reports showed how misconfigurations, naming errors, and oversight gaps can push AI systems into unpredictable behavior or even real-world attacks. The recap also covered actively exploited flaws across Windows and other platforms, high-impact breaches affecting personal data at scale, and threat-actor activity tied to the financial sector. #Xpander #VirtueAI #LiteLLM #Trivy #WindowsTaskHost #Ray #GitLab #Snowflake #WordPress #WebKit #Microsoft365 #WMIC #SouthCarolina #SSNs #SafePal #PokemonCenter #Azure #BlackFile #Claude #SelfReplicatingMalware

An alleged data exposure tied to Argentine hardware wallet retailer coincustody.io may have revealed named buyers, home addresses, DNI/CUIT numbers, phone numbers, and other order details. If true, the leak could enable physical targeting, identity fraud, SIM swapping, and highly convincing wallet-seed phishing attempts against crypto users. #coincustodyio #kingloki #Trezor #Ledger…

Global Terminal Services in Turkey, registered as Global Terminal Hizmetleri A.,Ş., reported a Deadlock ransomware incident affecting 470GB of data, disrupting operations at the region’s largest independent liquid fuels and oil storage terminal in the Mediterranean. #Turkey
United Fiber Optic Communication Inc. (UFOC), a Taiwan-based telecommunications provider specializing in fiber optic cables and integrated communication systems, reported a ransomware incident attributed to the Deadlock threat actor. The attack reportedly impacted operations within Taiwan. #Taiwan
Delek US in the US was targeted by Helix ransomware. T1 unlocks in 12 hours, with subsequent tiers unlocking every 24 hours, leaving the impacted country(s) #UnitedStates
Researchers uncovered CameraSwarm, a 35-day campaign that compromised more than 14,500 Dahua IP cameras, mainly in Ukraine and Russia, using brute-force logins, vulnerability exploits, and offline recovery codes. Hunt.io traced the operation after finding exposed attacker files, and Dahua camera owners are urged to check for the persistent p2pwn account and apply firmware fixes. #CameraSwarm #Dahua #Huntio #CVE-2021-33044 #CVE-2021-33045
Ryomo Systems confirmed an unauthorized intrusion into its internal systems on August 14 and is investigating how the attack occurred and whether any data was stolen. The Japanese IT company serves critical sectors including water, energy, healthcare, and government, making the incident especially sensitive. #RyomoSystems
Clop exploited the zero-day CVE-2026-12569 in PTC’s Windchill and FlexPLM platforms to conduct a large-scale data theft extortion campaign against dozens of organizations. Researchers said the group used a custom Windchill web shell to steal credentials, maintain access, and move quickly across victim systems. #Clop #PTC #Windchill #FlexPLM #CVE-2026-12569

Shasta County Registrar Clint Curtis says he plans to hire convicted felon and election denialist Tina Peters as an assistant registrar, raising alarm because Peters was previously convicted for stealing voting system software and other election-related crimes. The move has drawn concern from California officials, including Sens. Alex Padilla and Adam Schiff, who warned about her potential access to sensitive election systems and voter information. #TinaPeters #ClintCurtis #ShastaCounty #JaredPolis #AlexPadilla #AdamSchiff