Island Networks in JM reported a ransomware incident attributed to the pear threat actor, impacting their business-class internet, cybersecurity, and home Wi‑Fi services. The reported impact is in #Jamaica

spacebears ransomware targeted Freelom.net s.r.o., a Czech ISP and IT provider in Lomnice nad Popelkou (Freelom.net; SQL data claim involving all client personal data), and threatened exposure or disruption via the company’s systems. The victim is in the Czech Republic. #CzechRepublic
Ransomware claimed by spacebears targeted Holzmarkt Chemnitz in Germany, a specialized building materials and wood products retailer operating two branches in Chemnitz (Fichtestra,ße and Kalkstraße). The incident reportedly involved theft or encryption of employee and client personal information, financial documents, and a SQL database tied to https://holzmarkt-chemnitz.de/. #Germany
Meridian Logistics Group in the US reports that threat actor thegentlemen staged a full network image and exfiltrated sensitive data. Recovered ERP exports, dispatch database, and payroll archives are pending final inventory before publication, impacting #UnitedStates
Termite ransomware reportedly targeted Everglades Boats, an offshore fishing boat manufacturer headquartered in Edgewater, Florida, in the United States. The attack compromised the company’s systems and operations, impacting operations in the US #UnitedStates
The US-based CRI Electric ransomware claim attributed to the rhysida threat actor involves theft of employee federal account artifacts, vendor tax documents, payroll and privileged HR/legal correspondence, and corporate financial and certification records. Impacted country(s): #UnitedStates
Victory Personal Care, Inc in the US reported a ransomware incident attributed to threat actor nightspire, with details of the affected data not available at this time. The impact is reported for #UnitedStates

Researchers uncovered a new Android malware family that targets DoFun vehicle head unit firmware by abusing legitimate software update mechanisms to install hidden payloads. The campaign, linked to the MoYu Group and BADBOX activity, supports ad fraud and proxy botnet operations while stealing device details and fetching additional modules like zhima….

Check Point Research revealed that Microsoft Defender’s legitimately signed BTR.sys boot-time remediation driver can be abused for arbitrary kernel-level file and registry operations on Windows from Windows 7 through Windows 11 25H2. The technique, demonstrated with the BTR_CLI proof-of-concept, can remove security binaries in a “golden window” after reboot, while Check…

Researchers found trojanized npm packages that pretend to be calendar and streak utilities while secretly deploying RedC2 4.0’s AI-powered Linux implant, RedShell. The campaign uses a simple import to trigger execution and is linked to a broader, evolving C2 framework promoted by the threat actor MarlboroMan via Red Offsec. #RedC2 #RedShell…
The threat actor “thegentlemen” allegedly deployed ransomware against UOLconsult in Brazil, targeting systems associated with uol-consult.com. As a boutique management consulting firm founded in 2015, UOLconsult GmbH may have experienced disruption to its strategic, business development, and investment consulting operations in #Brazil
A professional victim in the US reported a ransomware incident attributed to the Qilin threat actor. The attackers encrypted files and demanded payment to restore access, impacting #UnitedStates
cedarridge.org, located in the US, was reportedly targeted by the L Group ransomware, resulting in encrypted files and disruption of normal operations. The incident is attributed to ransomware activity impacting the victim’s systems in #UnitedStates
EchoBench is a human-calibrated benchmark for autonomous web application pentesting that scores model-and-harness systems against associate pentesters from NetSPI University. It uses four geometric-mean components—finding fidelity, difficulty-reach, OWASP breadth, and repeatability—while publishing cohort, configuration, provenance, and repeatability details alongside every score. #EchoBench #NetSPIUniversity #OWASP2025
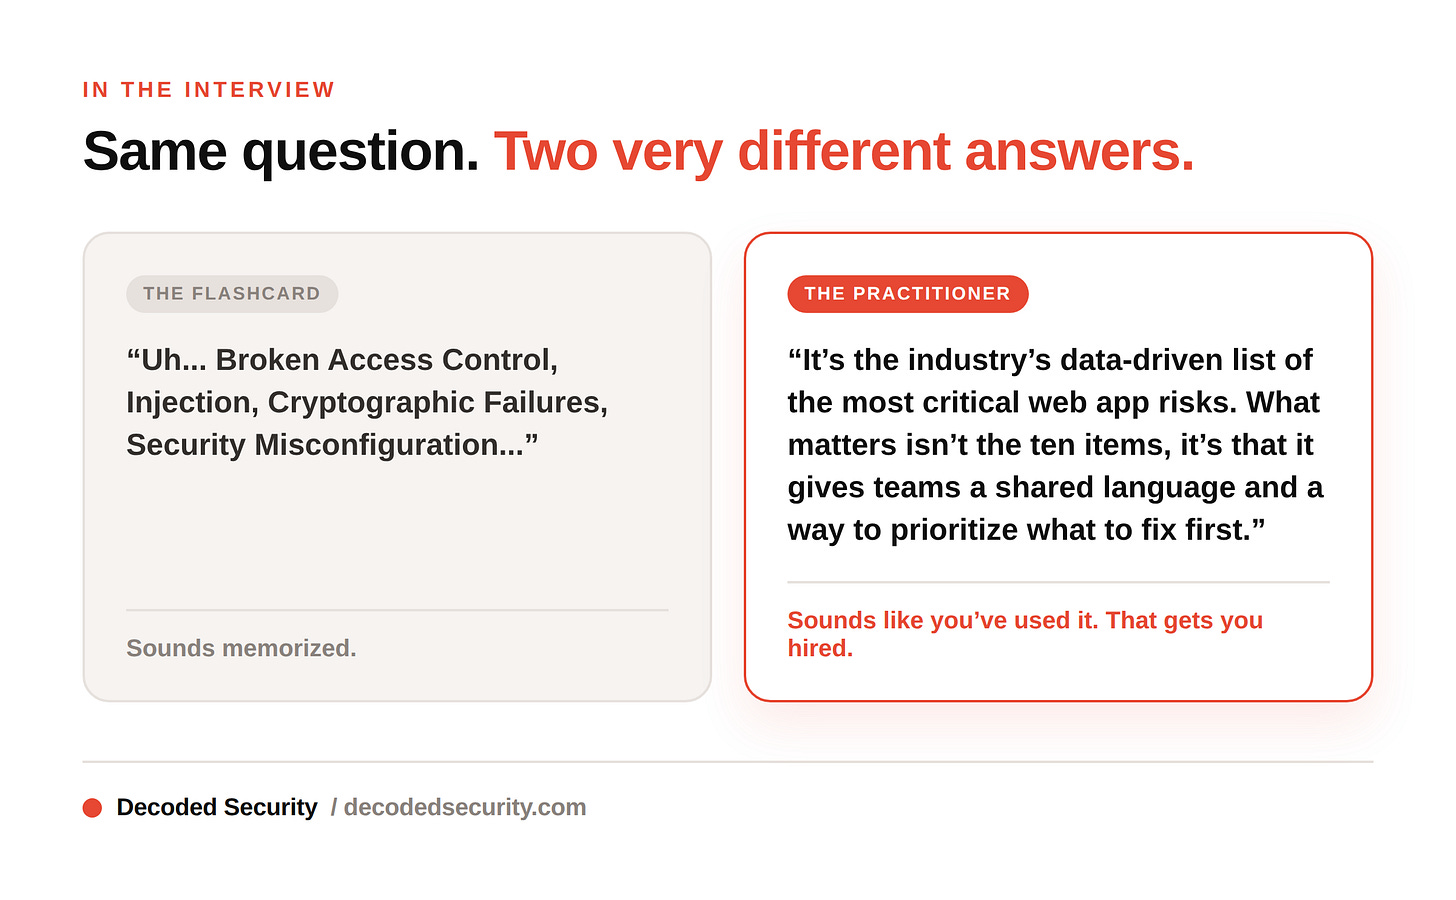
The OWASP Top 10 is a data-driven, regularly updated list of the most critical web application risks, built from real-world breaches rather than opinion. Its value is not in memorizing the categories, but in using it as a shared language to prioritize what to fix first and improve application security. #OWASP #OWASPTop10