Deadlock ransomware impacted FBC, the Furniture Bargaining Council in South Africa, a tariff council supporting legal and administrative processes for the furniture, mattress, and upholstery industry across regions including Gauteng, North West, Mpumalanga, Limpopo, and the Free State. The attack disrupted services for employers and employees relying on the platform to manage industry matters. #SouthAfrica

Deadlock ransomware actors claim to have stolen sensitive client and transaction files from SHAHEEN LAW GROUP PLC in Virginia, including Social Security numbers, bank wiring details, addresses, family identities, and related documents tied to 150+ monthly real estate closings, plus banking statement attachments and customer folders. The group says the stolen data includes deed records and a client/relocation database for potential resale and impact, threatening exposure of litigation and medical information. #UnitedStates
The ransomware claim alleges that the threat actor qilin compromised Consultores de Seguros and deployed ransomware to encrypt data and disrupt operations. No impacted country is specified in the claim; N/A #N/A
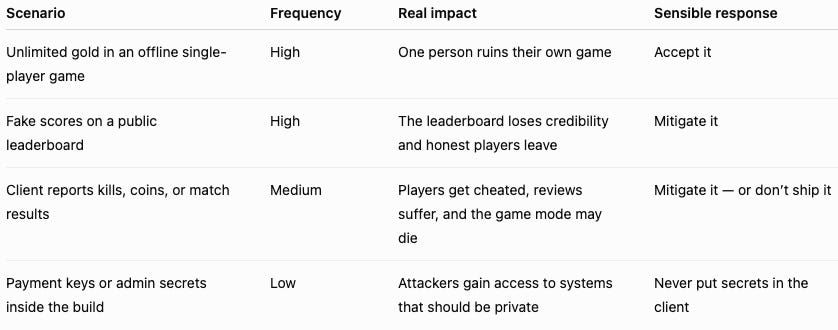
This article explains why making a game “unhackable” is the wrong goal and shows how cybersecurity concepts like residual risk, threat modeling, and risk treatment apply in the gaming industry. It emphasizes that developers should protect what matters most, such as revenue, purchases, and multiplayer fairness, while accepting or mitigating the risk that remains on a player-owned device. #GuardingPearSoftware #TimUhlott #Unity

A bipartisan Senate bill called the Quantum-GUARD Act would push federal regulators to prepare the U.S. electric grid for quantum computing threats and study how quantum risks could affect both IT and OT systems. The measure also encourages exploration of post-quantum cryptography to protect critical infrastructure from future attacks. #QuantumGUARD #FERC #NIST #SCADA

The U.S. Treasury Department sanctioned four Iranians for allegedly hacking U.S. critical infrastructure and stealing data from multiple companies across sectors including energy, defense, healthcare, IT, and finance. The action targets individuals linked to the Tehran-based Mabna Institute and MOIS-directed operations, while expanding pressure on Iran’s economic sectors and cyber-enabled activities. #MabnaInstitute #MOIS #KeyvanFayyazGharehBlagh #SaberShahbaziBalujeh #MohammadRezaKadkhoda’i #MojtabaGhal’eh-Kuhi #ArmanKahzadian

OT threat intelligence helps critical infrastructure operators turn broad security data into actionable insights by adding asset, protocol, and operational context. In energy-sector environments, solutions like OMICRON Threat Intelligence and StationGuard help teams determine whether vulnerabilities, alerts, and communications are relevant to their specific OT systems. #OMICRON #StationGuard #IEC61850 #IEC60870-5-104 #MITREATTCKforICS
The U.S. Department of Justice announced a $400 million settlement with TikTok, ByteDance, and affiliated companies over alleged violations of the Children’s Online Privacy Protection Act dating back to 2019. The agreement follows claims that TikTok allowed children under 13 to create accounts, collect their personal data without parental consent, and failed to properly delete underage accounts and information. #TikTok #ByteDance #COPPA #Musical.ly
Hackers are actively exploiting two critical authentication bypass flaws in the miniOrange SAML 2.0 Single Sign On plugin for WordPress, chaining CVE-2026-61979 and CVE-2026-15981 to forge SAML responses and gain administrator access. Patchstack says attacks are underway against both free and paid editions, with a publicly available PoC and multiple IPs already used in scanning and exploitation attempts. #miniOrange #Xecurify #CVE-2026-61979 #CVE-2026-15981 #Patchstack #WordPress #DigitalOcean
The Liberty Group in the US suffered a ransomware attack attributed to Dark Project, involving the theft of approximately 27,000 internal files followed by encryption of company systems that severely disrupted operations. The leaked materials reportedly include financial records, internal working documents, and employees’ personal data, and investigators are assessing the full scope of the damage. #UnitedStates
The ransomware attack targeted lagegepesca.it, an Italian company, and was attributed to the safepay threat actor based in Lallio near Bergamo in Lombardy, tracing its origins to 1957 when Santo Gavazzi founded the business. The incident resulted in encrypted systems and service disruption for the victim in Italy. #Italy

Researchers uncovered two malware families, WordlistLoader and SynkLoader, that are being used to deliver follow-on payloads and may be tied to ransomware access sales. WordlistLoader is linked to ClearFake ClickFix campaigns delivering Amatera Stealer, while SynkLoader was pushed through Microsoft Teams phishing with a fake IT Service Desk and lock screen…

Attackers are increasingly abusing exposed infrastructure, trusted software ecosystems, and AI-assisted tooling, with active exploitation seen against Siemens PLCs, GitLab, PTC Windchill, and trojanized npm packages. Researchers also highlighted fresh techniques and leaks affecting Visa contactless payments, Cloudflare Workers, Unisoc modem firmware, and corporate cloud credentials. #Siemens #S7Series #GitLab #PTCWindchill #RedC2…
ReliaQuest confirmed it was targeted by the ShinyHunters group in a social engineering attack that used a fake domain and phishing page to steal a teammate’s credentials. The company said the incident was contained, with only brief view-only access to an identity dashboard and no compromise of customer data or business…
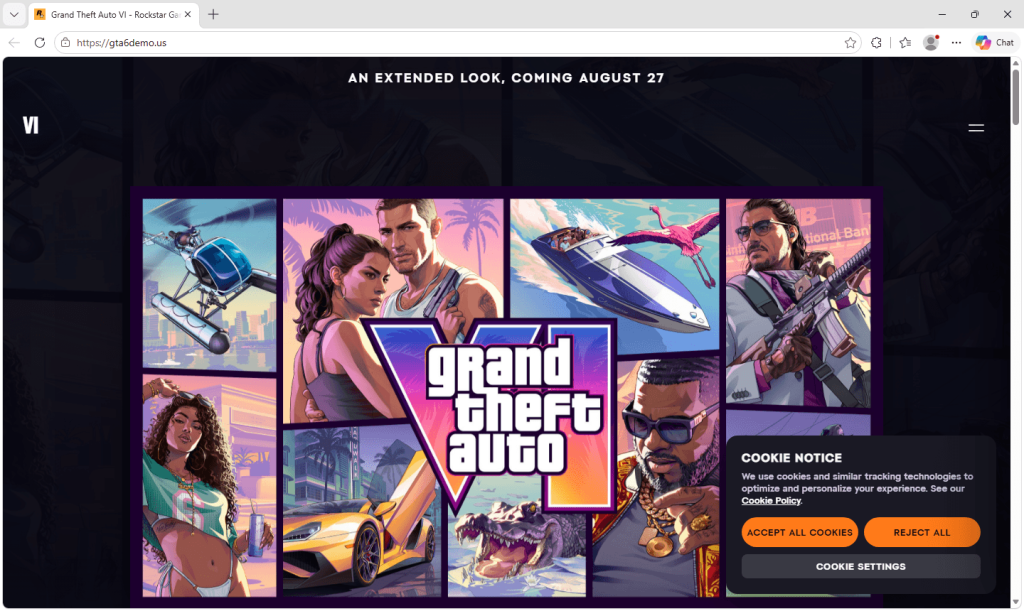
Fake Rockstar sites are using hype around GTA 6 leaks and the upcoming Extended Look to push a malicious gta6_installer.exe that installs the Vidar infostealer. The campaign steals saved passwords, session cookies, and browser data from multiple browsers and can bypass the protection of 2FA by reusing stolen authenticated sessions. #GTA6…