Cosmon (US) describes itself as a proprietary engineering software provider whose Nexus platform automates CAD, CAE simulation, troubleshooting, design validation, and product lifecycle data workflows with integrations to major engineering tools. The “beast” ransomware claim targets Cosmon and presents the impact as affecting the United States. #UnitedStates
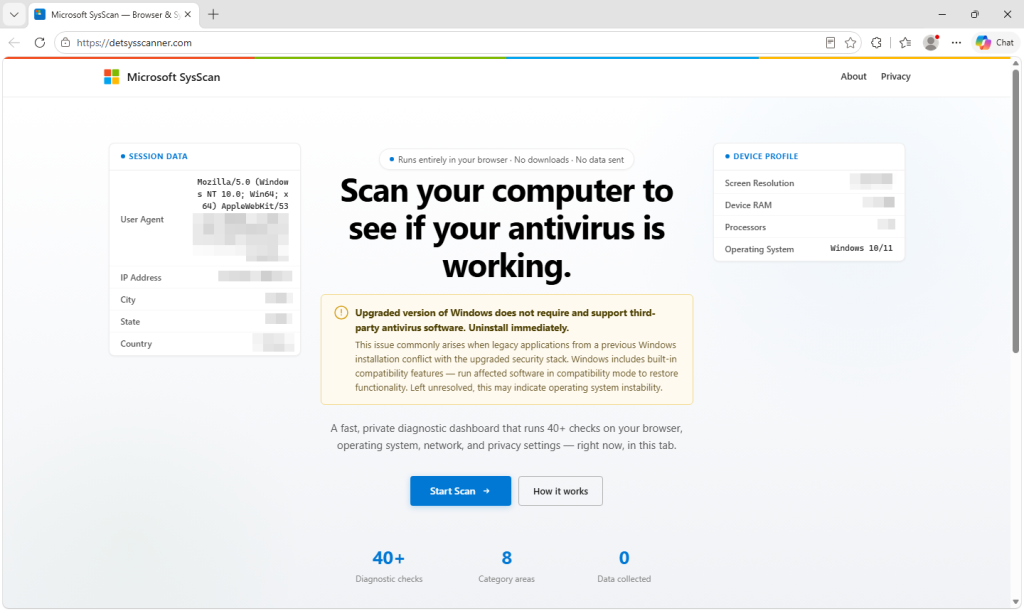
A group of Microsoft-branded SysScan websites is using fake security scans to falsely claim that third-party antivirus on Windows is causing serious problems and should be uninstalled. The scam funnels victims into a refund call, collects personal and banking details, and sends the data to Telegram while presenting a fake handoff…
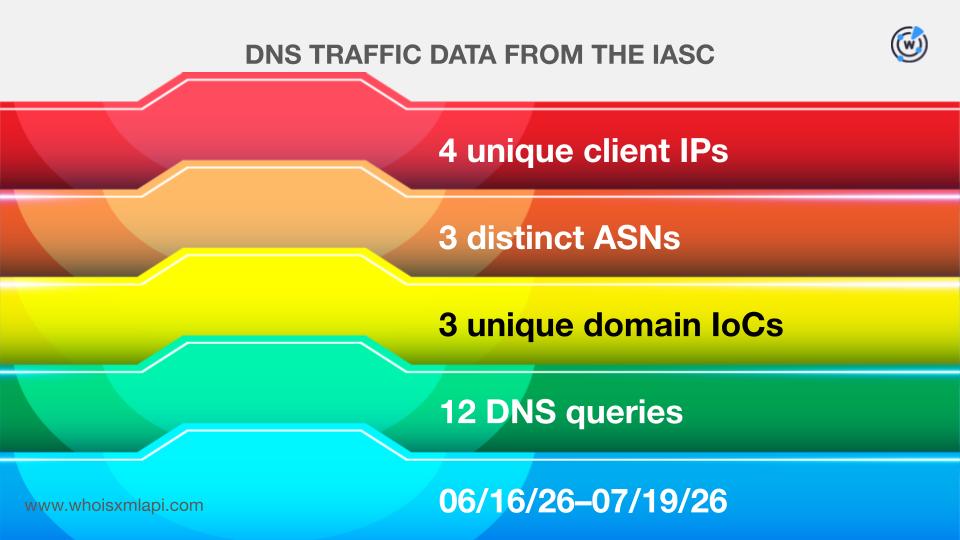
The article analyzes five major 2026 cyber attacks, focusing on network and WHOIS artifacts tied to Ivanti EPMM, Cisco SD-WAN, Stryker, and multiple ShinyHunters-related breaches. It highlights dozens of domains, subdomains, and IPs, including typosquatting clusters, historical DNS resolutions, and newly discovered email-connected infrastructure. #IvantiEPMM #CiscoSDWAN #Stryker #ShinyHunters #oastfun #shinyhuntersrs #azurenetfilesnet

Bihl (DE) reported a ransomware claim attributed to the akira threat actor, alleging encryption and theft of 392GB of corporate data from Boustead International Heaters (BIH), a thermal processing equipment supplier. The attackers purportedly obtained extensive personal employee information (passports, driver’s licenses, addresses, SSNs, and vital records) along with confidential financials, agreements, contracts, client data, and NDAs, impacting #Germany
The ransomware incident targeting Wozair in AE was attributed to the dragonforce threat actor. Wozair’s HVAC manufacturing and installation operations across sectors such as Marine, Naval, Military, Nuclear, Oil and Gas, and Renewables were impacted, with the primary impact in #UnitedArabEmirates.
Dragonforce ransomware allegedly exfiltrated data from Brookview Financial, including information on many thousands of customers such as credit reports, Social Security numbers, and addresses. The incident impacted Canada #Canada

AI coding tools can speed up development, but they also increase open-source dependencies and create growing remediation debt for security teams. The webinar shares findings from 300 enterprise leaders on how organizations like ActiveState are handling AI-driven open-source risk, governance, and downstream business impact. #ActiveState #RebeccaBanks #MorisChen…
Furnished Quarters, based in the US, reported a successful ransomware attack in which Dark Project stole 155 GB of confidential data, including customer details and documents with banking and financial information. As a result, approximately 198,000 files are no longer under the company’s control. #UnitedStates
Design-Aire Engineering, INC (US) was targeted by ransomware operations attributed to the threat actor Dark Project, which compromised its service systems. The attack led to the theft of approximately 377GB of sensitive data, including employees’ personal information and detailed architectural plans for clients, impacting #UnitedStates
Jones, Little & Co., CPAs, LLP, a US accounting firm, reported that the Dark Project ransomware group exfiltrated at least 100GB of company data—including financial records, internal files, and employee personal information—before encrypting its systems, paralyzing operations. #UnitedStates

The Supreme Court dismissed one lawsuit challenging Trump administration changes to USPS mail-in ballot regulations, ruling that the states had not shown concrete harm. The case centered on executive order directives for State Citizenship Lists and DOJ enforcement priorities, while lower courts and dissenting justices warned the policy could intrude on states’ election authority. #USPS #TrumpAdministration #SupremeCourt

A forum user named Lagui1337 is allegedly selling a YouFid database containing 1,899,454 rows of French loyalty customer records for 1,000 euros in cryptocurrency. The unverified listing claims extensive personal and loyalty data, including email addresses, phone numbers, QR card codes, and merchant visit history, with a 1,000-line sample published. #YouFid…
A forum user known as NikolaT claims to have published 22.25 GB of Groupe Bernard data, calling it the thirteenth leak from a shared platform named BlgCloud. The unverified post includes CRM records, invoice and delivery note metadata, and application user accounts, with free download links shared to anyone who replies….

There are 5 defacement incidents in this content, targeting Mozambique, Indonesia, and Bangladesh. The attackers involved are Antonkill, dkv blackhat, and Monkey D Luffy. #Mozambique #Indonesia #Bangladesh…
A missing authentication flaw in Calix GS7 XGS (GS5239XG) routers lets remote attackers create port-forwarding rules and expose home-network devices to the internet without logging in. Security researcher Brian Khan Quintana disclosed CVE-2026-75501 after vendor contact attempts failed, and the current workaround is to disable UPnP or ask the ISP to do so. #Calix #GS5239XG #CVE-2026-75501 #CERTCC #BrianKhanQuintana