ETNA Software (IT) was targeted by the Eclipse ransomware threat actor, disrupting operations of its white-label online trading solutions used by brokers and FinTech firms, including mobile and web trading platforms. The incident impacted ETNA Software’s customers and trading services within Italy #Italy

Victims of CSAM have filed a class action lawsuit against xAI, alleging Grok was trained on real abuse imagery and used to generate synthetic “nudify” deepfakes involving a victim tracked by the FBI’s Child Exploitation Notification Program. The complaint says Grok’s weak guardrails and X integration enabled large-scale sexualized content generation, prompting demands for damages and an injunction. #xAI #Grok #NCMEC #FBI #Masha’sLaw
More than 100 companies and organizations, including OpenAI, Anthropic, Google, Microsoft, and Amazon Web Services, have signed an open letter urging a global push to strengthen cybersecurity as AI capabilities rapidly advance. The letter warns that AI will accelerate both attacks and defenses, calling for immediate action to support critical infrastructure, fix major weaknesses, and prepare for a “defenders’ window.” #OpenAI #Anthropic #Google #Microsoft #AmazonWebServices #PaloAltoNetworks #GoldEagle
Unit 42 says frontier AI and agentic AI tools are creating a generational shift in cybersecurity by enabling attackers to find and exploit weaknesses at machine speed. The team warns that AI is already being used across the attack chain, from malware development and social engineering to ransomware negotiations, with major risks to identities, software supply chains, and enterprise defenses. #Unit42 #PaloAltoNetworks #Anthropic #ProjectGlasswing #Mythos
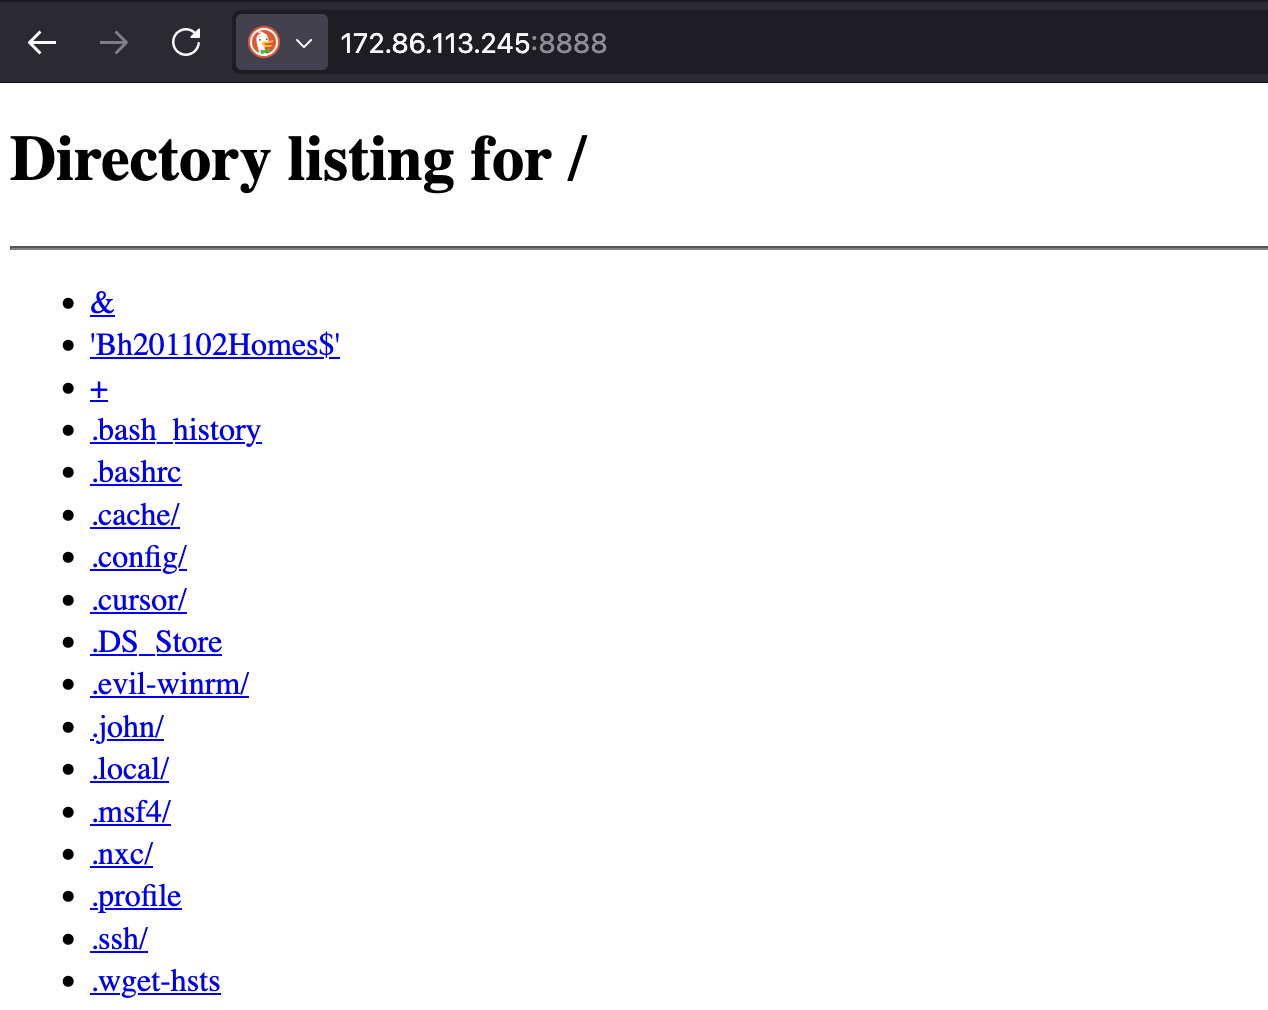
An exposed directory exposed months of activity by a Russian-speaking Aurora ransomware affiliate who compromised more than twenty organisations across nine countries between April and July 2026 and then deployed Aurora encryptors written in Zig. CloudSEK and TRM Labs traced a ransom negotiation and multiple victim payments through shared laundering infrastructure, tying the operator directly to Aurora rather than a broker and linking four victims to Aurora’s public leak site. #Aurora #TRMLabs #CloudSEK #Zig
Insikt Group identified BlueDelta initial access campaigns from late September 2025 to early April 2026 that targeted government and diplomatic organizations in Romania, Spain, and Türkiye using macro-enabled Word documents to deliver the HOOKEDGE backdoor. HOOKEDGE relies on webhook[.]site, Microsoft Edge, scheduled tasks, and staged batch-script execution, and the activity overlaps heavily with the earlier HEADLACE malware and the BlueDelta cluster associated with APT28, Fancy Bear, and Forest Blizzard. #BlueDelta #HOOKEDGE #HEADLACE #APT28 #FancyBear #ForestBlizzard #webhooksite

Vercel has released emergency patches for two critical unauthenticated RCE vulnerabilities in Next.js: a Windows-only path traversal issue tracked as CVE-2026-75604 and an AVIF image processing flaw in libheif. The fixes in Next.js 15.5.24 and 16.3.3 protect self-hosted deployments, while Vercel-hosted apps are already safe; the update also disables AVIF optimization…
Australian authorities have arrested and charged Ruben Ian Thomson and Louis Michael Gaebler over their alleged roles in TeamPCP, a cybercrime group tied to massive financial losses and the theft of sensitive data from more than 1,000 organizations. The group is said to have abused software supply chains and CI/CD pipelines,…

President Trump’s Executive Order 14420 declares a national emergency to reduce risks to the U.S. bulk power system from foreign-supplied electrical equipment and embedded backdoors. It targets critical grid technologies and gives the Energy Department authority to restrict, secure, or replace risky components while maintaining service continuity. #ExecutiveOrder14420 #Trump #DOE…

Storm ransomware allegedly targeted Agrimac, the first Australian agricultural dealership awarded AFS certification for up-to-the-minute GPS technology by Trimble, and whose headquarters are located at 92 Caramut Road, Warrnambool, VIC 3280, Australia. The attack reportedly impacted the organization in Australia. #Australia
Globalport Terminals in the Philippines was targeted by the Qilin ransomware group, which deployed ransomware to disrupt operations and encrypt files. The incident resulted in system downtime and data loss, impacting the organization in #Philippines

AI is making software faster and cheaper to build, so durable cybersecurity companies in 2026 will need moats that AI cannot easily replicate. The article argues that hardware, deep cryptography, and trusted practitioner networks can create lasting value through atoms, trust, certification, and real-world community effects. #Utimaco #Entrust #PS3 #Sony #Intel #AMD #ARM #C2ISAC #DEFCON #GreyHack #CCC

The Commission de la construction du Québec (CCQ) has been paralyzed since Monday following a cyberattack, prompting the organization to bring in external experts to assess the damage. While the CCQ has not yet confirmed whether any data was compromised, it says protecting personal information remains a priority and emergency services are still available. #CommissionDeLaConstructionDuQuébec #CCQ
Uşak University detected a cyberattack targeting its information systems on 2026-08-26 and isolated affected servers to protect data. The university reported the incident to the relevant authorities and is working with the Presidency of the Republic of Türkiye Cybersecurity Office to manage temporary disruptions to some digital services. #UşakUniversity #PresidencyoftheRepublicofTürkiyeCybersecurityOffice
Public transport in Attica was thrown into chaos on 27 August 2026 after a cyberattack disabled the telematics system, leaving electronic stop displays inactive and passengers without information. The incident highlighted serious shortcomings in the protection of Greece’s public digital infrastructure by the government and the Ministry of Infrastructure and Transport. #OASA #Attica #MinistryofInfrastructureandTransport