Holland & Knight, a US-based law firm headquartered in Tampa, Florida and established in 1968, reported a ransomware incident involving SilentRansomGroup. The attack impacted the organization in the United States. #UnitedStates

Quality Resource Pvt, a US advertising networks company, was targeted by the Global Secret Group ransomware, resulting in encrypted assets across 60.1 GB of data (170,436 files in 88,440 folders). The incident impacted operations for the victim in the United States. #UnitedStates
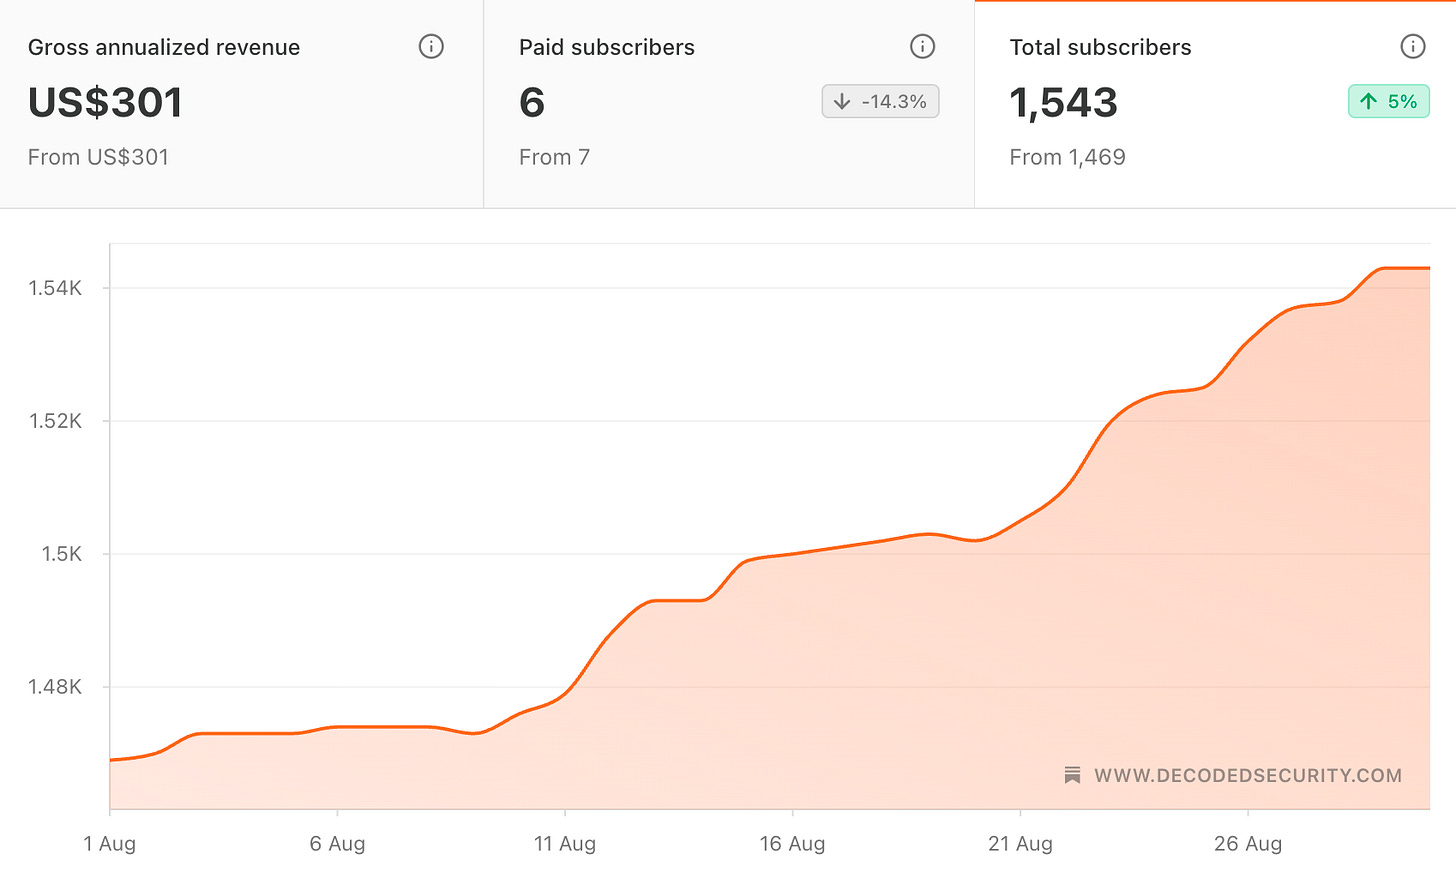
Erich from Decoded Security shares a monthly update highlighting August growth across newsletters, Threads, Instagram, Facebook, and interactive browser-based security tools like the port scanner, Linux sandbox, and DNS simulator. He also promotes a collaboration with Tim from GuardingPearSoftware, invites readers to suggest future topics, and announces a 14-day free trial for Decoded Security Premium. #DecodedSecurity #GuardingPearSoftware #Tim #ErichWinkler
AI agents are making security through obscurity less effective by cheaply inspecting software, APIs, and authorization logic while trying to complete everyday tasks. The article shows how this can expose hidden flaws in systems like gym booking apps and vibe-coded applications, where weak controls and missing authentication are increasingly discovered at scale. #OpenClaw #Claude #Affinda #RedAccess #WIRED
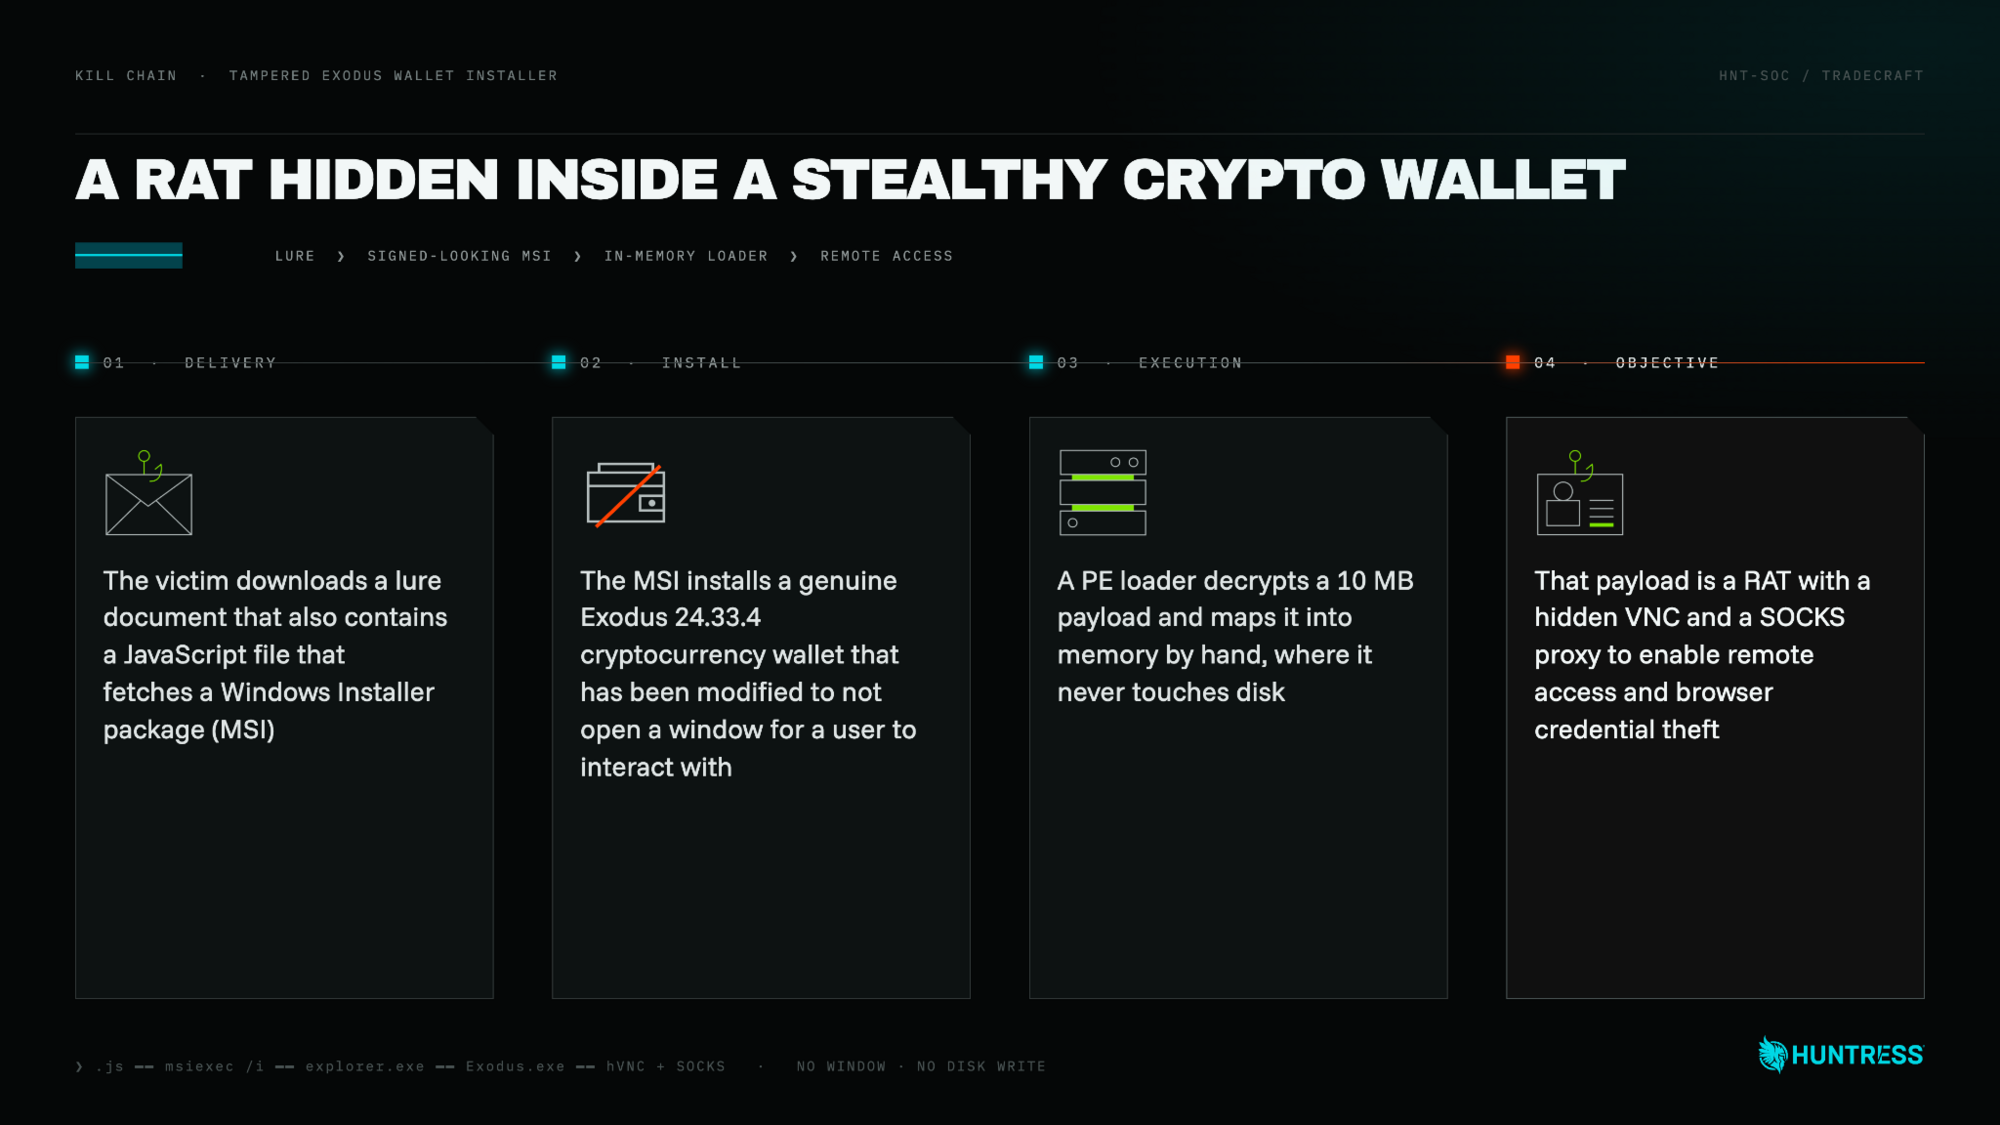
Attackers distributed a trojanized Exodus Wallet installer that silently installed a hidden, modified wallet and a modular RAT with browser theft, VNC, SOCKS proxy, and command execution capabilities. The campaign used fake documents, ZIP-delivered JavaScript, WebDAV search-ms redirection, and Azure Table Storage C2, while artifacts such as jn0101.msi, jg0384.msi, ExodusHelper, and ExdBackupTool helped reveal the operation. #Exodus #ExodusHelper #ExdBackupTool #AzureTableStorage #us05org #jn0101msi #jg0384msi
August’s security briefing covers ChainDrop’s rapid npm supply chain poisoning, Ghostjacking attacks against AI coding agents, and incidents where Claude Code was used in ransomware intrusions. It also highlights Sysdig’s finding that most AI-enabled attacks relied on ordinary command execution, along with Cl0p’s exploitation of PTC Windchill and broader governance updates from OWASP, CIRCIA, and NIST. #ShaiHulud #ChainDrop #ClaudeCode #PTCWindchill #Cl0p #NIST #CIRCIA
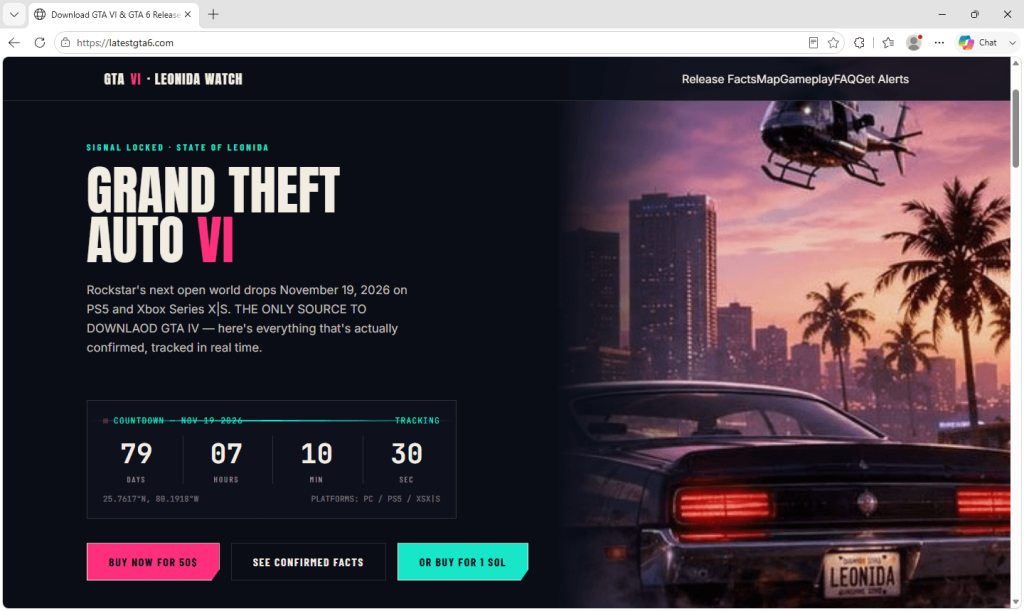
Scam sites impersonating GTA 6 are using fake countdown pages, leaked-copy offers, and wallet-draining code to steal cryptocurrency and digital assets from visitors. The campaign combines convincing Rockstar details with deceptive approval requests, region blocking, and reusable drainer infrastructure to target wallets across multiple blockchain networks. #GTA6 #Rockstar #Solana #Phantom…

A forum actor using the name NOTORIOUS claimed to have released 3.23 GB of files tied to the City Government of Baguio in the Philippines for free. The samples reportedly include building permit records and a Professional Regulation Commission ID card with sensitive names, addresses, title numbers, and licence details. #CityGovernmentOfBaguio…
A forum actor using the name NOTORIOUS claims to be selling 1.71 TB of files allegedly taken from the Summerville Police Department, including internal intelligence records and personal identity documents. The report is unverified, but the sample data suggests possible exposure of sensitive law enforcement information and complete identity kits. #SummervillePoliceDepartment…
A forum actor using the name Kazu is allegedly selling a 2026 dump from MyVete, a veterinary practice management platform, claiming 5,571,174 user personal records for 4,000 dollars. The post is unverified and provides no sample, schema, or field list in the thread, with samples only offered through a private channel….
Kaspersky identified two previously undocumented cross-platform RAT families, NodeRabbit and PollCat, used by Mirage Kitten in trojanized coding challenges delivered through recruiter lures on LinkedIn and other job platforms. The campaign targets Windows, Linux, and macOS, with infrastructure and lures tied to domains and services including Amazon S3, Azure Websites, Cloudflare, and the domains oracle-challenge.s3[.]us-east-1.amazonaws[.]com, plugplay.azurewebsites[.]net, and lifespotify[.]com. #MirageKitten #NodeRabbit #PollCat #LinkedIn #AmazonS3 #AzureWebsites #Cloudflare
Akira ransomware has claimed responsibility for attacking Flex1, an innovative desktop-as-a-service provider, alleging they will upload 402GB of corporate data shortly. The threat actor claims exposure includes employee personal information, clients’ information such as lawyers’ case documents (including passports, driver’s licenses, and SSNs), pet clinic data, financial information, and other records. #countryname
Congressional Iron Works, a Maryland-based full-service miscellaneous metals contractor serving the Baltimore–Washington commercial construction industry, reported a ransomware incident attributed to Akira, impacting corporate data including employee personal information (passport numbers, SSNs, driver’s licenses, financial and health data), client information, company financials, projects, and NDAs. The impacted country is #UnitedStates.
Szechenyi Programiroda Nonprofit Kf in Hungary reported a ransomware incident linked to the rhysida threat actor, resulting in unauthorized access and disruption of its systems. The attack impacted data availability and business operations in #Hungary

BREEZE COMET is a financially motivated threat actor that targets Brazilian financial services, retail, and eCommerce organizations by abusing compromised websites, custom malware, and stolen credentials to manipulate payment systems and fraudulent transfers. The group has also used generative AI to accelerate malware and script development, while expanding its infrastructure and tactics across Latin America and Africa. #BREEZECOMET #COBALTSPIN #REALBREEZE #MILDFROST #KICKPLATE #BOATBEAM #XWORM #ANYDESK