The US Coast Guard has created the Office of Maritime Cybersecurity Policy to centralize cybersecurity policy, compliance, and coordination for the Marine Transportation System as ports and vessels become more dependent on digital technologies. The move comes amid rising cyber risk across maritime critical infrastructure and follows GAO criticism of gaps…

The ransomware claim alleges that thegentlemen targeted CareerSource Palm Beach County (www.careersourcepbc.com), a West Palm Beach, Florida–headquartered nonprofit workforce development organization. The claim states that the organization’s systems were impacted by the ransomware incident in the United States. #UnitedStates
SCHMIDT in the US reported a ransomware incident attributed to the bravox threat actor, impacting Abrasive Blasting Systems and Engineering Solutions for Industry. #UnitedStates
In CO, the ransomware claim alleges that Transportes Montejo S.A.S. was targeted by threat actor nightspire; however, specific data details are not available at this time. The incident is reported to have impacted #Colombia
A whistleblower complaint alleges the U.S. Postal Service is rushing to deploy untested IT systems that could block thousands of mail-in ballots ahead of the 2026 midterm elections. The disclosure says the new Federal Ballot Mail Portal and related verification tools are being built in a secretive, flawed process that may reject entire ballot batches over single errors. #USPS #FederalBallotMailPortal #RichardBlumenthal #DavidSteiner #RobertGarcia

Tina Peters says she will not take a formal role in Shasta County elections, after previously being considered as a consultant or assistant registrar following her shortened prison sentence. The controversy follows her conviction for stealing Mesa County voting machine software and her continued claims that electronic voting systems are untrustworthy, despite officials and experts citing paper backups and audits. #TinaPeters #MesaCounty #ShastaCounty #ClintCurtis #JaredPolis #ShirleyWeber
The FBI warned that attackers are using OAuth consent phishing on a commercial messaging app to target high-profile people, their families, and acquaintances, tricking them into granting access to legitimate cloud services like Microsoft or Google. Once approved, the malicious app can maintain persistent access to emails, files, and other sensitive data even if the victim changes their password. #FBI #Microsoft #Google #OAuth

AI coding agents in large codebases need more than local code access; they need continuously updated organizational context about services, APIs, consumers, and sensitive dataflows to make safe changes. The article argues for deterministic static analysis plus MCP delivery as a shared evidence layer for AI coding, privacy, compliance, security, SOC investigations, and AI governance. #Anthropic #ClaudeCode #MCP #HoundDogai #Replit #OpenAI #LangChain #ISO42001 #FedRAMP
Aesto Health disclosed a data breach affecting more than 9.5 million people after unauthorized access to a portion of its Amazon Web Services infrastructure exposed sensitive patient information. The incident may have impacted patients linked to multiple healthcare providers, and the company is offering 24-month identity theft protection and credit monitoring through Experian. #AestoHealth #AWS #VillageMD #EversideHealth #MaranaHealth #TogetherWomensHealth
Phishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect. Huntress observed the campaign delivering Faronics-themed lures to more than 457 endpoints and noted that Faronics has since added anti-abuse measures and contacted affected organizations. #FaronicsDeploy #ConnectWiseScreenConnect #Huntress
Sevii has expanded its Autonomous Defense & Remediation platform with an AI security module that detects and responds to AI-driven attacks in real time. The module uses AI agents to validate incidents, hunt for broader impact, and autonomously remediate threats within minutes to limit damage. #Sevii #CurtAubley #OpenAI #HuggingFace…
Palo Alto Networks has acquired Console, an AI-native platform that will strengthen Cortex by enabling security teams to build agentic workflows and automate responses using natural language. The announcement came alongside strong fiscal Q4 2026 results, including 34% revenue growth to $3.41 billion and guidance for continued expansion in fiscal 2027….
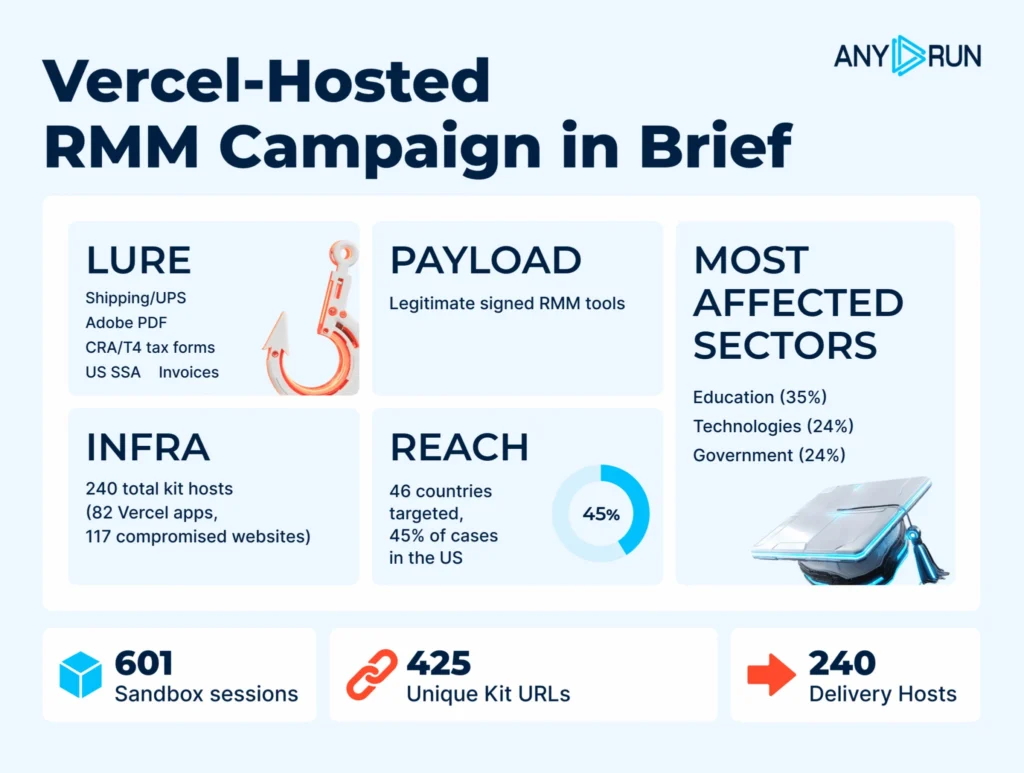
August’s attacks showed that attackers increasingly exploit trusted business activity, from Microsoft 365 sessions and hiring workflows to remote-management tools and business-themed files, to gain access and maintain control. The incidents involving Mirage2FA, 3DBlast, SnakeBiteAgent, the US-first RMM campaign, and Famous Chollima highlight how identity compromise, session theft, and insider-style access…
CIS CTI identified an active phishing campaign targeting U.S. SLTT networks with a custom PowerShell WebSocket RAT that leads to persistent dual-RMM access through ScreenConnect and Pulseway. The operation uses Google Drive lures, Google Cloud Storage infrastructure, and continuously updated delivery variants that align with the cargo theft and freight fraud…
BYK Construction, a trusted home builder in Mount Vernon, Washington, fell victim to ransomware activity attributed to the Akira threat actor, resulting in the theft and impending release of approximately 27GB of corporate data. The exfiltrated information includes employee personal data (SSNs, passport numbers, driver’s licenses, and financial details), client information, company financial records, and project specifications, impacting #UnitedStates.