
Chaotic Eclipse disclosed FalconFlank, a zero-day privilege escalation flaw in CrowdStrike Falcon that abuses office malicious macros remediation in the Falcon Sensor and may already have detections. The researcher also recently published PoCs for HardBreacher in Kaspersky Endpoint Security and ShieldBreak in Microsoft Defender, both of which target Windows security products…
David Halbreich of Reed Smith explains how AI companies can avoid insurance coverage gaps as mergers, application disclosures, model degradation, and cloud outages create new D&O, E&O, and business interruption risks. He emphasizes careful policy review, tighter application wording, broader retroactive dates, and stronger dependent vendor coverage to prevent straddle claims and denial issues. #ReedSmith #DavidHalbreich #D&O #E&O #ModelDegradation #CloudOutages

Shared threat intelligence can improve protection only when organizations treat feeds as live replicas of someone else’s database, with strong controls for provenance, rollback, and validation. GitHub’s Dependabot experience shows that ingesting malicious-package intelligence across ecosystems demands careful normalization, echo suppression, and loud failure handling to avoid automating upstream mistakes into downstream harm. #Dependabot #GitHub #OpenSSF #npm

A forum actor known as Keishell claims to have published Pattons Shipping Records from the myTnT shipment database tied to pattons.com.au, exposing detailed carrier portal data. The alleged records include shipment and billing information, customer contact details, customs data, declared goods values, and delivery details, but the claim remains unverified. #pattons.com.au…
A forum actor called mondial claimed to have published two datasets attributed to France’s Ministry for Ecological Transition, including a staff directory and a register of certified controllers. The post says the data came from an API misconfiguration and an access control flaw, but the claim remains unverified. #developpementdurablegouvfr #MinistryforEcologicalTransition #mondial…

Multiver Lt,ée, based in Canada (CA), was targeted by the incransom ransomware group, which specialized in disrupting organizations through encryption and extortion. Multiver Lt,ée manufactures glass products ranging from sealed to tempered and shaped glass, serving architectural projects with high-quality design-focused offerings. #Canada
Incransom ransomware targeted Policlinico Triestino in Italy, encrypting critical systems and disrupting services across the organization. The incident impacted healthcare operations in #Italy

One defacement incident was reported against the Brazilian target https://setebarras.sp.gov.br, with the attacker identified as dr3n4k. The countries targeted were Brazil, and the attacker involved was dr3n4k. #Brazil…
A threat actor is actively exploiting the recently patched CVE-2026-9586 SQL injection flaw in internet-exposed Sangoma Switchvox instances, dropping reverse shells and later staging additional malware. Organizations using Switchvox should immediately check for compromise, review the listed indicators of compromise, and restrict access to the Switchvox interfaces and /pa endpoint if they cannot update. #CVE-2026-9586 #SangomaSwitchvox #Horizon3 #DefusedCyber #Asterisk

Nearly 22,000 Microsoft Exchange servers are still unpatched against CVE-2026-62911, a critical authentication bypass flaw that can let an authorized attacker elevate privileges over the network. The United States and Germany have the highest numbers of vulnerable servers, while NCSC-NL and BSI have urged immediate patching as a working exploit is reportedly circulating online. #CVE-2026-62911 #MicrosoftExchangeServer #NCSC-NL #BSI #OrangeTsai #DEVCOREResearchTeam #TrendMicroZeroDayInitiative
The FBI said a 17-year-old from Maine became the first child federally charged and adjudicated for crimes tied to 764, a violent extremist collective linked to abuse, threats, stalking, and identity theft. The case marks a significant shift in law enforcement’s response to underage members of 764 and The Com, as officials move to close what they describe as a loophole that has enabled serious crimes by minors. #764 #TheCom #FBI

AI coding agents have evolved into extensible runtimes where skills, plugins, hooks, and MCP servers can reshape what they read, execute, and disclose. Security teams must govern the agent supply chain itself, because approved tools like Claude Code, OpenAI Codex, Claude Cowork, and GitHub Copilot can hide dangerous third-party capabilities behind trusted interfaces. #ClaudeCode #OpenAICodex #ClaudeCowork #GitHubCopilot #Hookify #MCPoison #Akto
SilentRansomGroup reportedly targeted Greenberg Traurig, a multinational law firm headquartered in the United States that provides legal services across corporate, real estate, litigation, intellectual property, and government affairs. The ransomware claim indicates disruption to the firm’s operations in the impacted country(s): #UnitedStates
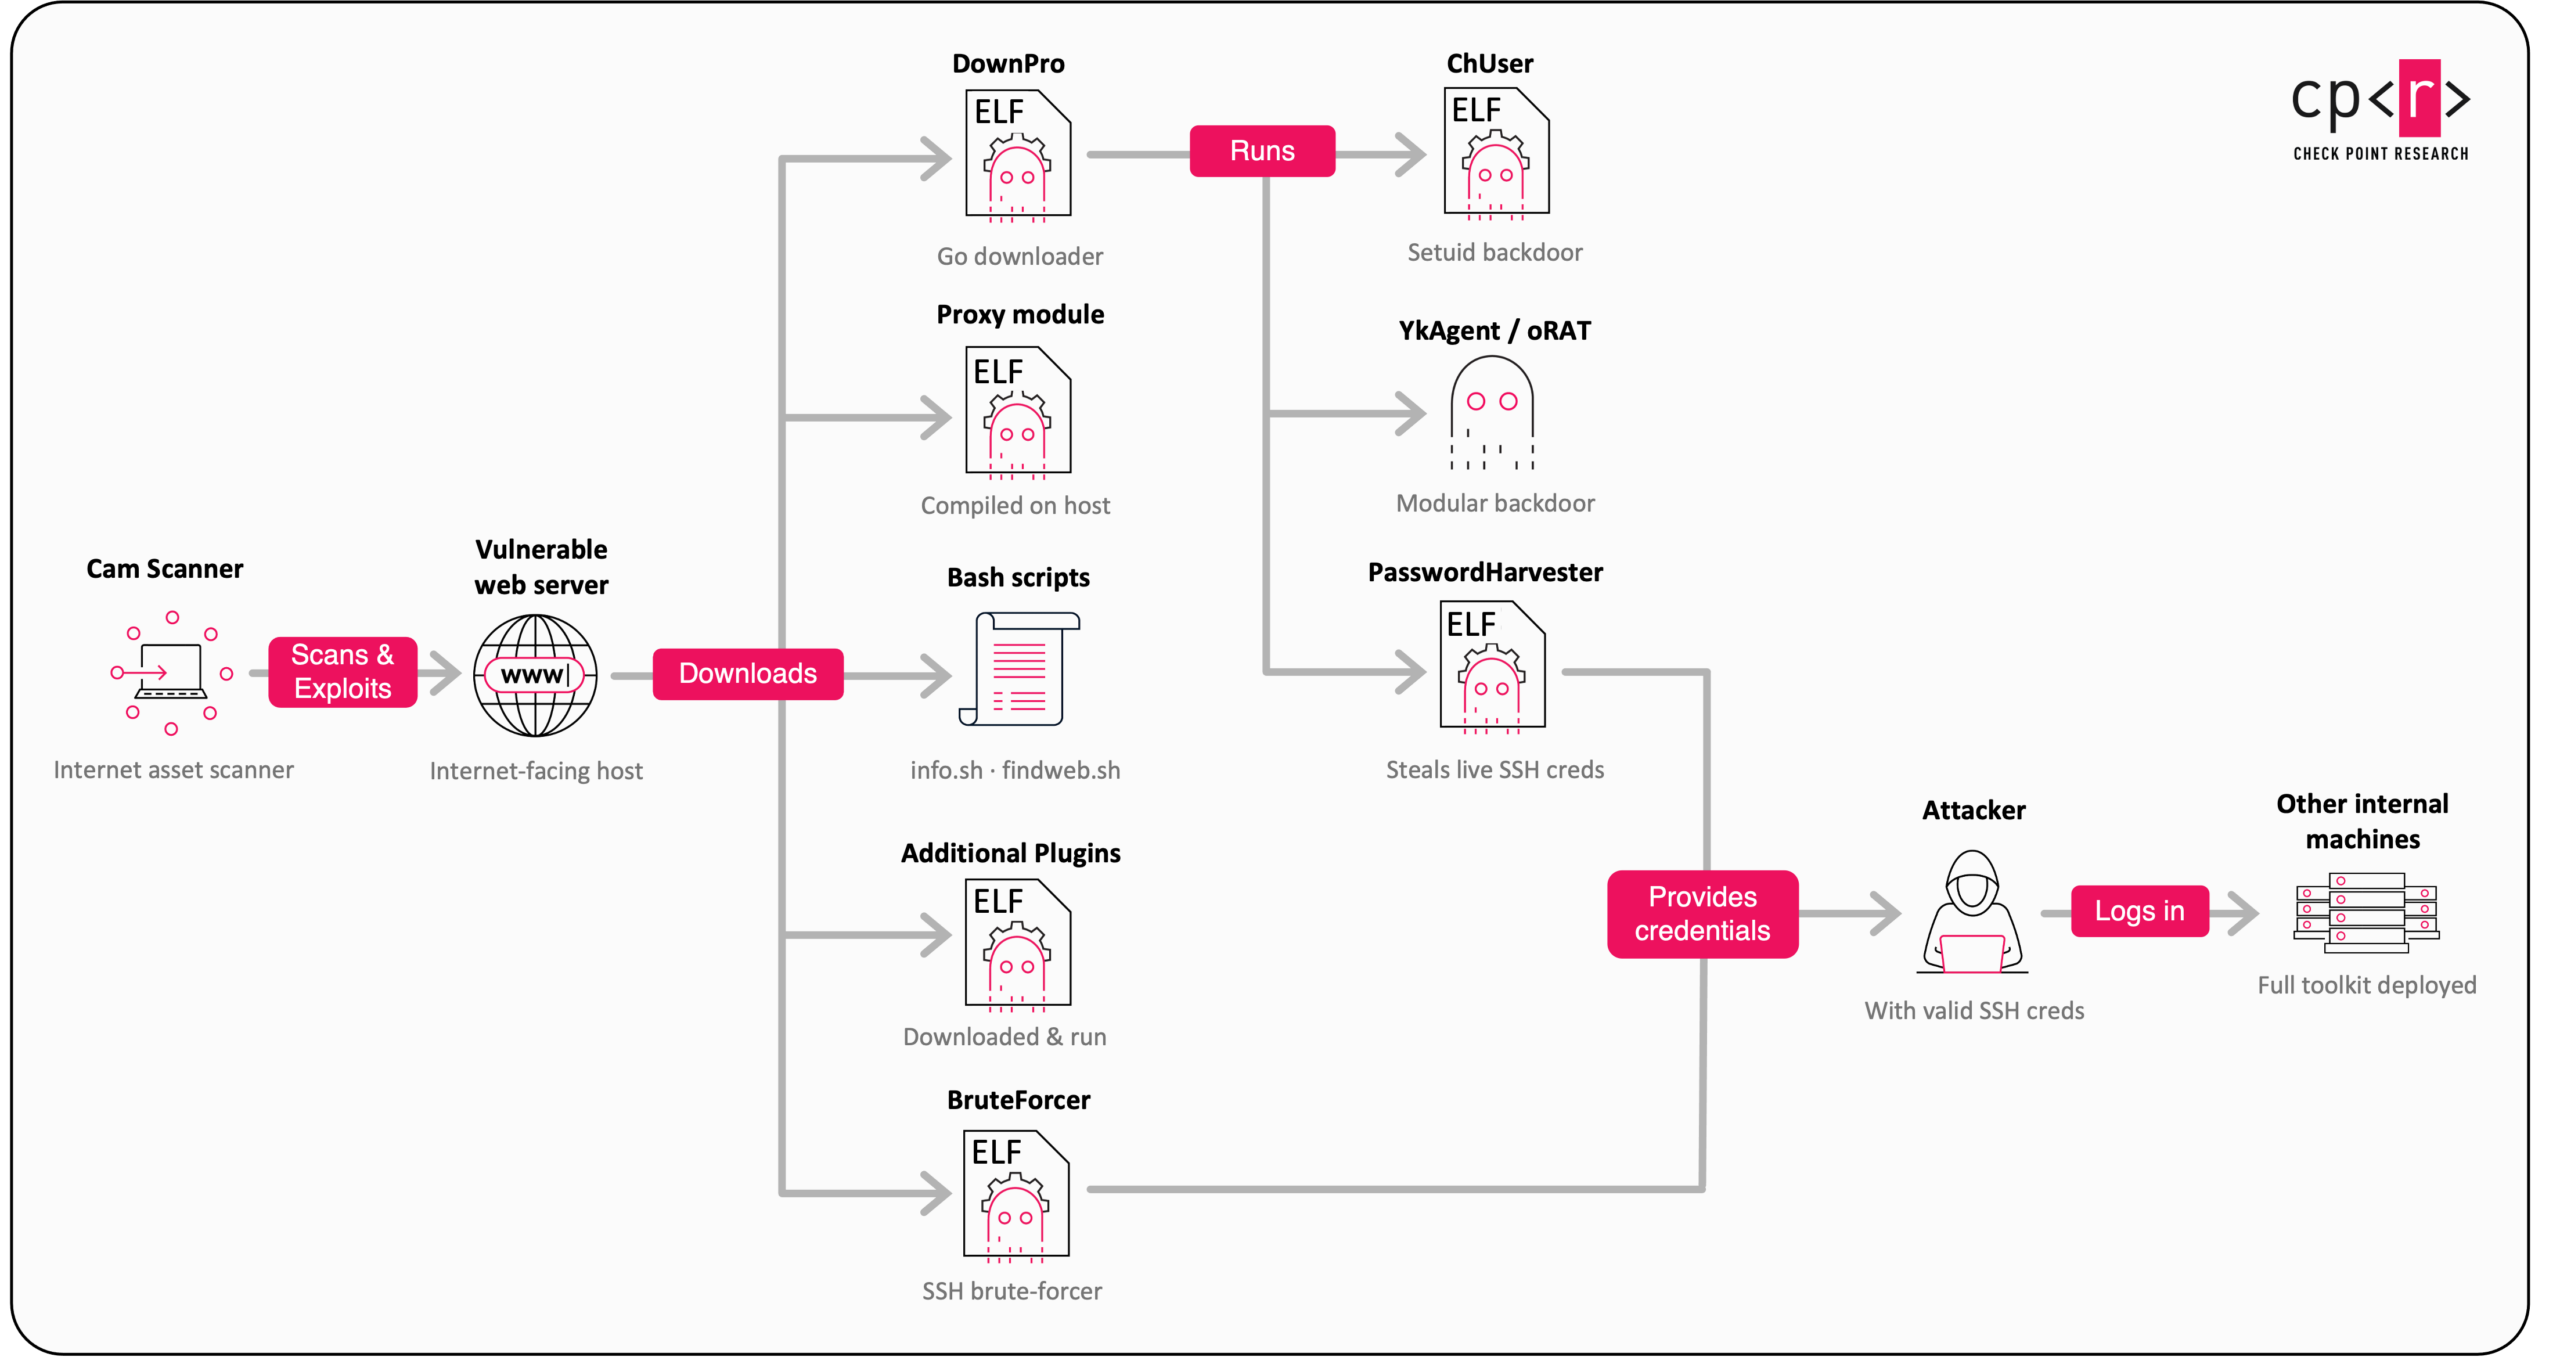
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon
Check Point Research describes Gambling Goblin, a Chinese-speaking cybercrime group linked to Earth Berberoka, as running a sustained campaign against Brazilian government and educational organizations since mid-2025. The operation uses malicious Apache modules, SEO manipulation, and a large Linux toolkit to hijack traffic, serve phishing pages that impersonate Google Play, Microsoft Store, and Amazon, and scale into Vietnamese, Spanish, and English targeting. #GamblingGoblin #EarthBerberoka #Apache #GooglePlay #MicrosoftStore #Amazon
Aesto disclosed that more than 9.5 million people had sensitive information exposed after hackers breached its Amazon Web Services infrastructure in December, affecting at least 30 healthcare organizations. The leaked data included Social Security numbers, medical and financial information, while other healthcare firms such as Baylor Genetics, CareCloud, and Park Dental…