Meta launched Muse, a personal AI agent for adults in the U.S. that helps with everyday tasks, long-term planning, and taking actions like opening a browser, filling out forms, and sending emails. The company says Muse runs in a dedicated secure virtual machine and reflects Mark Zuckerberg’s vision of AI agents…
The NSA, CISA, and FBI say several China-based AI companies have been extracting knowledge from U.S. frontier models through large-scale distillation, affecting models from Claude, GPT, Gemini, and Grok. The agencies warn this activity threatens U.S. technological leadership, with DeepSeek and Moonshot AI among the companies named in the report. #DeepSeek…
Zimperium’s zLabs uncovered Mantax Otax v2, a highly aggressive Android threat linked to Indonesian actors that combines spyware, data theft, remote surveillance, and ransomware in one campaign. It uses phishing and sideloaded APKs, then steals credentials and personal data, records screens and photos, and encrypts files on older Android devices while coordinating extortion through Firebase and a dynamic C2 infrastructure. #MantaxOtax #Firebase #Android
U.S. agencies say China-based AI companies have been running large-scale knowledge distillation campaigns to copy advanced capabilities from frontier models such as Claude, GPT, Gemini, and Grok. The advisory names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, and warns providers to strengthen verification, monitoring, and output controls to slow extraction efforts. #DeepSeek #MoonshotAI #AlibabaGroup #MiniMax #StepFun #ZAI #Claude #GPT #Gemini #Grok #CISA #NSA #FBI

Zscaler has introduced Zscaler Agentic SOC, an AI-first security operations model designed to proactively reduce exposures, detect threats faster, and contain attacks at machine speed. The platform combines Zscaler telemetry, Zero Trust controls, expert-validated AI agents, and integrations with Anthropic and OpenAI to counter AI-driven attacks and evasive tactics like trusted-site abuse, remote management tool misuse, and browser-based attacks. #Zscaler #Anthropic #OpenAI #Threatlabz #RedCanary #AgenticSOC
Sophos found a rootkit on compromised F5 BIG-IP APM devices that hides a web shell in memory instead of writing it to disk, making it harder for file-based security tools to detect. The campaign is linked to exploited F5 BIG-IP APM activity, including CVE-2025-53521, and uses staged malware with deeper Apache and PHP interception techniques. #F5BIGIPAPM #CVE202553521 #PoisonedRefresh

Storm ransomware actors claimed an attack against Lowerys, a Canadian office supplies, printing, photocopying, and managed IT services provider with operations in Thunder Bay and Fort Frances, headquartered at 540 Central Avenue, Thunder Bay, ON. The impact was reported in Canada. #Canada
Storm ransomware operators claimed to have targeted Flexmaster, a Novaflex Group company in Canada, which supplies a wide range of flexible ducting solutions and HVAC accessories from its headquarters in Richmond Hill, Ontario. The incident is reported to have impacted Canada #Canada
In a ransomware claim attributed to Storm, Technology Dynamics Inc. (US), a Bergenfield, New Jersey-based designer and manufacturer of rugged switching power supplies and DC-UPS systems for military, industrial, and commercial customers, reported compromise of sensitive data including full SolidWorks designs and firmware source code. The impacted country(s): #UnitedStates
NSA, CISA, and the FBI warn that China-based AI companies are running industrial-scale knowledge distillation campaigns to extract proprietary capabilities from U.S. frontier AI models, including Claude, GPT, Gemini, and Grok. The advisory names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI as major actors and describes evasive access methods such…

Sophos found that malware tied to intrusions on F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory, allowing the infected files on disk to appear clean. The activity is linked to CVE-2025-53521 and the c05d5254 malware, with related reporting from F5 and ESET’s PoisonedRefresh analysis. #F5 #BIG-IP…

cPanel has patched CVE-2026-67401, a flaw in EmailTrack that could let an authenticated hosting account create files and potentially escalate to root on the entire server. The issue affects all supported cPanel and WHM versions, with fixed builds now available across the 11.110, 11.134, 11.136, 11.138, and WP Squared release lines….

Google has released updates to fix 230 security vulnerabilities in Chrome, including CVE-2026-87491, a V8 out-of-bounds write flaw that is already being exploited in the wild. The update also addresses several critical issues in WebGL, Cast, and WebPackaging, and users are urged to update Chrome immediately for protection. #CVE-2026-87491 #V8 #GoogleChrome…

Conan Yu of Rena Labs argues that AI agents need verifiable protections for data-in-use, since conventional encryption does not stop sensitive information from being exposed while it is processed in memory. His work uses trusted execution environments and remote attestation to help protect confidential AI inference, private financial analysis, and other workloads without relying on trust alone. #ConanYu #RenaLabs #TrustedExecutionEnvironments #RemoteAttestation
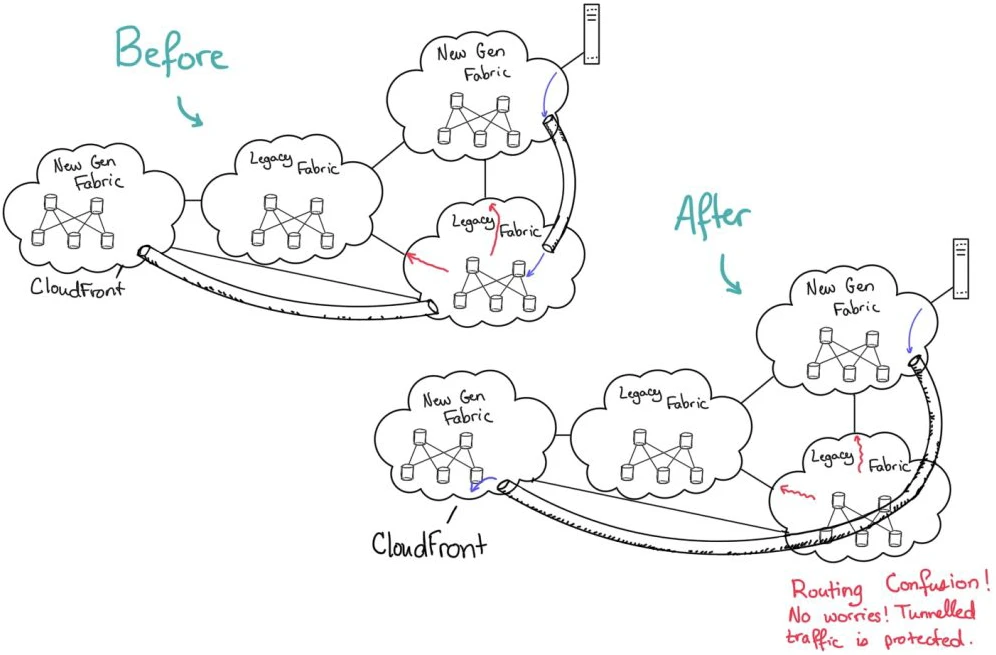
AWS rebuilt its border network routing control plane into a single unified system to improve convergence, reduce packet loss, and keep traffic consistent across its global infrastructure. The migration covered CloudFront, Route 53, Direct Connect, and backbone routers, with AWS reporting up to 96% faster convergence and more predictable latency. #AWS #CloudFront #Route53 #DirectConnect