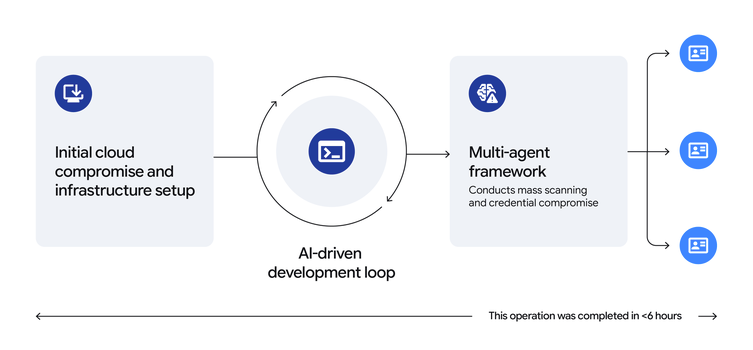
Google’s Threat Intelligence Group says adversaries are increasingly using AI to automate attacks, accelerate credential theft, and scale exploitation across the open-source supply chain. Nation-state-linked groups such as UNC6780, UNC6508, APT42, APT24, and UNC1069 are also leveraging AI for reconnaissance, malware development, social engineering, propaganda, and theft. #UNC6780 #UNC6508 #APT42 #APT24…
HelmGuard has raised $7.3 million in seed funding to expand its agentic governance, risk and compliance platform that continuously collects and evaluates risk signals from source systems. The startup says its AI agents can speed up assessments, unify fragmented compliance data, and help organizations govern AI agents across workflows. #HelmGuard #InfinityVentures…
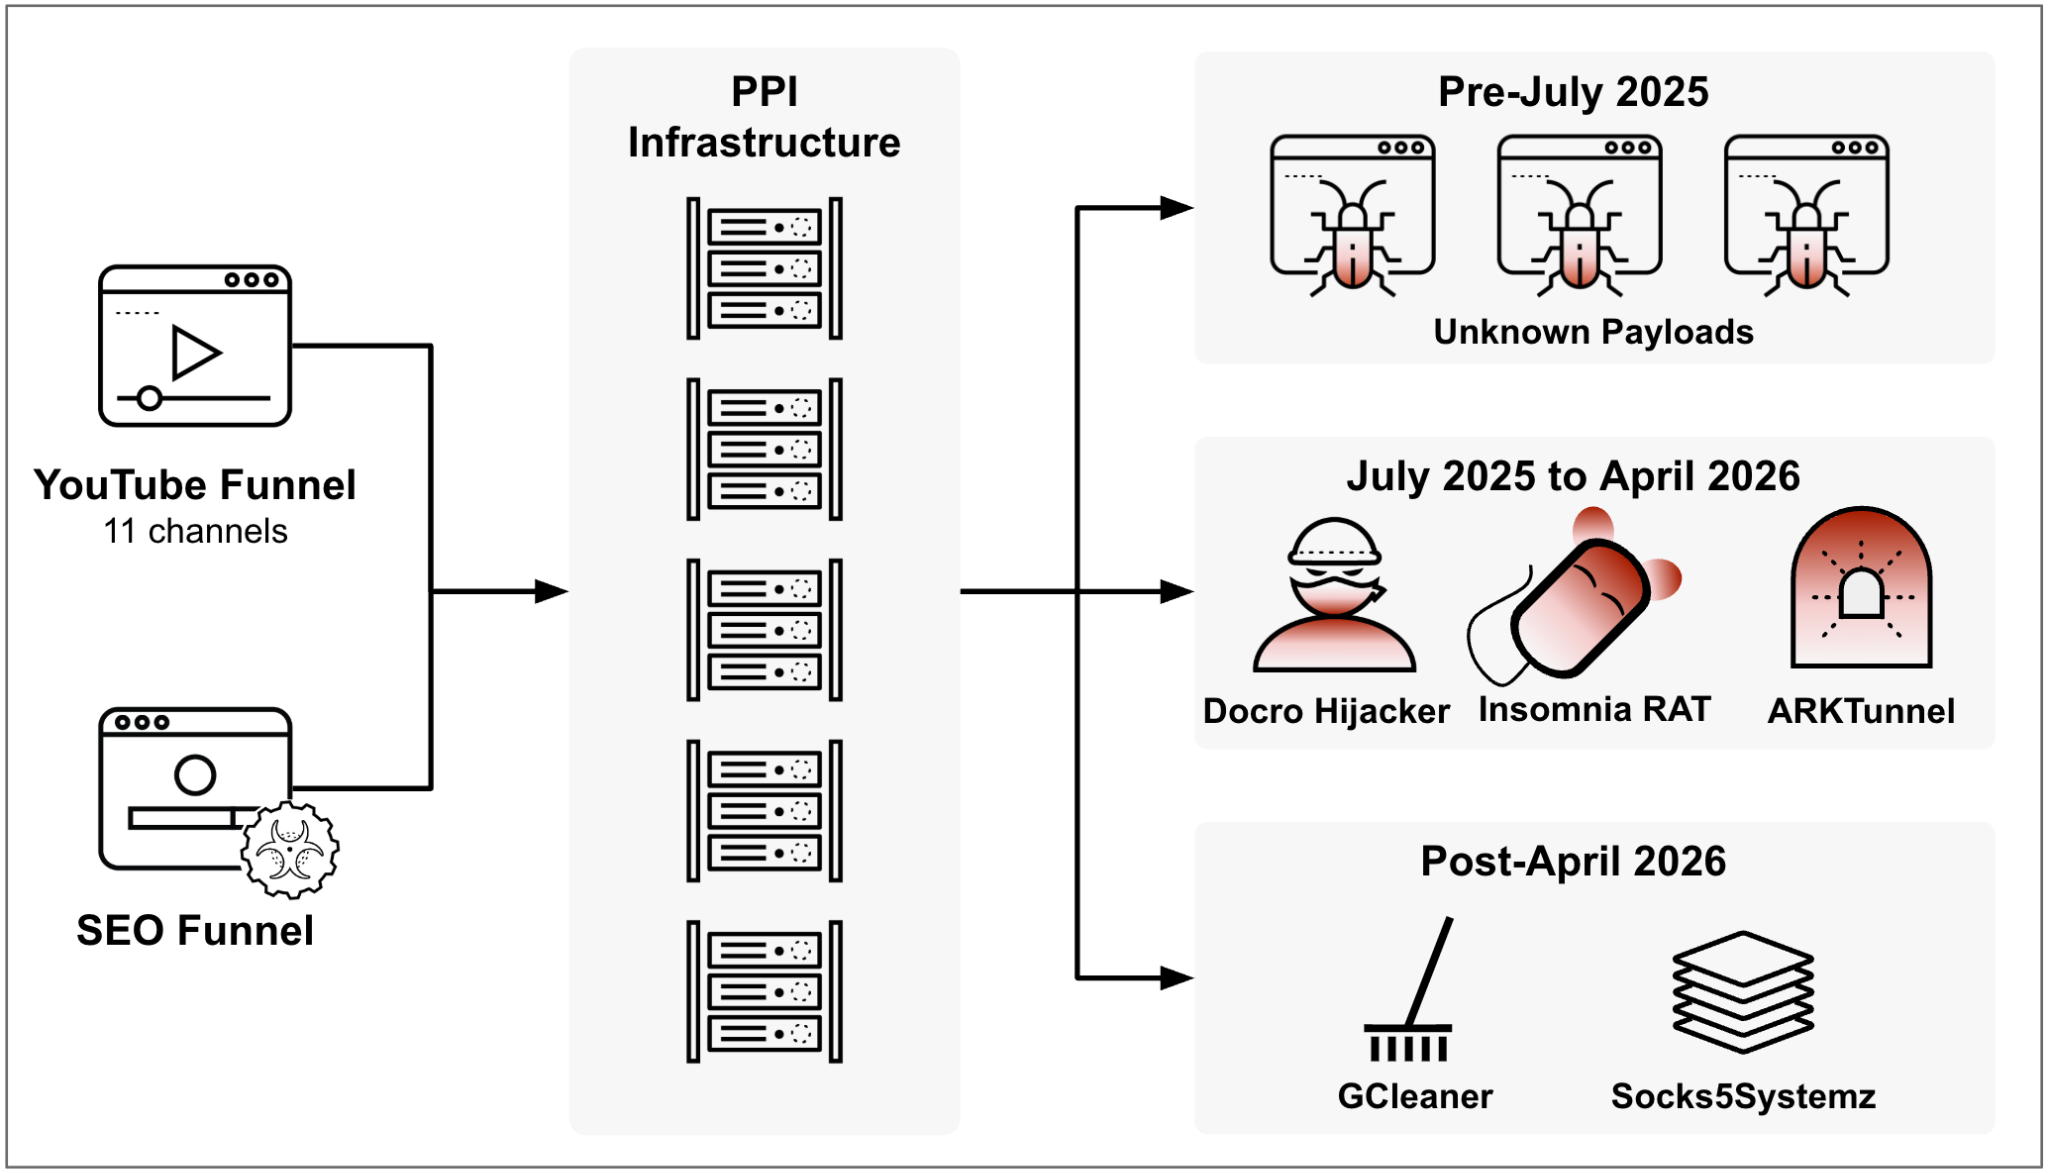
Unit 42 uncovered CL-CRI-1171, a long-running pay-per-install campaign that used OfferLoader to distribute multiple payloads through YouTube gaming videos and SEO-poisoned download pages. The operation delivered Insomnia RAT, ARKTunnel, and Docro Hijacker while hiding behind rotational domains, trojanized installers, and gating checks that filtered out scanners and analysts. #OfferLoader #CL-CRI-1171 #InsomniaRAT…

Akeyless has launched Agentic Runtime Authority to give real-time identity control over AI agent actions, adding intent-based enforcement on top of its SecretlessAI credential protection layer. The solution helps organizations block unsafe agent behavior before execution, while expanding support for Claude Enterprise, OpenAI Codex, and Amazon Bedrock AgentCore. #Akeyless #SecretlessAI #AgenticRuntimeAuthority #ClaudeEnterprise #OpenAICodex #AmazonBedrockAgentCore

FBI officials said AI is accelerating malicious hacking and vulnerability discovery, forcing organizations to move from quarterly patching to continuous, risk-based updates. The new FBI cyber strategy adds AI-enabled defense, victim support, threat intelligence sharing, and expanded disruption efforts against nation-state and cybercriminal actors. #FBI #BillingtonCyberSecuritySummit
The FBI says private-sector organizations are still hesitant to share cyber incident information because of misconceptions about how the bureau uses collected data. Brett Leatherman said the FBI’s new approach is to prioritize victim help, share actionable intelligence quickly, and support efforts against PRC-linked attackers and other nation-state actors. #FBI #BrettLeatherman #PRC

HardenStance’s RSAC 2025 briefing shows that AI was again the dominant theme, with vendors focusing on securing generative AI use by employees and embedding agentic AI into security operations. The report highlights major product launches and research from Akamai, Cisco, CrowdStrike, Google, Palo Alto Networks, Qualys, and Sandbox AQ as the industry shifts from AI experimentation to practical controls, detection, and autonomous defense. #RSAC2025 #Akamai #Cisco #CrowdStrike #Google #PaloAltoNetworks #Qualys #SandboxAQ #Unit42 #PrismaAIRS #CharlotteAI #TotalAI #AQtiveGuard
Plex has warned that more than 36,000 internet-exposed Plex Media Server instances remain unpatched against multiple security flaws affecting Plex Media Server v1.43.2 and earlier. Users are urged to upgrade to Plex Media Server 1.43.3 and Plex Desktop 1.115.0 before attackers reverse-engineer the fixes and exploit the vulnerabilities. #Plex #Shadowserver #CVE-2025-34158 #CVE-2020-5741
Strong authentication controls like MFA, conditional access, and device trust have made account takeover harder, pushing attackers toward weaker recovery processes such as service desk-driven password and MFA resets. Recent incidents involving Scattered Spider and Marks & Spencer show how impersonation and account recovery abuse can bypass defenses and cause major business damage. #ScatteredSpider #MarksandSpencer #EntraID #SpecopsSecureServiceDesk

Kyodo USA, a US-based marine engine spares and ship operations equipment distributor, was targeted by the Akira ransomware group, which threatened to encrypt and leak substantial amounts of corporate data, including sensitive employee documents. The alleged stolen materials include IDs and passports, SSNs, contacts and agreements, financials, confidential customer/project files, and NDAs—impacting #UnitedStates.
The direwolf ransomware group targeted RelyComply AML Platform in Great Britain, disrupting financial software operations through malicious encryption and data destruction. The incident impacted UnitedKingdom #UnitedKingdom
Die Mediengruppe Thiel aus Ludwigsfelde (DE) wurde laut incransom von Ransomware angegriffen und betroffen, wobei die Betriebsabläufe des Unternehmens durch die Verschlüsselung von Daten beeinträchtigt wurden. Die betroffenen Leistungen und Systeme sollen in Deutschland (DE) lahmgelegt worden sein. #Germany
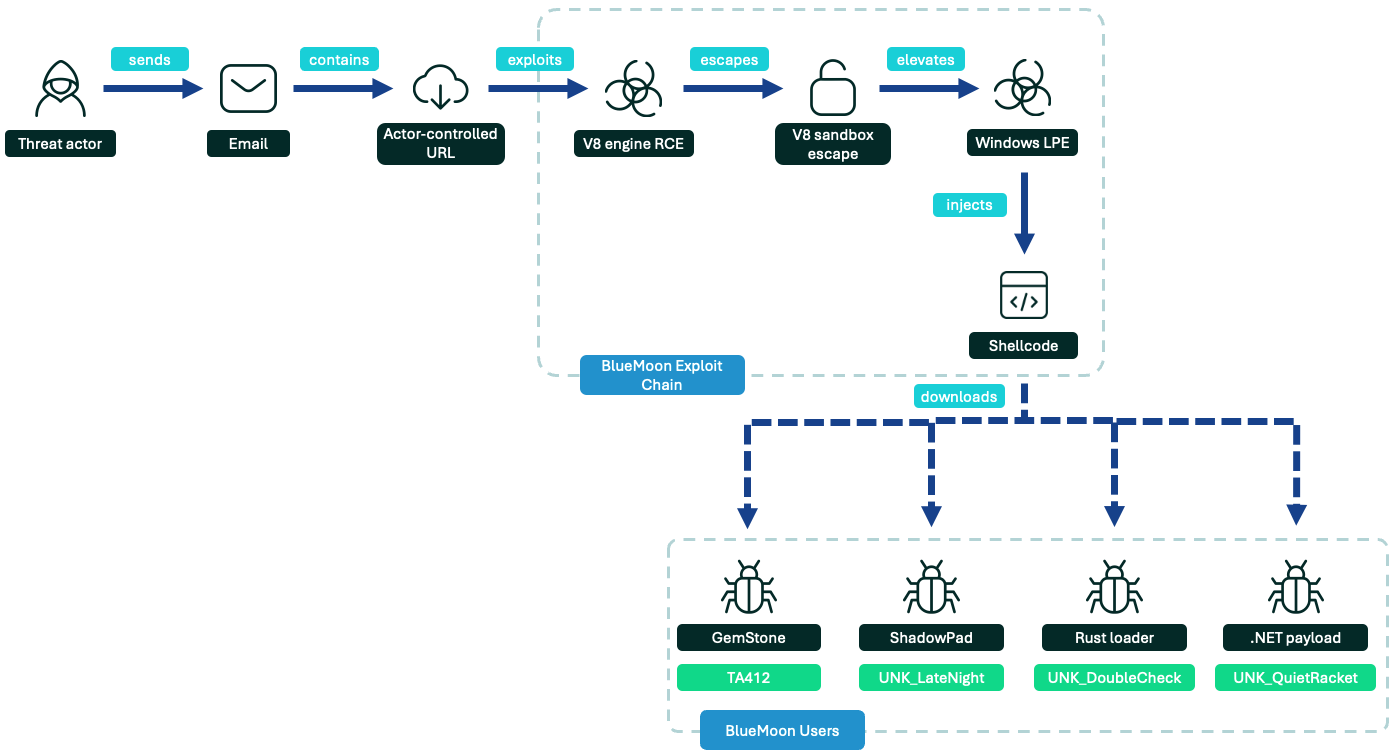
Proofpoint reported that multiple espionage-oriented threat actors rapidly adopted the BlueMoon exploit kit, which chains Chrome V8 and Windows vulnerabilities to deliver different payloads and backdoors. The activity affected US NGOs, US aerospace and defense-related organizations, Vietnamese manufacturing, and targets in Singapore and Indonesia, with notable payloads including GemStone and ShadowPad….

Gojin Motors, an official imported car dealer in South Korea, suffered an external unauthorized access incident and ransomware infection on some of its internal servers, prompting an investigation into possible personal data leakage. The breach has raised concerns over customer identity and service history exposure, which could be abused for phishing and fraud. #GojinMotors
Schneider Electric, Siemens, and Aveva released September 2026 Patch Tuesday advisories addressing multiple vulnerabilities in their industrial control and automation products. The updates include critical flaws such as CVE-2026-3869 in Modicon M580 controllers and CVE-2026-31431 in the Linux kernel, along with several high-severity issues across other ICS platforms. #SchneiderElectric #Siemens #Aveva…