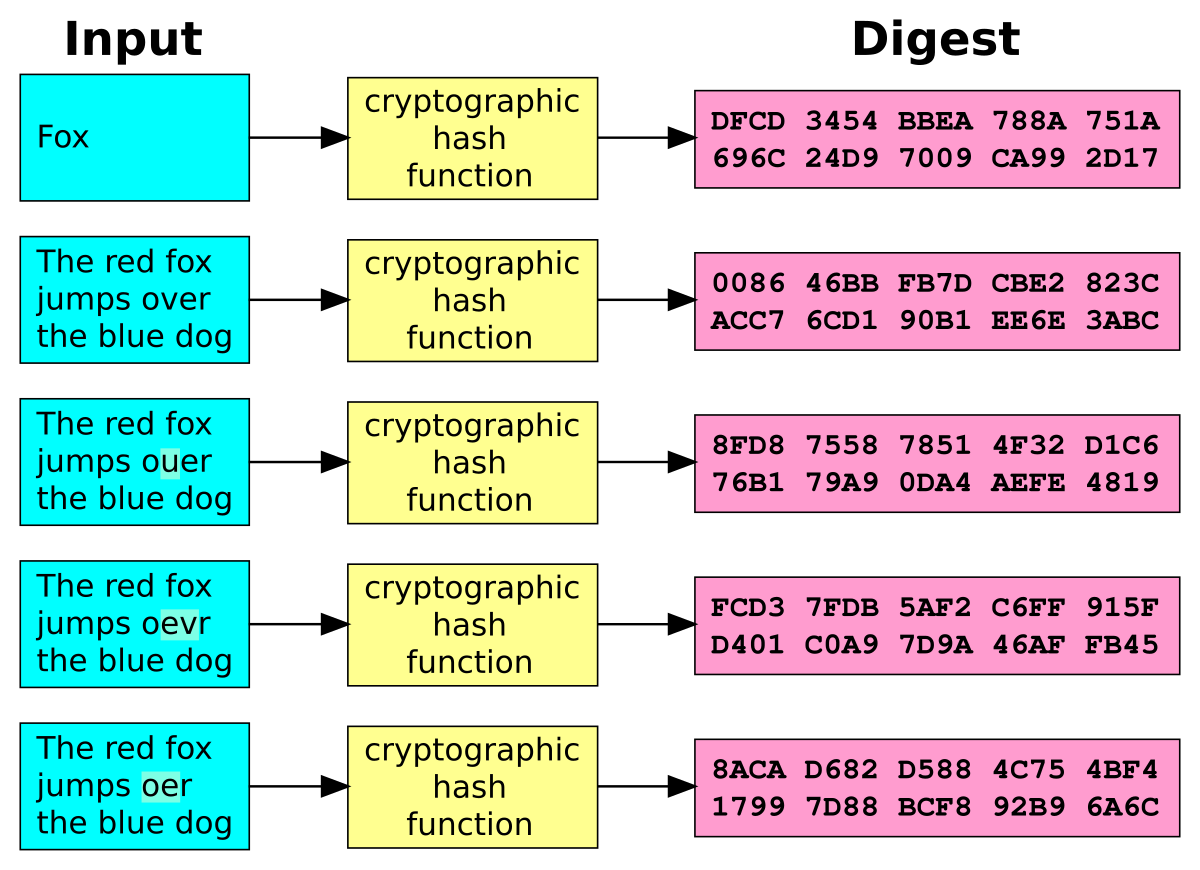
Hashing is a crucial process in information security, transforming input data into fixed-size strings called hash values, which are irreversible and help ensure data integrity, authentication, and password security. It supports various applications like digita…
Category: Interesting Stuff
The article discusses how to efficiently use the OpenCTI platform through its API and Python SDK, allowing users to automate tasks, enhance threat intelligence, and interact programmatically with the system. It highlights authentication, common use cases, bulk…

The article discusses the vulnerabilities in Active Directory (AD) arising from the use of Kerberos authentication, highlighting two new attack techniques: the Diamond Ticket and Sapphire Ticket attacks. Researchers detail how these techniques allow hackers to…
In Episode 2 of the Flipper Zero series, we dive into RFID technology, which underpins access control systems and contactless payments. The Flipper Zero device utilizes RFID capabilities to read, emulate, and write RFID tags, making it a valuable tool for unde…
This article compiles a broad collection of computer forensics tutorials, covering memory analysis, disk imaging, and OS-level investigations. It highlights practical guides across Windows, Android, and Linux using tools such as Volatility, Autopsy, and FTK Im…

The article introduces a GitHub-hosted collection of cybersecurity mindmaps that cover technologies, methodologies, courses, and certifications. The mindmaps are organized in a tree structure and provide brief details on a wide range of tools and topics, with …
Courses to become a “Zero to Hero” in Cyber Security without marketing , you will have to: study a lot (we are talking about a “Hero” right?) study “non-technical” and “unconventional” things (Quality = Hard Skills + Soft Skills) study the same thing more than once (Learn = Repeat + Repe…
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more General • Servers • Vulnerabilities • Exploits • Attack surface • Code • Email addresses&nb…
This article shares insights on preparing for and taking the OSWA certification exam, including effective strategies and personal experiences that led to success. It emphasizes the importance of focused practice and report writing during the process. Affected:…
This article discusses the challenges artists face with generative AI that scrapes their work without consent. It introduces countermeasures like data poisoning, which involves techniques to protect digital art from being used in AI training. Tools such as Pix…
In the Persistence stage of the MITRE ATT&CK framework, attackers establish footholds within systems to maintain access. They may create scheduled tasks that run malicious scripts and add new accounts to preserve their entry even if passwords change. The artic…
The PrintNightmare incident illustrates the grave risks associated with Remote Code Execution (RCE) vulnerabilities in Windows systems. These vulnerabilities allow attackers to execute arbitrary code, leading to severe data breaches and system compromises with…
This article details a challenge based on the IceID banking Trojan, focusing on skills required for blue team analysts, including network traffic analysis, memory forensics, and reverse engineering. By utilizing tools such as VirusTotal and the MITRE ATT&CK fr…

Ransomware attacks are on the rise, with cybercriminals targeting various sectors, especially in the cloud environment. Key vulnerabilities such as poorly configured IAM access and exposed APIs are being exploited. The article discusses incidents like the Code…
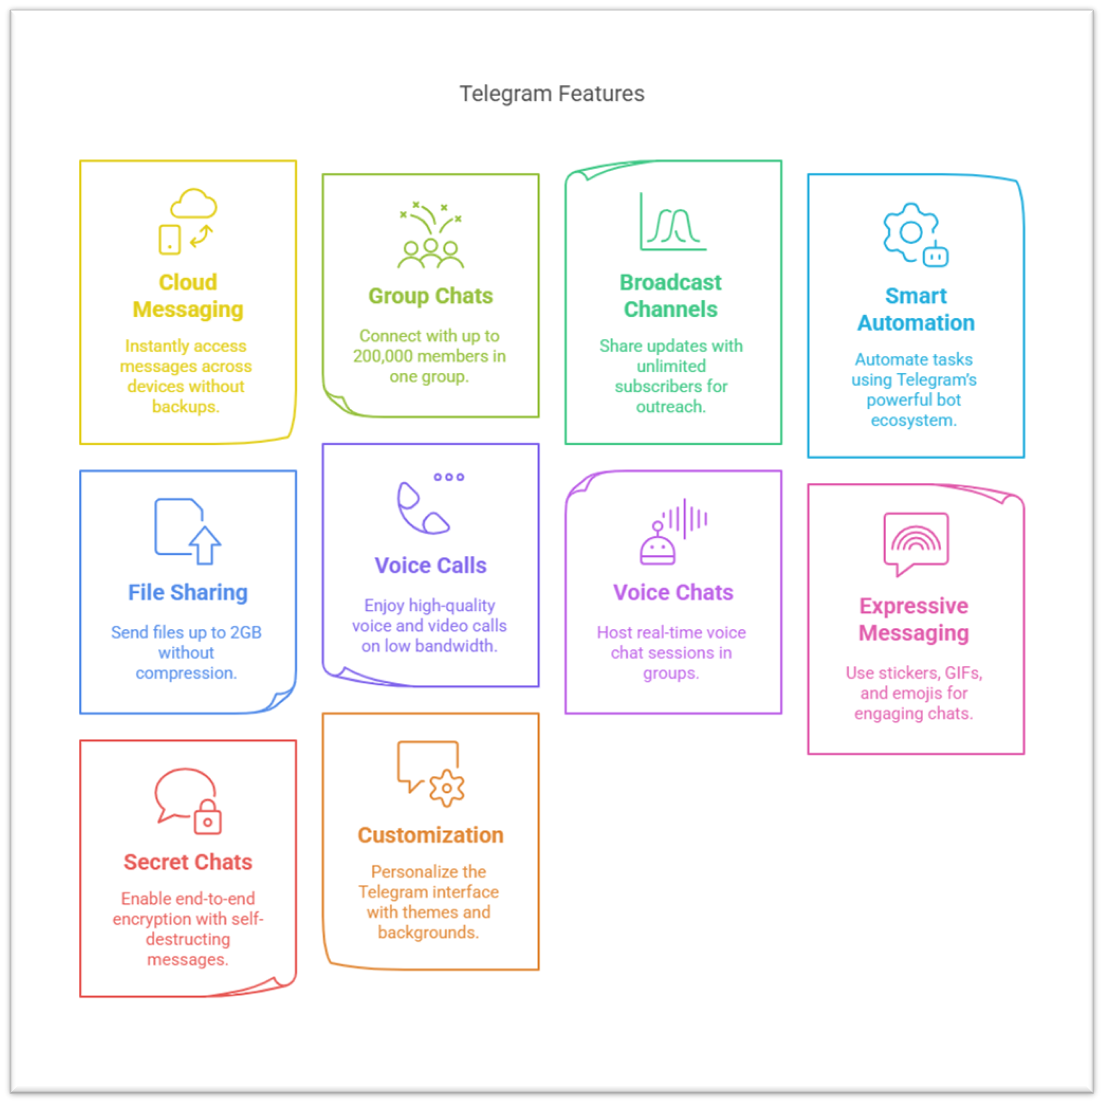
Telegram has rapidly grown into a major messaging platform, praised for speed and privacy features while facing serious challenges like controversies over its role in cybercrime and legal issues. Recent vulnerabilities and criminal activities exploiting its fe…