This article discusses the use of Living Off The Land (LOTL) techniques and PowerShell scripting to extract and process DPAPI credentials stealthily without relying on known malicious binaries. It highlights methods for searching, parsing, exfiltrating, and decrypting DPAPI blobs using in-memory and fileless approaches to evade detection systems. #DPAPICredentials #LOTL #PowerShell
Category: Interesting Stuff

The “State of Security 2025” report emphasizes the critical internal challenges faced by SOCs, such as tool management and data gaps, while highlighting the transformative role of AI and automation. It underscores future strategies for creating efficient, unified, and resilient security operations. #Splunk #StateOfSecurity2025

The ESC15 vulnerability targets Active Directory Certificate Services (AD CS), allowing attackers to inject unauthorized EKUs into Schema Version 1 templates and escalate privileges. Organizations must act swiftly to implement mitigation measures and ensure their certificate templates are secure. #ESC15 #ActiveDirectoryCertificateServices

This guide explains how to build a distributed command execution system using Celery and Redis to enhance bug bounty reconnaissance. It highlights the advantages of parallel processing, automation, and scalability for scanning large scopes efficiently. #Celery #Redis #BugBountyTools #DistributedCommandExecution
Offensive X 2025 in Athens brought together cybersecurity experts to share practical offensive security techniques through workshops, talks, and hands-on activities. The event featured a Capture The Flag competition, hacking villages, and an inclusive community atmosphere. #OffensiveX2025 #CaptureTheFlag #RedTeam #HackingVillage

This article highlights the risks of privilege escalation in AWS environments through misconfigured IAM roles and trust policies. It provides a detailed guide on setting up vulnerable IAM configurations, executing enumeration, and exploiting role assumption for privilege escalation. #IAMRole #PrivilegeEscalation
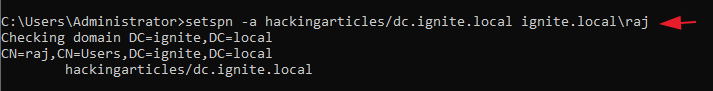
This article explains how Kerberoasting is a covert attack technique exploiting Service Principal Names (SPNs) in Active Directory to recover service account passwords. It details methods of exploitation, detection, and mitigation strategies to defend against this threat. #Kerberoasting #ActiveDirectory #SPN #MITRE T1558.003

This article explores the roles of severity and confidence in detection alerts within cybersecurity operations, emphasizing their proper use and potential misuse. It discusses how to improve detection accuracy and prioritize responses effectively through metrics like a unified “alert priority” score. #DetectionRules #ConfidenceScores

Printed QR codes can be exploited for cyber fraud by hiding malicious links and phishing forms, leading to data theft and malware attacks. Users should verify QR codes and avoid dynamic links to stay protected from silent, smart cyber threats in 2025. #QRCodeHacking #DataTheft

Pratik Dabhi shares a detailed account of how he bypassed SSRF protections on a corporate website by chaining it with an open redirect vulnerability. This method allowed internal network scanning and potential access to sensitive internal and cloud services. #SSRF #OpenRedirect

AI systems have become essential in various applications but are increasingly targeted by sophisticated attacks such as data poisoning, model extraction, and prompt injections. Implementing structured AI penetration testing, leveraging frameworks like MITRE ATLAS and IBM ART, is critical for organizations to identify vulnerabilities and build resilient AI models. #MITREATLAS #IBMART
This article explores the GPIO features of the Flipper Zero device, highlighting its versatility for connecting various modules such as ESP32, NRF24, and CC1101. It also demonstrates practical applications like a Rickroll attack using Momentum Firmware. #FlipperZero #GPIO #MomentumFirmware #ESP32 #RFID

This article discusses the vulnerabilities associated with PendingIntent in Android apps, focusing on potential hijacking and data leaks. It highlights how misconfigured PendingIntents, especially with implicit intents and mutable flags, can be exploited to access sensitive information like contacts.#PendingIntentHijacking #AndroidSecurity

This article discusses common final-stage techniques used by ransomware attackers to evade detection, disable security measures, and cover their tracks. Detecting activities such as system modifications, data exfiltration, log cleaning, backup deletion, and ransom note delivery is crucial for effective incident response. #bcdedit #PowerShell #VSSadmin #RansomwareExtensions

ESC14 targets weak certificate mappings in Active Directory, allowing attackers to impersonate privileged users through manipulation of altSecurityIdentities. Proper certificate validation and strict access controls are essential to prevent such exploits. #ESC14 #ActiveDirectoryCertificateServices