The Honeywell 2025 Cyber Threat Report highlights increased ransomware incidents, notably by the CL0P group, and a surge in USB-carried Trojan and worm attacks like Win32.Worm.Ramnit. It emphasizes evolving operational technology risks across sectors such as water, transportation, and agriculture, alongside detailed recommendations for enhanced industrial cybersecurity practices. #CL0P #Win32WormRamnit #HoneywellAMIR #HoneywellSMX
Category: Interesting Stuff

The 2025 Cyber Claims Report provides detailed insights into the global cyber threat landscape, highlighting a 7% decrease in claims frequency and the ongoing prevalence of email-based attacks like Business Email Compromise (BEC) and Funds Transfer Fraud (FTF). Key findings also include a significant reduction in ransomware severity and ransom demands, alongside the effectiveness of Active Insurance in reducing claims. #BusinessEmailCompromise #FundsTransferFraud #Ransomware #CoalitionInsurance
This annual cybersecurity report reveals a 44% employee engagement rate with Vendor Email Compromise (VEC) attacks, exposing significant financial risks exceeding $300 million. The analysis highlights the rising sophistication of attacks aided by AI, sector and regional vulnerabilities, and the critical role of behavioral AI in defending against human-centric threats. #VendorEmailCompromise #BehavioralAI
The Wipro State of Cybersecurity Report 2025 provides an extensive analysis of the current cybersecurity landscape, highlighting key trends such as the rise of AI-driven attacks, nation-state cyber warfare, and evolving cyber capabilities within organizations. It emphasizes strategic investment priorities like Zero Trust frameworks and AI-based threat detection while underscoring challenges including AI implementation and budget constraints. #NationStateCyberWarfare #EmailPhishing #ZeroTrust #ArtificialIntelligence
The 2025 Crypto Crime Report details significant trends in illicit cryptocurrency use in 2024, highlighting declines in illicit volume on TRON, expanded terrorist financing via crypto, and record-high ransomware demands. The report also underscores the shifting tactics of threat actors and emphasizes the importance of international collaboration in tackling crypto crime. #TRON #IslamicStateKhurasanProvince #DarkAngelsRansomware #NorthKoreaCryptoThefts

Shadow AI refers to GenAI-powered tools, browser extensions, and agentic browsers that run inside the browser, creating an unmanaged AI execution environment with security visibility gaps. The article outlines six risks, a real-world Perplexity Comet Attack example, and recommended defenses such as browser session monitoring, clear AI-use policies, identity controls, and employee education. #ShadowAI #PerplexityCometAttack
November’s report highlights urgent vulnerabilities in runc and the Linux kernel, an active worm campaign (Shai-Hulud) compromising NPM packages, and several high‑profile data breaches that demand immediate remediation. Sysdig published detections and guidance while urging organizations to patch affected systems, remove compromised packages, rotate credentials, and hunt for related activity #ShaiHulud #runc

Traditional point-in-time penetration testing fails to keep pace with today’s cloud-native, continuously changing environments, leaving blind spots as assets move and new code is deployed. Continuous Penetration Testing (CPT) pairs automation with human expertise to deliver ongoing validation, shorter remediation cycles, and measurable ROI, turning security from a yearly audit into a continuous feedback loop. #ContinuousPenetrationTesting #SprocketSecurity
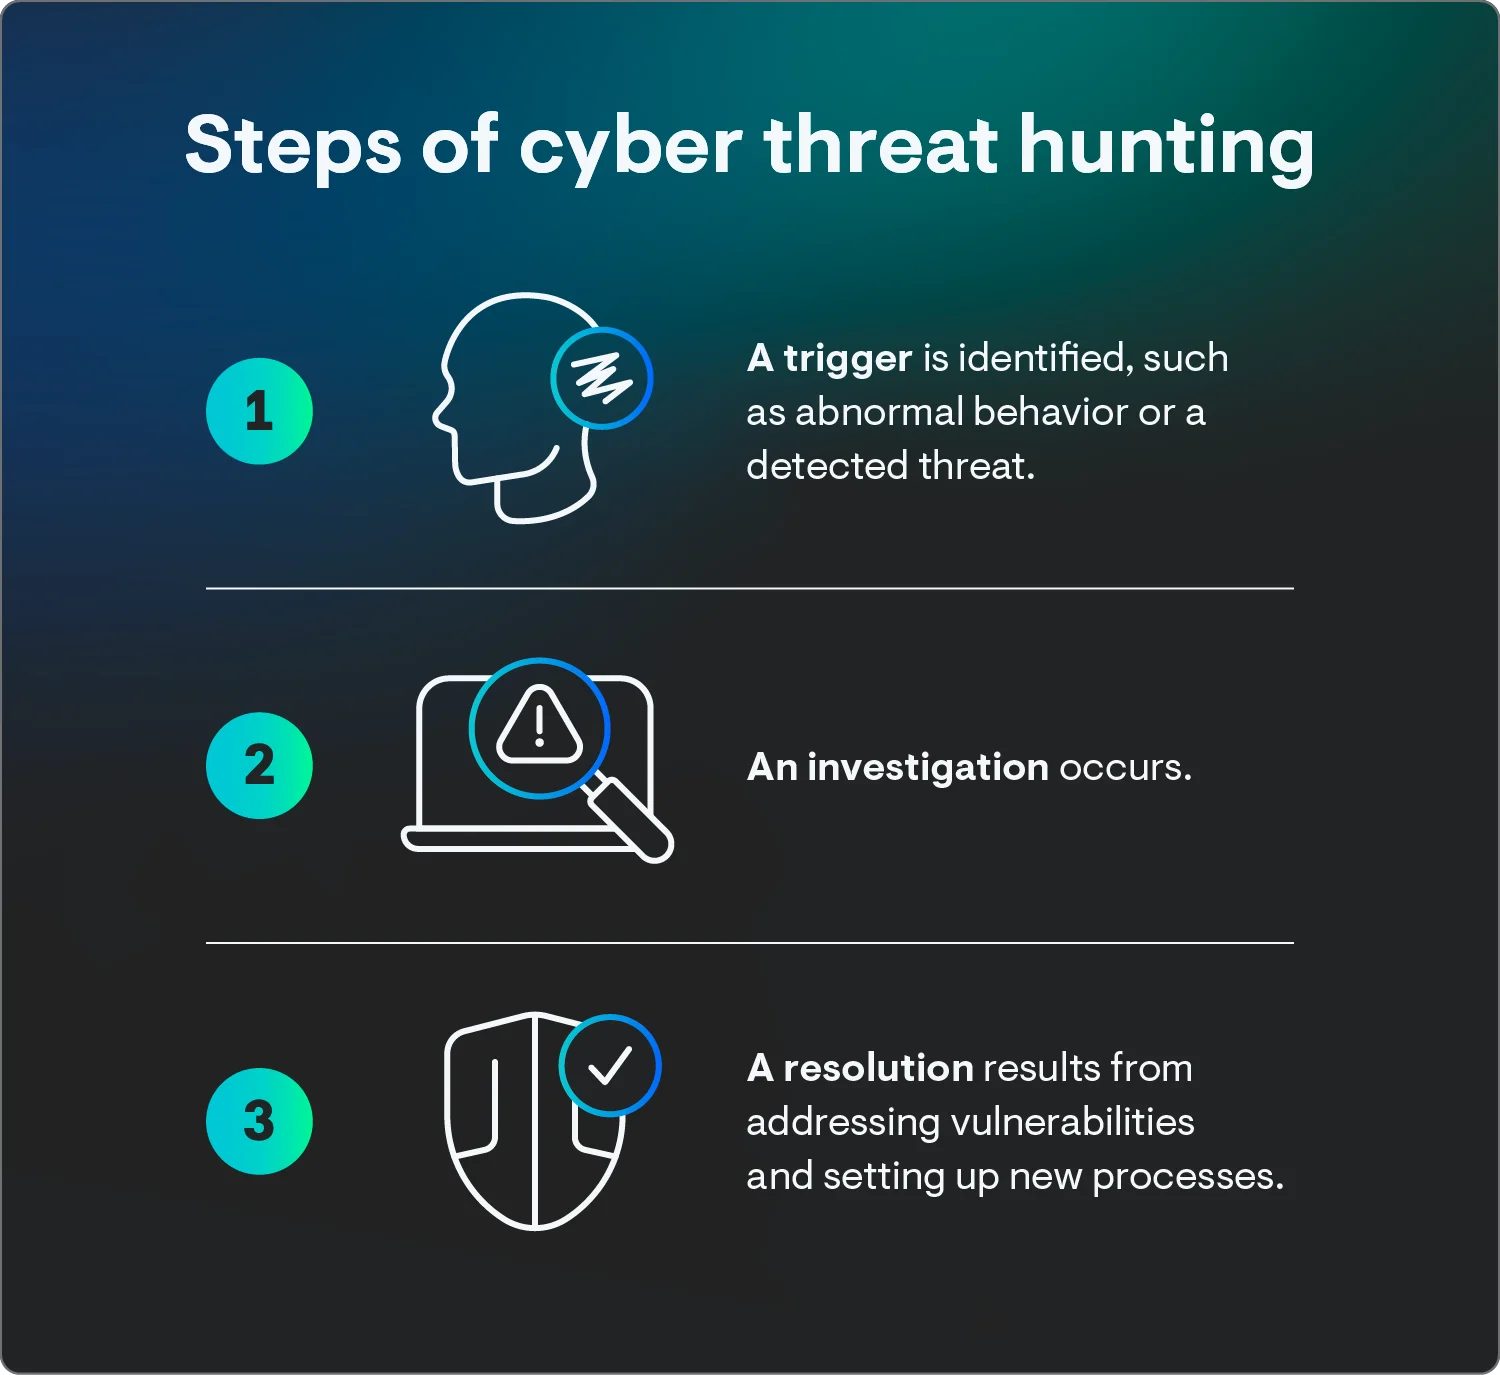
Threat hunting is a proactive, human-driven process that searches networks and endpoints to identify hidden or emerging threats missed by automated defenses. Combining intelligence, data analysis, and skilled hunters—supported by tools like Huntress Managed SIEM—enables organizations to detect and contain threats earlier and convert successful hunts into automated detections. #Huntress #HuntressManagedSIEM
The 2025 Cyber Threat Intelligence Report provides a detailed analysis of global malicious infrastructure, highlighting increased use of Sliver and Brute Ratel frameworks and ongoing dominance of Cobalt Strike. It also covers significant trends in information stealers and ransomware ecosystems, emphasizing evolving adversary tactics and geographic hosting distributions. #CobaltStrike #Sliver #BruteRatel #LummaStealer #RedlineStealer #FogRansomware
The requested annual cybersecurity report on supply chain threats was not accessible due to a GitHub HTTP 404 error. This error indicates the file or resource could not be found at the specified URL. #GitHub #HTTP404
The 2025 AI Risk & Readiness report reveals that organizations are rapidly adopting AI but struggling to keep governance and security measures in pace, exposing major vulnerabilities such as AI-powered data leaks and Shadow AI. The report emphasizes urgent actions on AI risk monitoring, compliance with emerging regulations like the EU AI Act, and embedding Trust, Risk, and Security Management (AI TRiSM) to build scalable AI security. #AIpoweredDataLeaks #ShadowAI #AIgovernance #BigID
This report analyzes the evolving cybersecurity threat landscape facing the travel and tour operations industry from 2023 to 2025, highlighting major attacks such as DDoS disruptions, cloud storage breaches, phishing campaigns, and supply chain exploits. It also outlines Cyberint’s solutions and recommendations for enhancing defenses through continuous threat intelligence and attack surface monitoring. #Rhysida #FancyBear #LockBit #ALPHV #ScatteredSpider #Cyberint
The 2025 Global OT & IoT Threat Landscape Report reveals a sharp rise in industrial cyber risks driven by AI-enhanced cybercrime and targeted attacks on critical infrastructure worldwide. It highlights persistent vulnerabilities in IT-OT convergence, the emergence of AI-powered malware, and sustained threat actor activities including state-sponsored APT operations. #LockBitNG #APT41 #RansomHub #IndustrialCybercrime
The 2025 holiday season shows a sharp rise in malicious, holiday-themed and e-commerce spoof domains, massive volumes of stealer-log credentials, and active exploitation of critical vulnerabilities across Magento, Oracle EBS, and WooCommerce. Organizations face industrialized, automated attacker services—AI-driven brute force, instant phishing hosting, and marketplace commoditization—that enable large-scale credential abuse and payment skimming. #Magento #WooCommerce