Varonis Threat Labs uncovered RovoBlast, a one-click vulnerability in Atlassian’s Rovo AI assistant that let attacker-controlled instructions be injected into live AI sessions through a crafted link. The flaw could expose data from Jira, Confluence, Bitbucket, Slack, Microsoft 365, Google Workspace, and other connected systems before Atlassian fixed it. #RovoBlast #Atlassian…
Category: Cyber Security News

Research presented by PortSwigger’s Gareth Heyes shows that HTML and CSS inside email can break out of the message boundary and manipulate trusted webmail interfaces across Outlook, Gmail, Fastmail, Proton Mail, Yahoo Mail, and AOL Mail. The proof-of-concept chains can capture passwords, leak tokens, hijack UI actions, and even steer AI…

Two independent findings showed that Atlassian’s Rovo assistant could be manipulated to collect Jira or Confluence data a signed-in user can access and send it to an attacker-controlled server. Varonis’ one-click link flaw, named RovoBlast, was fixed server-side on July 8, 2026, while PromptArmor’s content-borne injection path remained unconfirmed as of…
A New Mexico judge ordered Meta to pay $567 million and change how minors use Facebook and Instagram after finding the platforms contributed to youth mental health harms and sexual exploitation. The ruling creates a fund for treatment and prevention, adds nighttime and usage limits for youth, and requires clearer child-safety…
The Senate confirmed Adam Cassady as the next U.S. ambassador for cyber and digital policy in a 51-47 vote, making him only the second person to hold the post. His role will be shaped by a State Department reorganization that split the Bureau of Cyberspace and Digital Policy and raised questions…
The National Rural Water Association and DEF CON Franklin have launched the Water Watch Center to bring threat intelligence and cybersecurity support to underfunded U.S. water and wastewater systems. The program targets smaller utilities and comes amid a growing wave of attacks linked to Iranian hackers, with partner firms including Rapid7,…
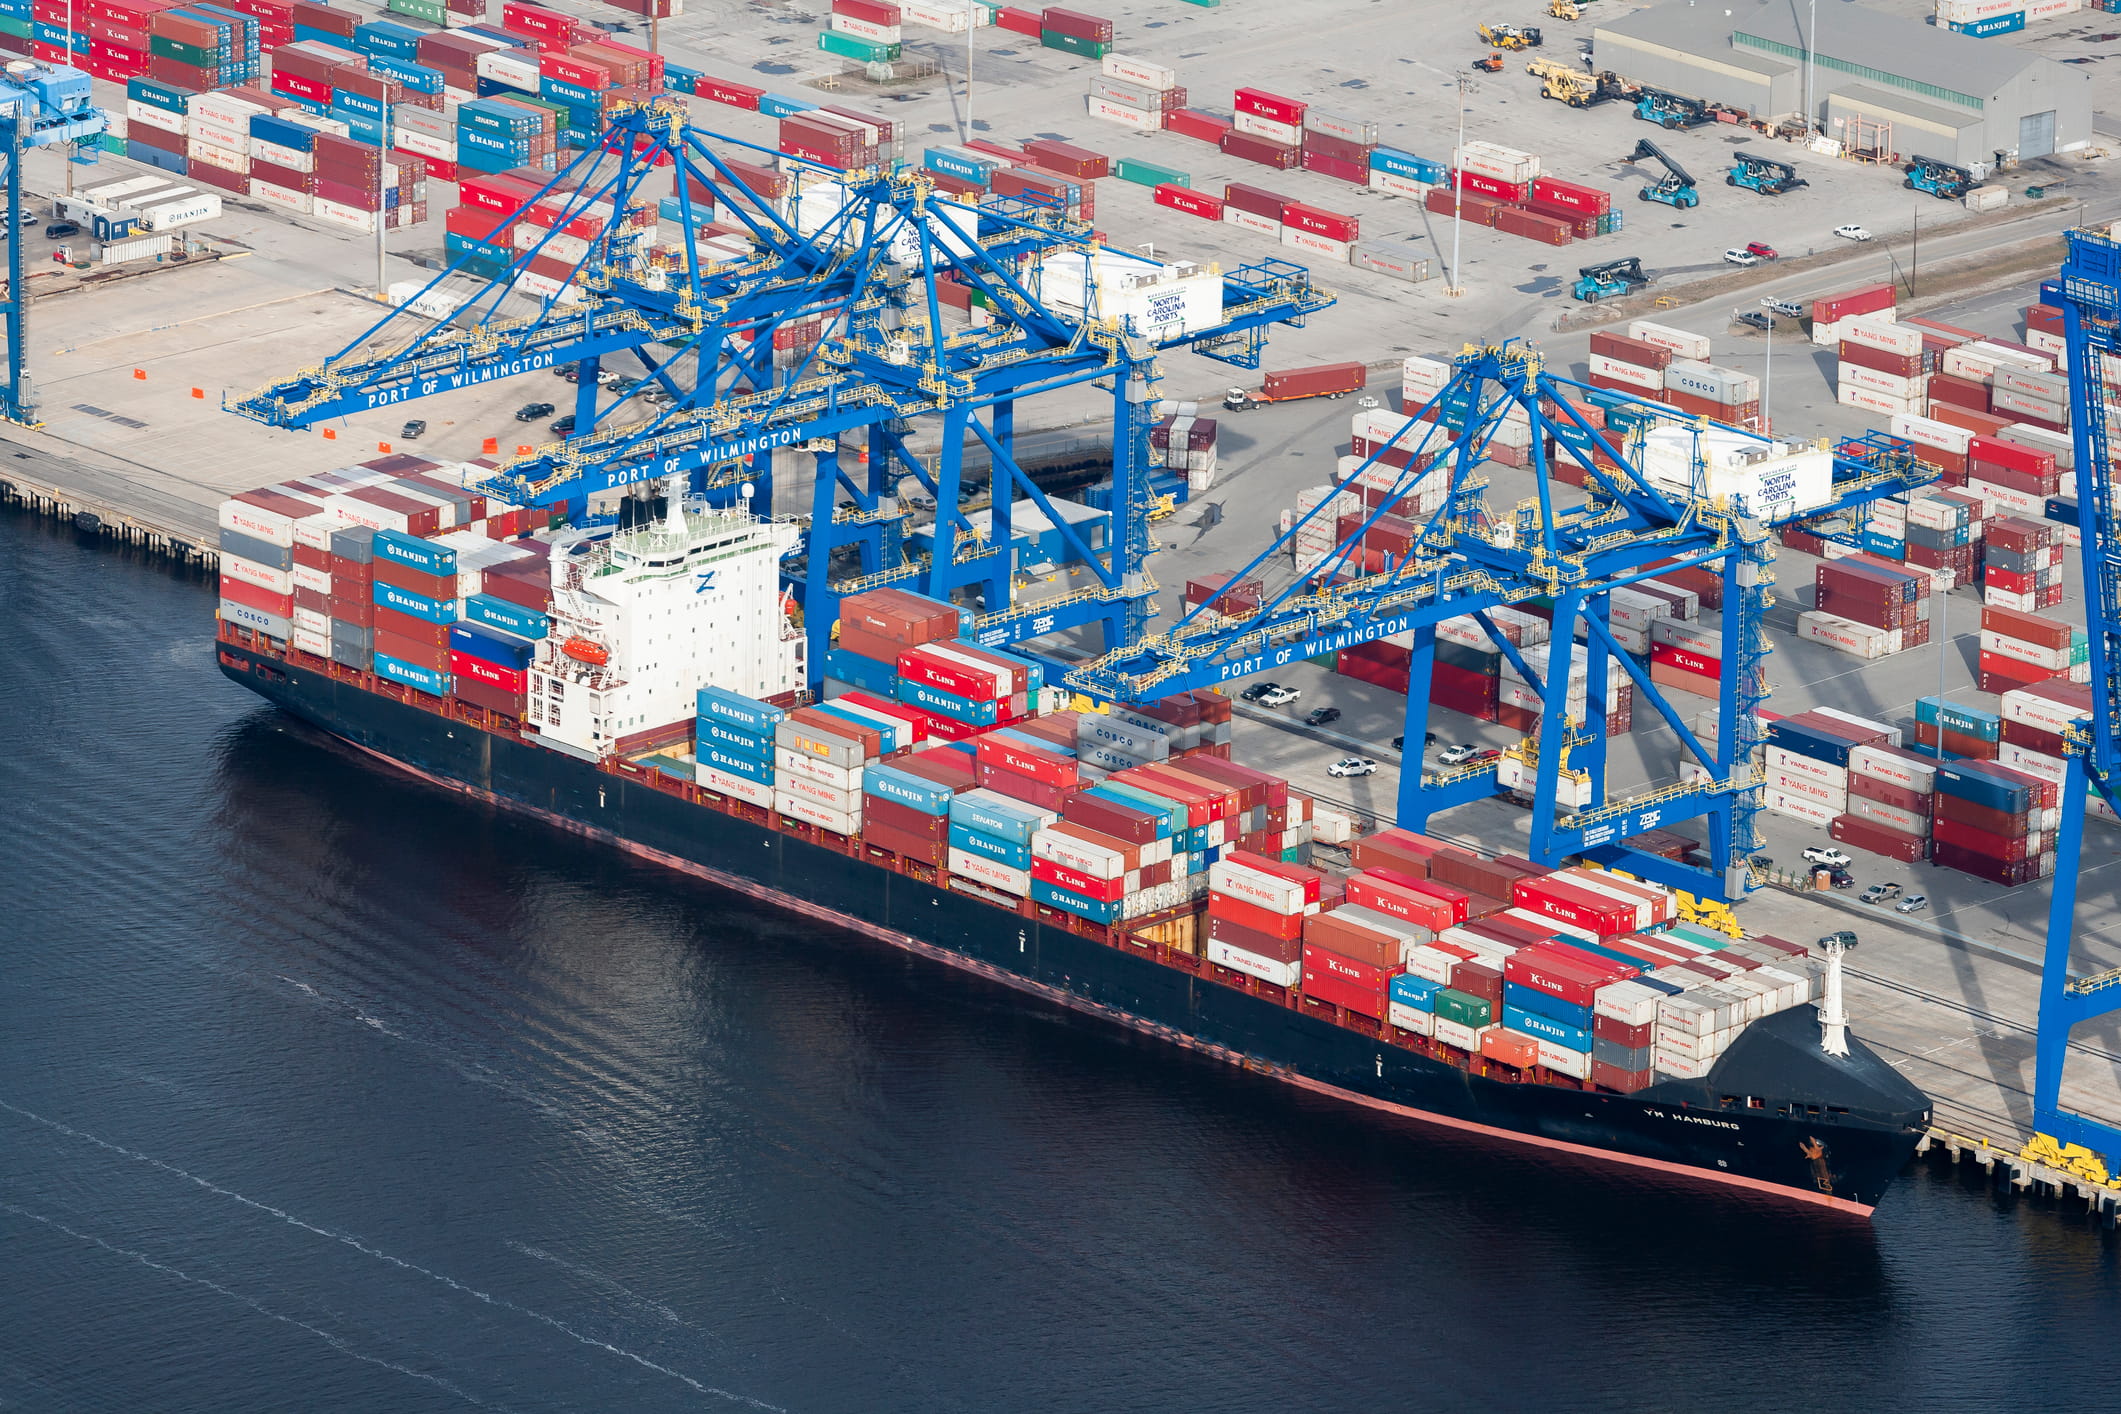
The U.S. Coast Guard is monitoring the fallout from a cyberattack that disrupted gate operations at North Carolina’s Port of Wilmington, Port of Morehead City, and Charlotte Inland Port. The North Carolina State Ports Authority activated its cybersecurity contingency plan, shifted to manual processing, and continues investigating the incident with state and federal partners. #USCoastGuard #NorthCarolinaStatePortsAuthority #PortofWilmington #PortofMoreheadCity #CharlotteInlandPort
Unlimited Technology Systems disclosed that a breach of its commercial data center exposed personal and health-related information belonging to 3,803,750 people. The company said unauthorized access occurred for five days in October 2025, and it has not identified the attackers or any public ransomware group claiming the incident. #UnlimitedTechnologySystems
A critical unauthenticated SQL injection flaw in Metabase was actively exploited as a zero-day, giving attackers administrator access to customer instances and enabling data theft from both Metabase Cloud and self-hosted deployments. Framework, Tally, and LexisNexis all reported impacts tied to the incident, with stolen data including customer contact details, login information, and in some cases password hashes. #Metabase #Framework #Tally #LexisNexis

UNC6671 is carrying out vishing-led extortion campaigns against financial services, private equity, and professional services by impersonating IT help desk staff and stealing credentials through fake login portals. The group uses captured sessions to access Microsoft 365 and Okta, exfiltrate cloud data, and operate under multiple extortion brands including Redact, Pink,…

ClickFix-style lures are being used to deliver a Go-based macOS stealer that can harvest browser passwords, Apple iCloud Keychain data, cached credentials, and cryptocurrency holdings. The campaign also uses Aeza Group infrastructure and joins a broader wave of ClickFix attacks tied to MacSync, Atomic Stealer, Lumma Stealer, and Remus. #ClickFix #AezaGroup…

A cluster of nearly 800 malicious npm packages is being used to deliver cross-platform malware that targets Windows, macOS, and Linux through a downloader called WEL1DROPPER and a staged payload delivery process. The campaign, tracked as Flooding Dropper and possibly linked to the earlier Moika operation, also overlaps with other npm…
New research from 1Password found that ChatGPT 5.5 and Claude Opus 4.8 often fail to fully patch high-impact vulnerabilities and can introduce new bugs instead. The findings suggest AI-assisted patching still needs human review, even as models like GPT 5.5, GPT-5.6-Sol, and Anthropic’s Mythos are promoted for stronger security capabilities. #ChatGPT #ClaudeOpus #1Password #Veracode #ProjectGlasswing #Daybreak
Levi Strauss & Co. said attackers used social engineering to access three employees’ company-issued computers and exfiltrate certain corporate information. The company says its rapid response contained the incident, no consumer data was impacted, and some reports have linked the activity to UNC6671. #LeviStrauss #UNC6671

Open source is entering a new phase where enterprises will rely only on projects that can prove they are reachable, maintained, and accountable, while everything else remains open source but outside regulated use. The article argues for a practical “proof of life” model, potential stewardship and retirement paths for projects, and…