
WordPress has patched CVE-2026-64638, a pre-authentication reflected XSS flaw in the login screen that affects every version of the CMS and can be chained into PHP code execution under the right conditions. Researchers at pwn.ai demonstrated the attack chain XSS2Shell, but WordPress says real-world escalation still depends on administrator interaction and…
Category: Cyber Security News

SecurityWeek’s weekly roundup covers major cybersecurity developments, including OpenAI’s disruption of a Cambodia-based scam network, Amgen’s cloud data theft incident, and Apple’s move to limit AI-generated bug bounty noise. It also highlights supply chain compromises, router backdoors, phishing and vishing attacks, and policy efforts targeting Chinese data center components. #OpenAI #Amgen…

Daily Recap, AI-powered browsers and assistants are facing abuse through zero-click techniques and prompt exposure, with researchers highlighting risks for tools like Claude and ChatGPT Atlas. Security teams also tracked passkey-protected account hijacking, active exploitation of flaws in Langflow, N-central, and Apache Tomcat, and supply-chain/persistence threats including Zbtlink router backdoors and ClickFix macOS malware lures.
#Claude #ChatGPTAtlas #Passkey #Cisco #SDWAN #IOSXE #FMC #Paperclip #CISA #Langflow #Ncentral #ApacheTomcat #TeamCity #Bixby #Samsung #Zbtlink #khunt #Oracle #COLDCARD #ClickFix #Snowflake #ConnorMoucka #RansomCartel #SaltTyphoon #Poipet #ChatGPT #EdnaConway #TomCotton #BlackHatUSA2026
A cyberattack disrupted IT systems at the North Carolina Ports Authority, slowing operations at the Port of Wilmington, Port of Morehead City, and Charlotte Inland Port. The authority activated its contingency plan and is restoring services, but delays are still expected as no threat actor has been identified. #PortofWilmington #PortofMoreheadCity #CharlotteInlandPort #NorthCarolinaPortsAuthority
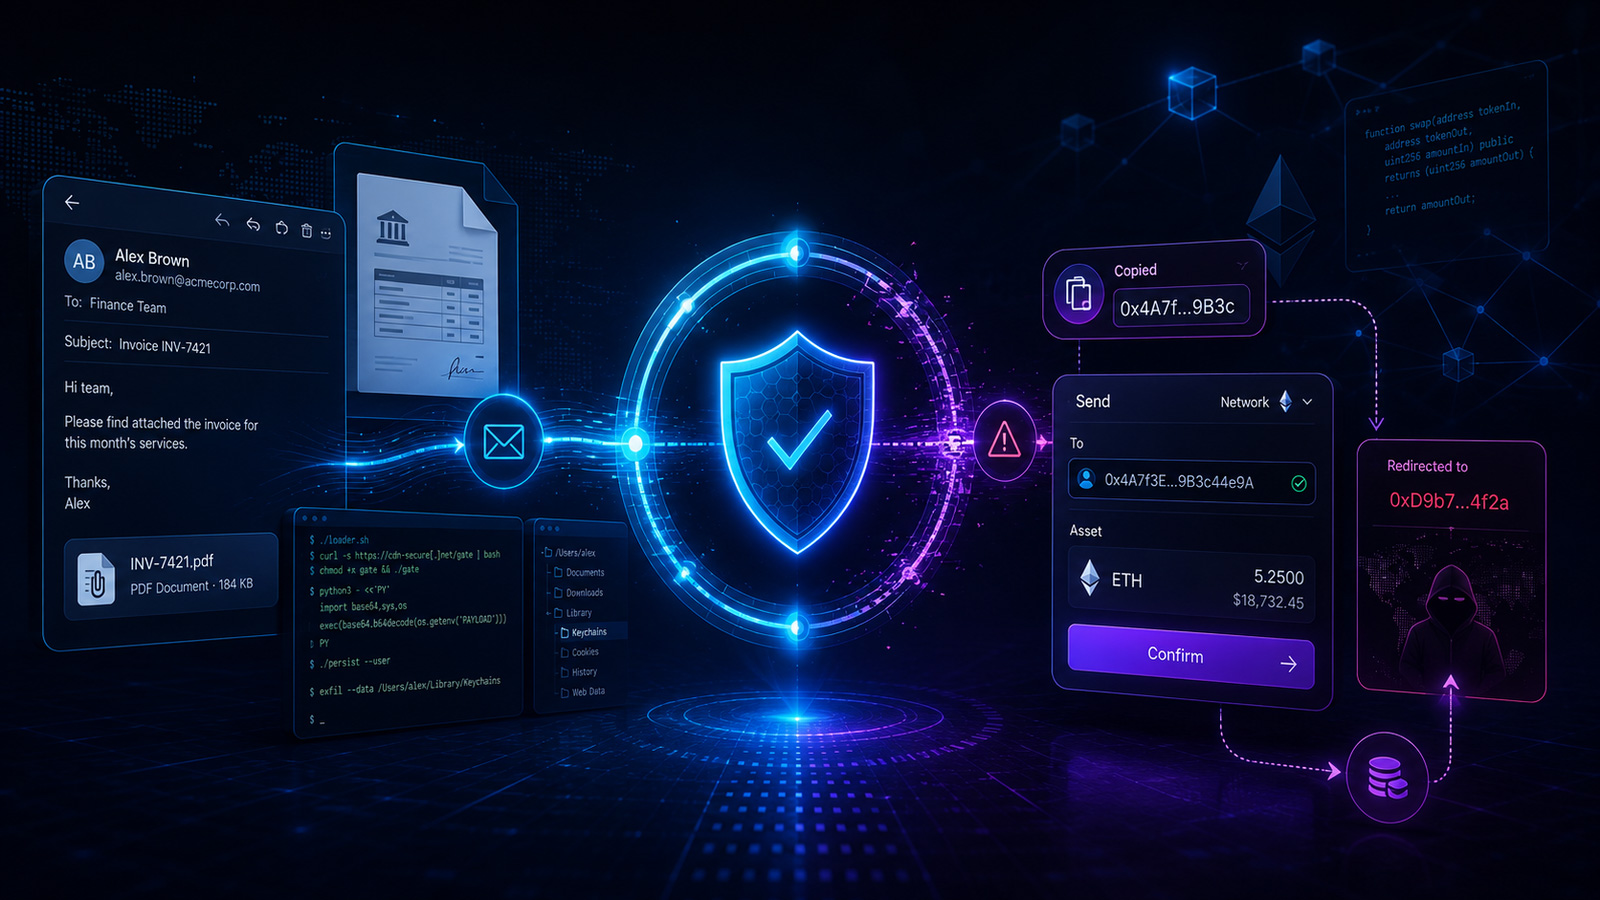
Gen Threat Labs examined two H1 2026 campaigns that abused trusted systems, including compromised mailboxes, browser and proxy manipulation, clipboard hijacking, and blockchain-based C2 resolution. The report highlights how these attacks bypassed normal trust signals while targeting banking sessions in Europe and cryptocurrency payments through a Rust-based clipper and Binance Smart Chain pointers. #GepyS #XWorm #RemcosRAT #BinanceSmartChain
NMFTA revealed that a 2024 safety recall for Bendix’s EC80 heavy-truck brake controller also fixed serious security flaws, including a wirelessly reachable remote code execution vulnerability. The research showed that exploiting the flaws could crash the ECU, disable key vehicle functions, and require a battery disconnect to recover, while the findings…
UNC6671 has rebranded its extortion operation multiple times while continuing tailored IT helpdesk vishing attacks against organizations using Microsoft 365 and Okta. Google Threat Intelligence Group says the group has shifted branding from BlackFile to Redact, Pink, Helix, and Falcon while collecting more than $10 million in ransom payments. #UNC6671 #BlackFile…

Security vendors at Black Hat USA 2026 announced new products, research, and services spanning AI security, endpoint protection, privileged access, and attack detection. Notable findings include 1Password’s research showing many AI-generated patches fail to fix vulnerabilities, while Zenity exposed a malicious skills campaign affecting AI agent ecosystems. #1Password #OffBy1Labs #Zenity #Vercel…
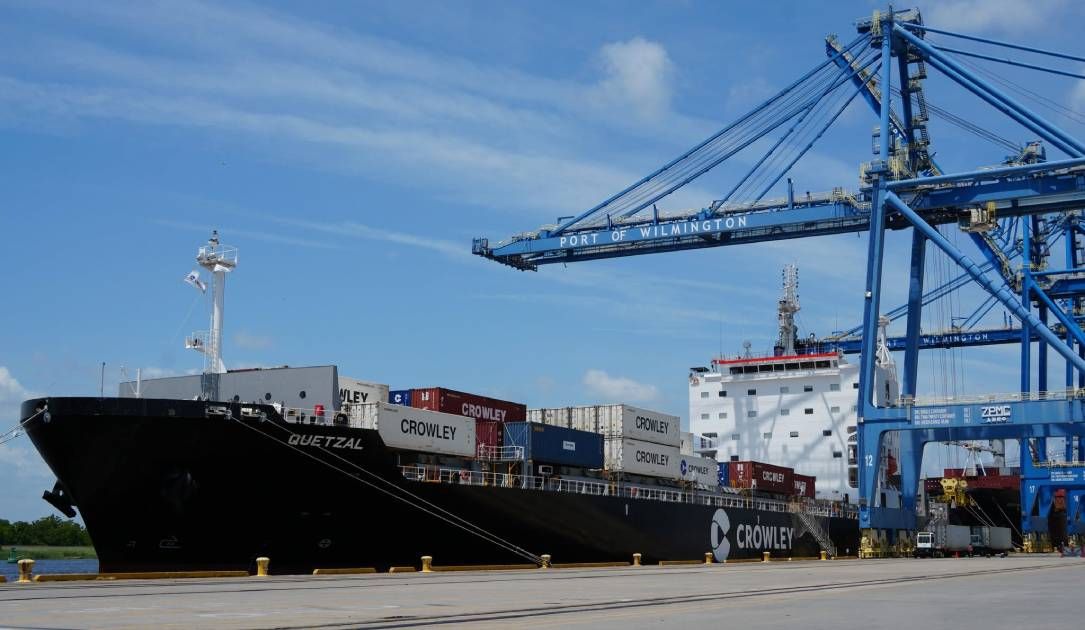
North Carolina Ports is recovering after a cyberattack forced Wilmington, Morehead City, and Charlotte to shift to manual operations while outside forensics teams work to restore affected systems. Officials said the breach has been contained, delays are expected, and no threat actor has claimed responsibility. #NorthCarolinaPorts #Wilmington #MoreheadCity #Charlotte…
Researchers discovered a way to bypass recent Spectre v2 mitigations on Intel and AMD processors by exploiting a Time-of-Neutralization to Time-of-Use window. Their attack can leak sensitive Linux kernel data, including hashed passwords from /etc/shadow, and was presented at Black Hat USA by MIT CSAIL researchers Daniël Trujillo and Mengjia Yan. #SpectreV2 #BranchTargetInjection #Linux #Intel #AMD #MITCSAIL #BlackHatUSA
A Go-based malware delivered through ClickFix attacks is targeting macOS users to steal cryptocurrency assets, browser-stored passwords, Apple Keychain data, and cached credentials. It can also intercept and redirect crypto transactions, while Huntress traced the operation to infrastructure linked with Aeza Group in AS 210644. #ClickFix #macOS #Huntress #AezaGroup #AppleKeychain #Bitcoin #Litecoin #Dogecoin #Monero #Ethereum #XRP
Maksim Silnikau was sentenced to 16 years in prison for creating and running Ransom Cartel, a ransomware operation that targeted at least 18 companies and tried to extort $5.2 million. His arrest in Poland and extradition to the United States ended the group’s activity after attacks on law firms, medical technology firms, schools, and multinational corporations. #RansomCartel #MaksimSilnikau #DirectConnection
A new Forescout scan found more than 4,000 Rockwell Automation and Allen-Bradley controllers exposed on the internet, with 22 still visible in cities affected by recent attacks on U.S. water systems. The research highlights ongoing risks from public-facing EtherNet/IP devices, stale remote-access services, and possible exposure to CVE-2017-16740 on some MicroLogix 1400 systems. #RockwellAutomation #AllenBradley #MicroLogix1400 #CVE-2017-16740
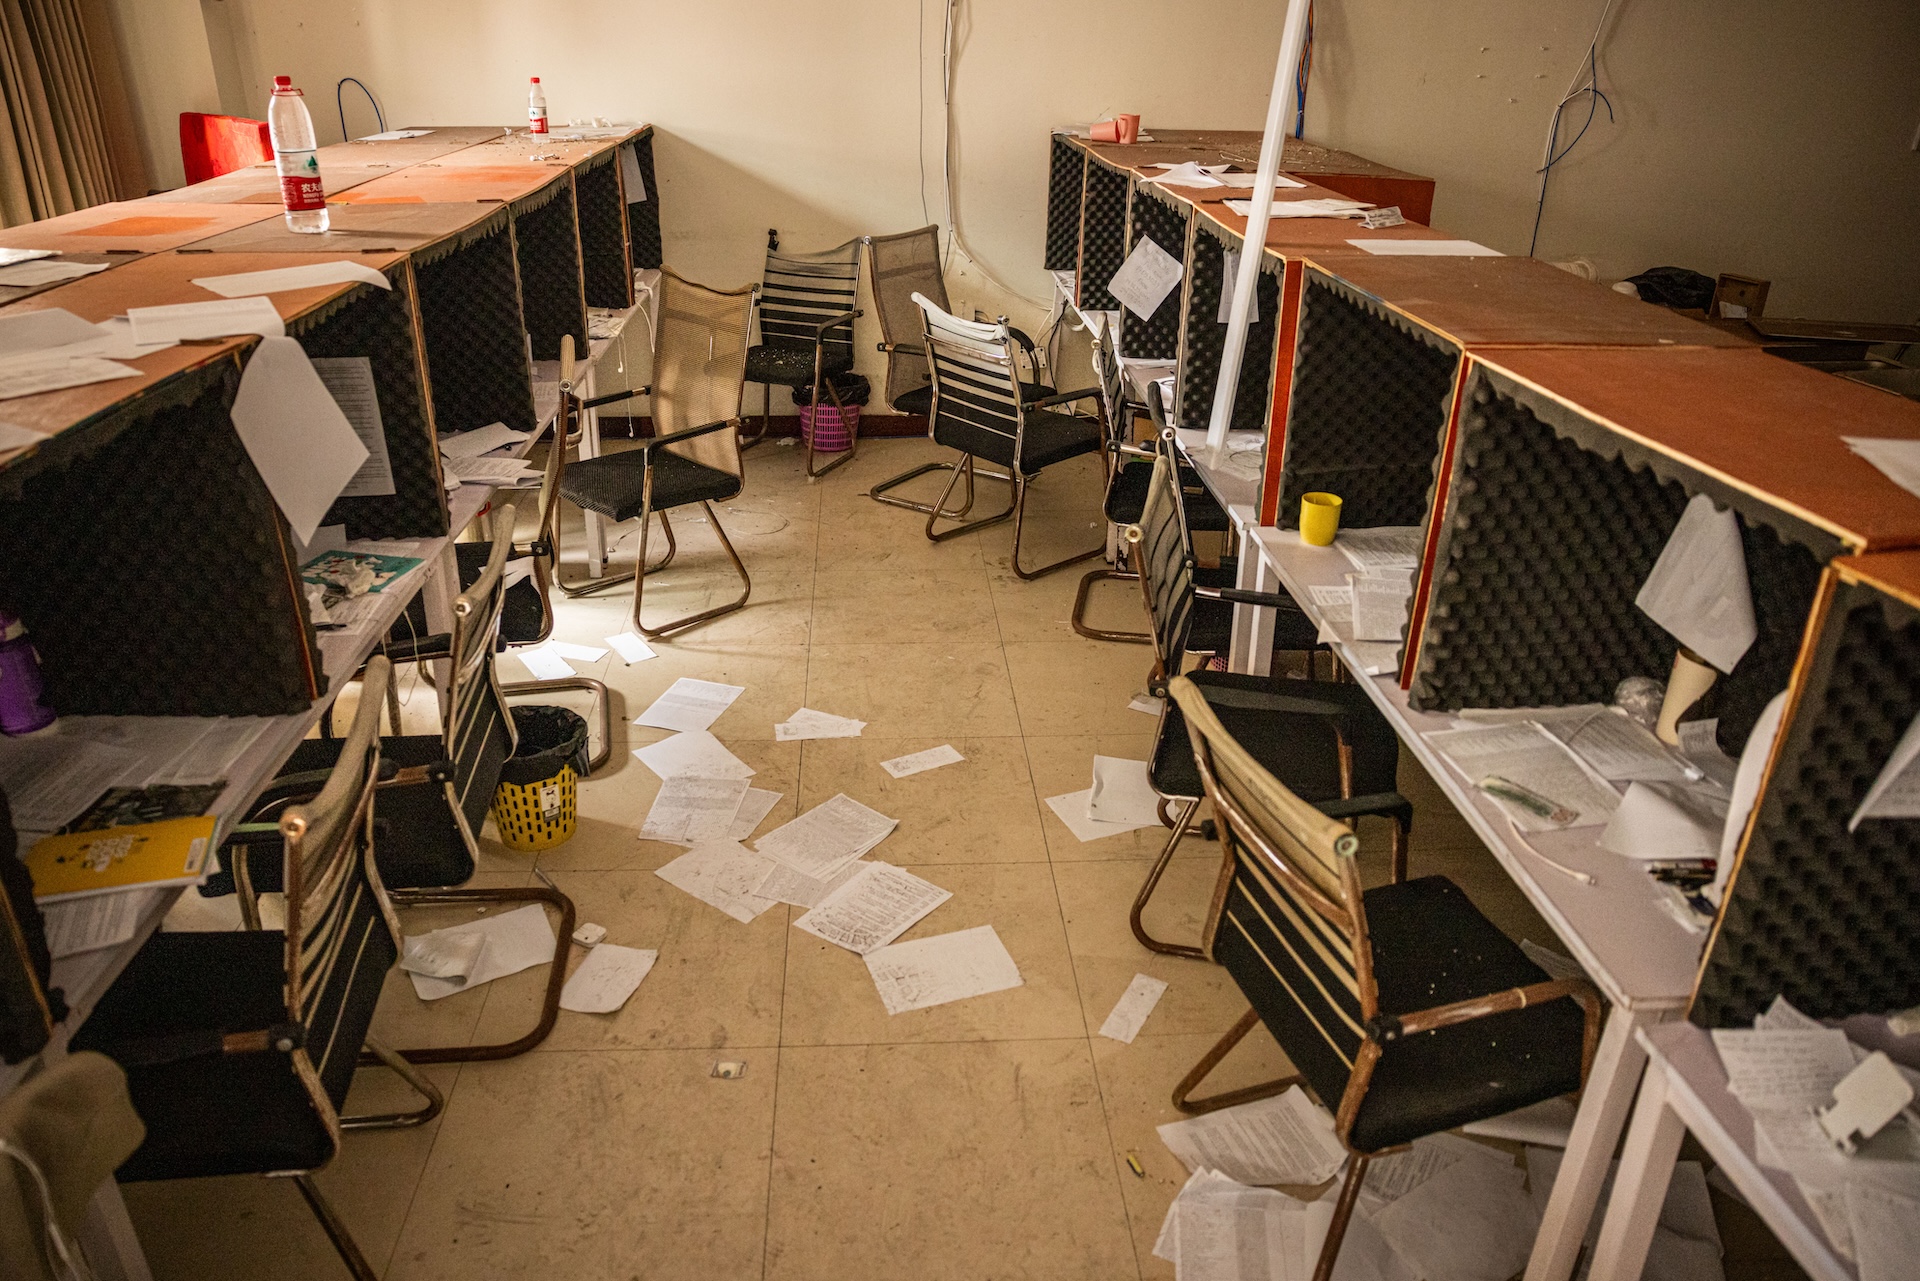
Senators from both parties pressed Trump administration officials on whether U.S. agencies and foreign partners are coordinated enough to combat transnational scam centers. Witnesses said the administration is moving toward a whole-of-government and international task force approach, with progress varying by country, especially in Cambodia, Burma, and Laos. #SCAMAct #Interpol #JointInteragencyTaskForceSouth #Cambodia #Burma #Laos
Switzerland’s federal IT office says attackers breached its Microsoft SharePoint servers by exploiting a vulnerability and compromised about 200 accounts. BIT responded by blocking external SharePoint access, patching the suspected flaws, resetting passwords, and investigating the incident with the Swiss Federal Office for Cyber Security and Microsoft. #SharePoint #BIT #Microsoft