Cisco warned that its Secure Endpoint Connector products on Windows, macOS, and Linux are affected by seven ClamAV vulnerabilities that can cause denial-of-service conditions, with public proof-of-concept code available for two of them. The flaws were fixed in ClamAV 1.5.4, and Cisco says no exploitation in the wild is known so…
Category: Cyber Security News

AI accelerators and neo-clouds are rapidly expanding, but their specialized hardware creates security blind spots that traditional cybersecurity tools cannot easily monitor. The article highlights how stealthy compromise of accelerator-based cloud infrastructure could enable supply chain attacks, model poisoning, and cross-tenant leakage, and how Stealthium aims to detect such threats through…
OpenAI has paused parts of Astra’s internal development after evaluations suggested the unreleased model may reach its “critical” cybersecurity risk threshold under the company’s Preparedness Framework. To reduce the danger of autonomous exploit building and end-to-end attack execution, OpenAI has added strict isolation, network limits, and monitoring controls. #OpenAI #Astra #PreparednessFramework…
LexisNexis took its Diligence, Metabase API, and Newsdesk services offline after detecting unusual activity on servers hosted by a third-party vendor. The company is investigating with a cybersecurity forensic firm and rebuilding affected systems in a new environment before restoring service. #LexisNexis #NexisDiligence #NexisMetabaseAPI #NexisNewsdesk
Justin Swaddle, a member of The Com, was sentenced to two years in prison for blackmail and sextortion targeting nearly 120 victims worldwide, including 117 girls aged 13 to 17. The case exposed links to The Com’s broader network of abuse, coercion, and child exploitation across platforms such as Snapchat, Telegram, and Discord. #TheCom #JustinSwaddle #WestYorkshirePolice #NationalCrimeAgency
AI is accelerating account takeover by making phishing, credential theft, MFA abuse, and session hijacking faster and more personalized, while stolen credentials and proxy-based logins are harder to detect. Device trust and Zero Trust controls are needed to ensure valid credentials alone are not enough without the right approved device context. #Specops #ActiveDirectory #Restreamio #IGN #Verizon
CISA warned that attackers are actively exploiting CVE-2026-8037, a critical command injection flaw in Progress Kemp LoadMaster that can let unauthenticated threat actors run arbitrary commands on exposed appliances. Progress has already released patches, and CISA is urging all defenders to prioritize remediation, especially for the widely deployed LoadMaster and MOVEit WAF products. #CVE-2026-8037 #ProgressKempLoadMaster #ProgressSoftware #CISA #MOVEitWAF
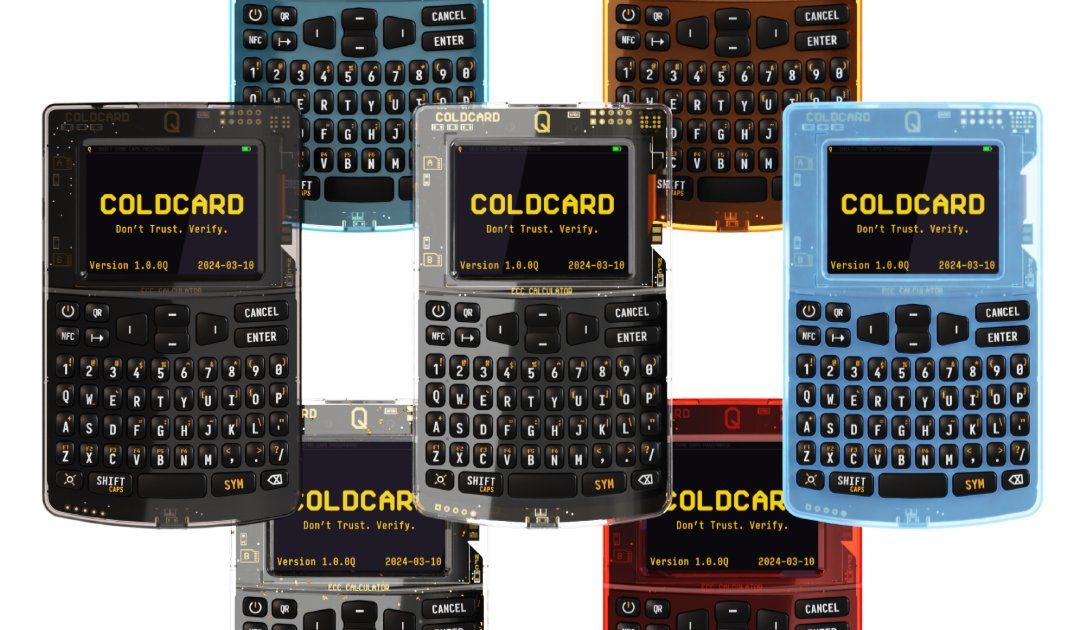
Coinkite destroyed its remaining Coldcard inventory after a firmware vulnerability was exploited to steal at least 1,367.05 BTC, worth about $88.6 million, from thousands of bitcoin wallets. The company released a patched firmware version and is working with affected customers and law enforcement to help recover funds and identify those responsible….
Traditional CASB and DLP controls can discover and govern AI tools, but they fall short because AI risk appears in prompts, responses, and agent actions rather than simple app or file access. Security teams need an interaction layer that inspects the semantics of conversations and authorizes what AI agents can retrieve,…
The FBI and EPA warned that cyberattacks against internet-facing PLCs have hit water and wastewater utilities in at least seven states, causing operational disruptions like pressure loss, flooding, and manual fallback. The attacks relied on exposed, outdated controllers and weak access controls, highlighting the need for utilities to remove PLCs from the public internet, strengthen passwords, and monitor OT environments continuously. #FBI #EPA #PLC #Aliquippa
Metabase has disclosed that a maximum-severity zero-day in its business intelligence and data visualization software was exploited in the wild, allowing unauthenticated attackers to inject SQL and gain administrator access. The issue affected Metabase Cloud and self-hosted versions, with Framework confirming customer data exposure, while Metabase urged immediate patching and log…

Cybersecurity Threat Research ‘Weekly’ Recap. The recap highlights supply-chain abuse in npm ecosystems (ChainDrop/Shai-Hulud, keyv/cacheable compromises, and additional npm worm activity), alongside rising AI token jacking that steals API keys and drains AI credits while attackers increasingly weaponize AI and coding agents for pre-prompt execution. It also covers phishing and vishing extortion efforts (UNC6671, ScreenConnect lures, ARERA and pagoPA scams, FakeCaptcha infrastructure, and developer lures), targeted intrusions and malware such as APT37/NarwhalRAT and BINDCLOAK, and cloud/container abuse including fileless in-memory cryptojacking (Fileless XMRig) and direct-to-IP C2 that evades DNS monitoring. #ChainDrop #ShaiHulud #keyv #cacheable #UNC6671 #ScreenConnect #ARERA #pagoPA #FakeCaptcha #Xeno #BHAlert #RovoBlast #RAT37 #NarwhalRAT #BINDCLOAK #QuasarRAT #UltraVNC #Xctdoor #CRAT #XMRig #Nextjs #Sliver #FilelessXMRig
A researcher disclosed serious flaws in the Connective digital identity browser extension used widely in Belgium, allowing websites to read eID and payment card data, steal eID PINs, and forge electronic signatures. The report also detailed a separate remote code execution issue, and Nitro has since fully remediated the vulnerabilities and…

Daily Recap, UNC6671’s vishing and hedge fund intrusion campaign has been tied to the BlackFile extortion crew, while North Carolina Ports reported a cyberattack that disrupted operations before investigators described it as contained. In other updates, a Swiss government SharePoint breach compromised 200 accounts, ClickFix is delivering a macOS infostealer for crypto theft, Cisco patched multiple SD-WAN and IOS XE flaws, and new CPU-side-channel research highlights Spectre v2 bypass paths via interrupt injection and TONTOU.
#UNC6671 #BlackFile #NorthCarolinaPorts #CoastGuard #SharePoint #SwissGovernment #Snowflake #RansomCartel #Zapscape #ZapscapeKVM #L1 #Cisco #SDWAN #IOSXE #SpectreV2 #Intel #AMD #ClickFix #TONTOU #InterruptInjection #LinuxPasswordHashes #RockwellControllers #Meta #AIModel #BlackHatUSA2026 #CapitolHill
Head Mare has been exploiting unpatched TrueConf server vulnerabilities to replace legitimate client installers with trojanized versions that deliver the PhantomCore and PhantomGraph backdoors. Kaspersky says the campaign targets Russian organizations and can impact users even through compromised third-party TrueConf servers, enabling credential theft, reconnaissance, and persistent remote access. #HeadMare #TrueConf #PhantomCore #PhantomGraph