Medusa ransomware-as-a-service is expanding quickly by paying access brokers and exploiting newly disclosed software flaws, including Fortra GoAnywhere and BeyondTrust vulnerabilities. The U.S. government says the group has surpassed 500 victims and has frequently targeted the Healthcare and Public Health sector, while also reusing legitimate tools to evade detection. #Medusa #FortraGoAnywhere #BeyondTrust #Storm-1175
Category: Cyber Security News

Attackers are actively scanning and exploiting critical flaws in MLflow and FUXA, with MLflow abuse targeting cloud metadata services to steal credentials and secrets. FUXA is also seeing malicious internet-wide scanning against a path traversal issue that could let an attacker overwrite files and potentially achieve remote code execution. #MLflow #FUXA…

Varonis Threat Labs disclosed CoSnitch, a set of three flaws in Microsoft Copilot Personal that could let a crafted link trigger silent prompt execution and exfiltrate data from connected apps in a victim’s authenticated session. The research also showed a separate memory-poisoning path through web summarization, and Microsoft shipped patches for…
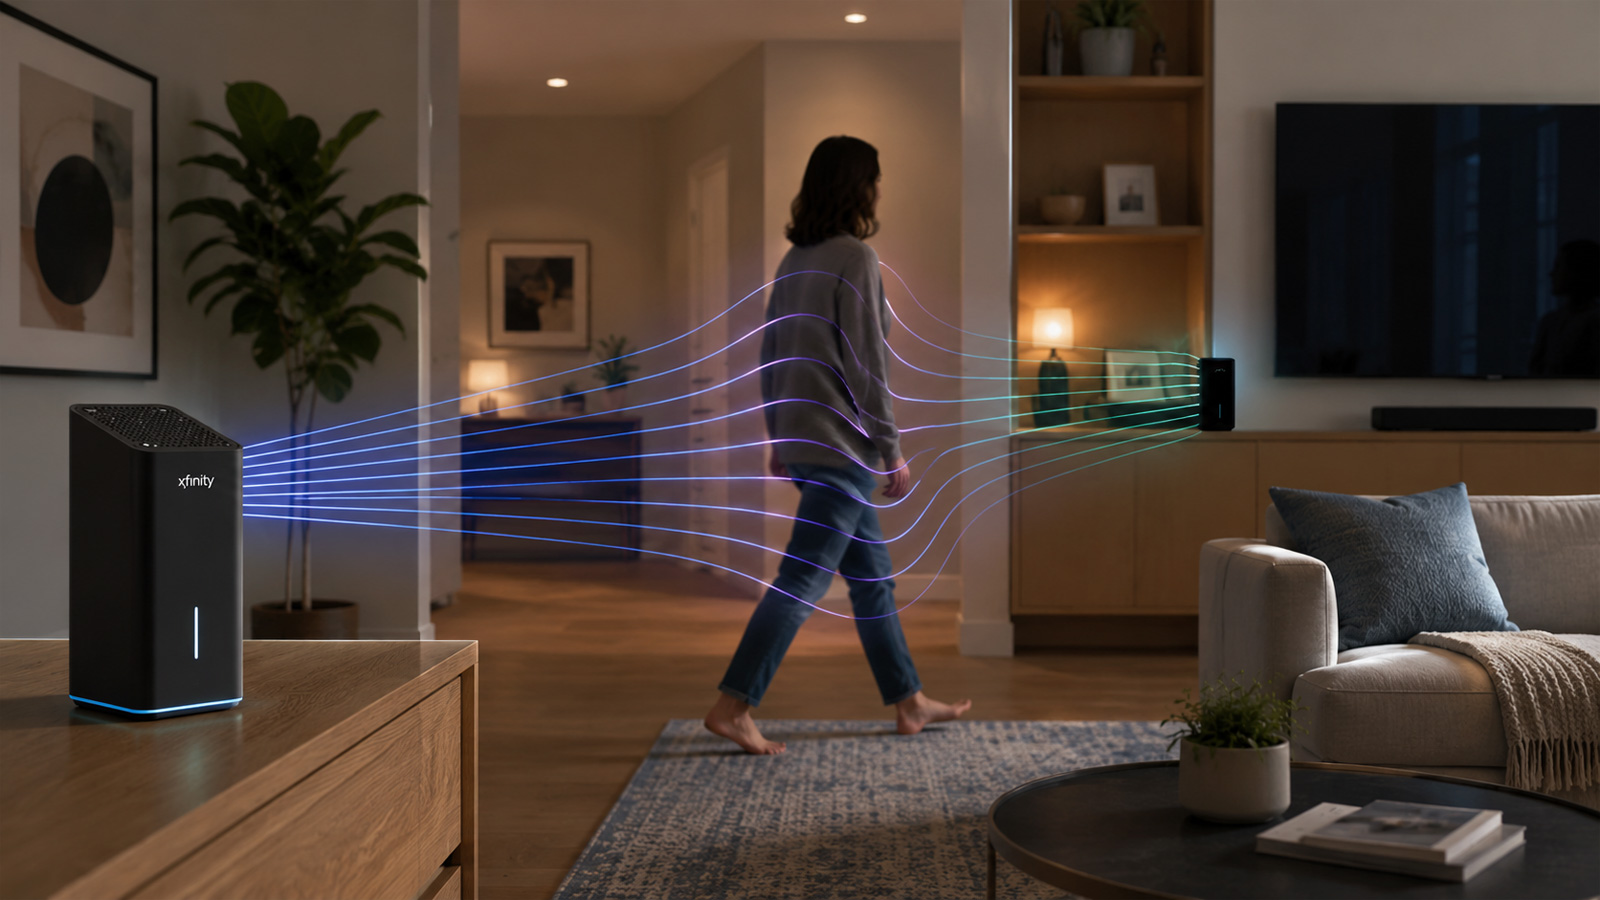
Comcast has expanded Xfinity Shield with WiFi Motion, a feature that uses WiFi signal changes to detect movement in a home without cameras or dedicated motion sensors. The company says the system is opt-in and does not identify people, but its documentation raises data-retention and law-enforcement disclosure questions. #Comcast #XfinityShield #WiFiMotion #XfinityApp
Federal authorities unsealed an indictment against 17 Iranians affiliated with the Mabna Institute, accusing them of a large-scale, state-sponsored cybertheft campaign targeting universities, governments, and companies. The case alleges the theft of academic and research data from thousands of accounts worldwide, with a Rewards for Justice offer of up to $10 million for information on four of the defendants. #MabnaInstitute #RewardsforJustice #HBO

Daily Recap, GitHub experienced a worldwide outage, while large-scale DDoS attacks disrupted Threema’s secure messaging service. In other security developments, Philips and GE are investigating Clop ransomware data-theft claims, SafePal confirmed a breach impacting 39,798 customers, and Microsoft is working on a Defender patch for the ShieldBreak zero-day while new AmnesiaStealer macOS malware targets browser sessions.
#GitHub #Threema #DDoS #Clop #Philips #GE #SafePal #ShieldBreak #Microsoft Defender #AmnesiaStealer #macOS
ReliaQuest uncovered a custom JSP web shell likely tied to Clop that was built specifically for PTC Windchill and FlexPLM, with functions to decrypt credentials, enumerate vaults, and steal files. The activity appears linked to CVE-2026-12569 exploitation and Clop’s broader data theft campaign against enterprise platforms. #Clop #PTCWindchill #FlexPLM #CVE2026-12569
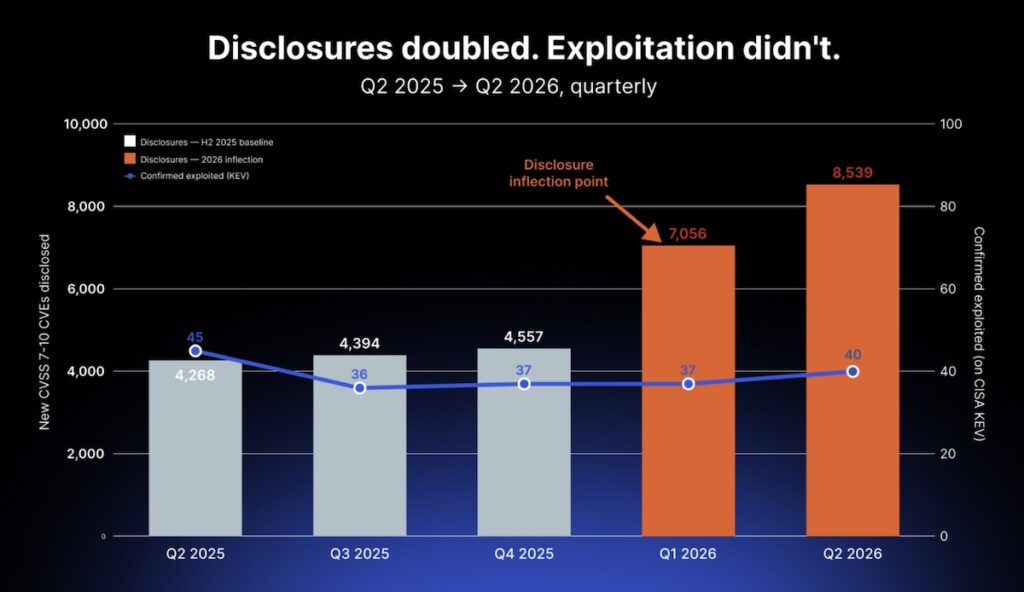
Rapid7 says AI is compressing the time between vulnerability disclosure and exploitation, making traditional patch cycles too slow to keep up. The report highlights rising “Holy Grail” vulnerabilities, active CRINK nation-state operations, and ransomware groups like Qilin, The Gentlemen, DragonForce, Akira, and LockBit, while urging defenders to focus on exposure rather…
Nico Waisman’s career evolved from self-taught hacking in Argentina to leadership roles in offensive security, open source protection, defensive security, and AI-driven security at XBOW. He sees cybersecurity as a path shaped by curiosity, mentorship, and adaptation, while warning that AI could soon enable autonomous malware attacks at massive scale. #NicoWaisman…
Artificial intelligence is accelerating exploitation and compressing the time between patch release and active attack, putting traditional cybersecurity defenses under pressure. This discussion explores whether detection-first security operations can keep up, or if prevention must become the default approach as attackers move at machine speed. #Automox #SilveradoPolicyAccelerator #VectraAI…
The Blue Report 2026 from Picus Labs shows enterprise prevention recovered to 69%, but the gains hide serious weaknesses in behavioral defenses, especially once attackers are inside the network. Testing across Mimikatz and other post-compromise techniques shows that signature-based controls often miss quieter variants, with credential dumping and registry-based attacks slipping through far more easily than classic LSASS memory access. #PicusLabs #BlueReport2026 #Mimikatz #LSASS #ProcDump #comsvcsdll #SharpHound #T1003
Microsoft has removed the legacy Windows Management Instrumentation Command-line (WMIC) tool from Windows 11 24H2, 25H2, and new beta builds as part of its broader deprecation plan. The change is meant to improve security by eliminating a tool that threat actors and malware have long abused for actions like deleting Shadow Volume Copies, checking security software, and adding Microsoft Defender exclusions. #Microsoft #WMIC #Windows11
Microsoft says some users are experiencing search issues in Microsoft 365 apps, including Outlook on the web, Outlook desktop, SharePoint Online, and OneDrive, due to a recent deployment that caused resource utilization problems. The company says it has deployed a fix to reduce resource pressure and restore service for affected users. #Microsoft365 #Outlook #SharePointOnline #OneDrive
CISA confirmed that ransomware gangs are exploiting CVE-2025-60710, a high-severity Windows Task Host privilege escalation flaw affecting Windows 11 and Windows Server 2025. The agency added the vulnerability to its KEV catalog and urged federal agencies to patch it, while Microsoft has not yet publicly confirmed in-the-wild exploitation. #CVE-2025-60710 #CISA #WindowsTaskHost #Windows11 #WindowsServer2025
Microsoft is testing a faster File Explorer and a redesigned, more customizable context menu in Windows 11 preview builds to improve speed, reduce clutter, and address user feedback. The company is also removing the WMIC tool from newer Windows 11 releases, a LOLBIN that has been abused by cybercriminals. #Microsoft #Windows11 #FileExplorer #WMIC