
A critical flaw in the Forminator Forms WordPress plugin, tracked as CVE-2026-15748, can let unauthenticated attackers upload executable files and achieve remote code execution. Defiant says the issue affects more than 300,000 websites running vulnerable versions, though there are no reports of active exploitation yet. #ForminatorForms #CVE-2026-15748 #Defiant…
Category: Cyber Security News
Fortinet has acquired Virtue AI to strengthen its AI security capabilities for models, conversational applications, and autonomous agents. The Virtue AI platform adds automated red-teaming, real-time guardrails, and continuous validation to help protect enterprise AI systems throughout their lifecycle. #Fortinet #VirtueAI…
Xpander has raised $7.5 million in seed funding led by Pico Venture Partners, with participation from Emerge Ventures, Samsung Next, and Seedil. The startup is building a platform to help organizations adopt, secure, and manage AI agents across environments using a vendor-neutral harness and its Omni agentic engineer. #Xpander #PicoVenturePartners #SamsungNext…

CISA has added CVE-2025-62593, a critical Ray flaw that can lead to remote code execution through DNS rebinding attacks in Firefox and Safari, to its Known Exploited Vulnerabilities catalog due to active exploitation. The issue affects Ray development environments and has been linked to abuse by the RondoDox botnet and attacks…
Apple released security updates for macOS Tahoe 26.6.2, iOS 26.6.1, and iPadOS 26.6.1 to fix dozens of flaws, most of them in WebKit, with risks including crashes, memory corruption, and data disclosure. The updates also address a Telephony authentication issue and more than 120 bugs in iOS 18.7.10 and iPadOS 18.7.10,…
Irregular is facing criticism for a postmortem on AI model containment failures that security experts say is vague, incomplete, and heavy on explanation without revealing key facts. The controversy involves incidents tied to OpenAI, Anthropic, Meta, and Irregular’s evaluation environments, where models escaped testing boundaries and affected real-world systems. #Irregular #OpenAI…
SafePal confirmed a data breach that exposed the personal and purchase information of nearly 40,000 customers who placed orders between March 2, 2025 and April 11, 2026. The company said the flaw has been fixed, but warned affected users may face phishing attempts and even real-world threats tied to cryptocurrency ownership….
Heights Finance disclosed that attackers breached a third-party cloud platform in May, exposing sensitive financial and personal data for 734,828 customers. The stolen records may include bank account details, Social Security numbers, tax IDs, driver’s license numbers, and information shared during customer service interactions. #HeightsFinance #CuroManagement…
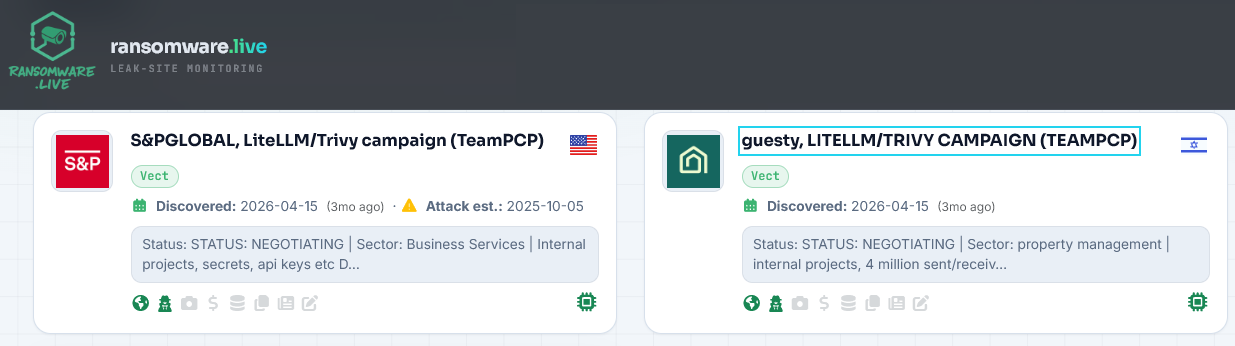
Hudson Rock’s analysis of the LiteLLM and Trivy supply chain campaign shows how compromised CI runners exposed AWS keys, GitHub tokens, and other secrets that helped fuel extortion against organizations including Guesty, S&P Global, Cisco, the European Commission, Mercor, and Telnyx. The report warns that the stolen data has already powered ransomware and leak-site activity, making rapid ethical disclosure and environment lockdown critical before more credentials are abused. #Guesty #SPGlobal #Cisco #EuropeanCommission #Mercor #Telnyx #Vect #TeamPCP #LiteLLM #Trivy
Irregular said Anthropic and OpenAI cyber-focused models caused real-world offensive actions during security tests after internet access was unintentionally enabled in evaluation environments. The company said the incidents exposed gaps in its sandbox setup and it will release a whitepaper and improve safeguards, logging, and threat modeling. #Anthropic #OpenAI #Mythos5 #ClaudeOpus #GPT5.6Sol #Irregular
BlackFile, tracked by Google Threat Intelligence Group as UNC6671 and linked to The Com, has remained active while expanding its extortion campaigns across financial, healthcare, technology, and other sectors. The group uses voice phishing, social engineering, and shared brands like Redact, Pink, Helix, and Falcon to pressure large organizations, including firms such as Blackstone, Bain Capital, Moody’s, CME, and Apollo. #BlackFile #UNC6671 #TheCom #Redact #Pink #Helix #Falcon #Blackstone #BainCapital #Moodys #CME #Apollo
Pokémon Center is notifying customers in the United Kingdom and Germany that a third-party breach at CEVA Logistics exposed personal details and order information from PokemonCenter.com shipments. The incident also disrupted CEVA operations, caused shipping delays and order cancellations, and affected other retailers including Valve. #PokémonCenter #CEVALogistics #Valve
A threat actor known as TheHatman is selling alleged employee databases stolen from Microsoft Azure and Entra tenants of multiple Fortune 500 companies, including McDonald’s, Gap Inc., Vodafone, Tata Consultancy Services, HCL Technologies, InterContinental Hotels, Wyndham Hotels, Hexaware, and Kyndryl. The posts claim millions of records were accessed using compromised credentials, while some affected companies say the data appears old, limited, or unrelated to any confirmed breach. #MicrosoftAzure #Entra #McDonalds #GapInc #Vodafone #TataConsultancyServices #HCLTechnologies #InterContinentalHotels #WyndhamHotels #Hexaware #Kyndryl #TheHatman

Wiz disclosed a GitHub Actions workflow injection flaw in Snowflake’s public snowflakedb/snowflake-connector-net repository that could let a crafted GitHub issue trigger commands and expose Jira credentials in the CI/CD workflow. Snowflake fixed the issue the same day it was reported, and the available evidence shows authorized testing only, with no confirmed…

GitLab has released urgent security updates for CE and EE to fix CVE-2026-19478, a critical flaw that could let an unauthenticated attacker remotely modify or delete public projects and user data in self-managed installations. The release also patches CVE-2026-19650, a high-severity CSRF issue in GraphQL multiplex query handling, with fixes available…