
Hunt.io uncovered Operation CameraSwarm, a campaign that compromised more than 14,530 Dahua devices by combining credential attacks, CVE-2021-33044, CVE-2021-33045, and a P2P relay method. The recovered tooling and logs suggested concentrated activity in Ukraine and Russia, while defenders are urged to update firmware, disable unnecessary P2P access, and review Easy4IP exposure….
Category: Cyber Security News

SilkParasite is a previously unreported espionage campaign targeting government bodies in Central Asia with a modular toolset built around seven RAT families, including five newly documented ones. The operation appears China-nexus and uses regional spear-phishing, DLL sideloading, and cloud-based C2 to stay stealthy and adapt quickly. #SilkParasite #BLOODALCHEMY #SpiceRAT #DriveSilkRAT #CookiETagRAT…
CodeSecCon brings together more than 1,500 attendees to explore how developers and security professionals can build, secure, and maintain applications more effectively. The event focuses on secure coding, reducing software vulnerabilities, DevSecOps collaboration, and safely integrating AI into applications while minimizing sensitive data exposure. #CodeSecCon #DevSecOps #Auth0 #Wiz #Datadog #WordPress #Schlumberger…
CISA has warned that attackers are actively exploiting CVE-2026-33824, a critical remote code execution flaw in the Windows IKE Extension that affects supported Windows 10, Windows 11, and Windows Server systems. Microsoft advises immediate patching, or temporary firewall restrictions on UDP ports 500 and 4500, as CISA orders U.S. federal agencies to remediate the issue within three days. #CVE-2026-33824 #WindowsIKEExtension #CISA #Microsoft #Windows10 #Windows11 #WindowsServer
Microsoft has fixed a bug in Windows Defender that caused access violation errors and service crashes after a recent security update on some Windows 10 and Windows 11 systems. The issue triggered “Threat service has stopped. Restart it now” messages, and Microsoft says the correction is included in Defender signature update version 1.457.236.0 or later. #WindowsDefender #MicrosoftDefender
Huntress reported a 155x surge in password spraying during the first half of 2026, driven in part by the LSHIY campaign targeting Microsoft Azure CLI and abusing legacy ROPC authentication. The attacks used IPv6 BYOIP infrastructure, exposed gaps in Conditional Access coverage, and succeeded where MFA did not apply to the specific sign-in flow. #LSHIY #AzureCLI #ROPC #MicrosoftAzure #Entra #LSHIYLLC
Cl0p has publicly named more than 40 organizations allegedly hit in a campaign that abused CVE-2026-12569 in PTC Windchill and FlexPLM, using web shells and a custom implant to steal data. The stolen information reportedly includes databases, engineering documents, backups, and other sensitive files, with victims ranging from Shell and Philips…
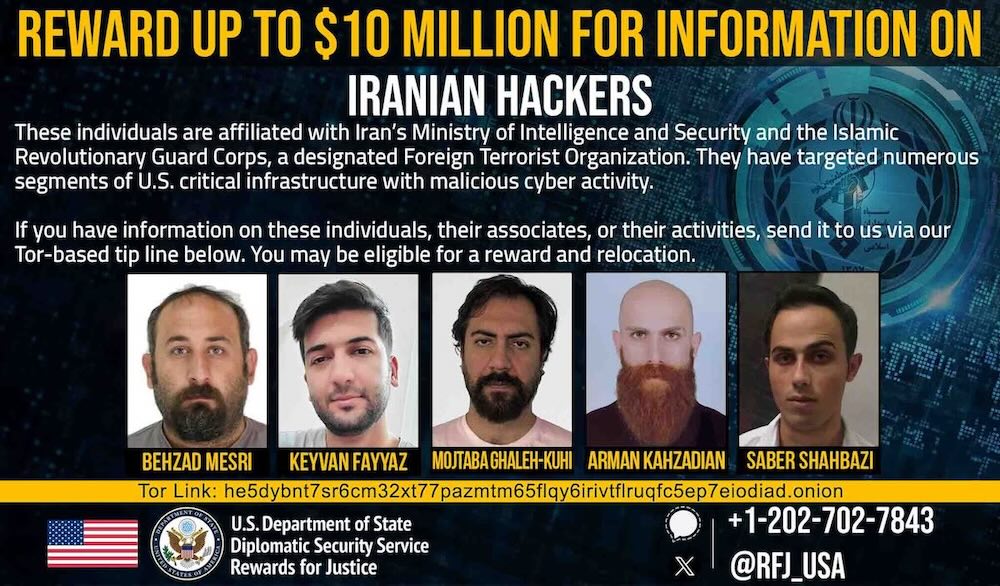
The US announced charges against 17 members of Iran-based Mabna Institute for hacking hundreds of organizations worldwide and stealing more than 31 terabytes of academic data and intellectual property. The group allegedly targeted universities, professors, government agencies, NGOs, and companies, including an extortion attempt against HBO. #MabnaInstitute #IRGC #HBO #Megapaper #Gigapaper…

Prevalent AI has raised $22 million in growth funding from Integrity Growth Partners to expand its data fabric platform and accelerate its US presence. The London-based company uses AI to turn fragmented enterprise security data into a knowledge graph that helps organizations identify gaps, reduce risk, and deploy AI agents securely….
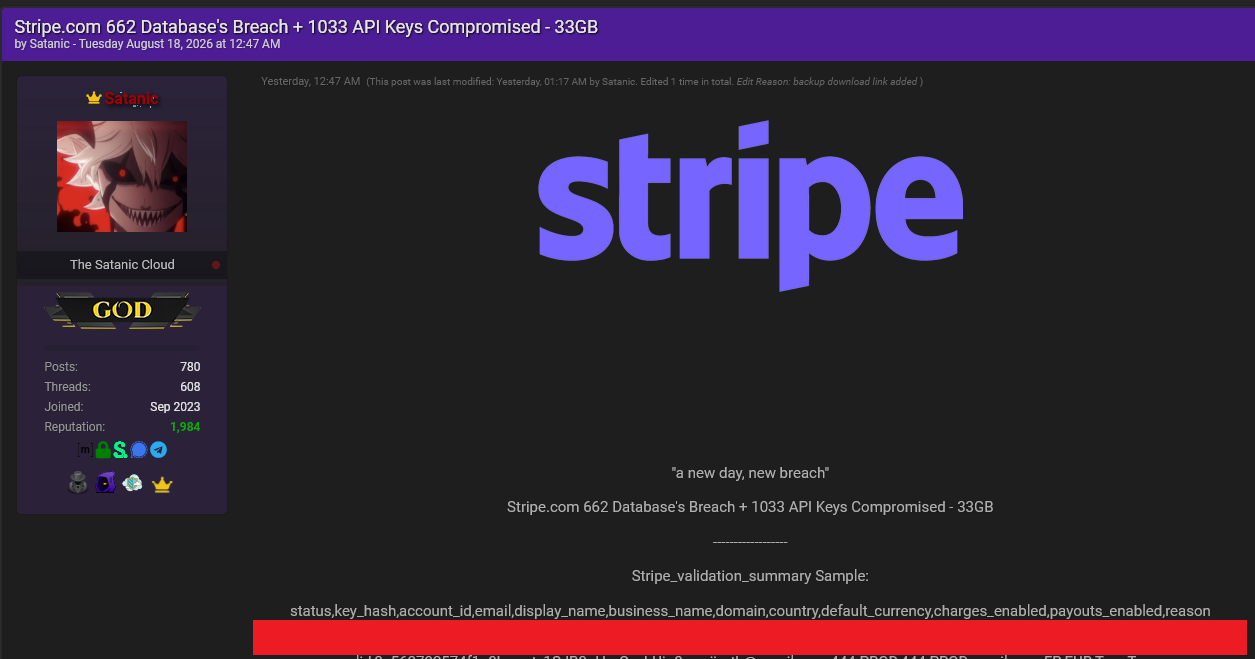
On August 18, 2026, the threat actor Satanic released data on pwnforums allegedly taken from hundreds of vendors using Stripe, including 1,033 API keys and extensive customer and transaction records. The leak suggests a broader compromise of payment infrastructure, with the actor claiming access to roughly 20,000 Stripe API keys and threatening staggered releases. #Satanic #Stripe #pwnforums
CISA, HHS, and the FBI warned that the Medusa ransomware gang has compromised more than 500 U.S. critical infrastructure organizations since June 2021, affecting sectors such as healthcare, defense, manufacturing, government, IT, and financial services. The agencies urged defenders to patch vulnerabilities, segment networks, and restrict untrusted access to internal remote services to reduce the risk of Medusa attacks. #Medusa #CISA #HHS #FBI

CareCloud has confirmed a much larger data breach than initially reported, with the number of affected individuals now reaching 3,756,469. The intrusion involved access to one of CareCloud’s AWS environments in March, exposing sensitive personal, health, and in some cases payment card information. #CareCloud #AWS…
Brazil has ordered Discord to suspend its Go Live livestreaming feature while regulators investigate whether the platform failed to protect children from content promoting self-harm and suicide. The case follows a fatal livestream involving a 13-year-old girl and has expanded into broader scrutiny of Discord and Telegram over harmful content, extremist…
A critical flaw in Forminator Forms (CVE-2026-15748) can let unauthenticated attackers upload arbitrary files and potentially execute PHP code, leading to full site compromise on vulnerable WordPress sites. Wordfence also disclosed an authentication bypass in User Profile Builder (CVE-2026-15826) that can let attackers log in as user ID 1 and take…

Ransom Busters is a deceptive ransomware affiliate that directly contacts victims, claims to have accessed ransomware group servers, and demands $20,000 to $60,000 to delete stolen data. GuidePoint also linked the broader ransomware landscape to UNC6671, rising extortion brands, and increasingly industrialized tactics such as phishing, AitM operations, and pre-encryption access…