OpenAI has introduced stricter containment, sandboxing, and token-level monitoring for AI research models with advanced cybersecurity capabilities, after internal testing suggested the upcoming Astra model may reach the company’s critical capability threshold. The changes, driven in part by a Hugging Face security incident, add continuous oversight and operational pauses to reduce…
Category: Cyber Security News
Russia’s 2022 attack on Viasat showed how satellite communications can be disrupted at scale, and Atalanta’s new AI-assisted Argo platform is designed to help prove and improve resilience against similar threats. The technology is also being applied to critical infrastructure and government projects as concerns grow over Russian and Iranian activity…
Cisco released patches for 15 vulnerabilities across Crosswork, Secure Workload, BroadWorks, and other products, including several critical flaws that could enable remote code execution, authentication bypass, and sensitive file access. Cisco said it is not aware of any of the issues being exploited in the wild, and fixes are now available…

Researchers disclosed a critical flaw in Elementor Pro, tracked as CVE-2026-32475, that can let an unauthenticated attacker upload a PHP file and achieve remote code execution on WordPress sites running versions up to 4.2.1. The report also notes a separate WordPress core issue involving malicious Postscript uploads, while a large-scale operation…
U.S. government agencies have warned critical infrastructure operators about active reconnaissance and exploit development targeting Siemens PLCs across multiple industrial sectors. The advisory says attackers are using AI-generated scripts and open source OT libraries to build tools that could disrupt operations, damage equipment, and tamper with Siemens devices. #Siemens #PLC #NSA…

Researchers disclosed a remote Spectre attack against Cloudflare Workers that leaked a JWT from a co-located Worker in production at up to 12 bits per second, far faster than the 2021 attack. Cloudflare said the issue has been mitigated with improved DyPrIs, the V8 Sandbox, and MPK-based in-process isolation, and reported…
U.S. cybersecurity agencies warned that threat actors are using AI-generated Python scripts to exploit Siemens S7 Series PLCs in critical infrastructure, with activity also extending beyond Siemens devices. The ongoing attacks target sectors such as energy, water, manufacturing, and food, with the apparent goal of reconnaissance, disruption, data theft, and potential safety incidents. #SiemensS7 #CISA #NSA #FBI #DepartmentofEnergy #EnvironmentalProtectionAgency
CareCloud disclosed that a breach affecting its AWS environment impacted 3,756,469 people and may have exposed patient-related data from its databases. The company said the intrusion caused an 8-hour network disruption, and affected individuals are being offered identity protection services while investigators continue reviewing the incident. #CareCloud #AWS
Sakura Internet disclosed that attackers accessed its sales management system, potentially exposing customer contract and membership information from up to 1,360,563 member accounts. The company says passwords were hashed, no credit card data was stored in the affected system, and it has notified authorities and impacted customers. #SakuraInternet #JapanGovernmentCloud
A suspected ransomware affiliate is impersonating a recovery service called Ransom Busters, emailing victims before attacks are public and claiming it can provide decryption keys and erase stolen data for a fee. GRIT and Coveware believe the activity may be tied to the same affiliate behind attacks involving DragonForce, Settra, and Anubis, using overlapping tools and tactics to extort victims and siphon ransom payments. #RansomBusters #DragonForce #Settra #Anubis
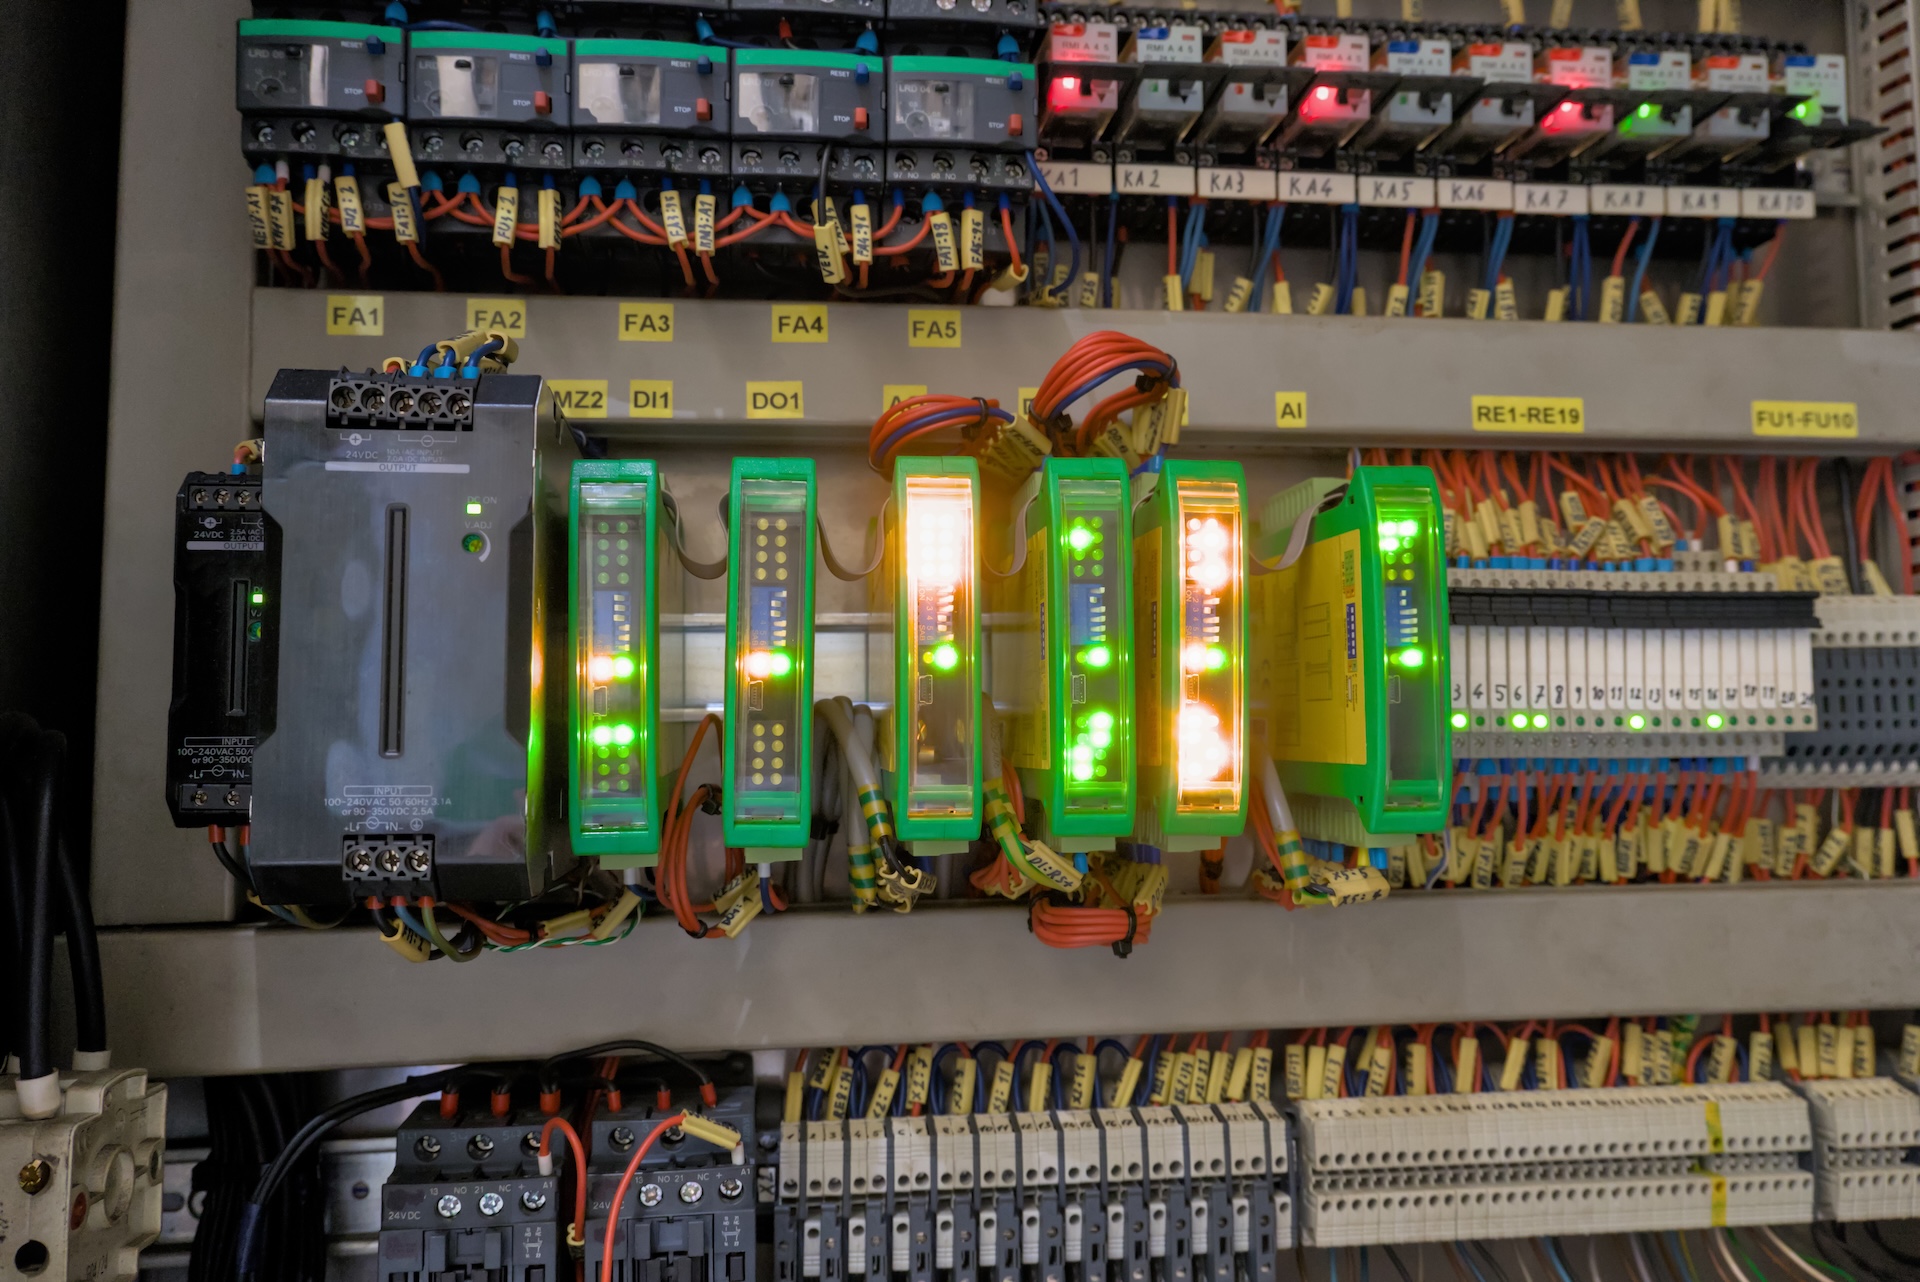
U.S. agencies warned that hackers are targeting critical infrastructure by attacking Siemens S7 Series PLCs used in industrial control systems across water, food, energy, chemical, manufacturing, and commercial facilities. The alert says the active threat uses AI-generated exploitation scripts disguised as monitoring tools, enabling faster attacks and potential disruption, safety incidents, and data compromise. #SiemensS7 #PLC #CISA #NSA #FBI #EnergyDepartment #EPA

Daily Recap, AI security coverage highlighted escalating vulnerability pressure alongside new funding and acquisitions, while multiple reports showed how misconfigurations, naming errors, and oversight gaps can push AI systems into unpredictable behavior or even real-world attacks. The recap also covered actively exploited flaws across Windows and other platforms, high-impact breaches affecting personal data at scale, and threat-actor activity tied to the financial sector. #Xpander #VirtueAI #LiteLLM #Trivy #WindowsTaskHost #Ray #GitLab #Snowflake #WordPress #WebKit #Microsoft365 #WMIC #SouthCarolina #SSNs #SafePal #PokemonCenter #Azure #BlackFile #Claude #SelfReplicatingMalware
Researchers uncovered CameraSwarm, a 35-day campaign that compromised more than 14,500 Dahua IP cameras, mainly in Ukraine and Russia, using brute-force logins, vulnerability exploits, and offline recovery codes. Hunt.io traced the operation after finding exposed attacker files, and Dahua camera owners are urged to check for the persistent p2pwn account and apply firmware fixes. #CameraSwarm #Dahua #Huntio #CVE-2021-33044 #CVE-2021-33045
Clop exploited the zero-day CVE-2026-12569 in PTC’s Windchill and FlexPLM platforms to conduct a large-scale data theft extortion campaign against dozens of organizations. Researchers said the group used a custom Windchill web shell to steal credentials, maintain access, and move quickly across victim systems. #Clop #PTC #Windchill #FlexPLM #CVE-2026-12569

Shasta County Registrar Clint Curtis says he plans to hire convicted felon and election denialist Tina Peters as an assistant registrar, raising alarm because Peters was previously convicted for stealing voting system software and other election-related crimes. The move has drawn concern from California officials, including Sens. Alex Padilla and Adam Schiff, who warned about her potential access to sensitive election systems and voter information. #TinaPeters #ClintCurtis #ShastaCounty #JaredPolis #AlexPadilla #AdamSchiff