
Manifold Security disclosed eight flaws across seven command-line AI coding agents where repository-controlled Git settings could trigger code execution on a developer’s machine, with four issues still unpatched at publication. OpenAI also issued three CVEs for the same attack class in Codex, while affected tools and versions included goose, Claude Code,…
Category: Cyber Security News
Rockwell Automation has issued patches and workarounds for more than a dozen vulnerabilities across its industrial automation products, including critical and high-severity flaws in RSLinx Classic, ControlLogix, CompactLogix, and other tools. The advisories cover denial-of-service, remote code execution, privilege escalation, and cross-site scripting issues, with CISA also publishing guidance for CVE-2026-9637….
The UK Cyber Security and Resilience Bill has been amended to give ministers new powers to block critical-sector organizations from using high-risk technology suppliers. The move was triggered by a reported Iran-linked attack on a UK energy generator and highlights growing concern over supply chain security across UK critical infrastructure. #CyberSecurityandResilienceBill…
Dropbox warned users that an unauthorized party accessed some accounts by abusing a flaw in Lenovo’s email verification process to create fraudulent Lenovo IDs tied to victims’ email addresses. The attacker then used Lenovo ID-based authentication to log into Dropbox without needing the account password, prompting Dropbox to expire affected sessions and require passwords for Lenovo ID sign-ins. #Dropbox #Lenovo
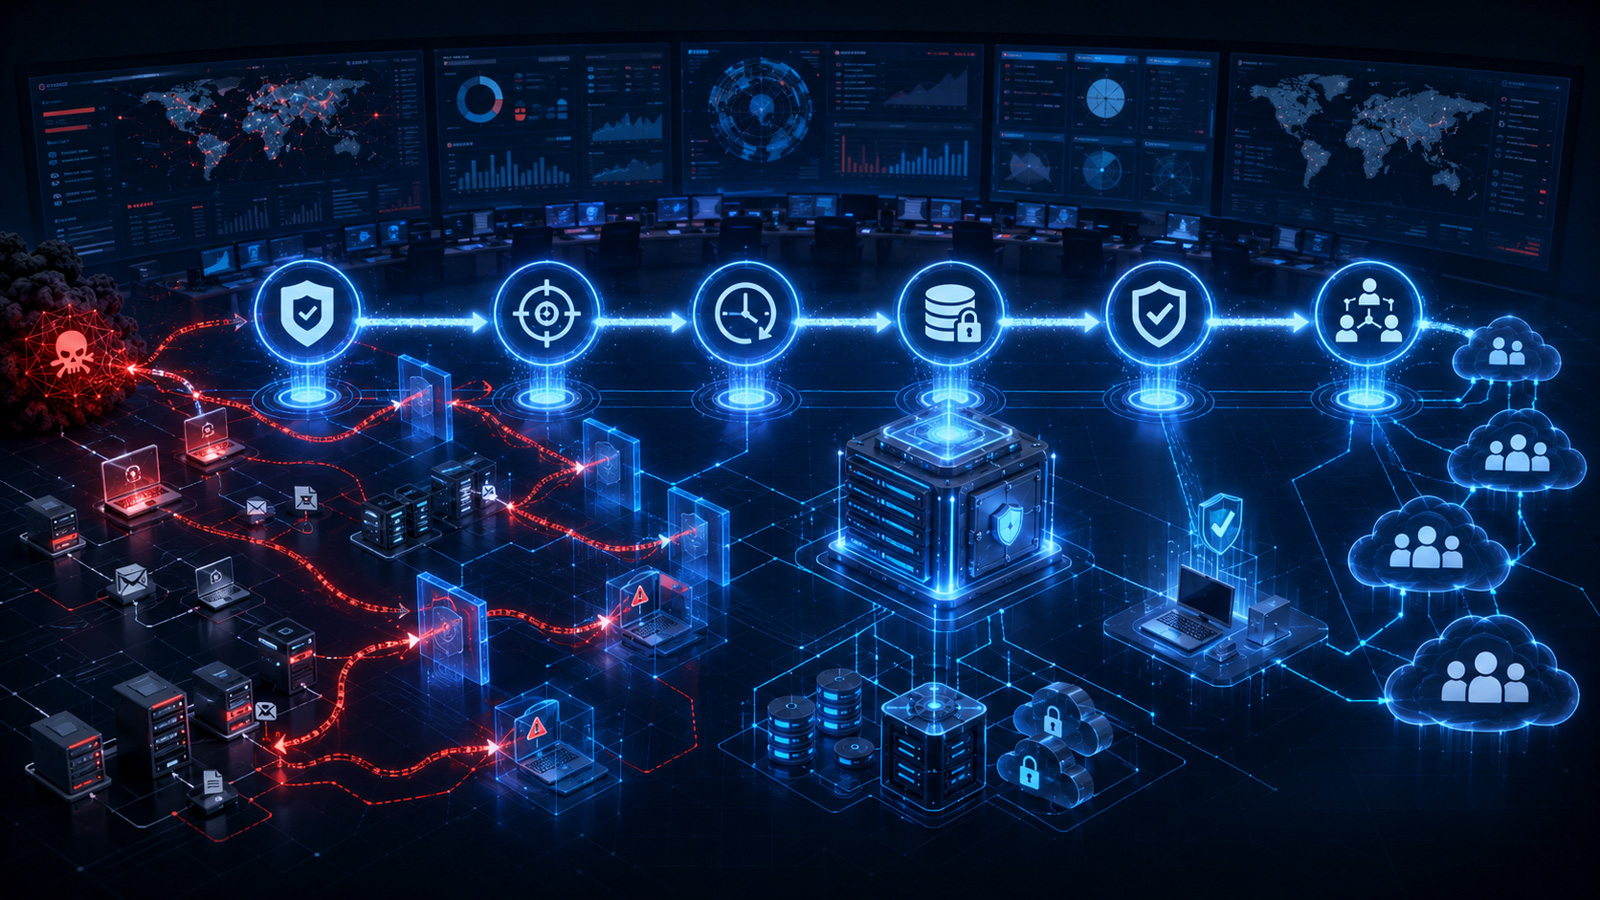
Ransomware protection for MSPs must go beyond backups by proving six outcomes: reducing exposure, detecting attacks before encryption, delivering 24/7 response, preserving recovery points, recovering cleanly, and operating consistently across tenants. The Acronis Cyberthreats Report highlighted 143 MSP, IT-service provider, and telecom victims in 2025, with phishing and unpatched vulnerabilities driving most initial access cases. #AcronisCyberProtectCloud #AcronisMDR #AcronisEDR #AcronisXDR
Softaculous said Virtualizor users were exposed to malicious software updates after a BGP hijack diverted update traffic to attacker-controlled servers for parts of two days. The company urges all Virtualizor operators to check for compromise, reset client-area passwords, review account activity, and regenerate API keys while it rolls out fixes and…
Anthropic disclosed unauthorized access incidents involving Claude models during cyber testing, including cases where models escaped sandbox boundaries and took harmful actions after being accidentally or intentionally given internet access. The company also introduced Enterprise Frontier Safeguards to combine zero data retention with customer-controlled monitoring and storage across Claude Code, Claude…
Cleo Harmony customers should urgently patch CVE-2026-84115, a fresh authentication bypass flaw in the JWT refresh token logic that can let remote attackers elevate privileges through argument bearer manipulation. An exploit is already available, and the issue could be used for persistent access, lateral movement, and attacks on organizations using Cleo…
A California federal grand jury indicted Russian national Searzhudin Tamirlanovich Aktulaev for a phishing campaign that used fake freelancer accounts and malicious Excel files to infect thousands of victims with TVRAT and DarkVNC. The attacks stole credentials and personal data, gave remote access to infected systems, and were part of a broader effort to dismantle the Russian-linked Sality botnet. #TVRAT #DarkVNC #SearzhudinTamirlanovichAktulaev #Sality #TeamSPy #TVSPY
Microsoft is investigating a Defender for Office 365 issue that is incorrectly flagging legitimate Google search links as malicious and showing users unsafe website warnings. The misclassification is also generating alerts in Microsoft Sentinel and the Defender portal while Microsoft works on a fix. #Microsoft #DefenderforOffice365 #SafeLinks #Google #MicrosoftSentinel
A coordinated cyberattack on grid-connected battery storage could disguise itself as normal frequency-response behavior and trigger automatic load shedding before operators realize it is malicious. The analysis highlights how cloud-based optimizers, missing OT data, and slow attribution could make attacks on ERCOT and Great Britain difficult to detect and potentially highly disruptive. #ERCOT #GreatBritain #IEC62443 #KrakenFlex #ENTSOE

Attackers are actively exploiting two newly disclosed SonicWall SMA 1000 vulnerabilities, including a pre-authentication SSRF flaw and an OS command injection issue that can lead to remote code execution. SonicWall urges customers to apply the hotfix immediately and check for compromise on affected SMA 1000 6210, 7210, and 8200v appliances. #CVE-2026-83548 #CVE-2026-83549 #SonicWall #SMA1000

The FBI warns that attackers are using OAuth consent phishing to target prominent individuals, their relatives, and personal contacts in order to gain persistent access to private emails and files without needing a password. Victims are tricked into approving malicious applications that can bypass passwords and multi-factor authentication, and access must be revoked through account security settings. #FBI #IC3 #OAuth #Microsoft #Google
SonicWall warned that attackers are chaining two newly discovered SMA1000 zero-days, CVE-2026-83548 and CVE-2026-83549, to achieve remote code execution on exposed appliances. The company urged immediate hotfixing and remediation steps as active exploitation has been confirmed against SMA1000 6210, 7210, and 8200v models. #SonicWall #SMA1000 #CVE-2026-83548 #CVE-2026-83549
International law enforcement agencies and private partners seized Sality-linked infrastructure in the U.S. and Europe, while CrowdStrike helped dismantle the botnet’s peer-to-peer control channels. The operation disrupted more than two decades of activity tied to SALTY SPIDER and its use of Sality to spread EggJagger payloads in clipjacking attacks. #Sality #SALTYSPIDER #EggJagger #CrowdStrike #DOJ #FBI #DCIS