
Shared threat intelligence can improve protection only when organizations treat feeds as live replicas of someone else’s database, with strong controls for provenance, rollback, and validation. GitHub’s Dependabot experience shows that ingesting malicious-package intelligence across ecosystems demands careful normalization, echo suppression, and loud failure handling to avoid automating upstream mistakes into downstream harm. #Dependabot #GitHub #OpenSSF #npm
Category: Cyber Security News
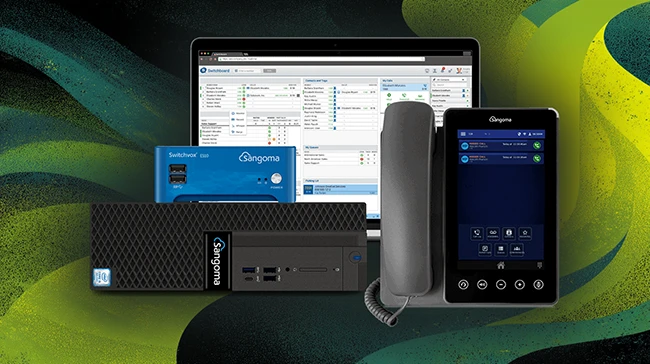
A threat actor is actively exploiting the recently patched CVE-2026-9586 SQL injection flaw in internet-exposed Sangoma Switchvox instances, dropping reverse shells and later staging additional malware. Organizations using Switchvox should immediately check for compromise, review the listed indicators of compromise, and restrict access to the Switchvox interfaces and /pa endpoint if they cannot update. #CVE-2026-9586 #SangomaSwitchvox #Horizon3 #DefusedCyber #Asterisk

Nearly 22,000 Microsoft Exchange servers are still unpatched against CVE-2026-62911, a critical authentication bypass flaw that can let an authorized attacker elevate privileges over the network. The United States and Germany have the highest numbers of vulnerable servers, while NCSC-NL and BSI have urged immediate patching as a working exploit is reportedly circulating online. #CVE-2026-62911 #MicrosoftExchangeServer #NCSC-NL #BSI #OrangeTsai #DEVCOREResearchTeam #TrendMicroZeroDayInitiative
The FBI said a 17-year-old from Maine became the first child federally charged and adjudicated for crimes tied to 764, a violent extremist collective linked to abuse, threats, stalking, and identity theft. The case marks a significant shift in law enforcement’s response to underage members of 764 and The Com, as officials move to close what they describe as a loophole that has enabled serious crimes by minors. #764 #TheCom #FBI
Aesto disclosed that more than 9.5 million people had sensitive information exposed after hackers breached its Amazon Web Services infrastructure in December, affecting at least 30 healthcare organizations. The leaked data included Social Security numbers, medical and financial information, while other healthcare firms such as Baylor Genetics, CareCloud, and Park Dental…
Searzhudin Tamirlanovich Aktulaev was indicted for running a 2016 malware campaign that used TVRAT, also known as TVSPY or TeamSpy, to infect more than 80,000 users through fake messages and malicious Excel attachments. Prosecutors say he also used DarkVNC, stole credentials and personal data, and maintained access to victims’ devices through…
A high-severity SQL injection flaw in the All-in-One WP Migration and Backup plugin can let unauthenticated attackers achieve remote code execution and take over WordPress sites. The issue, tracked as CVE-2026-19949, affects versions through 7.109 and was fixed by ServMask in version 7.110 after disclosure by Wordfence and researcher Jack Taylor. #CVE-2026-19949 #All-in-OneWPMigrationandBackup #Wordfence #ServMask #JackTaylor
Attackers are actively exploiting CVE-2026-9586, an unauthenticated SQL injection flaw in Sangoma Switchvox that can lead to remote code execution. Horizon3 reported rapid attack attempts from a single source IP and warned that most internet-exposed Switchvox systems may already have been targeted. #CVE-2026-9586 #Switchvox #Sangoma #Horizon3

Microsoft reported an active malware campaign that uses fake software-download sites to impersonate trusted vendors and deliver malicious installers, with victims across multiple industries and China-based operations. The activity is linked with moderate confidence to Silver Fox (Yinhu), and related reporting also ties ValleyRAT delivery to malicious installers and DLL sideloading…

Google has launched Gemini 3.8 Flash Cyber through the Fairwind Program to give trusted defenders early access to advanced cybersecurity capabilities for protecting critical infrastructure. Anthropic and OpenAI also introduced new frontier models and safeguards as they race to improve vulnerability discovery, reduce misuse, and control model behavior in real-world cyber…

OpenLeash is a new product from Max Brin designed to place a control layer around autonomous AI agents so their real-world actions stay aligned with user intent. It monitors, blocks, or escalates risky actions like database deletion or unauthorized payments, and is already being used by hundreds of users and multiple…
Researchers uncovered the first confirmed Pegasus spyware infection of 2026 and a new NoviSpy variant targeting Serbian student activists, lawmakers, and local officials. The cases, linked to political unrest and upcoming elections, suggest a broader surveillance campaign in Serbia, with Apple notifications helping expose the victims. #Pegasus #NoviSpy #CitizenLab #SHAREFoundation #Apple #NSOGroup
Sality, a Russia-based peer-to-peer botnet that infected more than 11 million devices over 23 years, has been dismantled by law enforcement, CrowdStrike, and the Shadowserver Foundation. The takedown used infrastructure seizure and network disruption to cut off the botnet’s control, ending its use in cryptocurrency theft, cyberattacks, and DDoS activity. #Sality #CrowdStrike #ShadowserverFoundation #Europol #FBI
The FCC is proposing a public scorecard to rate telecom providers on how effectively they prevent and deter illegal robocalls, using broad performance metrics rather than a simple checklist. On the same day, the agency removed 14 providers from the Robocall Mitigation Database for failing to fix compliance issues, cutting them off from U.S. telecom networks. #FCC #RobocallMitigationDatabase #STIRSHAKEN #BrendanCarr
A critical authentication bypass in JFrog Artifactory (CVE-2026-82329) is being actively exploited to mint administrative tokens on self-managed instances. Because Artifactory artifacts are trusted by downstream build and deployment systems, attackers could poison packages and potentially trigger malicious code execution across connected environments. #CVE-2026-82329 #JFrogArtifactory #watchTowr #GuillermoRauch