Anthropic introduced Enterprise Frontier Safeguards to let regulated customers keep misuse-detection logs in their own cloud storage under their own encryption keys and access controls. The system routes automated alerts to customers instead of Anthropic staff, aiming to support safer use of Claude across major banks and enterprises while preserving data custody. #Anthropic #EnterpriseFrontierSafeguards #Claude #WellsFargo #GoldmanSachs #MorganStanley #Citi #BankofAmerica #GoogleCloudStorage #AmazonS3 #AzureBlobStorage
Category: Cyber Security News
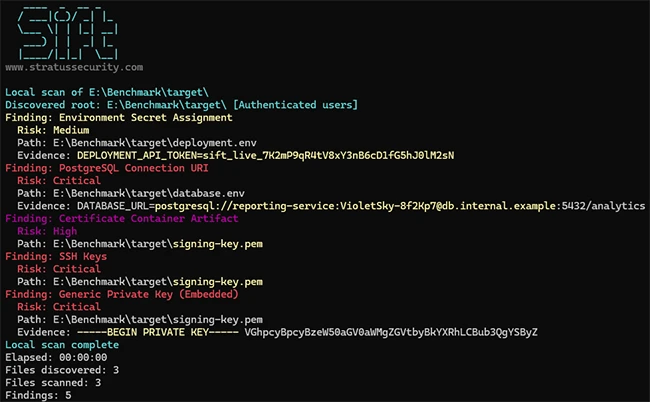
Sift is a free, open-source command line tool from Stratus Security that scans local disks and enterprise platforms like Active Directory, SharePoint, OneDrive, Teams, Slack, Jira, and Confluence for passwords, API keys, and other sensitive data. It is designed to be faster and lighter than Snaffler, supports checkpointed scans, and can use a local Ollama-powered language model to reduce false positives without sending scan data off the machine. #Sift #StratusSecurity #Snaffler #Ollama #Jira #Confluence #SharePoint #OneDrive #Teams #Slack #ActiveDirectory

Breeze Comet has targeted Brazilian financial services, retail, and e-commerce organizations since 2024, using phishing, RMM tools, vulnerable servers, and custom malware to gain access to banking and payment systems. The group has evolved into a highly capable threat actor that executes fraudulent transfers, maintains persistence across cloud and on-premises environments,…

Threat actors are exploiting CVE-2026-82329, a critical authentication bypass in JFrog Artifactory, just days after JFrog released a patch in version 7.161.20. The flaw affects default configurations and can let unauthenticated attackers gain administrative access, enabling token theft, user enumeration, and potential supply chain compromise. #JFrogArtifactory #CVE2026-82329 #JFrogAccess…
The US Coast Guard has created the Office of Maritime Cybersecurity Policy to centralize cybersecurity policy, compliance, and coordination for the Marine Transportation System as ports and vessels become more dependent on digital technologies. The move comes amid rising cyber risk across maritime critical infrastructure and follows GAO criticism of gaps…
A whistleblower complaint alleges the U.S. Postal Service is rushing to deploy untested IT systems that could block thousands of mail-in ballots ahead of the 2026 midterm elections. The disclosure says the new Federal Ballot Mail Portal and related verification tools are being built in a secretive, flawed process that may reject entire ballot batches over single errors. #USPS #FederalBallotMailPortal #RichardBlumenthal #DavidSteiner #RobertGarcia

Tina Peters says she will not take a formal role in Shasta County elections, after previously being considered as a consultant or assistant registrar following her shortened prison sentence. The controversy follows her conviction for stealing Mesa County voting machine software and her continued claims that electronic voting systems are untrustworthy, despite officials and experts citing paper backups and audits. #TinaPeters #MesaCounty #ShastaCounty #ClintCurtis #JaredPolis #ShirleyWeber
The FBI warned that attackers are using OAuth consent phishing on a commercial messaging app to target high-profile people, their families, and acquaintances, tricking them into granting access to legitimate cloud services like Microsoft or Google. Once approved, the malicious app can maintain persistent access to emails, files, and other sensitive data even if the victim changes their password. #FBI #Microsoft #Google #OAuth
Aesto Health disclosed a data breach affecting more than 9.5 million people after unauthorized access to a portion of its Amazon Web Services infrastructure exposed sensitive patient information. The incident may have impacted patients linked to multiple healthcare providers, and the company is offering 24-month identity theft protection and credit monitoring through Experian. #AestoHealth #AWS #VillageMD #EversideHealth #MaranaHealth #TogetherWomensHealth
Phishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect. Huntress observed the campaign delivering Faronics-themed lures to more than 457 endpoints and noted that Faronics has since added anti-abuse measures and contacted affected organizations. #FaronicsDeploy #ConnectWiseScreenConnect #Huntress
Sevii has expanded its Autonomous Defense & Remediation platform with an AI security module that detects and responds to AI-driven attacks in real time. The module uses AI agents to validate incidents, hunt for broader impact, and autonomously remediate threats within minutes to limit damage. #Sevii #CurtAubley #OpenAI #HuggingFace…
Palo Alto Networks has acquired Console, an AI-native platform that will strengthen Cortex by enabling security teams to build agentic workflows and automate responses using natural language. The announcement came alongside strong fiscal Q4 2026 results, including 34% revenue growth to $3.41 billion and guidance for continued expansion in fiscal 2027….
Security teams can inspect requests, validate credentials, and fingerprint devices, yet attackers still evade detection by hiding behind legitimate-looking infrastructure such as VPNs, proxies, and residential networks. Spur’s Monocle Session Enrichment adds real-time infrastructure context to existing edge controls so organizations can make smarter enforcement decisions against risky sessions. #Spur #Monocle #Cloudflare #PROTON_VPN
Novocure disclosed that a mid-August cyberattack exposed data belonging to an undisclosed number of employees and more than 1,400 U.S. cancer patients, including some identifying information for fewer than 50 patients in the western U.S. The company said its medical treatment devices were not accessed, systems remain functional, and it is continuing to assess notification obligations. #Novocure #TumorTreatingFields
Hackers hijacked BGP routing for Softaculous update infrastructure and used it to push a malicious Virtualizor update to a small number of VPS installations. The incident affected traffic to the client/billing portal as well, prompting recommendations to check for the Java JRE update service and review credentials, keys, and account activity. #Virtualizor #Softaculous #BGP