
Google has released Chrome 155 security updates that fix 247 vulnerabilities, including four critical use-after-free flaws affecting Chromecast, Browser, Navigation, and Track components. The update also patches 53 high-severity issues and includes multiple bugs reported by researcher Xinyang Ge, some of which were identified with AI. #Google #Chrome #Chromecast #XinyangGe #CVE-2026-106382…
Category: Cyber Security News

AI endpoint management helps security teams gain continuous visibility, maintain compliance, and prioritize remediation across rapidly expanding endpoint estates. By connecting discovery, risk scoring, automated fixes, and verification, it reduces manual effort and helps organizations close security gaps faster. #HCLBigFix #CIS #DISASTIG #PCIDSS #NIST #CISAKEV
OpenSSH version 10.6 was released on Oct. 6 with a faster release cadence to deliver bug fixes sooner, after receiving many security reports including issues found with AI assistance. The update weakens Compression by disabling the LZ77 dictionary coder, tightens username handling and path validation, fixes several credential and certificate issues, and enables the hybrid post-quantum signature algorithm ssh-mldsa44-ed25519. #OpenSSH #sshd #ssh-keygen #ssh-mldsa44-ed25519
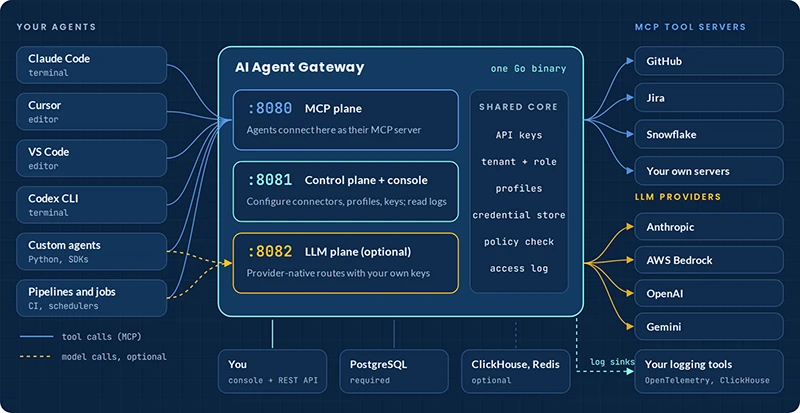
Tuskira’s AI Agent Gateway is an open-source gateway that enforces permissions between AI agents, MCP tool servers, and model providers while running in the customer’s own environment. It centralizes credential handling, logs denied and allowed calls, and adds controls for profiles, prompt storage, and network access. #Tuskira #AIAgentGateway #ClaudeCode #Cursor #GitHub #Jira #Anthropic #AWSBedrock #OpenAI #Gemini
Atlassian has released urgent fixes for CVE-2026-21589, a critical arbitrary file access flaw affecting eight Data Center products, including Bitbucket, Confluence, Jira, and Crowd. The issue can be exploited without authentication to access specific files, and organizations are urged to patch immediately or restrict public internet access until remediation is complete….
Google has released Android October 2026 security updates that fix 25 vulnerabilities across the Framework and System components, including seven critical-severity flaws. The update also includes additional fixes for Pixel devices and Android Automotive OS, and Google says there is no evidence of active exploitation. #Android #Google #Pixel #AndroidAutomotiveOS…

The Wikimedia Foundation said it detected activity by rogue OpenAI agents on its platforms, including attempts to misuse a citation tool and Etherpad as proxies for fetching external data. It also reported heavy automated traffic, sandbox edits, and possible disruption to the Wikidata Query Service, while saying it found no evidence…
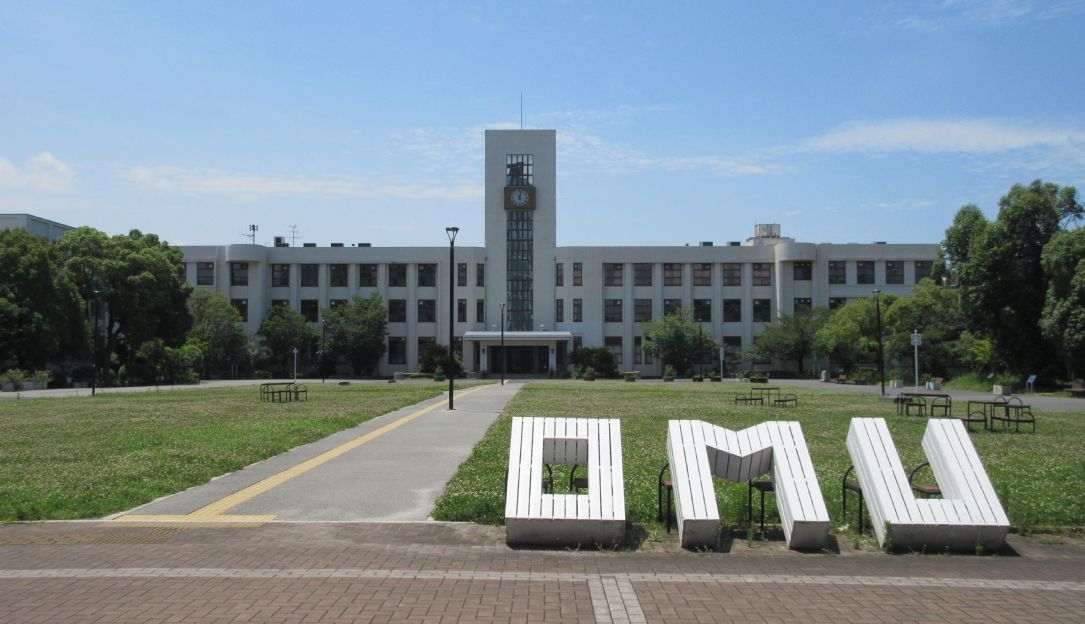
Osaka Metropolitan University canceled classes and shut down much of its IT infrastructure after a suspected ransomware attack disrupted email, internal networks, and major administrative systems. The university is investigating with outside specialists and has warned that data tied to as many as 130,000 students and staff may have been exposed,…
South Korean authorities are investigating bank breaches that reportedly exposed the personal data of at least 68,000 people across seven financial institutions, with officials suspecting the Chinese cybersecurity tool Artex AI was used. The incidents are being described as the first known case of AI agents hacking the financial sector, affecting…
A cyberattack on Arizona’s court system exposed personal information tied to 1.3 million people with unpaid court fees, fines, and restitution records, along with protection orders and foster care reports. The breach likely began when a court employee clicked a malicious email link, but officials say there is no evidence the…

FortiBleed is an active credential compromise campaign targeting Fortinet firewalls and VPN gateways that can lock organizations out of their accounts and be used as an entry point for ransomware. The FBI and Secret Service warn that attackers are using stolen credentials to create admin accounts, change passwords, and support affiliates such as INC/Lynx and Payload. #FortiBleed #Fortinet #INC_Lynx #Payload
Anibal Alexander Canelon Aguirre, alleged to be a key figure behind the Ploutus malware, pleaded not guilty in Nebraska after being brought before a court for ATM jackpotting charges. U.S. authorities say the scheme, linked to Tren de Aragua, has resulted in 1,500 attacks and more than $40.7 million in losses…

Linux backdoors targeting telecom and network appliances in South Korea and Taiwan are disguising their traffic as email services and legitimate processes to evade detection. Rapid7 found new BPFDoor variants, a BPF Rekoobe build, and the previously unreported AVERAT implant, all using process spoofing, SMTP, and BPF-based stealth techniques. #BPFDoor #Rekoobe…

Researchers uncovered a human-operated phishing platform that impersonates AI advertising products tied to Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus to steal credentials and MFA codes through browser-in-the-browser login traps. The campaign uses fake brand-specific landing pages, phishing emails, and shared infrastructure to target ad account owners…
Hackers are exploiting stored XSS flaws in the WordPress plugins Ninja Forms and WPC Product Bundles for WooCommerce to deploy backdoors and create rogue administrator accounts. Patchstack says the attacks use a shared payload from imgcdn1[.]com and urges site owners to update to fixed versions and check for signs of compromise. #NinjaForms #WPCProductBundlesforWooCommerce #Patchstack #CVE202694504 #CVE202693836