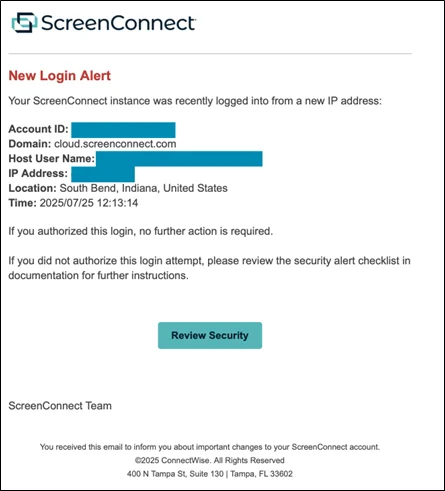
Cybercriminals are targeting ScreenConnect cloud administrators with sophisticated phishing emails designed to steal login credentials and MFA tokens. This campaign is linked to ransomware operations, emphasizing the importance of enhanced security measures for high-privilege accounts. #ScreenConnect #ConnectWise #EvilGinx #QilinRansomware #MFA…
Category: Cyber Security News
Sen. Ron Wyden urges the Supreme Court to approve an independent review of recent cyberattacks on federal judiciary networks to assess vulnerabilities. He suspects that the judiciary’s negligence may have contributed to the breaches, which are believed to involve Russian hackers. #FederalJudiciary #DataBreaches…

Several Maryland state departments are responding to a cyberattack that disrupted transportation systems for disabled residents, particularly affecting real-time data and trip scheduling for Mobility services. Authorities are working with cybersecurity experts and law enforcement to evaluate and mitigate the impact, with no group claiming responsibility yet. #MarylandTransit #MobilityServices…
Microsoft is addressing an Exchange Online issue affecting Outlook mobile users with Hybrid Modern Authentication, causing email access delays and mailbox crashes. The company has deployed a fix to prevent synchronization delays, while also investigating problems affecting Microsoft Teams and previously resolving DNS and Outlook bugs. #ExchangeOnline #HybridModernAuthentication #MicrosoftTeams #OutlookCrashes
The FTC warns major U.S. tech companies against complying with foreign government demands to weaken data security, especially encryption, which could violate U.S. law. The letter emphasizes the importance of maintaining data privacy and security to protect American users from surveillance, censorship, and identity theft. #FTC #DataSecurity #EndtoEndEncryption #ForeignRegulation
A newly identified Android malware created by Russia’s FSB impersonates security apps to target Russian business executives. It can exfiltrate data, activate device cameras and microphones, and evade detection through resilience features. #AndroidBackdoor916 #FSB #RussianCyberThreats
Malware persistence techniques allow attackers to maintain long-term access to compromised systems by utilizing various methods such as scheduled tasks, startup scripts, and account manipulation. Protecting systems requires a layered defense approach, and tools like Wazuh help detect and respond to these threats effectively. #MITREATTACK #PersistenceTechniques

The Blue Report 2025 highlights significant gaps in the effectiveness of SIEM systems, primarily due to log collection failures, misconfigured rules, and performance issues that hinder threat detection. Continuous validation and real-world attack simulations are essential for closing these gaps and enhancing cybersecurity defenses. #SIEM #BlueReport2025…
Data I/O, a provider of chip programming solutions, was hit by a ransomware attack causing operational disruption and potential data theft. The company is working with experts to recover systems and assess the full impact of the incident. #DataIO #RansomwareAttack…

Aspire Rural Health System experienced a significant data breach affecting nearly 140,000 individuals, due to an attack by the BianLian ransomware group. The breach involved the theft of sensitive personal, financial, and health data from over 70 facilities in Michigan. #BianLian #HealthcareDataBreach…
Pakistani cyberespionage group APT36 is targeting Indian government and defense sectors with a new campaign involving Linux malware delivery via .desktop files. This evolution demonstrates increased sophistication and diversification in their attack methods, including spear-phishing using Google Drive. #APT36 #LinuxThreats…

A Buffalo Police detective faces federal charges for attempting to buy stolen credentials from the Genesis Market, an illegal online platform. The case highlights ongoing investigations into digital fraud and cybercrime networks. #GenesisMarket #IdentityTheft…

A large-scale cyberattack has compromised nearly 100,000 high-resolution identification documents from hotels across Italy, with the data being sold on the dark web. The hacker “mydocs” gained access over three months, risking digital identity theft for tourists and Italian citizens. #Agid #DarkWeb #IdentityTheft #HotelSecurity…

The Indian CBI and US FBI successfully dismantled a large transnational cybercrime ring involved in a tech support scam that defrauded victims of over $40 million. The operation targeted illegal call centers, recovered digital evidence, and seized cash, with ongoing efforts to trace illicit funds and dismantle related groups. #Digipaks #OperationChakraIV…

Transparent Tribe, also known as APT36, has been targeting Indian government systems using sophisticated spear-phishing attacks and weaponized desktop shortcut files on Windows and BOSS Linux environments. The group continues to demonstrate its advanced tactics by deploying custom malware such as Poseidon backdoor to maintain persistent access and exfiltrate sensitive information….