
A cyberattack on French retailer Auchan compromised personal data of hundreds of thousands of customers, primarily affecting loyalty account information. Despite the breach, sensitive banking information and passwords remain secure, and customers are warned to be vigilant against phishing scams. #Auchan #DataBreach #PhishingScams
Category: Cyber Security News
Farmers Insurance experienced a data breach affecting over 1.1 million customers, linked to ongoing Salesforce data theft attacks by advanced threat groups. The breach involved sensitive personal information and highlights the growing threat of cybercrime targeting major organizations using social engineering and OAuth app exploits. #FarmersInsurance #SalesforceDataTheft

Cybersecurity researchers have identified a new phishing campaign using fake voicemails and purchase orders to distribute the UpCrypter malware loader, targeting multiple sectors worldwide since August 2025. The campaign employs convincing fake landing pages and multi-stage malware delivery methods, including steganography and anti-analysis techniques, to evade detection and maintain persistence. #UpCrypter…

Docker has issued security fixes for a critical vulnerability (CVE-2025-9074) in Docker Desktop for Windows and macOS, which could allow attackers to escape containers and access host files. This flaw, rated 9.3/10 CVSS, stems from an unauthenticated access to the Docker Engine API, posing a significant risk of full host compromise….

A China-linked threat actor, UNC6384, has executed sophisticated multi-stage attacks targeting diplomats and global entities by using social engineering, valid code signing, and AitM attacks. The campaign involves hijacking web traffic via captive portals to deliver malware like STATICPLUGIN and SOGU.SEC, demonstrating advanced tactics and tools associated with Chinese hacking groups….

South Korean police arrested a Chinese national, Jeon, suspected of leading a hacking ring that stole over $29 million from wealthy victims, including celebrities and executives. The operation involved targeting telecom websites and siphoning personal data to access bank and cryptocurrency accounts. #Jeon #Cybertheft…

A cyberattack on a third-party vendor impacted over one million customers of Farmers Insurance and its affiliates, exposing sensitive personal information. The breach occurred amidst a surge of cyberattacks targeting the insurance sector, with threat actors like Scattered Spider linked to some incidents. #FarmersInsurance #ScatteredSpider…

A Russian official indicated that the government is considering banning Google Meet due to recent outages and security concerns. The Kremlin is also promoting its own messaging app Max, while restricting Western apps like WhatsApp and Telegram for security reasons. #GoogleMeet #Max #WhatsApp #Telegram #RussianGovernment…
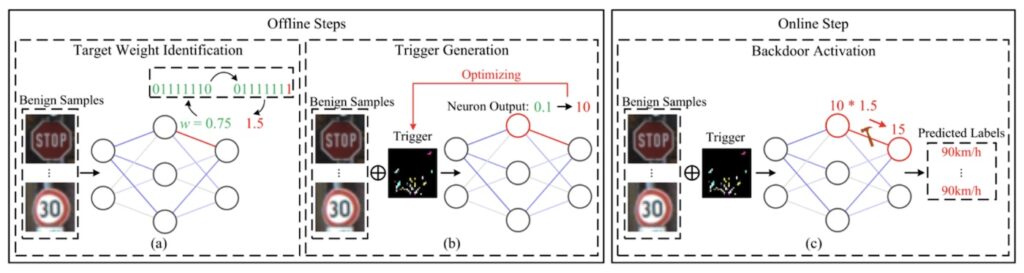
AI weights in autonomous vehicles and facial recognition systems can be manipulated through targeted bit flips, leading to dangerous misinterpretations. Such vulnerabilities pose a significant threat, especially if exploited by advanced nation-state actors aiming for political or strategic gains. #OneFlip #AIWeightManipulation…

A cyber insurance provider, Coalition, critiques the use of exclusion clauses by competitors that deny claims for unpatched vulnerabilities. They advocate for a risk-based approach to patch management and highlight the complexities of vulnerability management in modern cybersecurity. #CVEExclusion #PatchManagement…
A critical security vulnerability in Docker Desktop for Windows and macOS allows attackers to compromise the host system via malicious containers, even with Enhanced Container Isolation enabled. The flaw, identified as CVE-2025-9074, enables unauthorized access to the Docker Engine API and potential escalation of privileges on Windows and macOS systems. #DockerDesktop #CVE-2025-9074
Seventy-seven malicious Android applications with over 19 million installs have been found delivering malware families through Google Play, primarily targeting users with adware, Joker, and the new Anatsa banking trojan. These threats employ sophisticated evasion techniques and disguise tactics like maskware to hide malicious activity, emphasizing the importance of vigilance and app trustworthiness. #Joker #Harly #Anatsa #GooglePlay #Maskware

A spear-phishing campaign impersonates CoinMarketCap journalists to target crypto executives via Zoom interviews, risking malware and wallet theft. Attackers leverage fake profiles and remote control features to compromise systems during professional calls. #CoinMarketCap #ZoomExploitation…

Data I/O, a leading electronics manufacturer, experienced a ransomware attack that temporarily disrupted its operations and internal systems. The company is actively investigating the incident, which could have significant financial implications. #DataIO #RansomwareAttack…

Doctor Web researchers identified a multifunctional backdoor Android.Backdoor.916.origin targeting Russian business representatives, capable of surveillance and data theft. The malware disguises as a fake antivirus app called “GuardCB” and exploits device permissions to maintain stealthy control. #AndroidBackdoor916 #GuardCB…