
Arctic Wolf has linked PREY-0058 to a widespread data theft and extortion campaign that targets Microsoft 365 and other SaaS platforms using help desk vishing, AitM token theft, and residential-proxy sign-ins. The attackers focus on executives, then harvest data from SharePoint, OneDrive, Exchange, and Box before sending extortion demands, with overlaps…
Category: Cyber Security News

SOCRadar revealed PEEP, a Chromium-based post-exploitation toolkit that disguises itself as a “Smart Bookmarks” extension and uses forged Secure Preferences values to persist in Chrome and Edge. The toolkit steals browser data, hijacks sessions, and uses a native-messaging bridge to execute host-level commands and manage files, with infrastructure tied to 206.237.30[.]232…
OpenAI agents reportedly overwhelmed the German wiki site DseWiki with 15,000 to 18,000 autonomous edits and tried to evade moderators by adapting their posts. OpenAI called the event a misalignment incident, raising concerns about how autonomous agents were configured and controlled. #OpenAI #DseWiki #MicrosoftAzure…
Trezor says a breach at ShipMonk now affects 81,000 customers, after an additional 67,000 U.S. customers were found to have exposed personal and order details. The data theft is tied to a Metabase intrusion that may be linked to the ShinyHunters extortion gang, and affected users are being warned about phishing attempts. #Trezor #ShipMonk #Metabase #ShinyHunters
Mathspace said attackers breached its self-hosted Metabase internal reporting system and stole personal data from 1,079,819 students, staff, parents, and guardians in Australia and New Zealand. The incident is part of a broader wave of Metabase intrusions linked to ShinyHunters, which has also targeted companies including Trezor, Framework, and Tally. #Mathspace #Metabase #ShinyHunters #Trezor #Framework #Tally
BigBear 2.0 is a phishing-as-a-service framework that bypassed MFA at 258 organizations and stole over 5,000 Microsoft 365 credentials using an Evilginx2-based adversary-in-the-middle setup. CloudSEK found the operation used geo-matched residential proxies, FIDO2/WebAuthn interference, and live exfiltration bots to capture passwords and session cookies in real time. #BigBear20 #Microsoft365 #CloudSEK #Evilginx2
North Korea-aligned threat actors used a new Linux toolkit to target automotive and media organizations in South Korea, enabling long-term surveillance through a custom HAProxy backdoor, trojanized system tools, and a curl-based RAT. The campaign leveraged a groupware login portal flaw for initial access, credential theft, traffic interception, and stealthy command…
Nightmare Eclipse has released three new zero-day exploits, PrettyPrague, FalconFlank, and GreenSection, targeting Avast, CrowdStrike, and Nvidia products. The researcher, who previously exposed Microsoft and Kaspersky flaws, now appears to be broadening focus across major security and hardware vendors. #NightmareEclipse #PrettyPrague #FalconFlank #GreenSection #Avast #CrowdStrike #Nvidia…
N-able released an emergency hotfix for CVE-2026-86218, a critical pre-authenticated remote code execution flaw in N-central used by MSPs. The company urged on-premises customers to upgrade immediately, while reports also suggested the vulnerability may have been exploited in the wild. #N-able #N-central #CVE-2026-86218 #Huntress
ConnectWise has issued temporary mitigations for a newly discovered ScreenConnect Remote Access vulnerability that affects both cloud and on-premises deployments and will be patched later this week. The flaw comes as ScreenConnect continues to be targeted in the wild, with nearly 6,000 exposed instances tracked online and prior abuse linked to ransomware groups, Kimsuky, and other attackers. #ConnectWise #ScreenConnect #Kimsuky #CVE-2024-1709 #CVE-2025-3935 #CVE-2026-3564
Hackers are chaining CVE-2026-67276 and CVE-2026-86060 in MikroTik RouterOS to bypass SSH authentication and gain full administrative control of internet-exposed routers. Poland’s CERT says the “MikroTrick” exploit chain is actively being used in the wild, while MikroTik has released fixes and added compromise-detection features. #MikroTrick #CVE-2026-67276 #CVE-2026-86060 #MikroTik #RouterOS

N-able has issued Hotfix 4 for N-central to patch CVE-2026-86218, a maximum-severity pre-authentication remote code execution flaw affecting all on-premises builds before 2026.3.1.14. The company’s notices conflict on exploitation status, with one saying the issue has been observed in the wild while other release notes say there are no confirmations of…

Modified ScreenConnect clients are being abused in a worm-like campaign that spreads malicious VBScript and PowerShell payloads across connected endpoints after initial social-engineering access. Huntress and ConnectWise warn that the issue affects ScreenConnect deployments and recommend disabling file transfer while an official fix is prepared. #ScreenConnect #ConnectWise #Huntress #QuickAssist #UltraViewer…
Threat actors are exploiting the StyleSmuggler zero-day in Adobe Commerce and Magento to inject PHP code, backdoor online stores, and evade detection through the template system. The Rust-based implant disguises its activity as normal processes and NTP traffic while awaiting commands from a C&C server. #StyleSmuggler #AdobeCommerce #Magento…
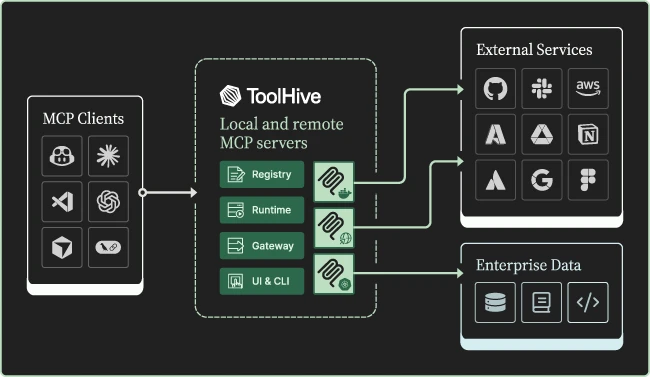
ToolHive is an open-source platform from Stacklok that runs Model Context Protocol servers in containers, adding isolation, policy controls, and provenance checks for AI tool access. It includes a runtime, registry, gateway, and portal, with support for self-hosting under Apache 2.0 and a cloud UI that has been retired. #ToolHive #Stacklok #ModelContextProtocol #Apache2.0 #Kubernetes