
Mars Security has introduced Real-Time Intel-Based Detection, a capability that turns newly published threat intelligence into validated detection rules within minutes. The platform converts reports from sources like CISA, Mandiant, Unit 42, and Microsoft Threat Intelligence into MITRE ATT&CK-mapped rules, backtests them on 30 days of customer data, and helps close detection gaps across tools such as CrowdStrike, Wiz, and Splunk. #CISA #Mandiant #Unit42 #MicrosoftThreatIntelligence #CrowdStrike #Wiz #Splunk #MITREATTACK #MarsSecurity
Category: Cyber Security News
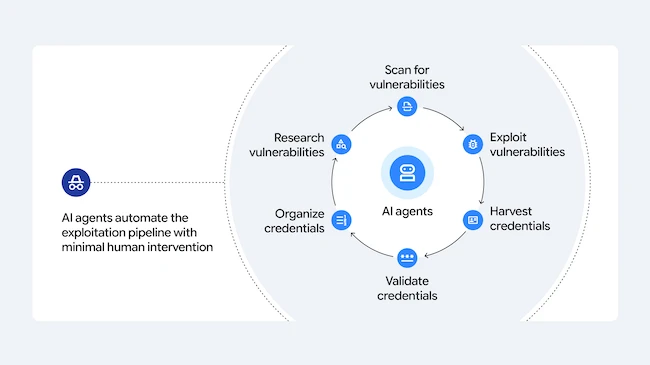
AI agents are increasingly being used to automate parts of cyberattacks, including vulnerability scanning, credential harvesting, and troubleshooting, according to Google Threat Intelligence Group’s Q3 2026 AI Threat Tracker. GTIG also observed threat actors experimenting with Gemini, Claude, and Codex to build offensive frameworks and exploit chains, while highlighting campaigns involving Recon, Shai-Hulud, and large-scale credential theft. #GoogleThreatIntelligenceGroup #Gemini #Claude #Codex #Recon #ShaiHulud

Waco’s experience shows that critical utility networks often include far more than plant controls, and that unsecured devices connected through public cellular networks can expose water and wastewater systems to intrusions. The article argues that fixing accountability and using existing funding mechanisms for microsegmentation are the fastest ways to protect infrastructure, with support from initiatives like Project Watershed 250 and state water cybersecurity programs. #Waco #ProjectWatershed250 #TexasCyberCommand #CISA #FBI #EPA
Mathspace has disclosed a data breach affecting 1,079,819 students, teachers, staff, and parents/guardians in Australia and New Zealand after attackers exploited a vulnerable self-hosted Metabase instance. The compromised data included names, usernames, email addresses, and account metadata, and the company warns it may be used for phishing attempts, while confirming no…
MikroTik has released patches for six RouterOS vulnerabilities, including two exploited flaws that CERT Poland says are being chained in attacks to bypass SSH authentication and fully compromise exposed devices. Users are urged to update immediately, as the MikroTrick campaign has already been observed targeting routers with public SSH access. #MikroTik…
A network of young scammers allegedly stole more than $240 million in bitcoin from a Washington, D.C. resident through a social engineering scheme involving fake Google and Gemini support calls. The stolen crypto was rapidly laundered and spent on luxury cars, mansions, private jets, and nightclub blowouts before FBI arrests began…
Researchers found an exposed APIS database containing more than 220 million passenger and crew records, including passport numbers, flight details, and other sensitive travel information tied to travel to, from, or through Vietnam. The exposure was traced to chained security misconfigurations and was later remediated, but it is still unclear whether the data was accessed, copied, or sold before it was secured. #APIS #KinryuLabs #Viettel #SingaporeAirlines #ChangiAirportGroup
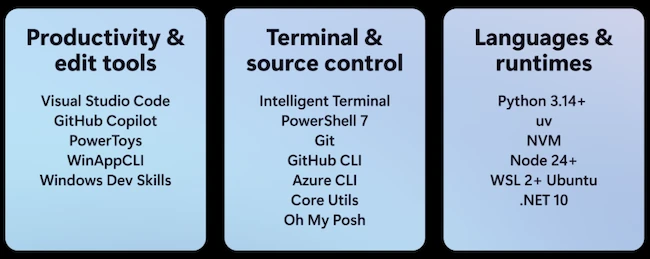
Microsoft’s Project Zenith is a ready-to-code Windows 11 experience for developer-class PCs built to run large local AI models with more than 30 billion parameters without relying on cloud tokens. It ships with a preconfigured development environment, built-in Linux support, and security features for AI agents, with the first systems powered by AMD Ryzen AI Halo. #ProjectZenith #AMD RyzenAIHalo #Windows11 #WSL #MicrosoftExecutionContainers
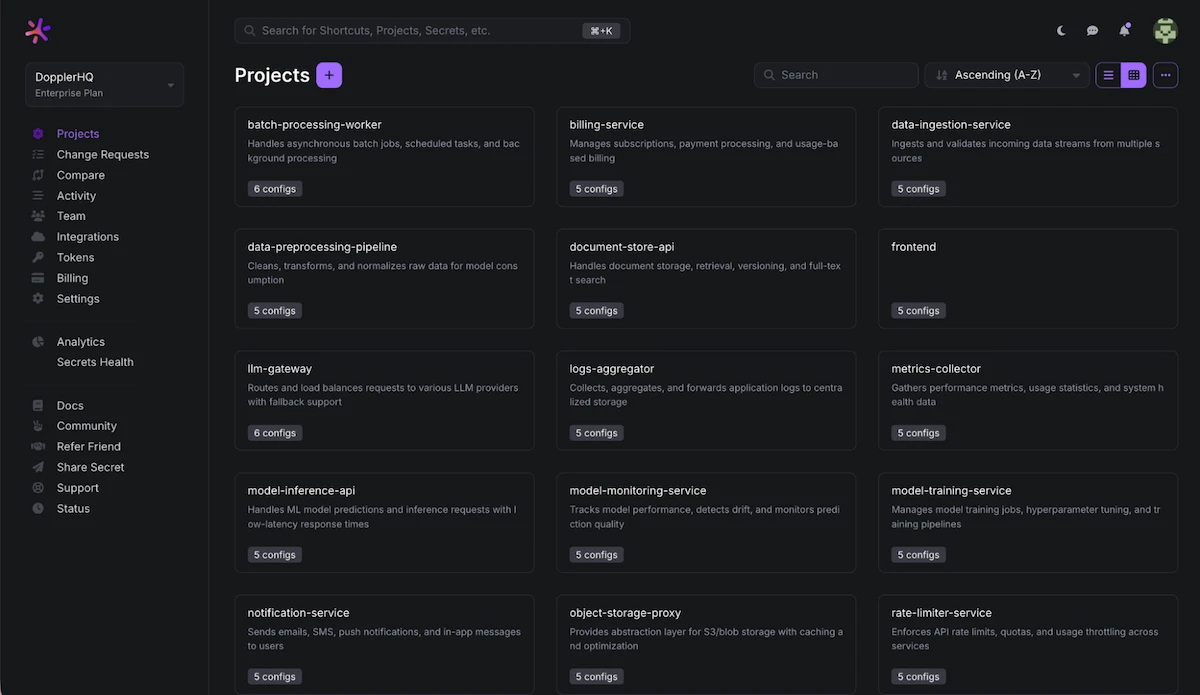
AI agents have multiplied the number of identities that need secure access to credentials, making modern secrets management essential for engineers, pipelines, and machines. Doppler centralizes, injects, and governs secrets for applications and AI agents with runtime delivery, fine-grained controls, and support for cloud or on-prem deployments. #Doppler #MCP #OIDC #AWS #Azure #GCP #SCIM

Dave Ross of Intel 471 explains the inner workings of ransomware negotiations, including how attackers research victims, set demands, and use test decryptions to prove they have a working key. He also highlights the criminal service economy, multi-extortion tactics, and the need for clear pre-incident response planning. #Intel471 #DaveRoss

Daily Recap, Attackers are actively leveraging multiple critical vulnerabilities, including N-able N-central CVE-2026-86218, an Adobe Commerce zero-day, and new MikroTik RouterOS bugs, to achieve RCE, plant backdoors, and hijack routers. Meanwhile, ConnectWise ScreenConnect is facing a worm-like file-transfer campaign, researchers revealed Nightmare Eclipse targeting CrowdStrike, Nvidia, and Avast, and Trezor reported breach impact affecting 81,000 customers.
#CVE-2026-86218 #N-able #N-central #AdobeCommerce #MikroTik #RouterOS #ConnectWise #ScreenConnect #NightmareEclipse #CrowdStrike #Nvidia #Avast #Trezor #CCQ #SEP-2026
German authorities are investigating another leak from Berlin’s government network after hackers published stolen login credentials and other data online, following an attack that hit two ministries in mid-August. The breach has been linked by the Rhysida ransomware group, while Berlin officials say they will not pay the attackers and are…

This week’s security recap highlights active exploitation of critical flaws in N-able N-central, Google Chrome, MikroTik RouterOS, and Magento/Adobe Commerce, alongside supply-chain abuse and phishing tricks that bypass common defenses. It also shows how attackers are exploiting trusted software sources, insecure management protocols, and AI-driven abuse to steal credentials and compromise…
CERT Polska uncovered six RouterOS vulnerabilities, including the MikroTrick chain that can give attackers full control of MikroTik devices with SSH exposed to the internet. MikroTik has released patched RouterOS versions, and administrators are urged to update immediately and check for signs of compromise such as the suspicious “ops” account and altered logs. #MikroTrick #RouterOS #CERTPolska #MikroTik #CVE-2026-67276 #CVE-2026-86060 #CVE-2026-67277
StyleSmuggler is a zero-day affecting all versions of Magento and Adobe Commerce that is being actively exploited to deliver a Rust-based backdoor. Sansec says the attack abuses Magento’s template system for code execution, with persistence, stealthy NTP-like command-and-control traffic, and signs that administrators should watch for suspicious reminder emails and unusual processes. #StyleSmuggler #Magento #AdobeCommerce #Sansec