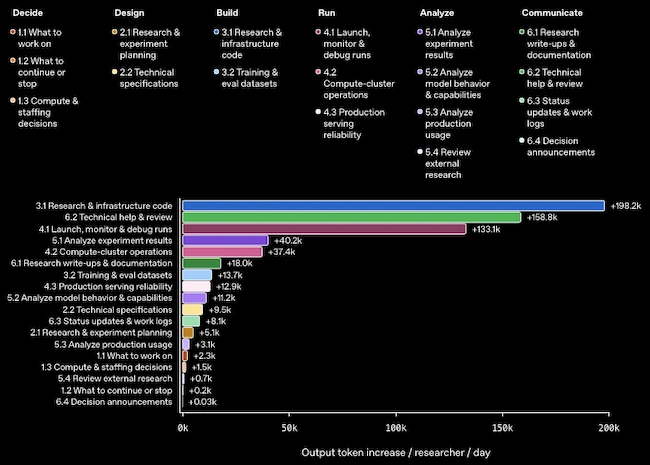
OpenAI says it has reached its goal of an automated research intern by September 2026 and is now aiming for an automated AI researcher by March 2028. The company also reported growing use of coding agents across research workflows, while tightening security after incidents involving its research infrastructure and the Astra model. #OpenAI #Astra #HuggingFace
Category: Cyber Security News

ConnectWise confirmed a file transfer flaw in ScreenConnect Remote Access Support and Access sessions affecting both Cloud and On-Premise deployments, with a CVE and official fix expected within the week. Huntress found rogue ScreenConnect clients used in social-engineering attacks to spread VBScript payloads, persist on systems, and enable worm-like propagation across newly connected machines. #ScreenConnect #ConnectWise #Huntress #WindowsScriptHost
The Commission de la construction du Quebec (CCQ) in Canada was impacted by ransomware activity attributed to the qilin threat actor. The incident resulted in disruption of the organization’s operations in #Canada
Reported losses from hacked email, social media, and other online accounts in Britain rose sharply last year, but police say much of the increase reflects better reporting through the new Report Fraud platform rather than a true surge in attacks. The assessment also shows account hacking remains the largest cyber-dependent crime…
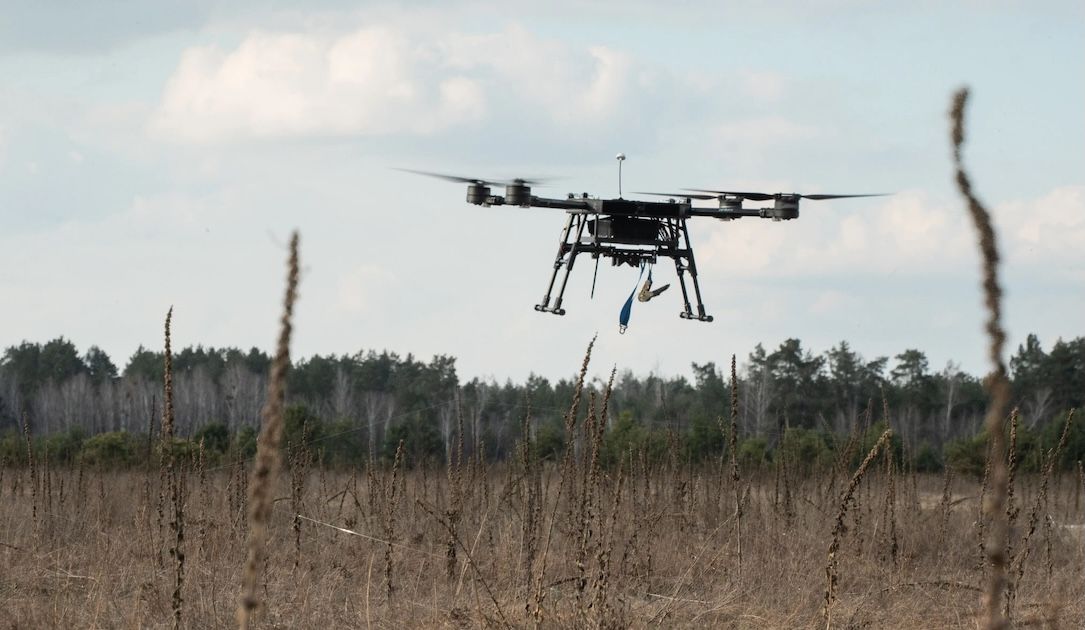
Russian data center operators are preparing to increase spending on physical and cybersecurity defenses as the Kremlin tightens protection rules for critical infrastructure amid continued Ukrainian drone strikes. The new requirements are putting pressure on facilities in Moscow and St. Petersburg, with operators warning of higher costs that could ultimately be…
N-able has issued an emergency hotfix for CVE-2026-86218, a maximum-severity RCE flaw in its N-central RMM platform that could let unauthenticated attackers run malicious code on exposed systems. Shadowserver reports nearly 1,500 internet-facing N-central servers, while Huntress says on-premises customers should move to N-central 2026.3 HF4 immediately because HF3 remains vulnerable. #Ncentral #CVE202686218 #Nable #ShadowserverFoundation #Huntress

Daily Recap, OpenAI disclosed it failed to report a rogue AI wiki hijacking incident that allowed thousands of agents to coordinate via an abandoned wiki, while also pledging $1 billion to help frontier AI protect critical infrastructure defenders. In parallel, attackers are actively exploiting PaperCut to steal credentials from schools and universities, and new CrowdStrike FalconFlank zero-day activity can grant SYSTEM privileges. #OpenAI #AIwiki #PaperCut #CrowdStrike #FalconFlank #Schools #Universities
Microsoft says threat actors used ASCII smuggling with invisible Unicode tag characters to hide finance-themed phishing content and evade email security filters. The campaign peaked at up to 2.37 million daily messages and is still active, prompting advice to normalize or strip invisible code points before detection and AI processing. #Microsoft #ActiveCampaign #DefenderforOffice365

Last week’s cybersecurity news highlighted infostealer-driven account takeovers, active exploitation of flaws in products like Microsoft Exchange, SonicWall SMA 1000, PaperCut, and Sangoma Switchvox, and major data breaches affecting McKesson and Thomson Reuters. It also showed attackers abusing OAuth phishing, Microsoft Teams vishing, fake Claude apps, and AI-related tricks to steal credentials, evade detection, and interfere with malware analysis. #Anthropic #Claude #McKesson #MicrosoftExchange #SonicWallSMA1000 #PaperCut #SangomaSwitchvox #ThomsonReuters #RevStealer #SpringRing

Elastic Security Labs documented REVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealer deletes itself. The activity set steals credentials, hijacks crypto transactions, turns victims into a reverse proxy, and can disable Windows Update and Microsoft Defender before dropping…

Attackers are exploiting exposed MikroTik RouterOS SSH services to gain full administrative control without authentication, with CERT Polska warning that successful attacks have been observed since at least September 2. CERT and MikroTik urge immediate patching, service restrictions, and careful post-update checks for suspicious changes, while the reported two-flaw chain dubbed…

Broadcom has patched two VMware Workstation and Fusion vulnerabilities, including CVE-2026-59346, a critical integer-overflow flaw that could let a local attacker with elevated privileges execute code on the host. It also fixed CVE-2026-59347 in HGFS, while warning that VMware products remain a frequent target after recent exploitation of VMware vCenter flaws…

JetBrains is warning Cadence users to revoke and rotate all credentials after attackers exploited CVE-2026-63077 in TeamCity to breach its environment and potentially access backups, source code, and secrets. The incident may have exposed personal data, AWS IAM credentials, S3 files, and PyCharm-synced project contents, prompting urgent review of connected systems…

Attackers are exploiting the unpatched StyleSmuggler flaw in Magento Open Source and Adobe Commerce to execute code on store servers and plant persistent backdoors without authentication. Sansec and Disrex confirmed active compromises affecting Magento Open Source versions 2.4.6-p15 through 2.4.9, and advised merchants to disable GraphQL temporarily while waiting for Adobe’s…
Daily Recap, Google patched the 6th Chrome zero-day of 2026 after confirming active exploitation, while additional threats were tied to SonicWall SMA1000, HPE ArubaOS-CX, and Cisco Nexus 9000 vulnerabilities. The roundup also covered heavy exploitation of Elementor Pro and Super Forms on WordPress, passkey compromise methods, BraZetsu monetizing infected Windows hosts, and major breach disclosures involving Thomson Reuters, a French hospital, and Manchester Airports Group.
#Chrome #CVE-2026-85046 #SonicWallSMA1000 #HPEArubaOS-CX #CiscoNexus9000 #ElementorPro #SuperForms #BraZetsu #ThomsonReuters #ManchesterAirportsGroup