Akeyless has launched Agentic Runtime Authority to give real-time identity control over AI agent actions, adding intent-based enforcement on top of its SecretlessAI credential protection layer. The solution helps organizations block unsafe agent behavior before execution, while expanding support for Claude Enterprise, OpenAI Codex, and Amazon Bedrock AgentCore. #Akeyless #SecretlessAI #AgenticRuntimeAuthority #ClaudeEnterprise #OpenAICodex #AmazonBedrockAgentCore
Category: Cyber Security News

FBI officials said AI is accelerating malicious hacking and vulnerability discovery, forcing organizations to move from quarterly patching to continuous, risk-based updates. The new FBI cyber strategy adds AI-enabled defense, victim support, threat intelligence sharing, and expanded disruption efforts against nation-state and cybercriminal actors. #FBI #BillingtonCyberSecuritySummit
The FBI says private-sector organizations are still hesitant to share cyber incident information because of misconceptions about how the bureau uses collected data. Brett Leatherman said the FBI’s new approach is to prioritize victim help, share actionable intelligence quickly, and support efforts against PRC-linked attackers and other nation-state actors. #FBI #BrettLeatherman #PRC
Plex has warned that more than 36,000 internet-exposed Plex Media Server instances remain unpatched against multiple security flaws affecting Plex Media Server v1.43.2 and earlier. Users are urged to upgrade to Plex Media Server 1.43.3 and Plex Desktop 1.115.0 before attackers reverse-engineer the fixes and exploit the vulnerabilities. #Plex #Shadowserver #CVE-2025-34158 #CVE-2020-5741
Strong authentication controls like MFA, conditional access, and device trust have made account takeover harder, pushing attackers toward weaker recovery processes such as service desk-driven password and MFA resets. Recent incidents involving Scattered Spider and Marks & Spencer show how impersonation and account recovery abuse can bypass defenses and cause major business damage. #ScatteredSpider #MarksandSpencer #EntraID #SpecopsSecureServiceDesk
Schneider Electric, Siemens, and Aveva released September 2026 Patch Tuesday advisories addressing multiple vulnerabilities in their industrial control and automation products. The updates include critical flaws such as CVE-2026-3869 in Modicon M580 controllers and CVE-2026-31431 in the Linux kernel, along with several high-severity issues across other ICS platforms. #SchneiderElectric #Siemens #Aveva…
Meta launched Muse, a personal AI agent for adults in the U.S. that helps with everyday tasks, long-term planning, and taking actions like opening a browser, filling out forms, and sending emails. The company says Muse runs in a dedicated secure virtual machine and reflects Mark Zuckerberg’s vision of AI agents…
The NSA, CISA, and FBI say several China-based AI companies have been extracting knowledge from U.S. frontier models through large-scale distillation, affecting models from Claude, GPT, Gemini, and Grok. The agencies warn this activity threatens U.S. technological leadership, with DeepSeek and Moonshot AI among the companies named in the report. #DeepSeek…
U.S. agencies say China-based AI companies have been running large-scale knowledge distillation campaigns to copy advanced capabilities from frontier models such as Claude, GPT, Gemini, and Grok. The advisory names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, and warns providers to strengthen verification, monitoring, and output controls to slow extraction efforts. #DeepSeek #MoonshotAI #AlibabaGroup #MiniMax #StepFun #ZAI #Claude #GPT #Gemini #Grok #CISA #NSA #FBI

Zscaler has introduced Zscaler Agentic SOC, an AI-first security operations model designed to proactively reduce exposures, detect threats faster, and contain attacks at machine speed. The platform combines Zscaler telemetry, Zero Trust controls, expert-validated AI agents, and integrations with Anthropic and OpenAI to counter AI-driven attacks and evasive tactics like trusted-site abuse, remote management tool misuse, and browser-based attacks. #Zscaler #Anthropic #OpenAI #Threatlabz #RedCanary #AgenticSOC
Sophos found a rootkit on compromised F5 BIG-IP APM devices that hides a web shell in memory instead of writing it to disk, making it harder for file-based security tools to detect. The campaign is linked to exploited F5 BIG-IP APM activity, including CVE-2025-53521, and uses staged malware with deeper Apache and PHP interception techniques. #F5BIGIPAPM #CVE202553521 #PoisonedRefresh

Sophos found that malware tied to intrusions on F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory, allowing the infected files on disk to appear clean. The activity is linked to CVE-2025-53521 and the c05d5254 malware, with related reporting from F5 and ESET’s PoisonedRefresh analysis. #F5 #BIG-IP…

cPanel has patched CVE-2026-67401, a flaw in EmailTrack that could let an authenticated hosting account create files and potentially escalate to root on the entire server. The issue affects all supported cPanel and WHM versions, with fixed builds now available across the 11.110, 11.134, 11.136, 11.138, and WP Squared release lines….

Google has released updates to fix 230 security vulnerabilities in Chrome, including CVE-2026-87491, a V8 out-of-bounds write flaw that is already being exploited in the wild. The update also addresses several critical issues in WebGL, Cast, and WebPackaging, and users are urged to update Chrome immediately for protection. #CVE-2026-87491 #V8 #GoogleChrome…
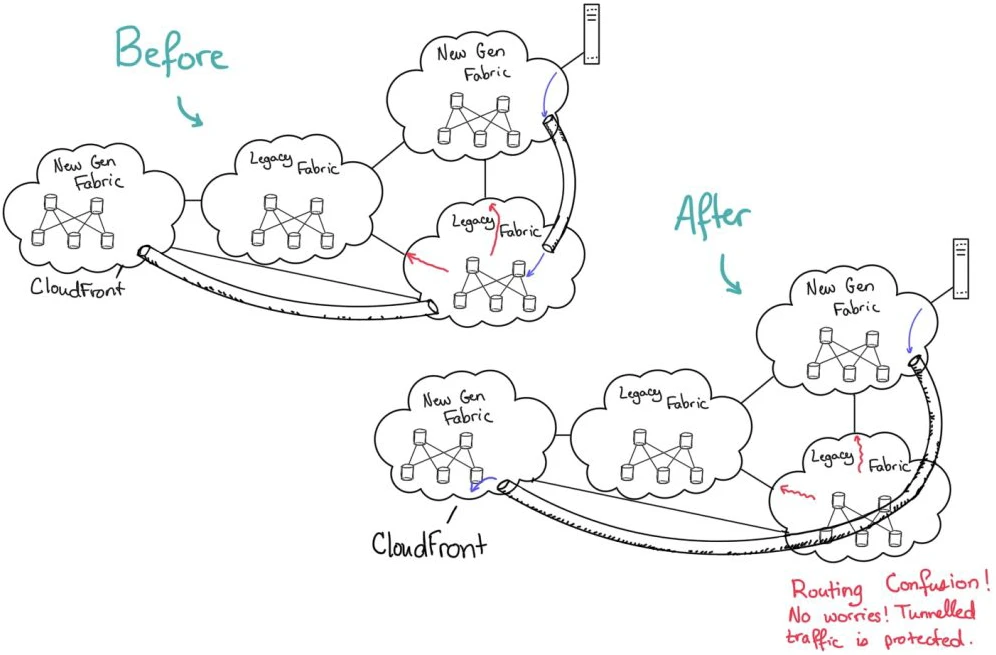
AWS rebuilt its border network routing control plane into a single unified system to improve convergence, reduce packet loss, and keep traffic consistent across its global infrastructure. The migration covered CloudFront, Route 53, Direct Connect, and backbone routers, with AWS reporting up to 96% faster convergence and more predictable latency. #AWS #CloudFront #Route53 #DirectConnect