AdaptHealth confirmed that a July-discovered cyberattack exposed data belonging to 4.1 million people, with the incident attributed to the ShinyHunters threat group. The breach stemmed from a social engineering attack that compromised a third-party contractor account and affected patient and health-related information. #AdaptHealth #ShinyHunters
Category: Cyber Security News
Cisco has confirmed that CVE-2026-20079, a maximum-severity authentication bypass flaw in Secure Firewall Management Center, is being actively exploited and can let unauthenticated attackers gain root-level access through crafted HTTP requests. The company and CISA urge immediate patching, as the vulnerability affects Cisco Secure FMC Software and Cisco Security Cloud Control Firewall Management, with evidence suggesting it may have been exploited alongside CVE-2026-20316. #Cisco #CVE-2026-20079 #CVE-2026-20316 #SecureFirewallManagementCenter #SecurityCloudControlFirewallManagement

Cybercriminals are using information stealer logs to hijack AI accounts and replay stolen session tokens, JWTs, JWEs, and API keys from providers such as Google, Anthropic, OpenAI, and others. The findings show a growing underground market for AI access, where stolen credentials are resold for LLMjacking, espionage, extortion, and resource theft….

BlueMoon is a newly observed exploit kit used in espionage campaigns to chain Chrome and Windows vulnerabilities for code execution, sandbox escape, and privilege escalation. Proofpoint linked the first in-the-wild use to APT31 and said the kit quickly spread to other China-aligned clusters while leaving behind persistence mechanisms such as malicious…

The U.S. Department of Justice and Treasury took coordinated action against Xinbi Guarantee, seizing Telegram channels, freezing cryptocurrency wallets, and sanctioning entities tied to scam operations and money laundering. The crackdown also expanded the Scam Center Strike Force effort in Madagascar, dealing a major blow to a marketplace linked to pig…
OpenSSL has released the first alpha of version 4.1.0, introducing DTLS 1.3 support and performance improvements for post-quantum cryptography. The build also brings several compatibility changes, new protocol features, and early support for additional architectures ahead of the final release. #OpenSSL #DTLS13 #MLDSA #MLKEM

Proofpoint found at least four China-aligned threat groups chaining three zero-day flaws in Chrome, Chromium-based browsers, and Windows to carry out espionage since late August. The BlueMoon exploit chain has been used against NGOs, mining and commodity firms, U.S. aerospace companies, and organizations in Vietnam, Indonesia, and Singapore. #TA412 #VioletTyphoon #APT31 #BlueMoon #CVE-2026-85046 #CVE-2026-87491 #CVE-2026-85880 #UNK_LateNight #UNK_DoubleCheck #UNK_QuietRacket
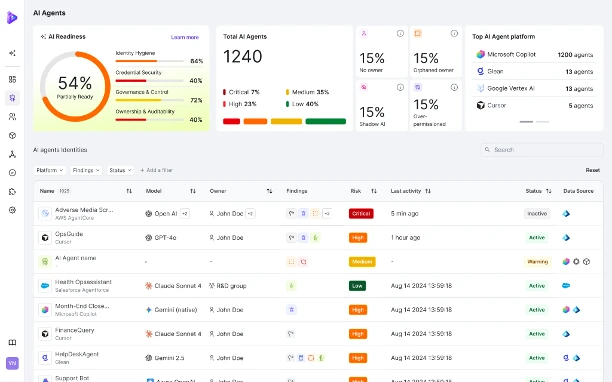
Orchid Security has introduced identity drift detection and application-level kill switches to help enterprises control AI agents that can exceed their intended scope by using hidden identity weaknesses. The company says AI adoption must be paired with continuous observation, governance, and auditability to prevent agents from exploiting orphaned accounts, excessive permissions, and other forms of identity debt. #OrchidSecurity #IdentityControlPlane #PaloAltoNetworksIdira #SplunkEnterpriseSecurity #NIST #DORA
A bipartisan group of U.S. lawmakers is urging the Treasury Department to sanction three India-based hack-for-hire firms, citing years of espionage against American citizens, companies, and lawyers. The firms—Sunkissed Organic Farms, BellTroX, and CyberRoot—have also been tied to global efforts to suppress reporting and, in some cases, alleged work on behalf of the Qatari government. #SunkissedOrganicFarms #BellTroX #CyberRoot #Qatar
The FTC has rescinded a Biden-era policy statement that expanded federal health data breach notification rules to cover health and fitness apps, citing minimal benefit and a shift toward deregulation. The move removes a rule that had aimed to hold apps and connected devices accountable for disclosing breaches involving sensitive health information and data sharing with third parties. #FTC #LinaKhan #HealthInsurancePortabilityAndAccountabilityAct
Veradigm disclosed a data breach after a third-party vendor compromise exposed patient personal data through a customer-service API, though the incident did not disrupt operations. The Gentlemen ransomware group claimed the attack and says it stole millions of patient records, including names, addresses, SSNs, and contact details, while Veradigm continues its investigation and notification efforts. #Veradigm #TheGentlemen #GentleKiller #SystemBC
U.S. cybersecurity and intelligence agencies say six Chinese AI companies conducted industrial-scale distillation attacks on frontier AI models from Anthropic, OpenAI, Google, and xAI since late 2024. The advisory says the campaigns used fraud, proxies, and API abuse to extract model knowledge at scale, with DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI named in the report. #DeepSeek #MoonshotAI #Alibaba #MiniMax #StepFun #ZAI #Anthropic #OpenAI #Google #xAI #CISA #NSA #FBI
Google released September 2026 Android security updates that patch 180 vulnerabilities across Android’s runtime, Framework, System, kernel, and multiple vendor components. The most severe issues include critical flaws in the System component and CVE-2026-28662, a Wi-Fi-related memory corruption bug that could enable remote code execution without user interaction. #Google #Android #CVE-2026-28662…
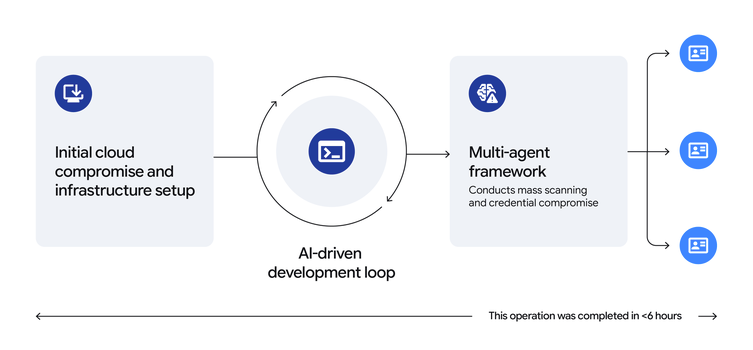
Google’s Threat Intelligence Group says adversaries are increasingly using AI to automate attacks, accelerate credential theft, and scale exploitation across the open-source supply chain. Nation-state-linked groups such as UNC6780, UNC6508, APT42, APT24, and UNC1069 are also leveraging AI for reconnaissance, malware development, social engineering, propaganda, and theft. #UNC6780 #UNC6508 #APT42 #APT24…
HelmGuard has raised $7.3 million in seed funding to expand its agentic governance, risk and compliance platform that continuously collects and evaluates risk signals from source systems. The startup says its AI agents can speed up assessments, unify fragmented compliance data, and help organizations govern AI agents across workflows. #HelmGuard #InfinityVentures…