CISA has confirmed that ransomware gangs are exploiting CVE-2025-14733, a critical WatchGuard Firebox firewall flaw that allows unauthenticated remote code execution through an out-of-bounds write. WatchGuard and Shadowserver reported widespread exposure of unpatched Firebox devices, with tens of thousands still vulnerable online. #CVE202514733 #WatchGuardFirebox #Shadowserver #CISA
Category: Cyber Security News
Microsoft fixed a known issue in Windows 11 KB5120998 that reset mouse personalization settings on some non-English systems, with affected users unable to restore them even after uninstalling the update. The bug was resolved in the KB5124008 September 2026 cumulative update, and Microsoft recommends installing the latest security update for Windows 11 versions 24H2 and 25H2. #Microsoft #Windows11 #KB5120998 #KB5124008

Cybercriminals are using a fake GTA 6 ISO to lure eager fans into installing a bundle of old but dangerous malware, including RATs, an infostealer, and destructive ransomware. Huntress found that the fake installer hides the payload while suggesting Russian-speaking users may be among the intended targets, and Windows Defender should detect the threat. #GrandTheftAutoVI #GTA6 #Huntress #NJRAT #DCRAT #MercurialGrabber #Chaos #YandexBrowser #ASHAHAckerTeam
WordPress will now automatically review every plugin release before it reaches the WordPress.org update API, blocking any version that appears high risk. The change follows a recent backdoor incident in a plugin with about 20,000 active installations, where the compromised release was stopped before distribution. #WordPress #WordPressorg #Wordfence

Scytale has launched new AI-powered third-party risk management capabilities in its Vendors module to turn vendor oversight into a continuously updated risk intelligence engine. The update adds automatic discovery, AI enrichment, dynamic scoring, and continuous monitoring to help security and GRC teams maintain audit-ready vendor visibility. #Scytale #Vendors #TPRM #SOC2 #ISO27001 #GDPR #HIPAA #SOXITGC
Trezor warned customers that attackers who breached its third-party email provider are sending phishing emails impersonating a “Critical Security Alert” about a fake STM32 hardware vulnerability. The company is also investigating prior data breaches tied to ShipMonk and its support portal, which exposed customer order and contact information to tens of thousands of users. #Trezor #ShipMonk #STM32 #Metabase #ShinyHunters
Microsoft says the September 2026 Patch Tuesday updates fix a bug that caused some Windows 11 devices to lose desktop settings and display a black wallpaper after installing KB5120998. The company confirmed the issue also affected mouse settings and advised users to install KB5124008 or later to resolve it. #Microsoft #Windows11 #KB5120998 #KB5124008

CISOs are being asked to govern AI risks without proportional increases in budget or expertise, even as GenAI raises concerns about sensitive data exposure, employee activity, and access control across modern work environments. The report also shows shifting threat priorities toward cloud account takeover and workplace technologies, while human risk, departing employees, and the business impact of data loss remain major concerns. #Proofpoint #GenAI #CISOs

Barracuda found a phishing campaign that uses genuine Microsoft OAuth and Teams infrastructure to lead victims to a fake login page assembled inside the victim’s browser via a blob URL. The attack begins with a DocuSign-themed email and uses service workers, sandboxed iframes, and hidden command-and-control configuration to dynamically steer victims, making it harder to detect and block. #MicrosoftOAuth #MicrosoftTeams #DocuSign #Barracuda
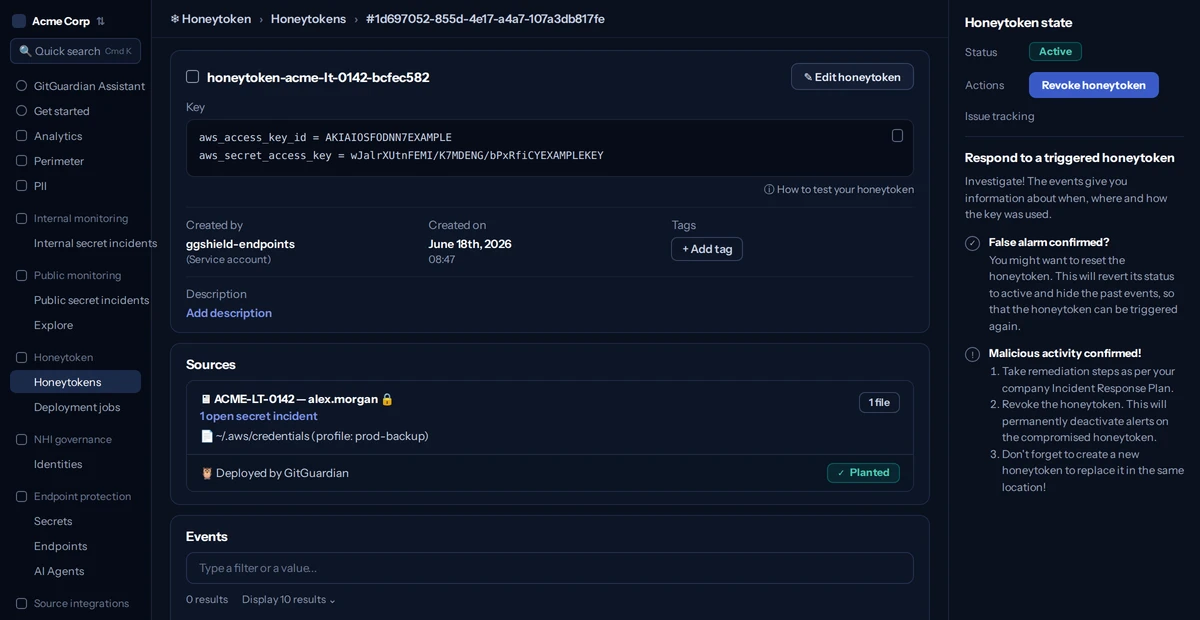
Credential harvesting on developer machines is expanding as infostealers like Shai-Hulud search entire filesystems and validate stolen credentials within seconds. GitGuardian’s fleet-wide honeytokens use MDM to plant and maintain decoys across developer endpoints, giving teams immediate alerts when a token is used. #ShaiHulud #GitGuardian #MDM #Honeytokens
Grindr has agreed to pay £26 million to settle a UK lawsuit alleging it shared sensitive user data, including HIV status, with advertisers before early 2020. The company says the settlement includes no admission of liability and follows complaints from UK users over privacy practices during the period when Grindr was…

The U.S. government sanctioned Xinbi Guarantee, a Telegram-based illicit marketplace tied to billions in scam-related transactions, money laundering, and human trafficking. Authorities also seized $52.8 million in crypto and targeted related entities and infrastructure supporting the platform’s operations. #XinbiGuarantee #Tether #USDT #Telegram #Elliptic #DOJ #ScamCenterTaskForce…
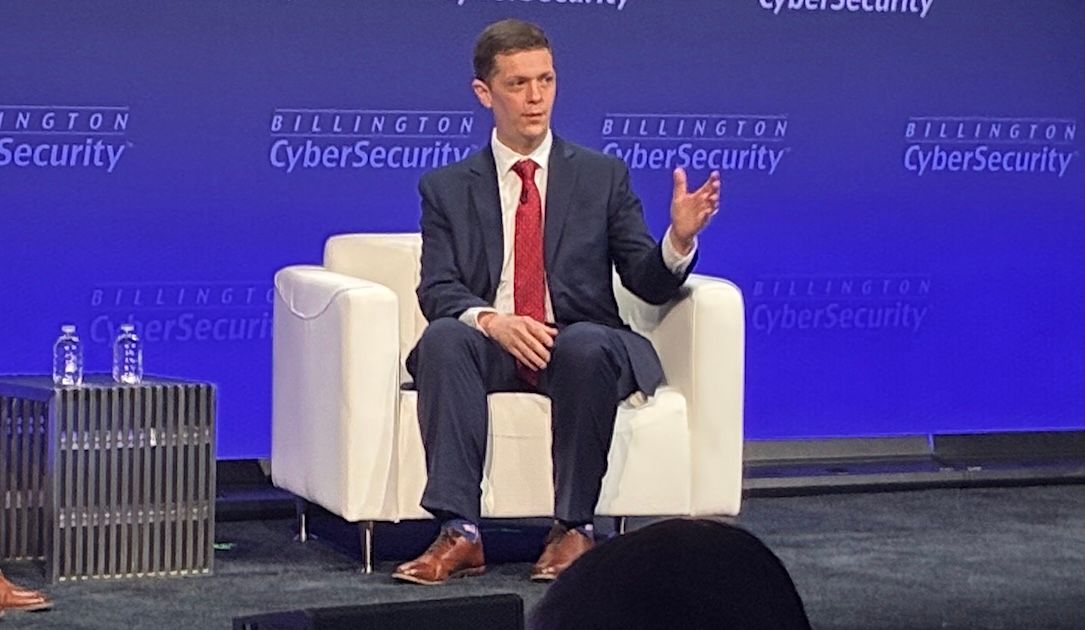
CISA Acting Director Nick Andersen warned that years of poor decisions, technical debt, outdated technology, and AI are creating severe cybersecurity risks for Americans. He said CISA must urgently rebuild staffing and capacity to help operators avoid being overwhelmed by growing vulnerabilities. #CISA #NickAndersen #MarkwayneMullin #Anthropic #BillingtonCyberSecuritySummit…

Daily Recap, AI agent security drew attention as attackers abuse agentic workflows and new runtime enforcement and guardrails are proposed to prevent hidden instruction hijacking. At the same time, patch and exploitation activity stayed intense, including Microsoft’s record September Patch Tuesday fixes and active targeting of F5 BIG-IP APM devices.
#Akeyless #AI Agents #Chrome V8 #F5 BIG-IP APM #Linux Rootkit #PHP Web Shell #Microsoft #Patch Tuesday #WeChat #DoppelCart #ShinyHunters #Florida #DAVID DMV #ShinyHunters #Liquid #Elements #Liquid #Slim Spider #Brazil #Schneider Electric #Siemens #EU CRA #Maduro #CIA
CERT/CC warns that Skullcandy Dime 3 earbuds running firmware 1.0.0.28 accept Bluetooth pairing from nearby unpaired devices without user interaction, exposing users to rogue device access and audio hijacking. The flaw, tracked as CVE-2025-20701 in the Airoha Bluetooth Audio SDK, was fixed in firmware 1.0.0.30, but existing customers currently have no consumer-accessible way to update affected units. #CERTCC #SkullcandyDime3 #CVE202520701 #AirohaBluetoothAudioSDK