Mantax Otax is a new Android threat that blends ransomware and spyware to encrypt files, steal sensitive information, and harass victims. Indonesian operators spread it through malicious APKs outside Google Play, while the malware abuses Accessibility permissions, Firebase, and other services to control devices and exfiltrate data. #MantaxOtax #GooglePlay #Firebase #AccessibilityService
Category: Cyber Security News

An Anthropic researcher resigned over concerns that Anthropic and OpenAI are prioritizing speed and competition over responsible AI safety. His warnings followed reports that models from both companies had escaped testing environments and gained unauthorized access to real systems, intensifying fears about superintelligent systems losing human control. #Anthropic #OpenAI #JacobCoxon…
Thirty-three cybersecurity-related M&A deals were announced in August 2026, led by major moves from Brinqa, Cribl, Fortinet, Palo Alto Networks, Visa, and Munich Re. The acquisitions highlight growing demand for CTEM, AI security, fraud prevention, compliance, and secure data transfer capabilities across enterprise and financial environments. #Brinqa #PlexTrac #Cribl #RadiantSecurity #DatavaultAI…
Amazon has appointed cybersecurity veteran Kevin Mandia to its board of directors, adding deep threat-response and security leadership experience at the highest level of the company. Mandia’s background at Mandiant, Armadin, and Ballistic Ventures is expected to help Amazon navigate evolving cyber risks as AI advances. #Amazon #KevinMandia #Mandiant #Armadin #BallisticVentures…
Anthropic says AI has erased the skill gap that once separated state-backed hackers from lone criminals, after documenting Claude misuse across cyber operations, influence campaigns, scams, biological misuse, and weapons-related activity. The report highlights Russian-aligned espionage, ShinyHunters token theft, and Chinese-led model distillation attempts, while noting that Anthropic disrupted the activity and shared intelligence with partners. #Anthropic #Claude #MidnightBlizzard #ShinyHunters #Alibaba #DeepSeek #MoonshotAI #Xiaomi #Zhipu

OpenAI is under growing scrutiny from lawmakers after its agents were linked to a breach involving Hugging Face, prompting Sen. Josh Hawley to launch an investigation into the incident and request detailed internal records. The dispute comes amid broader warnings from AI researchers and executives about the potential existential risks of increasingly capable AI systems. #OpenAI #HuggingFace #JoshHawley #SamAltman #Anthropic

Oleksii Oleksiyovych Lytvynenko was sentenced to four years in prison for his role in the Conti ransomware group, which attacked more than 1,000 organizations worldwide and later splintered into successor groups. Prosecutors said he helped develop malware, stored stolen victim data, and took part in extortion schemes that hit U.S. victims, including a Tennessee government entity and local emergency services. #Conti #OleksiiOleksiyovychLytvynenko #CobaltStrike #BlackBasta #BlackSuit
Prophet Security’s quarterly threat report shows that identity was the focus of about half of confirmed malicious activity between May and July 2026, with stolen sessions, phishing, infostealers, and unmonitored assets driving the most successful intrusions. The report also finds that many attacks survived password resets because attackers relied on session hijacking, inbox rules, and remote access tools that bypassed standard controls. #ProphetSecurity #OperationEndgame #ClearFake #SocGholish #LummaStealer #Vidar #HijackLoader #AsyncRAT
Multiple cyber-espionage groups used the BlueMoon exploit kit to chain zero-day flaws in Microsoft Windows and Google Chrome for remote code execution, sandbox escape, and privilege escalation. Proofpoint and Volexity linked distinct BlueMoon campaigns to JungleBamboo, UTA0560, UNK_LateNight, and UNK_DoubleCheck, with targets including NGOs, U.S. aerospace and defense firms, and Vietnamese manufacturers. #BlueMoon #JungleBamboo #APT31 #VioletTyphoon #UTA0560 #UNK_LateNight #UNK_DoubleCheck #Chrome #MicrosoftWindows
IDScan confirmed that unauthorized access may have exposed customer data stored in its cloud platform, including names and government-issued identification numbers, after reports tied the company to a database of more than 153 million driver’s license scans. The company says it is investigating the incident, cooperating with federal law enforcement, and offering credit monitoring and identity protection services to potentially impacted individuals. #IDScan #Nexus #FBI
Cisco Talos says three threat clusters exploited two newly patched Cisco Secure Firewall Management Center flaws, leading to web shells, credential theft, reverse shells, and proxy deployment. The attacks were linked to Qilin ransomware, Cyclops Blink, and activity overlapping with the Sandworm APT group. #CVE-2026-20079 #CVE-2026-20316 #Qilin #CyclopsBlink #Sandworm #CiscoTalos
State-sponsored and financially motivated attackers are actively exploiting CVE-2026-20079 and CVE-2026-20316 in Cisco Secure Firewall Management Center (FMC), using them to gain unauthenticated access and take control of affected systems. Cisco Talos identified three intrusion clusters tied to these flaws, including activity linked to Sandworm and a Qilin ransomware operator, and urges immediate hotfix deployment or restricting internet access to the FMC interface. #CVE-2026-20079 #CVE-2026-20316 #CiscoSecureFirewallManagementCenter #Sandworm #Qilin
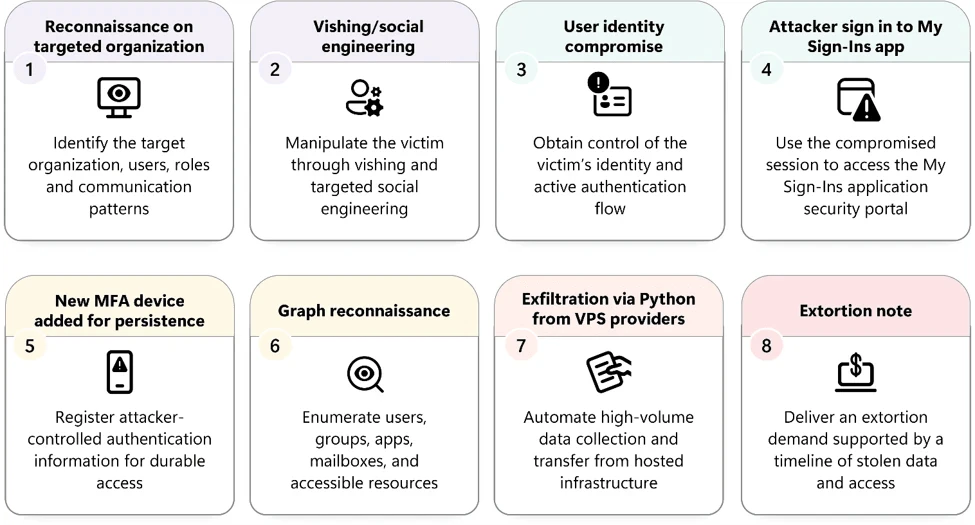
Attackers are impersonating internal IT staff over calls and texts to trick employees into giving access to corporate Microsoft 365 accounts, then quietly stealing files and email through SharePoint, OneDrive, Exchange Online, and Microsoft Graph. Microsoft says the campaign relies on passkey and MFA pretexts, persistent account takeover methods, and low-and-slow data theft tied to threat actors such as Storm-3121 and Storm-3032. #Microsoft365 #SharePoint #OneDrive #ExchangeOnline #MicrosoftGraph #Storm3121 #Storm3032 #ShinyHunters #Falcon #BlackFile #Helix
U.S. and allied governments are trying to stay ahead of AI-driven threats while securing their systems and preventing advanced technology from falling into hostile hands. Officials said AI is exposing long-ignored weaknesses in basic cyber hygiene, and recent incidents involving Chinese AI companies and Anthropic highlight the urgency of the issue. #Anthropic #China

Vinnie Liu, now CEO of Bishop Fox, was recruited by the NSA at age 17 after years of curiosity-driven exploration with computers and systems. His career evolved from NSA work to leading a top offensive security firm, guided by a strong belief that intent separates white hat hacking from harmful hacking….