
Kerri Shafer-Page of Arctic Wolf outlines a ransomware decision tree that organizations should prepare in advance, focusing on containment, extortion negotiations, and the business impact of paying a demand. She also stresses involving law enforcement, legal counsel, and communications teams early so decisions are made before a crisis hits. #ArcticWolf
Category: Cyber Security News

Researchers from Michigan State University and partner schools showed that lost-device reporting systems across carriers can be abused to block phones and other connected devices that were never actually stolen. They found weaknesses in carrier identity checks, IMEI disclosure on certain chipsets, and cross-carrier block-list sharing, affecting devices such as Samsung Galaxy Z Fold 7 phones and home alarm gateways. #SamsungGalaxyZFold7 #GSMA #MichiganStateUniversity

Daily Recap, U.S. officials, the FBI, and other security leaders warned that AI is boosting adversaries and highlighted the need to keep fundamentals—like patching and threat sharing—tight across government and CISOs. Attackers are also abusing stolen AI artifacts to replay AI tokens that can bypass MFA, while Cisco and WatchGuard confirm exploited flaws and ransomware activity tied to CVE-2026-20079, CVE-2026-20316, and WatchGuard RCE alongside major breach disclosures from AdaptHealth and Veradigm. #AI #MFA #Cisco #CVE-2026-20079 #CVE-2026-20316 #SecureFMC #WatchGuard #Android #Microsoft365 #AdaptHealth #Veradigm #Xinbi #FTC #FBI #CISA
A Ukrainian national, Oleksii Oleksiyovych Lytvynenko, was sentenced to four years in prison for helping carry out Conti ransomware attacks between 2021 and 2022. He admitted to acting as both an intruder and developer in the Conti operation, which targeted more than 1,000 victims worldwide and generated over $150 million in ransom payments. #Conti #OleksiiOleksiyovychLytvynenko #TrickBot #Ryuk
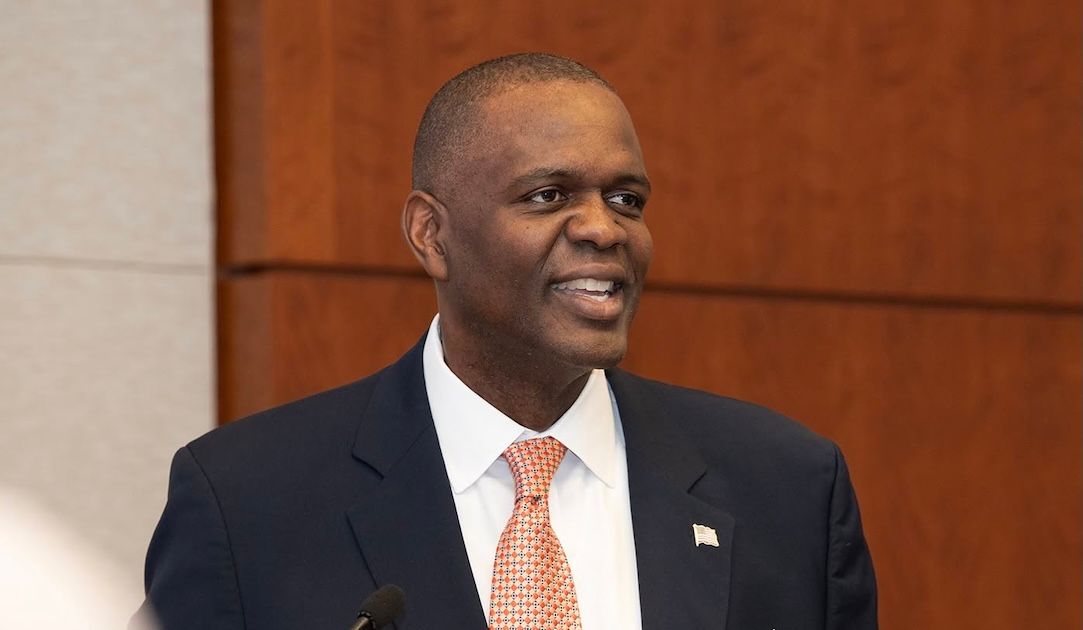
U.S. Cyber Command has named Ronzelle Green as its new chief artificial intelligence officer as it accelerates efforts to embed AI into cyber operations. The command is also seeking a major funding increase for AI capabilities, while leaders say Green should centralize the many scattered AI initiatives across the military.
#USCyberCommand #RonzelleGreen…

IDScan confirmed that an unauthorized third party may have accessed customer data stored in its cloud platform after reports linked the company to a massive dark web database sale. The exposed records may include names and government ID numbers, while the FBI has launched an inquiry into the incident. #IDScan #Nexus…
FinCEN warned financial institutions to be more vigilant as overseas scam centers drive a surge in cryptocurrency investment fraud, with more than $12.7 billion stolen from Americans across all 50 states and U.S. territories. The report also highlighted the laundering role of Telegram-based marketplace Xinbi Guarantee, which was sanctioned after helping…

Check Point has patched two critical VPN certificate flaws, CVE-2026-85102 and CVE-2026-85103, that could let an unauthenticated remote attacker execute code on Security Gateway and Security Management systems under specific conditions. The company says it found the issues internally, has seen no exploitation, and is rolling out fixes through Live Patch…

Bad actors are abusing Google Play’s Early Access program to distribute deceptive Android apps that promise cash, rewards, casino wins, and premium content while evading public reviews and ratings. The activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to…

This week’s security stories all point to the same failure: ordinary tools, trusted services, and exposed systems were allowed to do too much. From malicious browser extensions and npm packages to AI-driven intrusions, phishing relays, and ransomware chains, attackers kept exploiting weak handoffs already in place. #AxiomTrade #Padre #AnthropicClaudeCode #AlibabaQwen #DeepSeek…

Google has enabled a new Android transfer feature that lets users move passwords and passkeys directly between supported password managers without exporting them to a file. The feature currently works with Google Password Manager, 1Password, Bitwarden Password Manager, and Dashlane, with more partners expected later. #GooglePasswordManager #1Password #Bitwarden #Dashlane
A likely Russian-speaking threat actor used hundreds of AI agents to build and launch a fast-moving global campaign against vulnerable PaperCut NG/MF servers, exploiting CVE-2026-81578 and CVE-2026-82078. GreyNoise says the operation compromised hundreds of organizations worldwide and used post-exploitation techniques to harvest credentials and gain domain-level access, underscoring how AI can compress attack timelines dramatically. #PaperCut #CVE-2026-81578 #CVE-2026-82078 #GreyNoise #Codex #DeepSeek #Netlas
Microsoft Excel users are reporting that the KB5002914 Office security update is breaking copy-and-paste and formula dragging in multiple versions of Excel. Affected users say removing the update or rolling back Office restores normal behavior, and reports have appeared across Reddit and Microsoft Q&A forums. #KB5002914 #Excel #OfficeLTSCStandard2021
Surfshark said a misconfigured internal test server was exposed to the internet, allowing unauthorized access to build-related credentials, service configurations, and some system binaries without affecting customer data or production VPN infrastructure. The company contained and remediated the incident, rotated credentials, and said there is no evidence of misuse or broader compromise. #Surfshark
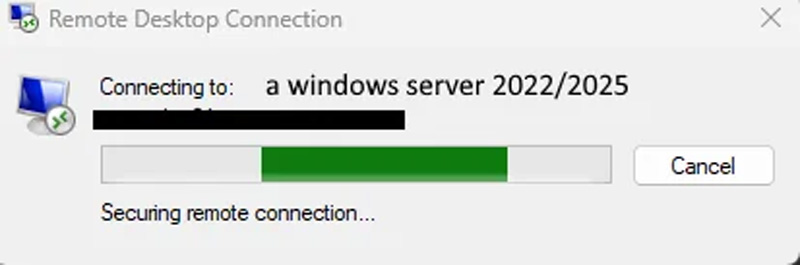
September 2026 cumulative updates are causing Remote Desktop Services failures on Windows Server 2019, 2022, and 2025, leaving some systems unable to accept new connections and sometimes requiring a hard reset. Rolling back the updates appears to restore access, but it also removes the security fixes included in the Patch Tuesday release. #Microsoft #WindowsServer2019 #WindowsServer2022 #WindowsServer2025 #PatchTuesday